Señales de Advertencia del Agente Doble: Una Guía de Contrainteligencia

agente doble, inteligencia, contrainteligencia, espionaje, contraespionaje, espía, C. Constantin Poindexter Salcedo, seguridad nacional, DNI, CNI, CIA, DIA

Leyendo el señuelo (dangle): guía de campo del profesional sobre la fuente controlada y la reforma de la validación de activos. Un ensayo en la voz de un antiguo tipo de la CI.

Lo más difícil en la HUMINT no es reclutar una fuente. Es saber si la fuente que reclutaste te pertenece a ti. La reciente reconstrucción de fuente abierta (“OSINT”) que hizo Alexander Orleans del caso GTPROLOGUE (el despacho que el KGB hizo en 1987 del oficial de planta Aleksandr “Sasha” Zhomov contra la Estación de Moscú de la CIA) es la mejor anatomía pública en años de cómo un servicio hostil construye, en la frase de Churchill, una escolta de mentiras alrededor de una sola verdad operativa (Orleans 2025). A Zhomov lo corrieron durante aproximadamente tres años antes de que la CIA concluyera que había estado controlado desde el primer contacto. Lo instructivo del caso no es que engañaran a la CIA. Eso le pasa hasta a los mejores servicios. Es que el caso levantó casi todas y cada una de las banderas de advertencia clásicas. Las banderas se vieron, se debatieron, y el caso sobrevivió (Orleans 2025; Bearden y Risen 2003).

He compilado aquí un catálogo de trabajo de esas banderas y de otras tomadas de una literatura un poco más amplia, cada una anclada a un caso real, seguido de las mejoras que el mecanismo de contrainteligencia debería institucionalizar. He tratado de mantenerme tan cerca de la tradecraft real como lo permite el registro abierto. Nada de esto requiere acceso clasificado para entenderse. La verdad dolorosa es que los indicadores son bien conocidos y lo han sido por lo menos desde el tratamiento fundacional que F. M. Begoum le dio al agente doble en 1962 en Studies in Intelligence (Begoum 1962). Por desgracia, los seguimos reaprendiendo.

Los Indicadores

Producción desproporcionada al acceso. El indicio más duradero es una fuente que se sienta sobre una montaña de secretos y te entrega gravilla. Zhomov era un oficial de planta del Primer Departamento que supervisaba la vigilancia del jefe de estación de Moscú, y sin embargo afirmaba tener apenas un “acceso periférico o infrecuente” al mismísimo material que su puesto debía hacerle rutinario (Orleans 2025; Grimes y Vertefeuille 2012). Los soviéticos tenían una razón estructural para esto: la doctrina estricta prohibía liberar alimentación genuina de alto grado, y los oficiales temían un ajuste de cuentas estilo Stalin por divulgar de más, así que sus señuelos venían entrenados para alegar acceso escaso (Diamond 2008; Earley 1997). Cuando los reportes de una fuente quedan consistente y convenientemente por debajo del techo que su ubicación implica, pregúntate a quién beneficia el racionamiento.

La fuente controla el plan de comunicaciones y el tempo. El control es la capacidad del servicio que corre el caso de iniciar, alterar o detener el comportamiento del agente (Begoum 1962). Zhomov llegó con un plan de comunicaciones impersonal completamente formado —buzones de cartas a través del carro sin seguro de Downing, contacto a discreción de Zhomov, sin reuniones cara a cara prolongadas— que ponía cada palanca en manos del KGB e incluso restringía los movimientos físicos de sus manejadores de la CIA (Orleans 2025; Bearden y Risen 2003). Compárese con el estándar de oro del arreglo opuesto: el Comité XX británico en la Segunda Guerra Mundial, que poseía física y comunicacionalmente a cada agente alemán en el Reino Unido y por tanto podía alimentar a Berlín con confianza (Masterman 1972). Cuando el agente dicta la arquitectura del contacto, no lo estás corriendo a él. Él te está corriendo a ti.

Motivación delgada, genérica o sin respaldo. El espionaje contra el propio servicio es un acto psicológico profundo. Un activo o fuente creíble puede narrar de forma convincente por qué cruzó esa línea, y la historia se sostiene bajo verificación colateral. Zhomov ofreció el cliché de un sistema que se agriaba y un matrimonio en quiebra (y el interrogatorio independiente del desertor Sergey Papushin lo contradijo de plano, describiendo a Zhomov como felizmente casado y devoto de su hija) (Orleans 2025; Grimes y Vertefeuille 2012). Un motivo que no sobrevive a una segunda fuente no es un motivo; es una leyenda de cobertura.

La llegada “demasiado buena para ser cierta”. Los servicios hostiles leen tus brechas de recolección y las llenan a pedido. Zhomov apareció precisamente cuando la CIA estaba desesperada por explicar las catastróficas pérdidas de activos de 1985–86, con exactamente el acceso para “explicarlas” (Orleans 2025). “Demasiado bueno” y “cierto” no son mutuamente excluyentes. Los voluntarios espontáneos (walk-ins) genuinos sí ocurren en el peor momento posible; sin embargo, una oportunidad tan perfectamente a tono debería elevar la carga de la prueba, no bajarla (Johnson 2009). El desastre cubano es el monumento aleccionador aquí. Cuando el mayor Florentino Aspillaga Lombard desertó en Viena en junio de 1987, reveló que esencialmente cada cubano que la CIA creía haber reclutado desde principios de los años sesenta había sido un agente doble corrido por La Habana, que había mercadeado deliberadamente a sus oficiales como latinos aficionados para operar por debajo del radar (Latell 2012). Décadas de “éxitos” eran un solo engaño paciente.

Ninguna urgencia genuina por la exfiltración. Un hombre que dice que se quiere salir, y que está guardando su mejor material para su interrogatorio en suelo seguro, eventualmente debería preguntar: “¿Cuándo me voy?”. Zhomov nunca pidió un cronograma. Cuando finalmente le ofrecieron una ruta de exfiltración en 1990, la repudió por ser demasiado riesgosa y se fundió de vuelta en su equipo de vigilancia (Orleans 2025; Bearden y Risen 2003). El supuesto desertor que nunca quiere desertar está hablando mierda, no empacando su maleta de fuga.

Bona fides autovalidantes y alimentación que nunca hiere de verdad al servicio matriz. Una fuente controlada construye credibilidad con material que parece costoso pero no lo es. Zhomov entregó un padrón preciso de las pérdidas de 1985–86, dañino a primera vista, pero lo envolvió dentro de la falsa narrativa del SCD “cabrón e infalible” de que las pérdidas se debían a una tradecraft soviética brillante y no a un topo (Orleans 2025). La alimentación validaba el canal mientras protegía el secreto que el canal existía para proteger: Aldrich Ames. Escudriña si las “joyas de la corona” de tu fuente realmente le costaron algo a su servicio, o si cada divulgación adelanta calladamente los intereses de su servicio. Para ponerlo en lenguaje de riesgo: si no representa un peligro para el servicio matriz, no vale nada.

Errores de tradecraft de la oposición incompatibles con la competencia que reclama. Los reportes de Zhomov predecían una ola de señuelos del KGB. La CIA entonces vio al KGB correrlos tan chapuceramente que dos quedaron descaradamente expuestos como provocaciones. La Estación de Moscú racionalizó el desliz como descuido soviético endémico, sin notar nunca que la tradecraft descuidada era lógicamente irreconciliable con el SCD omnisciente del que Zhomov alardeaba (Orleans 2025). Un servicio no puede ser simultáneamente infalible y chapucero. Cuando el cuadro que pinta tu activo contradice el comportamiento que observas, créele a tus ojos.

La ventaja de jugar “en casa” en el área denegada. El entorno es en sí mismo un indicador porque moldea cuáles otros indicadores puedes siquiera poner a prueba. Todo el caso Zhomov se desenvolvió dentro de Moscú, donde el KGB controlaba la calle, impedía interrogatorios largos y podía rechazar cualquier reunión bajo el argumento incontestable de que no podía evadir a sus propios equipos de vigilancia (Orleans 2025). El resumen franco de Paul Redmond sobre la validación en área denegada —pocas o ninguna fuente colateral, fuerte dependencia del valor del material y de cómo empezó el caso, etc.— describe un problema que la oposición diseña deliberadamente (Redmond 2010). Un caso nacido y criado enteramente en terreno del adversario ha tenido sus opciones de validación estranguladas al nacer.

Resistencia a las pruebas operativas, y su jodido inverso que da miedo. Zhomov respondía las preguntas duras de verificación con respuestas que sus propios oficiales de contrainteligencia hallaban vagas o improbables, y se desviaba con la promesa de contarlo todo después de la extracción (Orleans 2025; Grimes y Vertefeuille 2012). La renuencia a ser puesto a prueba —la evasión del polígrafo, de las tareas provocadoras, de la “lista de compras” diseñada para atraparlo— es en sí misma reveladora e instructiva. Este indicador trae una advertencia que el caso GTPROLOGUE no provee, y que la profesión debe internalizar. La paranoia también quema a las fuentes reales. El manejo prolongado y brutal del desertor soviético Yuri Nosenko como presunta provocación, y la sospecha que casi le cuesta a la CIA al genuinamente invaluable general del GRU Dmitri Polyakov, son la patología igual y opuesta de la credulidad que protegió a Zhomov (Bagley 2007; Wise 1992). La validación es duda calibrada, no un reflejo en ninguna de las dos direcciones.

“El hambre”, y los incentivos que la alimentan. Orleans nombra al culpable silencioso: el apetito del oficial de caso por un golpe espectacular, la reticencia institucional a presionar una fuente deslumbrante lo bastante duro como para perderla (Orleans 2025). Redmond fue más franco, atribuyendo los fracasos de validación posteriores a Angleton en parte a oficiales que no creían que sus propios casos pudieran ser fabricados, “particularmente cuando había ascensos de por medio” (Redmond 2010). La catástrofe cubana hizo metástasis exactamente en este suelo: una voluntad organizacional de creer en reclutamientos que halagaban a los reclutadores (Latell 2012). La bandera más cara es la que elegimos no ver porque verla nos cuesta un logro de carrera.

Lo Que la Función de Contrainteligencia Debería Implementar

Los indicadores son necesarios pero no suficientes; una agencia que meramente los enumera será engañada igual, porque el caso Zhomov prueba que las banderas pueden estar ondeando y la operación aún sobrevivir. Las reformas de abajo se tratan de forzar a los indicadores a morder.

Institucionalizar la revalidación continua. La respuesta de la CIA a las quemas de los años ochenta fue el Sistema de Validación de Agentes, desarrollado a partir de 1987 e introducido formalmente al Directorio de Operaciones en 1991 (Mahle 2004; Olson 2019). El principio es sólido y debería ser doctrina en toda la comunidad: las bona fides establecidas una vez no quedan establecidas para siempre. Un activo debe ser recalificado en un calendario recurrente contra los seis métodos clásicos de validación: corroboración por otras fuentes, tareas específicas y pruebas operativas, recolección sobre el activo, polígrafo, penetración de su servicio matriz y vigilancia sobre él. Nada puede asumirse acerca de lo que le ha pasado a una fuente desde la última vez que se probó a sí misma (Orleans 2025; Olson 2019).

Separar al validador del manejador. El oficial que reclutó una fuente y el oficial que la certifica no deberían ser la misma persona, e idealmente no la misma cadena de mando. El hambre es un conflicto de interés; la estructura debe neutralizarlo dándole a una célula de contrainteligencia independiente la autoridad permanente de impugnar cualquier caso, con protección para el analista que disienta. El registro de GTPROLOGUE muestra que el sistema funcionaba a medias. Gerber y Redmond se mantuvieron escépticos y el equipo de contrainteligencia siguió planteando preocupaciones, pero esas preocupaciones fueron repetidamente subordinadas al deseo de no “hacerlo enojar” (Orleans 2025). La disidencia que puede ser anulada por los dueños del caso es un feo adorno de pared.

Tratar “controlado” como una hipótesis permanente por refutar. La disciplina de Richard Heuer del Análisis de Hipótesis en Competencia pertenece al centro de la validación. Enumera las hipótesis (de buena fe, fabricador, controlado), y pesa cada dato por su valor diagnóstico, qué tan bien discrimina entre ellas en lugar de qué tan bien encaja con la respuesta que quieres (Heuer 1999). La mayoría de las “bona fides” de Zhomov eran consistentes tanto con un voluntario genuino como con un señuelo. Tenían un valor diagnóstico casi nulo, y sin embargo se trataron como confirmación. Un activo que sobrevive un esfuerzo deliberado por probar que es hostil vale muchísimo más que uno del que simplemente nunca se dudó en serio.

Privilegiar la penetración de la oposición como el único validador decisivo. Esta es la lección escrita con sangre a lo largo de todos estos casos. A Zhomov lo desenmascaró un desertor, Papushin (Orleans 2025). El engaño cubano lo desenmascaró un desertor, Aspillaga (Latell 2012). Al propio Ames finalmente lo acorralaron con la ayuda de fuentes dentro del FIS ruso. La producción propia de una fuente literalmente nunca resuelve sus bona fides. El interior del servicio del adversario sí. Esto es precisamente por lo que Olson clasifica “Sé Ofensivo” como el primero de sus Diez Mandamientos de la Contrainteligencia. El reclutamiento de penetraciones y el manejo agresivo de agentes dobles no es un lujo sino el motor de la validación misma (Olson 2019).

Diseñar los incentivos contra “el hambre”. Este es, por supuesto, el argumento de calidad sobre cantidad. Si el ascenso premia el volumen de reclutamiento, los oficiales reclutarán, defenderán e inflarán. La contramedida correctiva es una cultura de evaluación de daños en la que sacar a la luz un fabricador o un caso controlado se trate como un éxito profesional y no como una “F”, y en la que el dinero pagado a una fuente se entienda como una inversión operativa, no como un costo hundido que hay que justificar (Orleans 2025).

Mis Reflexiones Finales

Zhomov fue, como concede Orleans, un trabajo sólido. Cada elemento, desde el escenario hasta la alimentación hasta el plan de comunicaciones, fue diseñado para tomar y retener la iniciativa (Orleans 2025). El caso también confirma, sin embargo, una máxima tan vieja como Begoum. La producción por sí sola nunca establece las bona fides, y ninguna métrica individual debería jamás eximir a una fuente del escrutinio continuo, y menos que nada una penetración potencial, que es la cosa más peligrosa de todas si resulta que pertenece al otro bando (Begoum 1962; Orleans 2025). La disciplina no es paranoia, que destruyó los años de Nosenko y casi la vida de Polyakov; ni es el hambre, que le entregó a La Habana un cuarto de siglo de victorias fantasma. Es la disposición a seguir poniendo a prueba a una fuente en la que quieres desesperadamente creer, y a tomar en serio al colega de la mesa que no deja de hacer la pregunta incómoda.

Todo pasa una vez por primera vez, incluido un oficial de planta lanzado como señuelo por un servicio que “nunca” lanzaría un oficial de planta como señuelo. El oficial de contrainteligencia que olvida esa oración está en algún lugar, ya siendo corrido.

~ C. Constantin Poindexter, MA en Inteligencia, Certificado de Posgrado en Contrainteligencia, JD, certificación OSINT CISA/NCISS, Certificación BFFOC del DoD/DoS

Bibliografía

  • Bagley, Tennent H. 2007. Spy Wars: Moles, Mysteries, and Deadly Games. New Haven, CT: Yale University Press.
  • Bearden, Milt, y James Risen. 2003. The Main Enemy: The Inside Story of the CIA’s Final Showdown with the KGB. New York: Random House.
  • Begoum, F. M. 1962. “Observations on the Double Agent.” Studies in Intelligence 6, no. 1: 57–72.
  • Diamond, John. 2008. The CIA and the Culture of Failure: U.S. Intelligence from the End of the Cold War to the Invasion of Iraq. Stanford, CA: Stanford Security Studies.
  • Earley, Pete. 1997. Confessions of a Spy: The Real Story of Aldrich Ames. New York: G. P. Putnam’s Sons.
  • Grimes, Sandra, y Jeanne Vertefeuille. 2012. Circle of Treason: A CIA Account of Traitor Aldrich Ames and the Men He Betrayed. Annapolis, MD: Naval Institute Press.
  • Heuer, Richards J., Jr. 1999. Psychology of Intelligence Analysis. Washington, DC: Center for the Study of Intelligence, Central Intelligence Agency.
  • Johnson, William R. 2009. Thwarting Enemies at Home and Abroad: How to Be a Counterintelligence Officer. Washington, DC: Georgetown University Press.
  • Latell, Brian. 2012. Castro’s Secrets: Cuban Intelligence, the CIA, and the Assassination of John F. Kennedy. New York: Palgrave Macmillan.
  • Mahle, Melissa Boyle. 2004. Denial and Deception: An Insider’s View of the CIA. New York: Nation Books.
  • Masterman, J. C. 1972. The Double-Cross System in the War of 1939 to 1945. New Haven, CT: Yale University Press.
  • Olson, James M. 2019. To Catch a Spy: The Art of Counterintelligence. Washington, DC: Georgetown University Press.
  • Orleans, Alexander. 2025. “Beautiful in Another Context: A Counterintelligence Assessment of GTPROLOGUE.” Studies in Intelligence 69, no. 2 (Extracts, June).
  • Redmond, Paul J. 2010. “The Challenges of Counterintelligence.” En The Oxford Handbook of National Security Intelligence, editado por Loch K. Johnson, 537–54. New York: Oxford University Press.
  • Wise, David. 1992. Molehunt: The Secret Search for Traitors That Shattered the CIA. New York: Random House.
Share this post:

Double Agent Warning Signs: A Counterintelligence Guide

Double Agent Warning Signs: A Counterintelligence Guide, Reading the Dangle: A Practitioner's Field Guide to the Controlled Source and the Reform of Asset Validation. An essay in the voice of a former C.I. guy, intelligence, counterintelligence, espionage, counterespionage, spy, C. Constantin Poindexter, CIA, DIA, NSA, Intelligence Community

Reading the Dangle: A Practitioner’s Field Guide to the Controlled Source and the Reform of Asset Validation. An essay in the voice of a former C.I. guy.

The hardest thing in human intelligence is not recruiting a source. It is knowing whether the source you have recruited belongs to you. Alexander Orleans’s recent open-source reconstruction of the GTPROLOGUE case (the KGB’s 1987 dispatch of staff officer Aleksandr “Sasha” Zhomov against the CIA’s Moscow Station) is the best publicly released anatomy in years of how a hostile service builds, in Churchill’s phrase, a bodyguard of lies around a single operational truth (Orleans 2025). Zhomov was run for roughly three years before the CIA concluded he had been controlled from the first contact. What makes the case instructive is not that the CIA was fooled. That happens to the very best services. It is that the case threw up nearly every classic warning flag. The flags were seen, debated, and the case survived (Orleans 2025; Bearden and Risen 2003).

I am have compiled here a working catalogue of those flags and others drawn from a bit wider literature, each anchored to a real case, followed by the improvements that the counterintelligence mechanism should institutionalize. I have tried to stay as close to actual tradecraft as the open record allows. None of this requires classified access to understand. The painful truth is that the indicators are well known and have been since at least F. M. Begoum’s foundational 1962 Studies in Intelligence treatment of the double agent (Begoum 1962). We keep relearning them, unfortunately.

The Indicators

Production disproportionate to access. The most durable tell is a source who sits on a mountain of secrets but hands you gravel. Zhomov was a First Department staff officer supervising surveillance of the Moscow chief of station, yet he claimed only “peripheral or infrequent access” to the very material his posting should have made routine (Orleans 2025; Grimes and Vertefeuille 2012). The Soviets had a structural reason for this: strict doctrine forbade releasing genuine high-grade feed, and officers feared a Stalin-style reckoning for over-disclosure, so their dangles were trained to plead thin access (Diamond 2008; Earley 1997). When a source’s reporting is consistently and conveniently below the ceiling his placement implies, ask who benefits from the rationing.

The source controls the communications plan and the tempo. Control is the running service’s capacity to start, alter, or stop the agent’s behavior (Begoum 1962). Zhomov arrived with a fully formed, impersonal commo plan, i.e., letter drops through Downing’s unlocked car, contact at Zhomov’s discretion, no extended face-to-face meetings, that placed every lever in KGB hands and even constrained the physical movements of his CIA handlers (Orleans 2025; Bearden and Risen 2003). Compare the gold standard of the opposite arrangement: the British XX Committee in the Second World War, which physically and communicationally owned every German agent in the United Kingdom and therefore could feed Berlin with confidence (Masterman 1972). When the agent dictates the architecture of contact, you are not running him. He is running you.

Motivation that is thin, generic, or unbackstopped. Espionage against one’s own service is a profound psychological act. A credible asset or source can convincingly narrate why he crossed that line, and the story holds up under collateral. Zhomov offered the boilerplate of a souring system and a failing marriage (and the independent debriefing of defector Sergey Papushin flatly contradicted it) describing Zhomov as happily married and devoted to his daughter (Orleans 2025; Grimes and Vertefeuille 2012). A motive that cannot survive a second source is not a motive; it is a legend.

The “too good to be true” arrival. Hostile services read your collection gaps and fill them on cue. Zhomov surfaced precisely when CIA was desperate to explain the catastrophic 1985–86 asset losses, with exactly the access to “explain” them (Orleans 2025). “Too good” and “true” are not mutually exclusive. Genuine walk-ins do occur at the worst possible moment, however, topicality this perfect should raise the burden of proof, not lower it (Johnson 2009). The Cuban debacle is the cautionary monument here. When Major Florentino Aspillaga Lombard defected in Vienna in June 1987, he revealed that essentially every Cuban national CIA believed it had recruited since the early 1960s had been a double agent run by Havana, which had deliberately marketed its officers as Latino amateurs to operate under the radar (Latell 2012). Decades of “successes” were a single, patient deception.

No genuine urgency about exfiltration. A man who says he wants out, and that he is hoarding his best material for his debriefing on safe ground should eventually ask, “When do I leave?” Zhomov never requested a timeline. When he was finally offered an exfiltration route in 1990, he repudiated it as too risky and melted back into his surveillance team (Orleans 2025; Bearden and Risen 2003). The professed defector who never wants to defect is bullshitting, not packing a bug-out bag.

Self-validating bona fides and feed that never truly wounds the parent service. A controlled source builds credibility with material that looks costly but is not. Zhomov handed over an accurate roster of the 1985–86 losses, damaging on its face but wrapped it inside the false “badass infallible SCD” narrative that the losses were due to brilliant Soviet tradecraft rather than a mole (Orleans 2025). The feed validated the channel while protecting the secret the channel existed to protect, Aldrich Ames. Scrutinize whether your source’s “crown jewels” actually cost his service anything, or whether each disclosure quietly advances his service’s interests. To put it into risk language, if it doesn’t represent a peril to the parent service, it’s worthless.

Opposition tradecraft errors inconsistent with claimed competence. Zhomov’s reporting foretold a wave of KGB dangles. The CIA then watched the KGB run them so sloppily that two were blatantly exposed as provocations. Moscow Station rationalized the lapse as endemic Soviet carelessness, never noticing that careless tradecraft was logically irreconcilable with the omniscient SCD Zhomov was boasting (Orleans 2025). A service cannot be simultaneously infallible and sloppy. When the picture that your asset paints contradicts the behavior you observe, believe your eyes.

The denied-area home-field advantage. The environment is itself an indicator because it shapes which other indicators you can even test. The entire Zhomov case unfolded inside Moscow, where the KGB controlled the street, precluded long debriefings, and could refuse any meeting on the unanswerable grounds that he could not evade his own surveillance teams (Orleans 2025). Paul Redmond’s candid summary of denied-area validation, i.e., few or no collateral sources, heavy reliance on the value of the take and on how the case began, etc., describes a problem the opposition deliberately engineers (Redmond 2010). A case born and raised entirely on the adversary’s turf has had its validation options strangled at birth.

Resistance to operational testing, and its scary f* inverse. Zhomov met hard vetting questions with answers his own counterintelligence officers found vague or improbable, and deflected with the promise to tell all after extraction (Orleans 2025; Grimes and Vertefeuille 2012). Reluctance to be tested, i.e., evasion of the polygraph, of provocative taskings, of the “shopping list” designed to catch him out, is itself prescient and instructive. This indicator carries a warning that the GTPROLOGUE case does not supply, and which the profession must internalize. Paranoia burns real sources too. The protracted, brutal handling of Soviet defector Yuri Nosenko as a presumed provocation, and the suspicion that nearly cost CIA the genuinely priceless GRU general Dmitri Polyakov, are the equal-and-opposite pathology of the credulity that protected Zhomov (Bagley 2007; Wise 1992). Validation is calibrated doubt, not a reflex in either direction.

“The hunger,” and the incentives that feed it. Orleans names the quiet culprit, the case officer’s appetite for a spectacular coup, the institutional reluctance to push a glittering source hard enough to lose him (Orleans 2025). Redmond was blunter, attributing post-Angleton validation failures partly to officers who would not believe their own cases could be fabricated, “particularly when promotions were involved” (Redmond 2010). The Cuban catastrophe metastasized in exactly this soil, an organizational will to believe in recruitments that flattered the recruiters (Latell 2012). The most expensive flag is the one we choose not to see because seeing it costs us a career achievement.

What the Counterintelligence Function Should Implement

The indicators are necessary but not sufficient; an agency that merely lists them will still be deceived, because Zhomov’s case proves the flags can be flying and the operation still survive. The reforms below are about forcing the indicators to bite.

Institutionalize continuous revalidation. CIA’s response to the burnings of the 1980s was the Agent Validation System, developed beginning in 1987 and formally introduced to the Directorate of Operations in 1991 (Mahle 2004; Olson 2019). The principle is sound and should be doctrine across the community: bona fides established once are not established forever. An asset must be re-graded on a recurring schedule against all six classical validation methods, i.e., corroboration by other sources, specific taskings and operational testing, collection on the asset, polygraph, penetration of his parent service, and surveillance of him. Nothing can be assumed about what has happened to a source since he last proved himself (Orleans 2025; Olson 2019).

Separate the validator from the handler. The officer who recruited a source and the officer who certifies him should not be the same person, and ideally not the same chain of command. The hunger is a conflict of interest; structure must neutralize it by giving an independent counterintelligence cell standing authority to challenge any case, with protection for the analyst who dissents. The GTPROLOGUE record shows the system was half-working. Gerber and Redmond stayed skeptical and the counterintelligence staff kept raising concerns, but those concerns were repeatedly subordinated to the desire not to “make him mad” (Orleans 2025). Dissent that can be overruled by the case’s owners is ugly wall art.

Treat “controlled” as a standing hypothesis to be disproven. Richard Heuer’s discipline of Analysis of Competing Hypotheses belongs at the center of validation. Enumerate the hypotheses (bona fide, fabricator, controlled), and weigh each datum by its diagnostic value, how well it discriminates between them rather than by how well it fits the answer you want (Heuer 1999). Most of Zhomov’s “bona fides” were consistent with both a genuine volunteer and a dangle. They had near-zero diagnostic value, yet they were treated as confirmation. An asset who survives a deliberate effort to prove him hostile is worth far more than one who was merely never seriously doubted.

Privilege penetration of the opposition as the only decisive validator. This is the lesson written in blood across all these cases. Zhomov was unmasked by a defector, Papushin (Orleans 2025). The Cuban deception was unmasked by a defector, Aspillaga (Latell 2012). Ames himself was ultimately run to ground with the help of sources inside Russian FIS. A source’s own production literally never resolves his bona fides. The inside of the adversary’s service does. This is precisely why Olson ranks “Be Offensive” first among his Ten Commandments of Counterintelligence. The recruitment of penetrations and the aggressive running of double agents is not a luxury but the engine of validation itself (Olson 2019).

Design incentives against ‘the hunger’. This is, of course, the quality over quantity argument. If promotion rewards recruitment volume, officers will recruit, defend, and inflate. The corrective countermeasure is a damage-assessment culture in which surfacing a fabricator or a controlled case is treated as a professional success rather than an “F”, and in which money paid to a source is understood as an operational investment, not a sunk cost that must be justified (Orleans 2025).

My parting thoughts

Zhomov was, as Orleans concedes, solid work. Each element, from setting to feed to commo plan, was engineered to seize and hold the initiative (Orleans 2025). The case also confirms, however, a maxim as old as Begoum. Production alone never establishes bona fides, and no single metric should ever excuse a source from continued scrutiny, least of all a potential penetration, who is the most dangerous thing of all if he turns out to belong to the other side (Begoum 1962; Orleans 2025). The discipline is not paranoia, which destroyed Nosenko’s years and nearly Polyakov’s life; nor is it the hunger, which delivered Havana a quarter-century of phantom victories. It is the willingness to keep testing a source you want desperately to believe in, and to take seriously the colleague at the table who will not stop asking the uncomfortable question.

Everything happens once for the first time, including a staff officer dangled by a service that “would never” dangle a staff officer. The counterintelligence officer who forgets that sentence is somewhere, already being run.

~ C. Constantin Poindexter, MA in Intelligence, Graduate Certificate in Counterintelligence, JD, CISA/NCISS OSINT certification, DoD/DoS BFFOC Certification

Bibliography

  • Bagley, Tennent H. 2007. Spy Wars: Moles, Mysteries, and Deadly Games. New Haven, CT: Yale University Press.
  • Bearden, Milt, and James Risen. 2003. The Main Enemy: The Inside Story of the CIA’s Final Showdown with the KGB. New York: Random House.
  • Begoum, F. M. 1962. “Observations on the Double Agent.” Studies in Intelligence 6, no. 1: 57–72.
  • Diamond, John. 2008. The CIA and the Culture of Failure: U.S. Intelligence from the End of the Cold War to the Invasion of Iraq. Stanford, CA: Stanford Security Studies.
  • Earley, Pete. 1997. Confessions of a Spy: The Real Story of Aldrich Ames. New York: G. P. Putnam’s Sons.
  • Grimes, Sandra, and Jeanne Vertefeuille. 2012. Circle of Treason: A CIA Account of Traitor Aldrich Ames and the Men He Betrayed. Annapolis, MD: Naval Institute Press.
  • Heuer, Richards J., Jr. 1999. Psychology of Intelligence Analysis. Washington, DC: Center for the Study of Intelligence, Central Intelligence Agency.
  • Johnson, William R. 2009. Thwarting Enemies at Home and Abroad: How to Be a Counterintelligence Officer. Washington, DC: Georgetown University Press.
  • Latell, Brian. 2012. Castro’s Secrets: Cuban Intelligence, the CIA, and the Assassination of John F. Kennedy. New York: Palgrave Macmillan.
  • Mahle, Melissa Boyle. 2004. Denial and Deception: An Insider’s View of the CIA. New York: Nation Books.
  • Masterman, J. C. 1972. The Double-Cross System in the War of 1939 to 1945. New Haven, CT: Yale University Press.
  • Olson, James M. 2019. To Catch a Spy: The Art of Counterintelligence. Washington, DC: Georgetown University Press.
  • Orleans, Alexander. 2025. “Beautiful in Another Context: A Counterintelligence Assessment of GTPROLOGUE.” Studies in Intelligence 69, no. 2 (Extracts, June).
  • Redmond, Paul J. 2010. “The Challenges of Counterintelligence.” In The Oxford Handbook of National Security Intelligence, edited by Loch K. Johnson, 537–54. New York: Oxford University Press.
  • Wise, David. 1992. Molehunt: The Secret Search for Traitors That Shattered the CIA. New York: Random House.
Share this post:

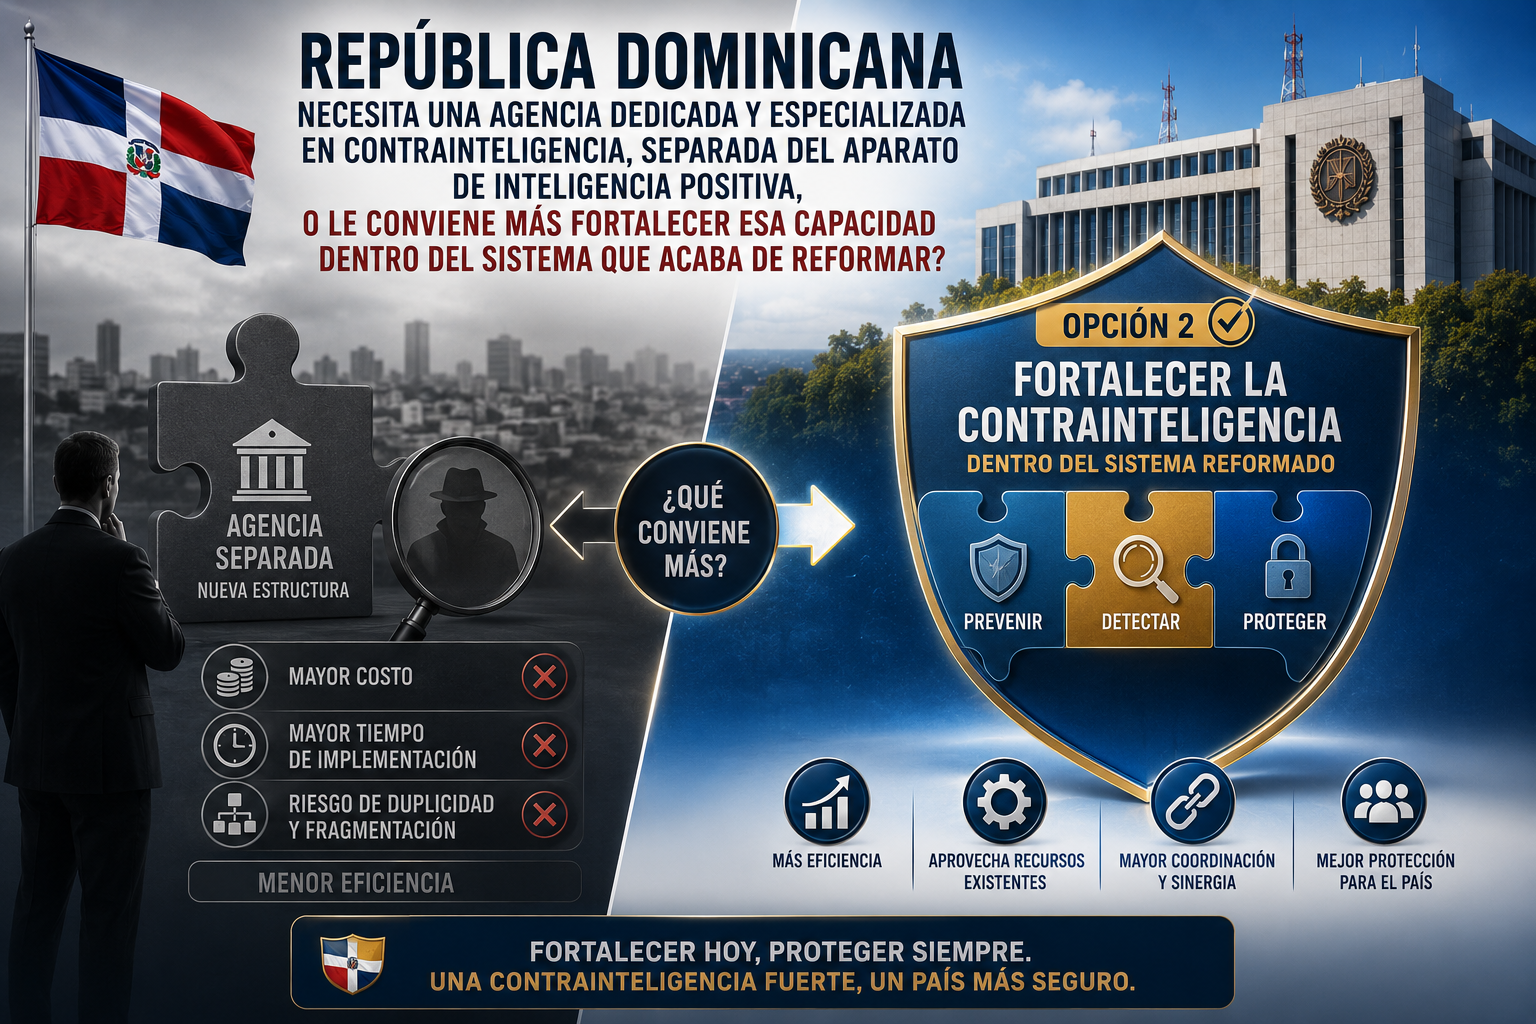
¿Necesita la República Dominicana una Agencia de Contrainteligencia?

contrainteligencia, agencia de contrainteligencia, República Dominicana, Dirección Nacional de Inteligencia, DNI, Sistema Nacional de Inteligencia, Ley 1-26, seguridad nacional, reforma de inteligencia, control democrático de inteligencia, C. Constantin Poindexter Salcedo

El caso por fortalecer el Sistema Nacional de Inteligencia en lugar de crear un nuevo organismo.

La República Dominicana no necesita crear una agencia de contrainteligencia independiente. Lo que necesita es fortalecer y profesionalizar la función de contrainteligencia dentro del Sistema Nacional de Inteligencia que acaba de reformar mediante la Ley Orgánica 1-26 de 2026, bajo la coordinación de la Dirección Nacional de Inteligencia y con controles democráticos verificables. La contrainteligencia ya es un mandato legal vigente: el reto del país es de capacidad y de control, no de arquitectura institucional.

La pregunta sobre si la República Dominicana requiere una agencia de contrainteligencia suele plantearse como si existiera un vacío que llenar. No lo hay. Antes de decidir si conviene crear un organismo nuevo, hace falta reconocer un hecho que reordena por completo el debate. La contrainteligencia dominicana ya posee base legal, mandato expreso y un coordinador formal. La discusión pertinente no es entonces si el Estado debe hacer contrainteligencia, porque la ley ya lo obliga, sino cómo organizar mejor esa función. Y allí la respuesta más prudente apunta a la consolidación, no a la proliferación de agencias.

Punto de partida: la contrainteligencia ya es un mandato legal vigente

La arquitectura de seguridad dominicana acaba de atravesar su transformación más profunda en décadas. Con la promulgación de la Ley Orgánica 1-26, publicada en la Gaceta Oficial núm. 11227 del 13 de enero de 2026, el país sustituyó el antiguo Departamento Nacional de Investigaciones por una Dirección Nacional de Inteligencia (DNI) reestructurada, ahora dependiente del presidente de la República y dotada de autonomía presupuestaria (Congreso Nacional 2026). La norma define a la DNI como órgano rector del Sistema Nacional de Inteligencia (SNI) y le atribuye expresamente la misión de realizar y coordinar actividades de inteligencia y contrainteligencia relacionadas con la seguridad nacional que ejecuten los organismos militares, policiales y financieros del Estado (Congreso Nacional 2026).

Esa redacción no es nueva en su espíritu. Ya la Ley 1-24 de 2024, antecedente directo de la reforma, había creado el SNI y enmarcado la inteligencia y la contrainteligencia como funciones coordinadas del Estado (Congreso Nacional 2024). El sentido de toda la reforma fue precisamente integrar: durante décadas los cuerpos de seguridad dominicanos operaron de manera fragmentada, generando duplicidad de esfuerzos y vacíos de información, y la creación formal del SNI buscó corregir esa dispersión (Redacción Acento 2024). En consecuencia, levantar ahora una agencia de contrainteligencia separada implicaría reintroducir, por la puerta trasera, la fragmentación que el legislador acababa de combatir.

El entorno de amenazas: por qué la contrainteligencia importa, y mucho

Sostener que no conviene una agencia nueva no equivale a minimizar la amenaza. Al contrario: el perfil de riesgo dominicano es exigente y justifica una capacidad de contrainteligencia robusta. El primer vector es el narcotráfico. El Departamento de Estado de los Estados Unidos clasifica a la República Dominicana como país de tránsito primario de la cocaína que cruza el Caribe rumbo a Norteamérica y Europa, y la Determinación Presidencial estadounidense para el año fiscal 2025 la mantiene en la lista de principales países de tránsito de drogas (U.S. Department of State 2025) (The White House 2024).

Lo relevante para la contrainteligencia no es el volumen del flujo, sino el mecanismo que lo sostiene. Las investigaciones de campo muestran que el contrabando por contenedores en puertos como Caucedo depende casi siempre de la complicidad de empleados portuarios: clonar los sellos de seguridad de un contenedor exige acceso a documentación de embarque y a la carga misma, algo imposible sin un infiltrado interno (InSight Crime 2024). El mismo Departamento de Estado vincula las limitaciones del país a la corrupción endémica y a las restricciones de capacidad institucional (U.S. Department of State 2025). La penetración y la corrupción de funcionarios de seguridad por parte de organizaciones criminales transnacionales es, por definición, el terreno propio de la contrainteligencia: proteger las instituciones del Estado frente a su captura desde dentro.

El segundo vector es el espionaje, estatal y económico. Tras el cambio de reconocimiento diplomático de Taiwán a la República Popular China en 2018, la República Dominicana quedó expuesta a una relación asimétrica con una potencia que despliega capacidades de influencia e inteligencia. La ambigüedad del gobierno dominicano respecto del papel de Huawei en su red 5G ilustra esa vulnerabilidad, sobre todo en infraestructura crítica de telecomunicaciones (Ellis 2022). A ello se suman la frontera con Haití, foco de inestabilidad y de actores que operan a través de ese flanco, y la dimensión cibernética, que la propia Ley 1-26 incorpora al asignar a la DNI tareas de seguridad de las infraestructuras críticas (Congreso Nacional 2026). La conclusión provisional es clara: el país necesita contrainteligencia de verdad. La discusión es sobre el envase, no sobre el contenido.

El argumento contrario: la tentación de una agencia especializada

Existe un razonamiento serio a favor de crear un organismo dedicado, y conviene exponerlo con honestidad. La contrainteligencia es una disciplina distinta de la inteligencia positiva. Mientras esta recolecta y analiza información sobre amenazas externas, aquella se ocupa del contraespionaje, de la amenaza interna, de la protección de secretos de Estado y de la depuración de personal. Cuando ambas conviven bajo el mismo techo, la experiencia comparada sugiere que la contrainteligencia suele quedar subordinada a las prioridades de recolección y se atrofia. Una entidad con mandato propio acumularía experticia especializada y reduciría el conflicto de interés que surge cuando quien recolecta es también quien se vigila a sí mismo. En la literatura clásica de reforma de inteligencia este principio de separación entre el cazador y el guardabosque es un argumento recurrente a favor de la diferenciación funcional (Bruneau y Boraz 2007).

El argumento tiene mérito. Pero confunde dos cosas distintas: la necesidad de especialización con la necesidad de un organismo separado. Se puede lograr lo primero sin incurrir en los costos de lo segundo. Y para un Estado de los recursos y la trayectoria institucional de la República Dominicana, los costos de lo segundo son considerables.

Capacidad y diseño: por qué la consolidación supera la creación de un nuevo organismo

El primer costo es presupuestario y de talento humano. Construir una agencia desde cero exige una nómina propia, una cadena de mando autónoma, instalaciones, sistemas y, sobre todo, personal formado en una disciplina escasa en el mercado regional. Para un país de capacidad institucional limitada, el retorno de invertir en una nueva burocracia es previsiblemente inferior al de reforzar la capacidad de contrainteligencia dentro del sistema que acaba de crearse, dotándolo de cuadros, tecnología y procedimientos. Somos un país pequeño con presupuesto limitado. Aunque un mecanismo de contrainteligencia independiente sería la utopía, vivimos en un mundo real.

El segundo costo es de coherencia. La experiencia latinoamericana de reforma de inteligencia ofrece un punto de comparación útil. Brasil, al reconstruir su sistema tras el régimen militar, optó por priorizar el análisis y la contrainteligencia de alcance doméstico privilegiando instituciones civiles, con una estructura distribuida entre múltiples organismos coordinados centralmente por la Agencia Brasileña de Inteligencia (ABIN) (Bruneau y Matei 2010). El rasgo dominante de esa reforma fue estructural y de coordinación, no la multiplicación de agencias autónomas (Cepik 2007). La lección para Santo Domingo es directa. La coordinación de una estructura distribuida, que es exactamente lo que el SNI dominicano pretende ser, resuelve mejor el problema de la dispersión que la creación de un nuevo actor que reclame su propia parcela de poder.

El riesgo decisivo: control democrático y el legado autoritario

El argumento más fuerte contra una agencia de contrainteligencia independiente no es presupuestario ni organizativo, sino político. De todas las funciones de inteligencia, la contrainteligencia es la más propensa a desbordarse hacia la vigilancia interna de la prensa, la oposición y la sociedad civil. Quien tiene el mandato de detectar la penetración del Estado posee también, casi por la misma vía, las herramientas para espiar a los ciudadanos. Concentrar ese poder en un organismo secreto, separado y con cadena de mando propia es precisamente la receta que la historia dominicana enseña a temer.

La memoria institucional pesa. El aparato de inteligencia dominicano nació como instrumento de represión durante la dictadura de Trujillo y se prolongó en las redes de vigilancia de las décadas posteriores, una herencia que la literatura sobre culturas de inteligencia en América Latina y el Caribe documenta como un lastre que las reformas democráticas aún no terminan de superar (Matei, Halladay y Estévez 2022). Esa preocupación no es solo histórica. Durante el trámite legislativo de la reforma, la Sociedad Dominicana de Diarios advirtió que ciertos artículos de ambigua redacción, en particular la obligación de toda persona e institución de entregar información a la DNI, podían representar un riesgo para la libertad de prensa y la privacidad (Redacción Acento 2024).

La literatura comparada confirma el peligro. En las democracias nuevas, los organismos de inteligencia tienden a resistir el control externo, amparados en el secreto de su oficio y en la falta de expertise de los supervisores políticos, y esa resistencia puede obedecer al deseo de perpetuar prácticas abusivas en nombre de la eficacia (Bruneau y Matei 2010). El propio caso brasileño, pese a su reforma modélica, mostró señales de que su agencia coordinadora reincidía en la lógica de policía política (Cepik 2007). Si un sistema reformado y centralizado ya enfrenta esa tentación, una agencia de contrainteligencia autónoma, con menos contrapesos y mayor opacidad, la multiplicaría.

El verdadero riesgo no es que la República Dominicana carezca de contrainteligencia, sino que construya un instrumento que termine protegiendo al gobierno de turno más que al Estado.

Recomendaciones: especializar dentro del sistema, no fuera de él

De lo anterior se desprende una vía intermedia que captura los beneficios de la especialización sin asumir los riesgos de la fragmentación y la concentración de poder. En primer lugar, la contrainteligencia debe alojarse como una dirección o subdirección especializada dentro de la DNI, con mandato, doctrina y personal propios, pero subordinada a la coordinación única del Sistema Nacional de Inteligencia. La especialización se logra por diseño funcional, no por separación institucional.

En segundo lugar, esa unidad debe concentrarse en tres prioridades verificables: el blindaje de las instituciones del Estado frente a la penetración del narcotráfico y el crimen organizado; el contraespionaje frente a actores estatales con presencia creciente en el país; y la protección de la infraestructura crítica y de los secretos del Estado, incluida la dimensión cibernética. La seguridad del personal y la verificación de antecedentes, que el reglamento de la Ley 1-26 ya contempla, son piezas centrales de esa función.

En tercer lugar, y de manera no negociable, la capacidad de contrainteligencia debe quedar enmarcada en controles democráticos reales: supervisión judicial de las medidas intrusivas, control parlamentario efectivo, un inspector general con dientes, límites explícitos a la vigilancia doméstica y plazos razonables de reserva de la información. La eficacia y el control democrático no son objetivos en tensión, sino las dos caras de un servicio de inteligencia maduro (Bruneau y Boraz 2007). Un servicio sin control pierde legitimidad y, con ella, la cooperación ciudadana de la que depende su eficacia.

Mis pensamientos finales

La República Dominicana enfrenta amenazas que hacen de la contrainteligencia una necesidad estratégica, no un lujo. Pero la respuesta institucionalmente (y presupuestaria) correcta a esa necesidad no es un nuevo organismo con letrero propio, sino una capacidad de contrainteligencia seria, profesionalizada y bien acotada, alojada dentro de la arquitectura que la Ley 1-26 acaba de levantar. Opino que crear una agencia separada deshacería el esfuerzo de consolidación que inspiró la reforma, gravaría a un Estado de recursos limitados con una burocracia adicional y, sobre todo, concentraría en un cuerpo opaco el tipo de poder que la propia historia dominicana enseña a vigilar. Fortalecer el Sistema Nacional de Inteligencia, y dentro de él la función de contrainteligencia, es la opción que mejor sirve a la vez a la seguridad nacional y a la democracia que esa seguridad debe proteger.

~ C. Constantin Poindexter Salcedo, Maestría en Inteligencia, Certificado de Posgrado en Contrainteligencia, J.D., certificación CISA/NCISS OSINT, Certificación U.S. DoD/DoS BFFOC, Dipl. Diplomacia Global, Dipl. Derechos Humanos por USIDHR, Dipl. Negociación Diplomática por Harvard

Bibliografía

  • Bruneau, Thomas C., y Steven C. Boraz, eds. 2007. Reforming Intelligence: Obstacles to Democratic Control and Effectiveness. Austin: University of Texas Press.
  • Bruneau, Thomas C., y Florina Cristiana Matei. 2010. «Intelligence in the Developing Democracies: The Quest for Transparency and Effectiveness». En The Oxford Handbook of National Security Intelligence, editado por Loch K. Johnson, 757 a 773. Oxford: Oxford University Press.
  • Cepik, Marco. 2007. «Structural Change and Democratic Control of Intelligence in Brazil». En Reforming Intelligence: Obstacles to Democratic Control and Effectiveness, editado por Thomas C. Bruneau y Steven C. Boraz. Austin: University of Texas Press.
  • Congreso Nacional de la República Dominicana. 2024. Ley núm. 1-24 que crea la Dirección Nacional de Inteligencia (DNI) y regula el Sistema Nacional de Inteligencia. Gaceta Oficial. Santo Domingo.
  • Congreso Nacional de la República Dominicana. 2026. Ley Orgánica núm. 1-26 que crea la Dirección Nacional de Inteligencia (DNI) y regula el Sistema Nacional de Inteligencia. Gaceta Oficial núm. 11227, 13 de enero. Santo Domingo.
  • Ellis, R. Evan. 2022. «Chinese Engagement with the Dominican Republic: An Update». Análisis sobre relaciones China a América Latina. revanellis.com.
  • InSight Crime. 2024. «The Dominican Republic: The Caribbean’s Cocaine Hub». Investigación de InSight Crime.
  • Matei, Florina Cristiana, Carolyn Halladay y Andrés de Castro Estévez, eds. 2022. The Handbook of Latin American and Caribbean Intelligence Cultures. Lanham: Rowman & Littlefield.
  • Redacción Acento. 2024. «Ejecutivo promulga la ley que crea la Dirección Nacional de Inteligencia». Acento, 18 de enero.
  • The White House. 2024. «Presidential Determination on Major Drug Transit or Major Illicit Drug Producing Countries for Fiscal Year 2025» (Presidential Determination núm. 2024-12). Federal Register, 24 de septiembre.
  • U.S. Department of State. 2025. International Narcotics Control Strategy Report (INCSR), Volume I: Drug and Chemical Control. Washington, D. C.: Bureau of International Narcotics and Law Enforcement Affairs.
Share this post:

Deliberate Disarmament: How the United States is Systematically Dismantling its Disinformation Defenses

disinformation, information warfare, grey zone, influence operations, Russian FIS, psyops, intelligence, counterintelligence, DIA, CIA, NSA;

In the contemporary geopolitical landscape, the battle against disinformation has emerged as a critical front in maintaining national security and democratic integrity. It is hybrid warfare, plain and simple, . . . offensive operations in the “grey zone” the theorists like to call it. The United States has been systematically and purposefully disarming itself in this information warfare through a series of policy decisions and institutional changes that constitute nothing less than a strategic surrender. By examining the dismantling of counter-disinformation agencies, reduction of international alliances, constraints on broadcasting capabilities, prioritization of tech deregulation, and the purging of experienced intelligence personnel, my thoughts here demonstrate how these actions collectively represent a deliberate retreat rather than a mere series of isolated administrative changes. I am also going to share here my opinion on the implications of this unilateral disarmament for U.S. national security interests and the broader information ecosystem, concluding with a stark assessment of America’s vulnerability in an era of escalating information warfare.

The information environment has become a critical domain of modern warfare, where adversaries can achieve strategic objectives without firing a single shot. Russia’s 2026 budget allocation of $1.77 billion for propaganda efforts, supplemented by covert troll farms, front organizations, and cyber operations, demonstrates the seriousness with which state actors approach information warfare (Geraghty, 2026). Against this backdrop of escalating adversarial investment, the United States has paradoxically moved in the opposite direction, systematically dismantling its counter-disinformation infrastructure and capabilities in what can only be described as a deliberate act of strategic self-immolation.

My blog essay here examines how the United States has unilaterally disarmed itself in the information war through a series of deliberate policy choices that extend beyond mere administrative inefficiency to constitute a comprehensive strategic withdrawal. The evidence suggests this represents a fundamental recalibration of America’s approach to information warfare with profound and deeply troubling implications for national security. By examining the various dimensions of this disarmament, from institutional dismantling to personnel purges, we can better understand the emerging vulnerabilities in America’s information defenses and the strategic vacuum being created for adversaries to exploit.

The Systematic Dismantling of Counter-Disinformation Infrastructure

The most striking example of America’s unilateral disarmament in the information war is the systematic dismantling of its counter-disinformation infrastructure. The Trump administration has implemented policies that effectively prohibit federal agencies from combating misinformation or disinformation not tied to criminal activity, barring efforts that had previously been central to America’s information defense strategy (Nurick, 2026). This policy shift represents a fundamental reorientation of federal priorities away from proactive counter-disinformation work toward a reactive posture that only addresses disinformation when it rises to the level of criminal activity, a threshold that most sophisticated influence operations never cross.

The impact of this policy shift has been particularly devastating for agencies that had developed specialized expertise in tracking and countering foreign influence operations. The Global Engagement Center (GEC) at the State Department, which had been at the forefront of exposing Russian, Chinese, and Iranian disinformation campaigns, has seen its mandate severely constrained. Similarly, the Cybersecurity & Infrastructure Security Agency’s “Mis-, Dis-, and Malinformation Resource Library” has been effectively sidelined as part of a broader effort to scrub references to “misinformation” and “disinformation” from technical documents and official communications (Nurick, 2026). This linguistic cleansing reflects a deeper ideological opposition to the very concept of counter-disinformation as a legitimate government function.

Perhaps most alarmingly, the Trump administration has moved to politicize the research funding process that underpins America’s ability to understand and counter disinformation. A recent proposal would give political appointees at federal science agencies the role of approving all scientific research awards, replacing the traditional merit-based system determined by apolitical expert scientists (Lofgren, 2026). As Ranking Member Zoe Lofgren has warned, this move “would destroy what remains of merit-based review, dealing a crippling blow to science” and specifically targets research on topics deemed “politically inconvenient” (Lofgren, 2026). This politicization of research funding effectively ensures that studies of foreign disinformation campaigns and their effects will be starved of resources, leaving America blind to the very threats it should be countering.

The Purging of Expertise and Institutional Knowledge

The deliberate disarmament of America’s counter-disinformation capabilities extends beyond institutional structures to include the systematic purging of experienced personnel from key agencies. The Trump administration has targeted career intelligence analysts and counter-disinformation specialists for removal, replacing them with political loyalists lacking the specialized expertise necessary to understand and counter sophisticated influence operations. This personnel purging represents perhaps the most damaging aspect of America’s unilateral disarmament, as it destroys institutional knowledge that cannot be quickly rebuilt.

The impact of these personnel losses is particularly acute in the counterintelligence domain, where understanding adversary tactics and intentions requires years of specialized experience and the development of deep analytic tradecraft. The departure of these experts has left critical gaps in America’s ability to detect and counter foreign influence operations, creating vulnerabilities that adversaries have been quick to exploit. Even more troubling, the administration has attempted to require all current and future federal employees to sign loyalty oaths that effectively prioritize political alignment over professional expertise (PBS NewsHour, 2026). This approach ensures that the remaining counter-disinformation capabilities will be staffed by personnel selected for their political reliability rather than their analytic acumen.

The personnel purges have also disrupted the continuity of counter-disinformation efforts and severed critical professional networks. Many of the departed officials had developed deep expertise in specific adversary approaches and maintained professional relationships with their counterparts in other countries. Their departure has not only eliminated this expertise from government service but has also disrupted these critical networks and relationships, further isolating the U.S. from the broader counter-disinformation community. This isolation is particularly damaging given the transnational nature of modern influence operations, which require coordinated multinational responses to be effectively countered.

The Strategic Withdrawal from International Information Partnerships

The U.S. retreat from counter-disinformation extends beyond domestic institutions to include the weakening of international alliances and partnerships that had proven effective in combating foreign influence operations. The Trump administration’s “America First” approach has systematically undermined the collaborative frameworks that had been developed to share information about disinformation campaigns and coordinate responses across borders. This withdrawal from international partnerships represents a strategic miscalculation that leaves both the United States and its allies more vulnerable to foreign influence operations.

The impact of this withdrawal is already visible in the declining effectiveness of multinational initiatives like the EU vs Disinfo program and NATO’s strategic communications center, which had worked closely with U.S. agencies to expose Russian and Chinese influence operations. Without U.S. leadership and intelligence support, these partnerships have struggled to maintain their effectiveness against increasingly sophisticated adversaries. This is particularly damaging for smaller nations that lack the resources to develop their own counter-disinformation capabilities and have relied on U.S. support to counter foreign influence operations.

The strategic withdrawal from international partnerships is particularly concerning given the evolving nature of modern influence operations. As Russia, China, and other state actors have developed more sophisticated approaches to information warfare, they have increasingly targeted not just the United States but its allies and partners as well. By withdrawing from these partnerships, the United States has not only isolated itself but has also left its allies more vulnerable to influence operations that ultimately serve to undermine the broader Western alliance system. This strategic withdrawal represents a failure to recognize that information warfare is fundamentally a transnational threat that requires coordinated multinational responses.

The Constraining of Broadcasting and Public Diplomacy Capabilities

The constraints on Voice of America (VOA) and other international broadcasters represent a particularly damaging form of unilateral disarmament. These services had developed sophisticated approaches to reaching audiences in closed societies, often at great risk to their local partners and journalists. By providing independent news and information to audiences that otherwise lack access to unbiased reporting, these broadcasters served as a critical counterweight to state-sponsored propaganda and an important tool of public diplomacy.

The Trump administration has systematically undermined these broadcasting capabilities through budget cuts, leadership changes, and policy directives that have effectively neutered their ability to fulfill their missions. The administration has instructed managers to “reduce performance, . . . to the minimum presence and function required by law,” effectively gutting these organizations’ ability to conduct meaningful public diplomacy (Nurick, 2026). This approach stands in stark contrast to the investments being made by adversaries like Russia, which has expanded its RT network (a known Russian FIS propaganda channel forced to register as a foreign agent) from a traditional broadcaster to an entity with sophisticated cyber capabilities that conducts information operations and covert influence activities worldwide.

The constraining of U.S. broadcasting capabilities is particularly damaging in the context of modern authoritarianism, which increasingly relies on controlling information environments to maintain power. By limiting the ability of U.S. broadcasters to reach these audiences, the United States has effectively abandoned one of its most effective tools for supporting democratic aspirations and countering state propaganda. This retreat is particularly ironic given that these same broadcasters had been instrumental in countering Soviet propaganda during the Cold War—a historical precedent that suggests their current value should be recognized rather than diminished.

The Prioritization of Tech Deregulation Over Information Security

Another dimension of America’s unilateral disarmament in the information war is the prioritization of tech deregulation over information security. While private technology platforms have become the primary battleground for influence operations, the U.S. has moved toward reducing oversight rather than strengthening it. This approach reflects a fundamental misunderstanding of the role that technology platforms play in modern information warfare and the responsibility that both government and industry share for protecting the information ecosystem.

The Trump administration has consistently opposed regulation of technology platforms, even as evidence mounts that these platforms are being exploited by foreign actors to conduct influence operations. This deregulatory approach stands in stark contrast to the recognition by previous administrations that technology platforms play a critical role in both the dissemination of accurate information and the propagation of disinformation. By prioritizing deregulation over information security, the United States has effectively surrendered one of its most potent tools for countering foreign influence operations.

The impact of this deregulatory focus is particularly concerning given the evolving tactics of foreign influence operations. As state actors have developed more sophisticated approaches to information warfare, they have increasingly exploited the vulnerabilities of technology platforms to conduct influence operations at scale. Without adequate oversight and cooperation between government and technology companies, these platforms remain vulnerable to manipulation by foreign actors. The U.S. approach of prioritizing deregulation over information security effectively ensures that these vulnerabilities will remain unaddressed, creating significant opportunities for adversaries to exploit.

The Strategic Implications of Unilateral Disarmament

The cumulative effect of these various dimensions of unilateral disarmament is a significant reduction in America’s ability to compete in the information environment. This retreat has several deeply troubling strategic implications that extend beyond immediate tactical considerations to fundamental questions about America’s ability to protect its interests in an era of information warfare.

Unilateral disarmament creates asymmetries that adversaries can exploit with increasing effectiveness. While Russia, China, and other state actors continue to invest heavily in influence operations—with Russia alone allocating $1.77 billion to propaganda efforts in its 2026 budget—the United States has reduced its capabilities to counter these activities (Geraghty, 2026). This imbalance allows adversaries to shape narratives and influence public opinion with minimal resistance, creating strategic opportunities that they are already exploiting to advance their interests at America’s expense.

The U.S. withdrawal undermines the credibility of its commitments to allies and partners. The inability or unwillingness to maintain counter-disinformation capabilities raises questions about America’s reliability as a security partner, particularly for nations facing intense information warfare campaigns from adversaries. This credibility gap has already begun to reshape alliance dynamics, with some partners questioning whether they can count on U.S. support in the face of foreign influence operations. These doubts have broader implications for alliance cohesion and the ability of the United States to lead collective responses to shared security challenges.

Unilateral disarmament erodes America’s ability to protect its own democratic institutions from foreign influence. As foreign disinformation campaigns aim to “manipulate and weaken adversaries” through tactics designed to “discredit, divide, disarm, and demoralize them,” the United States becomes increasingly vulnerable to these influence operations (Geraghty, 2026). The January 6th Capitol attack and subsequent events have demonstrated how effectively foreign influence operations can exploit existing divisions within American society, a vulnerability that will only grow as counter-disinformation capabilities continue to be dismantled.

The Ideological Dimensions of the Disarmament Strategy

Perhaps most troubling about America’s unilateral disarmament in the information war is the ideological dimension that underlies these policy choices. The systematic dismantling of counter-disinformation capabilities appears to be driven not by pragmatic considerations of effectiveness or efficiency but by a fundamental ideological opposition to the very concept of government involvement in countering disinformation. This ideological opposition manifests in policies that prioritize political loyalty over expertise, deregulation over security, and isolation over cooperation.

The ideological dimensions of this disarmament strategy are particularly evident in the Trump administration’s approach to research funding and scientific expertise. By seeking to place political appointees in control of research funding decisions, the administration has demonstrated a preference for politically convenient narratives over evidence-based analysis (Lofgren, 2026). This approach extends to the very language used to discuss information warfare, with terms like “misinformation” and “disinformation” being systematically scrubbed from official documents and communications (Nurick, 2026). This linguistic cleansing reflects a deeper ideological opposition to acknowledging the existence and threat of foreign influence operations.

The ideological dimensions of the disarmament strategy are also evident in the administration’s approach to international partnerships and alliances. The systematic withdrawal from multinational counter-disinformation initiatives reflects not just a pragmatic assessment of costs and benefits but a deeper ideological opposition to collective approaches to security challenges. This “America First” approach assumes that the United States can effectively address information warfare threats on its own, despite abundant evidence to the contrary. This ideological isolationism leaves America more vulnerable to influence operations while simultaneously undermining the collective security architecture that had been developed to counter these threats.

The Path to Strategic Vulnerability

The evidence that I have presented in this piece demonstrates that the United States has been systematically and purposefully disarming itself in the war on disinformation. Through the dismantling of counter-disinformation agencies, cutting of international alliances, constraints on broadcasting capabilities, prioritization of tech deregulation, banning of funding for independent researchers, and purging of experienced intelligence personnel, the U.S. has created significant vulnerabilities in its information defenses.

This unilateral disarmament is particularly concerning given the escalating investments by adversaries in influence operations. As Russia’s 2026 budget allocation of $1.77 billion for propaganda efforts demonstrates, state actors are increasingly viewing the information environment as a critical domain of warfare (Geraghty, 2026). The U.S. retreat from this domain represents not just a strategic miscalculation but a deliberate surrender with profound implications for national security and the future of democratic governance.

Reversing this unilateral disarmament will require more than simply restoring previous programs and initiatives. It will require a fundamental reorientation of America’s approach to information warfare. This must include rebuilding counter-disinformation capabilities, restoring international partnerships, redeveloping expertise in countering foreign influence operations, and most importantly, rejecting the ideological opposition to government involvement in countering disinformation. Until such efforts are undertaken, the United States will remain at a significant disadvantage in the information environment, unable to effectively counter the sophisticated influence operations being conducted by its adversaries.

The stakes in this information war could not be higher. As foreign actors continue to exploit America’s self-inflicted vulnerabilities, the very foundations of democratic governance are at risk. The unilateral disarmament of America’s counter-disinformation capabilities represents not just a strategic retreat but a betrayal of the government’s fundamental responsibility to protect the nation from foreign threats, both conventional and informational, and both foreign and domestic. So pronounced is the betrayal that experienced elements in the U.S. Intelligence Community, addressing the malign information operations of Russian FIS as an example, have stated clearly, “We couldn’t do a worse job if Putin himself was sitting in the White House and giving orders.” Without a course correction, the United States will continue to cede the information environment to its adversaries, with consequences that will reverberate for generations to come.

~ C. Constantin Poindexter, MA in Intelligence, Graduate Certificate in Counterintelligence, JD, CISA/NCISS OSINT certification, DoD/DoS BFFOC Certification

Bibliography

  • Geraghty, Jim. 2026. “In the disinformation war, the U.S. unilaterally disarmed.” The Washington Post, May 26.
  • Lofgren, Zoe. 2026. “Ranking Member Lofgren Slams Trump Administration for Plan to Politicize Research Funding Process, Undermine Expert Review.” House Committee on Science, Space, and Technology Democrats, May 29.
  • Nurick, Jacob K. 2026. “The Trump administration’s goals, outlined in Project 2025, were to weaken federal…” Facebook post, April 15.
  • PBS NewsHour. 2026. “The Trump administration wants all current and future federal…” Facebook post, March 22.
  • Myers, Steven Lee. 2026. “Trump Officials Try to Fight Foreign Disinformation They Once…” The New York Times, April 1.

Share this post:

El barril que nos cae encima: qué debe hacer Abinader

El barril que nos cae encima qué debe hacer Abinader, Crisis petrolera República Dominicana 2026, factura energética dominicana, guerra Irán impacto Caribe, medidas económicas Abinader petróleo, dependencia hidrocarburos RD, transición energética Dominicana, estrecho de Ormuz Caribe, subsidio combustibles dominicano, C. Constantin Poindexter Salcedo;

El barril que nos cae encima: lo que el presidente Abinader tiene que hacer ya para salvarnos del despelote petrolero provocado por Washington.

La guerra que Estados Unidos e Israel desataron contra Irán le va a costar a la República Dominicana unos US$900 millones adicionales en factura petrolera este año 2026, llevando el total a cerca de US$5,400 millones, según un análisis del Banco Central de la República Dominicana (BCRD 2026). Vean, . . . “República Dominicana pagará 900 millones de dólares más en petróleo por la guerra en Irán” (el Día), “Guerra en Irán le costará a RD 900 millones de dólares y una inflación elevada” (TeleNord), “Guerra de Irán golpea a RD: Cobijar la economía ante crisis” (El Nacional), “República Dominicana ante difícil escenario por la guerra en Irán” (el País), y la mala noticia del sacude del bolsillo dominicano no acaba. Otro gran error del sátrapa del país vecino mierda coño, un tamaño dolor impuesto por una guerra ilegal. Mi ensayo aquí plantea una explicación corta y sin paños tibios del enredo en que nos metieron, y dedica el grueso de su extensión a las medidas concretas, ejecutables y verificables que el Poder Ejecutivo debe poner en marcha para amortiguar el daño mientras se estabilizan los mercados internacionales.

Les voy a decir algo claro. La República Dominicana no fabrica un solo barril de petróleo. Compramos prácticamente todo lo que quemamos, desde la gasolina que mueve el carro hasta el GLP con el que la doña en Capotillo cocina el sancocho del domingo. De acuerdo con cifras de la Dirección General de Aduanas recogidas por Diario Libre (2026a), en 2025 el país importó hidrocarburos por US$4,685.63 millones, y aproximadamente el 89 % de las necesidades energéticas nacionales se cubren con combustibles fósiles importados (AlMomento 2026). Esa es una vulnerabilidad estructural de primer orden, la cual ha sido documentada por economistas y consultores energéticos durante décadas sin que se haya hecho lo suficiente al respecto.

Entonces llega el señor de la Casa Blanca, con esa retórica de cowboy soplón que ya cansa al mundo, y decide junto a Israel atacar a Irán. Un berrinche imperial, hablando sin filtros. Irán responde cerrando el estrecho de Ormuz desde el 28 de febrero, por donde transitaba alrededor del 20 % del petróleo y gas mundial antes del conflicto (BCRD 2026), y el precio del barril se va a casi US$100, cuando el Presupuesto Nacional 2026 dominicano se elaboró con un barril a US$65 (Presidencia de la República Dominicana 2026). La aritmética es brutal: cada dólar que sube el barril, los dominicanos lo pagamos en la bomba, en la factura de la luz, en el pasaje del público, en el plato de comida. Y todo porque a un señor que ni siquiera sabe ubicar Santo Domingo en un mapa le dio por jugar a Rambo en el Golfo Pérsico. Aquí en la media isla nadie votó por esa guerra, nadie firmó ese cheque, y sin embargo nos están pasando la cuenta como si fuéramos cómplices del despelote.

La inflación interanual dominicana llegó al 5.11 % en abril de 2026, por encima del rango meta de 4 % ± 1 % del Banco Central (BCRD 2026). Diario Libre (2026b) reporta que la institución emisora proyecta que la inflación podría empujar por encima del 5 % entre el segundo y tercer trimestre, alcanzando su pico en este último período. Mientras tanto, las reservas internacionales se mantienen sobre los US$15,800 millones, lo cual da cierto margen de maniobra, pero no es plata infinita.

Habiendo dicho lo anterior, el lloriqueo no resuelve nada. Toca actuar, y toca actuar ya. Luis Abinader tiene sobre el escritorio una agenda de emergencia que debe ejecutar sin titubeos, porque cuando el barril baje y los mercados se normalicen, lo único que va a quedar es lo que hayamos construido en este apretón. Veamos qué debe pasar.
Subsidio focalizado, no regalo populista

El gobierno ha venido subsidiando combustibles a un ritmo significativo. En 2025 se destinaron RD$11,500 millones a subsidios de combustibles y más de RD$105,000 millones al sector eléctrico, mientras que en lo que va de 2026 el subsidio al combustible ya asciende a unos RD$4,000 millones (Presidencia de la República Dominicana 2026). El problema con los subsidios generalizados es que terminan beneficiando proporcionalmente más a quien echa gasolina premium en la Yipeta del año que a la señora que llena un solo galón para la motoconcho.

La medida correcta es lo que Abinader ya empezó a esbozar, pero debe profundizar: mantener congelado el precio del GLP, que es el combustible de los hogares más vulnerables, y aplicar ajustes graduales del 5.2 % al 6.7 % en los demás derivados (Diario Libre 2026c). Sin embargo, eso no basta. Hay que crear un bono de combustible directo, transferido vía la Tarjeta Supérate, para conductores del transporte público y para hogares clasificados en el Índice de Calidad de Vida en los niveles ICV 1 y ICV 2. Esto significa enfocar el subsidio donde duele, no regarlo como agua bendita.

Reasignación presupuestaria sin tocar gasto social

El propio presidente anunció que ya se identificaron cerca de RD$10,000 millones que pueden reasignarse desde partidas menos prioritarias hacia la mitigación del choque petrolero, sin aumentar el gasto total (Presidencia de la República Dominicana 2026). Esto va por buen camino, pero hay que ir más lejos. Toca poner la tijera en la publicidad oficial, los viajes no esenciales del funcionariado, las consultorías recicladas y las nóminas paralelas en las instituciones autónomas. Esa plata existe y todo el mundo sabe dónde está. Si Washington nos puso esta vaina arriba, que al menos el ajuste empiece por la grasa del Estado y no por el bolsillo de la gente.

Acelerar la matriz renovable de una buena vez

El Plan Energético Nacional dominicano tiene como meta alcanzar al menos un 30 % de participación renovable en la matriz (Acento 2026). Llevamos años hablando de eso. Mientras tanto, el sol nos cae todo el día gratis y el viento sopla en Pedernales sin que nadie le cobre IVA. La crisis actual es la excusa perfecta para que el presidente firme un decreto de emergencia que agilice todos los permisos pendientes de parques solares y eólicos, que reduzca a 90 días los plazos de aprobación ambiental sin saltarse la rigurosidad técnica, y que ordene al CDEEE acelerar la incorporación al sistema interconectado de los proyectos ya licitados.

El consultor en energía Marvin Fernández, citado por Acento (2026), ha advertido que los subsidios a combustibles fósiles tienden a perpetuar la dependencia y retrasan el cambio estructural hacia una matriz más sostenible. Por eso cada peso que el Estado dominicano gaste de aquí en adelante subsidiando hidrocarburos debe ir acompañado de un peso equivalente, como mínimo, invertido en infraestructura renovable.

Diversificar suplidores y reducir la dependencia del mercado estadounidense

Del enero a septiembre de 2025, Estados Unidos concentró el 81.8 % de las importaciones dominicanas de combustibles, equivalente a US$2,863.5 millones (Acento 2026). Hay una ironía amarga aquí: el país que nos generó la crisis es a la vez nuestro principal suplidor. El presidente Abinader debe ordenar a la Refinería Dominicana de Petróleo y al Ministerio de Industria, Comercio y MiPymes una hoja de ruta de diversificación que incluya acuerdos de suministro con Brasil, Colombia, Guyana y otros productores regionales del hemisferio. No se trata de pelearse con Estados Unidos, se trata de no tener todos los huevos en una sola canasta que sigue tambaleando. ¡Reitero, DIVERSIFICAMOS! (pero no con China)

Reservas estratégicas de combustible

La República Dominicana carece de reservas estratégicas suficientes de combustibles. Esto es una falla histórica que cada crisis vuelve a exponer. Toca legislar y construir, dentro de los próximos veinticuatro meses, una reserva estratégica equivalente a por lo menos sesenta días de consumo nacional de diésel y gasolina, financiada mediante un fondo especial alimentado por un pequeño gravamen sobre las utilidades extraordinarias de las generadoras eléctricas en años de bonanza. Países más pequeños que el nuestro ya lo tienen.

Medidas monetarias y cambiarias: protegiendo el peso

El BCRD ha mantenido su tasa de política monetaria sin cambios y decidió aplazar hasta enero de 2027 el retorno de RD$46,000 millones en facilidades de liquidez (Hoy 2026). Esta postura prudente debe sostenerse. Sin embargo, el presidente, en coordinación con el gobernador del Banco Central, debe asegurar una comunicación pública clara que evite el pánico cambiario. La apreciación del peso frente al dólar del 6.6 % a mediados de mayo (Infobae 2026) es una buena noticia que la prensa apenas ha destacado, y conviene aprovecharla para anclar expectativas.

Diplomacia firme y digna ante Washington

Aquí viene la parte que muchos políticos dominicanos no se atreven a decir. El presidente Abinader debe convocar al embajador estadounidense para entregarle, en términos cordiales pero absolutamente firmes, una nota de protesta formal por los daños colaterales económicos que esta aventura militar le ha ocasionado a la economía dominicana. Que se sepa públicamente. La República Dominicana es un país soberano y aliado, no un cliente que aguanta callado cualquier capricho geopolítico que se le ocurra a un mandatario gringo con afán de protagonismo. Pedir compensación, o al menos acceso preferencial a líneas de financiamiento blando del Banco Interamericano de Desarrollo y del Fondo Monetario Internacional para países afectados por el choque petrolero, no es mendigar: es exigir lo que corresponde.

Protección del aparato productivo y del empleo

Las pequeñas y medianas empresas dominicanas son las que más sufren cuando suben los costos energéticos. El Banco de Reservas debe abrir, por instrucción presidencial, una ventanilla especial de financiamiento a tasas preferenciales para MiPymes afectadas por el alza de costos energéticos, condicionada a que dichas empresas mantengan su nómina sin reducciones durante el período del préstamo. Esto evita una contracción del empleo formal, que ya creció apenas 4,1 % en el primer trimestre (BCRD 2026), por debajo del potencial dominicano histórico.

Comunicación honesta y permanente con la ciudadanía

El presidente ya hizo un esfuerzo importante al hablarle al país directamente en marzo de 2026 y pedir comprensión ante los ajustes. Eso se aplaude. Pero la comunicación no puede ser un evento aislado. Tiene que haber un informe quincenal del Ministerio de Hacienda y del BCRD, transmitido por todos los canales, explicando en lenguaje sencillo cómo va la factura petrolera, cuánto se ha ahorrado en reasignaciones, qué proyectos renovables han entrado al sistema y qué se espera para el próximo trimestre. La transparencia es el mejor antídoto contra los rumores y la especulación.

La vaina que está realmente en juego

Cuando los mercados petroleros se estabilicen, y se estabilizarán porque los choques de oferta históricamente son transitorios (Listín Diario 2026), la pregunta no será cuánto sufrimos sino qué construimos durante el sufrimiento. La República Dominicana tiene la oportunidad de salir de esta crisis menos dependiente, más diversificada y con una matriz energética más limpia. O tiene la opción de salir igualita, esperando el próximo arrebato imperial para volver a llorar.

Abinader tiene las herramientas, tiene las reservas, tiene el respaldo institucional del Banco Central y tiene un Congreso que, aunque la oposición critique, cuenta con el respaldo de la mayoría del pueblo, sabe que no es momento de improvisaciones. Lo que falta es ejecución sin demora ni pausa, y voluntad política para no patear la lata. Esta crisis, provocada por decisiones tomadas a miles de kilómetros de aquí por personas que jamás van a pagar las consecuencias de sus actos, debería convertirse paradójicamente en el momento bisagra que nuestra República lleva décadas esperando. Si así fuera, hasta le daríamos las gracias al dictador-quiereser por patada, . . . pero solo si actuamos. De lo contrario, dentro de diez años, cuando vuelva a estallar otra guerra del otro lado del mundo, estaremos otra vez aquí, yo escribiendo el mismo ensayo, con los mismos números pero más caros y maldiciendo los que nos meten en otra mierda.

~ C. Constantin Poindexter Salcedo, M.A. en Inteligencia, Certificado de Posgrado en Contrainteligencia, J.D., certificación CISA/NCISS OSINT, Certificación U.S. DoD/DoS BFFOC, Dipl. Diplomacia Global, Dipl. Derechos Humanos por USIDHR, Dipl. Negociación Diplomática por Harvard

Bibliografía

  • Acento. 2026. “Dependencia energética y presión global: el reto de República Dominicana ante la volatilidad del petróleo”. Acento, 26 de marzo de 2026. https://acento.com.do/economia/dependencia-energetica-y-presion-global-el-reto-de-republica-dominicana-ante-la-volatilidad-del-petroleo-9647645.html.
  • AlMomento. 2026. “Dependencia energética y vulnerabilidad macroeconómica en la República Dominicana”. AlMomento.net, 19 de abril de 2026. https://almomento.net/dependencia-energetica-y-vulnerabilidad-macroeconomica-en-la-republica-dominicana/.
  • Banco Central de la República Dominicana (BCRD). 2026. “Análisis: impacto del choque petrolero en la economía dominicana”. Página Abierta, Asesoría de la Gobernación del BCRD. 24 de mayo de 2026.
  • Diario Libre. 2026a. “RD depende casi totalmente del mercado global e incierto de energía”. Diario Libre, 7 de abril de 2026. https://www.diariolibre.com/economia/energia/2026/04/07/rd-depende-casi-totalmente-del-mercado-global-e-incierto-de-energia/3493384.
  • Diario Libre. 2026b. “BCRD: guerra le costará al país US$900 millones y una elevada inflación”. Diario Libre, 24 de mayo de 2026. https://www.diariolibre.com/economia/macroeconomia/2026/05/24/bcrd-guerra-le-costara-al-pais-us900-millones-y-una-elevada-inflacion/3544267.
  • Diario Libre. 2026c. “Abinader advierte impacto económico por guerra en Irán; anuncia ajustes fiscales y subsidios”. Diario Libre, 22 de marzo de 2026. https://www.diariolibre.com/politica/gobierno/2026/03/22/abinader-advierte-impacto-economico-por-guerra-en-iran/3478076.
  • Hoy. 2026. “Choque petrolero subirá factura energética US$900 millones”. Periódico Hoy, 25 de mayo de 2026. https://hoy.com.do/economia/choque-petrolero-subira-factura-energetica-us-900-millones_1088452.html.
  • Infobae. 2026. “República Dominicana ante la presión del petróleo: impacto del conflicto en Medio Oriente”. Infobae, 25 de mayo de 2026. https://www.infobae.com/republica-dominicana/2026/05/25/republica-dominicana-ante-la-presion-del-petroleo-impacto-del-conflicto-en-medio-oriente/.
  • Listín Diario. 2026. “El drenaje de divisas del choque petrolero al sostener crecimiento del PIB en 4 %”. Listín Diario, 15 de mayo de 2026. https://listindiario.com/puntos-de-vista/20260515/drenaje-divisas-choque-petrolero-sostener-crecimiento-pib-4_905783.html.
  • Presidencia de la República Dominicana. 2026. “Presidente Abinader afirma que el país está preparado para enfrentar el impacto de la crisis internacional del petróleo”. Presidencia.gob.do, 22 de marzo de 2026. https://presidencia.gob.do/noticias/presidente-abinader-afirma-que-el-pais-esta-preparado-para-enfrentar-el-impacto-de-la.
Share this post:

Narrative Engineering for Deception in the Age of A.I.? Yes, but with some Caveats

Narrative Engineering for Deception in the Age of A.I. Yes, but with some Caveats, deception operations, D&D, intelligence, counterintellingence, espionage, counterespionage, C. Constantin Poindexter, strategic deception

Henry W. Prunckun’s Narrative Engineering for Deception (NED) framework offers a disciplined architecture for thinking about operational deception. His recent piece, Engineering Plausibility in Deception Operations, published in the International Journal of Intelligence and CounterIntelligence, is just another in a long list of robust scholarship on intelligence and counterintelligence matters, many volumes of which I had the pleasure of reading and citing during my Master’s Degree in Intelligence studies years past. By treating plausibility as a behavioral threshold rather than an epistemic state, and audit resilience as expected time to falsification, Prunckun reframes the deception planner’s work as a problem of structural engineering rather than improvisational craft. The seven levers he identifies, namely point of view, coherence, persona, pacing, texture, cognitive alignment, and exit strategy, provide a vocabulary that is parsimonious AND operationally tractable. The framework deserves the respect it has begun to receive in professional literature.

The framework was calibrated for an operational environment that is already disappearing. Verification in the twentieth and early twenty-first centuries was human-paced, institutionally siloed, and bounded by the labor cost of cross-domain correlation. Each of those constraints has now collapsed under the combined weight of machine learning, aggregated commercial datasets, and what the United States Intelligence Community now formally designates Ubiquitous Technical Surveillance (Office of the Director of National Intelligence 2024). The thesis of this essay is therefore qualified rather than dismissive: NED remains a coherent and useful design discipline, but several of its central levers invert under machine audit, and the framework requires recalibration toward operational ephemerality rather than durable cover.

The Pre-A.I. Verification Environment that NED Presupposes

NED’s levers presume a particular kind of adversary. The adversary is intelligent, motivated, and possibly skilled, but is also resource-constrained. The adversary tires. The adversary works within bureaucratic procedures that batch information rather than fuse it. The adversary’s analysts each see a portion of the picture, and the seams between their views are exploitable. Prunckun’s pacing lever, for instance, exists precisely because human auditors trade thoroughness for speed under workload pressure. His texture lever exists because mundane detail saturates limited human attention. His cognitive alignment lever depends on biases (anchoring, fluency, confirmation, closure) that are characteristically human (Kahneman 2011).

These presumptions described real adversaries for most of the twentieth century. The operational histories Prunckun draws on, Argo and Operation Copperhead, succeeded against human pattern recognition operating without machine support. Tony Méndez exploited the bureaucratic fluency of customs officers reviewing paperwork at human speed (Méndez and Baglio 2012). M.E. Clifton James exploited the visual heuristic that famous generals look like themselves (Crowdy 2008). Both operations would have run differently, and arguably failed, against modern fused intelligence.

How Machine Audit Screws with the Levers

The transition from human to machine-assisted verification does not merely accelerate audit. It changes its kind. Five of Prunckun’s seven levers face structural inversion.
Texture inverts most sharply. Prunckun treats mundane detail as camouflage, on the premise that ordinary noise occupies the auditor’s attention without rewarding scrutiny. Under machine audit, metadata is more legible to algorithms than to humans. Aggregated commercial datasets, including those acquired in bulk by foreign services, permit rapid correlation of timestamps, registries, travel records, financial transactions, and social graphs (Sherman 2025). What was once camouflage becomes signal density. The receipts, routine emails, and habitual patterns that grounded a cover identity in the human era now feed anomaly detection systems that thrive on exactly such structured exhaust. The Federal Bureau of Investigation’s recent Office of Inspector General review found UTS to constitute, in plain language, an existential threat to operational security across U.S. federal law enforcement (Department of Justice Office of the Inspector General 2025).

Coherence faces a parallel inversion. Prunckun’s lever assumes coherence is tested within a domain by an analyst with limited cross-domain access. Machine systems test coherence across domains simultaneously. A timeline that is internally consistent across an identity’s documentary record may nonetheless contradict ambient cellular geolocation, satellite imagery cadence, or financial network rails the planner did not know were being correlated. Former Central Intelligence Agency Deputy Director for Science and Technology Dawn Meyerriecks publicly acknowledged in 2018 that in roughly thirty countries, CIA officers were no longer followed by local services because surveillance density made physical followers redundant (Dorfman 2020). The point generalizes: the auditor’s view has become panoramic in ways no individual analyst could previously achieve.

Persona degrades under stylometric, biometric, and behavioral pattern analysis. Prunckun lists idiolect as a persona strength, reasoning that distinctive speech patterns reinforce credibility under contact. Machine learning systems now cluster on idiolect as a fingerprint (Constâncio et al. 2023). Facial recognition, gait analysis, voice print identification, and writing pattern matching collectively render alias work, in former intelligence officials’ assessment, likely impossible across hard target environments such as China, Russia and perhaps Iran within the next operational generation (Dorfman 2020). The persona that survives casual human interrogation may yet fail silently against a database query the target never visibly executed.

Pacing loses its purchase. The lever depends on the gap between heuristic and deep verification, the seam through which an operation completes its objective before slow checks catch up. Machine systems do not batch, do not tire, and do not have a casual inspection mode. The seam narrows toward zero for anything machine auditable. Verification that previously took days now runs in seconds, and runs continuously rather than on prompt.

Cognitive alignment, the lever Prunckun treats as cross-cutting, breaks hardest against algorithmic auditors. Anchoring, fluency, confirmation, availability, and closure are human cognitive shortcuts. A trained classifier does not weight early evidence more heavily simply because it arrived first, does not find fluent narratives more credible, and does not seek closure in ways that suppress further inquiry (Constâncio et al. 2023). The bias terrain on which Prunckun’s framework operates is, at the machine layer, largely flat.

The Levers that Survive, and Why

Two levers retain force under machine audit, though with shifted emphasis.
Point of view survives because what an auditing system checks is determined by what an operation triggers it to check. A well-constructed narrative that does not enter high-resolution surveillance regimes, or that does not trip the thresholds that escalate routine screening to a targeted investigation, may still slip through. Footprint minimization is the modern expression of the point of view lever. The planner shapes not the auditor’s interpretation of signals but the auditor’s decision to collect them.

Exit strategy survives, and arguably becomes more important. Where machine audit makes durable cover increasingly infeasible, the disposability of an operation becomes a planning variable rather than a contingency. The National Security Commission on Artificial Intelligence warned explicitly that adversary adoption of AI tools makes the U.S. Intelligence Community more vulnerable to deception, source exposure, and counterintelligence pressure, and the Commission’s framing implicitly favors operations designed to complete and dissolve before correlation catches them (National Security Commission on Artificial Intelligence 2021).

The Two Audience Dilemma

A critical refinement is required. Even in an environment of machine audit, the ultimate target of most deception operations remains a human decision maker. Machine systems flag anomalies; humans decide whether to escalate, act, or stand down. The behavioral threshold that NED targets is still crossed inside a human head, and the cognitive biases that align with the lever framework still operate at that level.

So, modern deception is a two-audience problem. The first audience is the machine filter, which is governed by data, correlation, and statistical anomaly. The second audience is the human decision maker downstream, who is governed by attention, narrative, and the cognitive shortcuts NED was designed to exploit. The framework retains substantial force at the second audience and substantially less at the first.

This insight reframes the planning problem. The operation must clear the machine filter not by being credible to it but by being uninteresting to it, that is, by minimizing the data footprint the filter has to correlate. Once past the filter, the operation may then engage human cognition through the classical levers of persona, texture, and pacing. Phase compression becomes structural rather than optional. The operation must complete its work in the window between machine flagging and human investigation.

Generative A.I. and the Offense Defense Balance

The picture is not uniformly bleak for the deception planner. Generative artificial intelligence cuts in both directions. Mandiant has documented threat actors using generative models to produce backstop content for inauthentic personas, including profile imagery, plausible filler text, and language-localized communications that previously required substantial human labor (Mandiant 2024). The Federal Reserve and the World Economic Forum have separately documented the rise of agentic AI fraud systems that create synthetic identities, interact with verification systems in real time, and adjust behavior based on outcomes (Federal Reserve 2024; World Economic Forum 2025). The Office of the Director of National Intelligence has noted, in an unclassified discussion of foreign intelligence service activity, that adversary services now reportedly generate inauthentic communications and synthetic digital identities at operational scale (Goldman 2026).

What this means for NED is that the framework’s underlying logic, treating narrative elements as engineerable parameters under verification pressure, becomes more rather than less relevant. The arms race is not planner versus machine but planner with machine versus auditor with machine. Defense holds the structural advantage of aggregation, where one anomaly is enough, but offense retains the advantage of needing only a short operational window. Whether the balance favors offense or defense in any given operation is now a function of phase compression, footprint discipline, and exit modularity, all of which Prunckun’s framework already names, though without developing them to the depth current conditions require.

A Recalibrated NED

What survives the transition, then, is the framework’s grammar rather than its operational parameters. The constructs of plausibility as behavioral threshold and audit resilience as time to falsification remain valid and arguably become sharper under machine audit, where falsification windows are measurable in hours rather than months. The seven levers remain a useful vocabulary for design discussion, though several require inversion in their operational settings. The phase model retains explanatory power, though its emphasis shifts decisively toward the withdrawal phase.

The honest version of post-A.I. NED might be like the following. Assume verification windows in hours or days, not months. Build for phase compression. Minimize footprint to the bone, accepting thinner cover in exchange for fewer correlation points. Design the exit before the entry. Treat texture not as camouflage but as a controlled liability whose volume must be calibrated against the data exhaust it generates. Assume that idiolect, gait, and metadata signatures are identifying even when the underlying identity claim is uncontested. Treat the human decision maker as a distinct audience from the machine filter, and design lever settings appropriate to each.

Prunckun has given the field a vocabulary it badly needed. Aside from just loving this guy and appreciating the depth and breadth of his knowledge in our subject matter, the discipline of treating deception as engineering rather than as intuitive craft will outlast the particular operational environment in and for which he is currently articulating the framework. What changes is the calibration. The durable, texture-rich, persona-deep cover that worked against human auditors in the bureaucratic era is increasingly infeasible against A.I.-assisted verification in a world of ubiquitous data exhaust. What replaces it is something closer to operational ephemerality, . . . thin, fast, disposable narratives engineered to complete their behavioral work before correlation completes its analytic work. NED in the age of A.I. is not obsolete. It is, however, a different framework than the one initially described, and the gap between the framework as written and the framework as required is the territory in which the next generation of operational deception is going to be contested.

~ C. Constantin Poindexter, MA in Intelligence, Graduate Certificate in Counterintelligence, JD, CISA/NCISS OSINT certification, DoD/DoS BFFOC Certification

Bibliography

  • Constâncio, Alex Sebastião, Denise Fukumi Tsunoda, Helena de Fátima Nunes Silva, Jocelaine Martins da Silveira, and Deborah Ribeiro Carvalho. 2023. “Deception Detection with Machine Learning: A Systematic Review and Statistical Analysis.” PLOS ONE 18 (2): e0281323.
  • Crowdy, Terry. 2008. Deceiving Hitler: Double Cross and Deception in World War II. Oxford: Osprey Publishing.
  • Department of Justice, Office of the Inspector General. 2025. Audit of the Federal Bureau of Investigation’s Efforts to Mitigate the Effects of Ubiquitous Technical Surveillance. Washington, DC: U.S. Department of Justice.
  • Dorfman, Zach. 2020. “Shattered: Inside the Secret Battle to Save America’s Undercover Spies in the Digital Age.” Yahoo News, December 30, 2020.
  • Federal Reserve. 2024. Generative Artificial Intelligence Increases Synthetic Identity Fraud Threats. Federal Reserve Financial Services Synthetic Identity Fraud Mitigation Toolkit.
  • Goldman, Adam. 2026. “AI and the Reconfiguration of the Counterintelligence Battlefield.” International Journal of Intelligence and CounterIntelligence. Advance online publication.
  • Kahneman, Daniel. 2011. Thinking, Fast and Slow. New York: Farrar, Straus and Giroux.
  • Mandiant. 2024. Threat Actors are Interested in Generative AI, but Use Remains Limited. Google Cloud Threat Intelligence Report. Mountain View, CA: Mandiant.
  • Méndez, Antonio J., and Matt Baglio. 2012. Argo: How the CIA and Hollywood Pulled Off the Most Audacious Rescue in History. New York: Viking.
  • National Security Commission on Artificial Intelligence. 2021. Final Report. Washington, DC: NSCAI.
  • Office of the Director of National Intelligence. 2024. Unifying Intelligence Strategy for Counterintelligence. Washington, DC: National Counterintelligence and Security Center.
  • Prunckun, Henry W. 2025. “Engineering Plausibility in Deception Operations.” Journal of Intelligence and Counterintelligence Studies. Advance online publication.
  • Sherman, Justin. 2025. “Ubiquitous Technical Surveillance Demands Broader Data Protections.” Lawfare, July 25, 2025.
  • World Economic Forum. 2025. The Global Risks Report 2026: Identity Fraud in the Age of AI. Geneva: World Economic Forum.
Share this post:

When the Watchers Get Watched: The FBI Wiretap Breach

When the Watchers Get Watched: What the FBI Wiretap Breach Means for Everyone Else, FBI, CIA, DNI, C. Constantin Poindexter, counterintelligence, counterespionage, covert action

The compromise of the Federal Bureau of Investigation’s wiretap infrastructure by Chinese state-sponsored hackers represents not merely a cybersecurity failure but a fundamental counterintelligence catastrophe that demands immediate strategic reassessment. The Salt Typhoon intrusion, attributed to China’s Ministry of State Security (MSS), exploited the very systems mandated by the Communications Assistance for Law Enforcement Act (CALEA) to transform America’s lawful intercept capabilities into an open door for adversarial intelligence collection. While public discourse has focused on the compromise of political communications and the exposure of millions of Americans’ metadata, the counterintelligence community must confront a more insidious implication: by accessing the target lists and surveillance parameters within FBI wiretap systems, Chinese FIS likely have obtained a roadmap to their own compromised operatives, informants, and recruitment networks (NBC News 2025; Nextgov/FCW 2025).

The technical architecture of the breach reveals a systemic vulnerability that has persisted for years. Salt Typhoon operators infiltrated at least nine major U.S. telecommunications providers, including AT&T, Verizon, and Lumen, maintaining persistent access since approximately 2019 (Wikipedia 2025; Nextgov/FCW 2025). The exploitation vector was not sophisticated zero-day weaponry but rather the CALEA-mandated lawful intercept systems themselves—backdoors engineered into telecom infrastructure to facilitate court-authorized surveillance. As Senator Maria Cantwell noted in December 2025 Senate Commerce Committee hearings, “They exploited the wiretapping system that our law enforcement agencies rely on under CALEA. These systems became an open door for Chinese intelligence” (U.S. Senate Committee on Commerce, Science, & Transportation 2025). The hackers leveraged outdated equipment, unpatched router vulnerabilities with patches available for seven years, and weak credential management to establish a persistent presence across carrier networks (U.S. Senate Committee on Commerce, Science, & Transportation 2025).

The counterintelligence dimension of this compromise extends far beyond the immediate theft of communications data. When Salt Typhoon accessed FBI wiretap systems, they potentially obtained the target lists, identifying which individuals, phone numbers, and accounts were subject to active or pending surveillance authorizations. This intelligence bonanza enables Chinese services to identify which of their operatives, assets, and informants have been compromised by U.S. counterintelligence, which recruitment networks have been penetrated, and which communication channels have been compromised (UMBC 2025; The Conversation 2025). As one security analysis noted, “By compromising lawful intercept systems, Chinese intelligence operatives gained visibility into which of their agents and informants were under U.S. surveillance, knowledge that can help those targets try to evade such surveillance” (InstaTunnel 2025).

The implications for HUMINT operations are devastating. Every target list compromised represents potential exposure of recruited assets, informants who have provided critical intelligence, and the methods by which U.S. counterintelligence identifies foreign operatives. Chinese intelligence can now cross-reference these lists against their own personnel databases, identify personnel who may have been turned or are under suspicion, and take protective measures ranging from enhanced surveillance of suspected leaks to elimination of compromised assets. The damage is not merely retrospective. It is prospective. Future counterintelligence operations against Chinese targets will face heightened suspicion that their targets have been alerted to surveillance through this compromise.

The scope of the intelligence loss is staggering. FBI assessments indicate Salt Typhoon targeted over 80 countries and compromised approximately 600 organizations (Nextgov/FCW 2025; The Record 2025). While fewer than 100 individuals had actual call content and text messages directly intercepted, the metadata exposure and geolocation tracking affected millions (InstaTunnel 2025). High-profile targets included then-presidential candidate Donald Trump, Vice Presidential candidate JD Vance, and the staff of the Kamala Harris campaign, clearly demonstrating the group’s willingness to target the highest levels of American political leadership (Wikipedia 2025; Axios 2024). The interception of unencrypted text messages and audio recordings from these targets represents not merely political espionage but a demonstration of capability that sends a clear signal about Chinese reach into American communications infrastructure.

Senate Intelligence Committee leadership has characterized the breach in apocalyptic terms. Senator Mark Warner, Vice Chairman of the Senate Select Committee on Intelligence, called Salt Typhoon the “worst telecom hack in our nation’s history” (Lawfare 2025). Former FBI Director Christopher Wray described it as the “most significant cyber espionage campaign in history” (Lawfare 2025). These assessments reflect not merely the scale of the compromise but its strategic implications: the demonstrated ability of Chinese intelligence to penetrate the infrastructure underlying American signals intelligence and law enforcement surveillance capabilities.

The FBI’s formal designation of the wiretap compromise as a “major cyber incident” under federal data security law acknowledges the severity of the breach. Such designation applies only to compromises involving personally identifiable information that could cause “demonstrable harm” to national security interests, foreign relations, or civil liberties (NBC News 2025; HSToday 2025). The Bureau’s April 2025 offer of a $10 million reward for information leading to Salt Typhoon operator identification underscores the ongoing nature of the threat and the difficulty of attribution in state-sponsored operations (Breached.Company 2025).

From a counterintelligence perspective, the Salt Typhoon compromise demands a fundamental reassessment of how lawful intercept capabilities are architected and secured. The CALEA mandate created a centralized surveillance infrastructure that, while facilitating legitimate law enforcement needs, simultaneously created a high-value target for adversarial exploitation. The security of these systems was predicated on the assumption that telecommunications providers would implement “rudimentary cybersecurity measures”—an assumption that proved catastrophically unfounded (U.S. Senate Committee on Commerce, Science, & Transportation 2025).

The ongoing remediation challenges compound the counterintelligence damage. As of December 2025, telecom companies infiltrated in the attack had failed to prove that Chinese hackers had been eradicated from their networks (U.S. Senate Committee on Commerce, Science, & Transportation 2025). The November 2025 FCC decision to roll back cybersecurity regulations implemented after Salt Typhoon—championed by Chairman Brendan Carr—has drawn sharp criticism from security experts who note that vulnerabilities “are still being exploited” (U.S. Senate Committee on Commerce, Science, & Transportation 2025). This regulatory environment suggests that the conditions enabling Salt Typhoon’s initial penetration persist, raising the specter of continued or renewed compromise.

For the counterintelligence practitioner, the lessons of Salt Typhoon are clear and troubling. First, the lawful intercept infrastructure designed to support counterintelligence operations has become a liability, potentially compromising the very operations it was meant to enable. Second, the persistence of Chinese access since 2019 suggests that counterintelligence targeting of Chinese operatives during this period may have been visible to adversary services. Third, the inability to confirm remediation means that current and future operations remain at risk of exposure through compromised infrastructure.

The Salt Typhoon breach represents a paradigm shift in counterintelligence operations. When the watchers’ own surveillance infrastructure becomes the vector for adversarial intelligence collection, traditional operational security models collapse. The counterintelligence community must now operate under the assumption that Chinese intelligence possesses visibility into historical FBI target lists and may possess ongoing access to surveillance parameters. This requires not merely technical remediation but operational adaptation: reassessment of ongoing investigations, validation of asset security, and development of surveillance methodologies that do not rely on compromised infrastructure.

The breach also carries implications for allied intelligence sharing. The FBI assessment that Salt Typhoon targeted over 80 countries suggests that the compromise extends beyond American networks to allied telecommunications infrastructure (Nextgov/FCW 2025; The Record 2025). Allied counterintelligence services must now assess whether their own lawful intercept capabilities have been similarly compromised and whether shared targeting information has been exposed to Chinese intelligence.

The Salt Typhoon compromise of FBI wiretap infrastructure represents a watershed moment in cyber-enabled counterintelligence. The transformation of lawful intercept systems from tools of surveillance to vectors of exposure demonstrates the fundamental vulnerability of centralized surveillance architectures in an era of persistent cyber threats. For the counterintelligence community, the challenge is not merely technical remediation but strategic adaptation: developing operational methodologies that assume adversarial FIS’s visibility into surveillance infrastructure while maintaining the capability to identify and neutralize foreign intelligence threats. Compromising Red Hook is only one of a myriad of penetrations, . . . the alarm is blinking red. The watchers have been watched, and the counterintelligence implications of that reversal should frighten everyone.

~ C. Constantin Poindexter, MA in Intelligence, Graduate Certificate in Counterintelligence, JD, CISA/NCISS OSINT certification, DoD/DoS BFFOC Certification


Bibliography

  • Axios. 2024. “China-backed Salt Typhoon spied on politicians phones for months: reports.” Axios, October 29. https://www.axios.com/2024/10/29/salt-typhoon-targets-politicians-phones.
  • Breached.Company. 2025. “FBI Wiretap Systems Compromised: Inside Salt Typhoon’s Infiltration of America’s Lawful Intercept Infrastructure.” Breached.Company, April. https://breached.company/fbi-wiretap-systems-compromised-salt-typhoon-lawful-intercept/.
  • HSToday. 2025. “FBI Labels China-Linked Hack of Surveillance System a ‘Major Cyber Incident.'” Homeland Security Today, April 1. https://www.hstoday.us/fbi/fbi-labels-china-linked-hack-of-surveillance-system-a-major-cyber-incident/.
  • InstaTunnel. 2025. “Salt Typhoon: When State-Sponsored Hackers Infiltrate Telecom Infrastructure.” Medium, January. https://medium.com/@instatunnel/salt-typhoon-when-state-sponsored-hackers-infiltrate-telecom-infrastructure-8d8aeb5ce19c.
  • Lawfare. 2025. “Reconfiguring U.S. Cyber Strategy in the Wake of Salt Typhoon.” Lawfare, January. https://www.lawfaremedia.org/article/reconfiguring-u.s.-cyber-strategy-in-the-wake-of-salt-typhoon.
  • NBC News. 2025. “FBI labels suspected China hack of law enforcement data ‘a major cyber incident.'” NBC News, April 1. https://www.nbcnews.com/news/us-news/fbi-labels-suspected-china-hack-law-enforcement-data-major-cyber-incid-rcna266495.
  • Nextgov/FCW. 2025. “Salt Typhoon hackers targeted over 80 countries, FBI says.” Nextgov/FCW, August 27. https://www.nextgov.com/cybersecurity/2025/08/salt-typhoon-hackers-targeted-over-80-countries-fbi-says/407719/.
  • The Conversation. 2025. “What is Salt Typhoon? A security expert explains the Chinese hackers and their attack on US telecommunications networks.” The Conversation, January. https://theconversation.com/what-is-salt-typhoon-a-security-expert-explains-the-chinese-hackers-and-their-attack-on-us-telecommunications-networks-244473.
  • The Record. 2025. “Allied spy agencies blame 3 Chinese tech companies for Salt Typhoon attacks.” The Record from Recorded Future News, January. https://therecord.media/allied-spy-agencies-blame-chinese-companies-salt-typhoon.
  • UMBC (University of Maryland, Baltimore County). 2025. “What Is Salt Typhoon? A Security Expert Explains The Chinese Hackers And Their Attack On US Telecommunications Networks.” UMBC News, January. https://umbc.edu/stories/what-is-salt-typhoon-a-security-expert-explains-the-chinese-hackers-and-their-attack-on-us-telecommunications-networks/.
  • U.S. Senate Committee on Commerce, Science, & Transportation. 2025. “Experts Agree U.S. Communications Networks Remain Vulnerable Following Salt Typhoon Hack.” Senate Commerce Committee Press Release, December 2. https://www.commerce.senate.gov/2025/12/experts-agree-u-s-communications-networks-remain-vulnerable-following-salt-typhoon-hack.
  • Wikipedia. 2025. “Salt Typhoon.” Wikipedia, last modified January. https://en.wikipedia.org/wiki/Salt_Typhoon.
Share this post:

La injerencia inaceptable de la Embajadora Leah Campos: una afrenta a la soberanía dominicana

leah campos, Republica Dominicana, dimplomacia, canciller, embajada, C. Constantin Poindexter Salcedo, Abinader

Escribo esto con la indignación encendida y con la firme convicción de que ciertas fronteras jurídicas, morales y protocolares no pueden ser cruzadas sin consecuencias. Las recientes declaraciones de la Embajadora de los Estados Unidos en la República Dominicana, Leah Francis Campos, cuestionando (“condenando” más bien) públicamente, por medio de sus redes sociales personales, la asistencia de representantes del nuestro Estado a la IV Cumbre en Defensa de la Democracia celebrada en Barcelona bajo los auspicios del gobierno del presidente Pedro Sánchez, constituyen una violación flagrante del derecho internacional público, de los principios elementales del sistema interamericano y de la ética diplomática más básica. No se trata de una opinión marginal ni de un exabrupto privado ni simplemente de su patanería. Se trata de una funcionaria acreditada que utiliza el peso simbólico de su investidura para descalificar una decisión soberana de política exterior dominicana. Permitir que esto pase sin un rechazo argumentado sería, en sí mismo, una claudicación. Déjeme aclarar o ampliar sobre estos tamaños disparates de Campos, porque los hechos están bien documentados.

El consultor jurídico del Poder Ejecutivo y ministro de Justicia, Antoliano Peralta Romero, asistió en calidad de invitado a la cumbre de Barcelona y pronunció unas palabras sobre la lucha contra la desinformación digital, aclarando expresamente que la República Dominicana no suscribió declaración alguna ni le fue solicitado hacerlo (Listín Diario 2026). En respuesta, la Embajadora Campos publicó en sus historias de Instagram una fotografía del ministro estrechando la mano de Pedro Sánchez, acompañada de un pasaje del Apocalipsis 3:16 sobre los tibios a quienes Dios vomitaría de su boca, y añadió que cuando la izquierda global habla de desinformación está abogando por la censura (Ensegundos 2026; El Nuevo Diario 2026). Voy a detenerme aquí, con alguna severidad, en la forma que asumió ese mensaje porque no es un detalle menor. La Embajadora no emitió un comunicado razonado. No convocó una rueda de prensa. No articuló un argumento jurídico ni político. Recurrió, en cambio, a un meme bíblico, es decir, a un formato típico de la cultura digital adolescente (o en el caso extante “Trumpista”), en el que una imagen cargada de connotación amenazante (un versículo apocalíptico sobre vómito divino) se superpone burlonamente a la fotografía de un funcionario extranjero. Ese registro, propio de las peleas de redes sociales entre escuincles y de los cristofascistas americanos que parecen de moda allá, resulta MEGA-indigno del rango de jefa de misión. Una embajadora no insinúa que Dios vomitará a un ministro del Estado receptor por haberle estrechado la mano a un anfitrión que a ella le disgusta o que haya ofendido en alguna forma al jefe del Estado de ella. Ese tipo de burla pública, que prescinde del argumento y se refugia en la mofa emoji-bíblica, no solo envilece su propio cargo, sino que trivializa la seriedad con que deben tratarse las relaciones entre Estados soberanos. La Cancillería dominicana no fue consultada. No hubo nota verbal. No hubo comunicación privada. Hubo, en cambio, un ejercicio de presión pública, ejecutado con el tono de quien chotea a un compañero de curso, desde la cuenta oficial de una diplomática acreditada. Y es precisamente allí donde reside el corazón del problema.

Primera violación: el artículo 41 de la Convención de Viena sobre Relaciones Diplomáticas

La Convención de Viena sobre Relaciones Diplomáticas de 1961, instrumento al que tanto los Estados Unidos como la República Dominicana son Estados parte, establece en el párrafo primero de su artículo 41 que todas las personas que gocen de privilegios e inmunidades diplomáticas están obligadas a no inmiscuirse en los asuntos internos del Estado receptor (Naciones Unidas 1961). Esta obligación no es decorativa ni aspiracional. Como ha señalado la Corte Internacional de Justicia en el caso Nicaragua vs. Estados Unidos (1986), el principio de no intervención posee carácter consuetudinario y forma parte del núcleo duro del derecho internacional general (Petrova Georgieva 2026). Cuando la Embajadora Campos objeta públicamente a qué cumbre internacional puede o no puede asistir un representante del gobierno dominicano, se inmiscuye de manera directa, flagrante y documentable en un ámbito que es competencia exclusiva del Estado acreditante ante el cual ella está acreditada. La definición de la política exterior dominicana corresponde al presidente de la República y a su canciller, no a la embajadora de una potencia extranjera operando desde Instagram.

Segunda violación: el artículo 41.2 y el principio del canal oficial

Aun si se aceptara, por pura hipótesis, que los Estados Unidos tuvieran alguna observación legítima que formular sobre la participación dominicana en un foro internacional, el párrafo segundo del mismo artículo 41 de la Convención de Viena es igualmente claro: todos los asuntos oficiales de que la misión esté encargada por el Estado acreditante han de ser tratados con el Ministerio de Relaciones Exteriores del Estado receptor, por conducto de él, o con el Ministerio que se haya convenido (Naciones Unidas 1961; OEA s.f.). Esta disposición codifica lo que la práctica diplomática centenaria ha consagrado como el canal oficial. La existencia misma de este canal presupone que la diferencia de opinión entre gobiernos se airea mediante notas verbales, comunicaciones reservadas, démarches o, en casos graves, el llamado a consultas. Jamás mediante publicaciones en redes sociales que, por su propia naturaleza, están diseñadas para inflamar la opinión pública del país receptor y presionar políticamente a su gobierno. La Embajadora Campos no desconoce este canal, lo despreció deliberadamente.

Tercera violación: el artículo 19 de la Carta de la OEA

La República Dominicana y los Estados Unidos son Estados miembros fundadores de la Organización de los Estados Americanos. El artículo 19 de la Carta de esa organización, suscrita en Bogotá en 1948, establece de manera categórica que ningún Estado o grupo de Estados tiene derecho a intervenir, directa o indirectamente, y sea cual fuere el motivo, en los asuntos internos o externos de cualquier otro, y precisa que el principio anterior excluye no solamente la fuerza armada, sino también cualquier otra forma de injerencia o de tendencia atentatoria de la personalidad del Estado, de los elementos políticos, económicos y culturales que lo constituyen (Organización de los Estados Americanos 1948; Vargas Carreño 2003). La decisión sobre a qué cumbres internacionales asistirá la República Dominicana pertenece, de manera inequívoca, a los asuntos externos del Estado. Cualquier intento de presionar esa decisión, incluso por medios no coercitivos pero sí públicamente humillantes, constituye una injerencia prohibida en términos que la propia diplomacia hemisférica ha refinado durante casi un siglo, desde la Conferencia de Montevideo de 1933 hasta el Protocolo de Buenos Aires de 1936 (Pinho De Oliveira 2020).

Cuarta violación: el artículo 2.7 de la Carta de las Naciones Unidas

A nivel universal, el párrafo séptimo del artículo 2 de la Carta de las Naciones Unidas consagra el principio de no intervención en los asuntos que son esencialmente de la jurisdicción interna de los Estados (Vargas Carreño 2003). La Asamblea General, mediante sus resoluciones 2131 (XX) de 1965 y 2625 (XXV) de 1970, ha reiterado una y otra vez que ningún Estado puede aplicar o fomentar medidas de cualquier índole para coaccionar a otro Estado a fin de obtener de él la subordinación del ejercicio de sus derechos soberanos (Pinho De Oliveira 2020). Publicar en redes sociales, desde la cuenta institucional de una embajadora, mensajes que buscan avergonzar públicamente al gobierno receptor por ejercer su derecho soberano a participar en un foro multilateral es, precisamente, una forma sutil pero inequívoca de esa coacción que el derecho internacional proscribe.

Quinta violación: la ética diplomática y el uso instrumental de las redes sociales

Más allá de las normas positivas, existe un cuerpo de costumbres, usos y expectativas que constituye la ética diplomática. Esa ética supone discreción, tacto, respeto por el gobierno receptor y, sobre todo, comprensión de que la investidura diplomática no es una plataforma personal de activismo ideológico. La Embajadora Campos ha convertido su cuenta de Instagram en un púlpito desde el cual dicta lecciones sobre lo que, según ella, debe o no debe hacer la política exterior dominicana. Esto no solo viola el espíritu del artículo 3 de la Convención de Viena, que enumera taxativamente las funciones de una misión diplomática sin incluir en ningún lugar la crítica pública al Estado receptor, sino que además instrumentaliza el prestigio institucional del cargo para fines que parecen más propios de un activista político que de una representante de Estado.

El contexto que ilumina el motivo y la hipocresía de fondo

No se me escapa, y quiero consignarlo con total franqueza, que estas declaraciones ocurren en un momento internacional muy específico. El gobierno español de Pedro Sánchez, anfitrión de la cumbre, se ha negado recientemente a autorizar el uso de las bases militares de Rota y Morón, así como del espacio aéreo español, para las operaciones militares estadounidenses contra Irán, calificando esa intervención como injustificada y fuera de la legalidad internacional (CNN en Español 2026; La Nación 2026). Es imposible no ver en la publicación de la Embajadora Campos un elemento de represalia política dirigido contra cualquier gobierno que haya osado compartir mesa con Sánchez. Pero ese contexto, lejos de atenuar la gravedad de su conducta, la agrava. Convierte una injerencia en un instrumento de presión de terceros, coñazo y utiliza a la República Dominicana como ficha en un tablero que no es el nuestro.

¡No he terminado! Hay otra mierda, una dimensión aún más incómoda que hay que señalarla con nombre y apellido. La materia misma que convocaba la cumbre de Barcelona, a saber, la defensa de la democracia y la lucha contra la desinformación digital, constituye en sí una afrenta simbólica directa al mandatario al que la embajadora representa. El presidente Donald Trump es, para ser preciso, el jefe de Estado contemporáneo que más daño ha infligido a la democracia de su propio país mediante la práctica sistemática de aquello que la cumbre precisamente denunciaba. Los ejemplos son abundantes, públicos y documentados por fuentes autoritativas. El Centro Brennan para la Justicia de la Escuela de Derecho de Nueva York ha documentado que el presidente indultó el mismo día de su investidura a aproximadamente 1,600 personas procesadas por el asalto al Capitolio del 6 de enero de 2021, incluyendo a condenados por conspiración sediciosa como Enrique Tarrio, cuya sentencia de veintidós años fue conmutada (Brennan Center for Justice 2025; CNN en Español 2025). Ese asalto tenía por objetivo, de manera expresa y comprobada, impedir la certificación congresional de un resultado electoral legítimo: la definición misma de desinformación convertida en violencia política.

A ese precedente se suma una política ejecutiva sostenida de ataque contra las instituciones intermedias que sostienen toda democracia funcional. En marzo de 2025 el presidente emitió una orden ejecutiva que pretende dictar reglas federales a los estados sobre cómo administrar sus propias elecciones, en contradicción con el diseño federal consagrado por la Constitución (Brennan Center for Justice 2025). Amnistía Internacional, en su informe Ringing the Alarm Bells de enero de 2026, documenta la revocación de más de seis mil visas de estudiantes extranjeros por su activismo político identificado mediante vigilancia en redes sociales, la detención con fines de deportación de manifestantes pacíficos como Mahmoud Khalil y Leqaa Kordia tras sus protestas en la Universidad de Columbia, y el condicionamiento de fondos federales a universidades a cambio de limitar su autonomía académica y sus programas de diversidad (Amnistía Internacional 2026). El Real Instituto Elcano ha calificado este patrón como una guerra contra las universidades sin precedentes en la historia reciente de los Estados Unidos (Aldecoa 2025). Añádase a esto la presión política directa sobre medios de comunicación como ABC y Paramount, la negativa del país a participar en su propio Examen Periódico Universal ante las Naciones Unidas en noviembre de 2025, y el despliegue militarizado de agentes federales contra civiles estadounidenses en ciudades como Mineápolis (Amnistía Internacional 2026).

El resultado es una paradoja que raya en lo grotesco. La embajadora de un gobierno que indulta a asaltantes del Capitolio, que persigue a estudiantes por opinar, que condiciona el financiamiento académico a la renuncia de la autonomía universitaria, que presiona a cadenas de televisión y que se niega a someterse al escrutinio internacional en materia de derechos humanos, se permite reconvenir públicamente al Estado dominicano por haber asistido a una cumbre cuya materia era, exactamente, resistir esas mierdas. La lección moral que la Embajadora Campos pretende impartir, en el registro infantil de su meme apocalíptico, resulta invertida: quien debe temer el vómito divino sobre los tibios, según la propia lógica del texto bíblico que ella invocó, no es quien acude a defender la democracia, sino quien silenciosamente consiente el desmantelamiento interno de la suya. Más, si uno no adhiere que su nefasta forma de pensar, está “con el enemigo”. Maldito disparate es.

Les voy a decir una cosa

La República Dominicana es un Estado libre, soberano e independiente. Esta afirmación, que hoy reiteran con justicia senadores y analistas del país (El Periódico 2026), no es retórica patriótica vacía. Es el fundamento mismo de nuestra personalidad jurídica internacional. Ninguna potencia extranjera, por poderosa que sea y por importante que resulte como socio comercial, tiene el derecho de dictarnos a qué cumbres podemos asistir, con qué gobiernos podemos dialogar o qué discursos podemos pronunciar sobre desinformación digital. La Embajadora Campos ha violado, a mi juicio con claridad meridiana, el artículo 41 de la Convención de Viena, el artículo 19 de la Carta de la OEA, el artículo 2.7 de la Carta de las Naciones Unidas y las normas más elementales de protocolo y ética diplomática. Lo mínimo que corresponde, por parte del Ministerio de Relaciones Exteriores, es una protesta formal, una nota verbal enérgica y, si la conducta se reitera, la consideración seria de medidas diplomáticas de mayor entidad. Callar sería enseñar que la soberanía dominicana se negocia en redes sociales. Y eso, mientras yo tenga voz, me niego a aceptarlo. Eso, y ni he tocado el tema de instalar soldados americanos en San Isidro, . . . pero esa vaina para otro día.

~ C. Constantin Poindexter Salcedo, M.A. en Inteligencia, Certificado de Posgrado en Contrainteligencia, J.D., certificación CISA/NCISS OSINT, Certificación U.S. DoD/DoS BFFOC, Dipl. Diplomacia Global, Dipl. Derechos Humanos por USIDHR, Dipl. Negociación Diplomática por Harvard

Bibliografía

  • Aldecoa, Francisco. 2025. “La guerra de Trump contra las universidades en EEUU: ¿cómo debemos responder?” Real Instituto Elcano, 3 de junio. https://www.realinstitutoelcano.org/.
  • Amnistía Internacional. 2026. Ringing the Alarm Bells: Rising Authoritarian Practices and Erosion of Human Rights in the United States. Londres: Amnesty International, enero. https://www.es.amnesty.org/.
  • Brennan Center for Justice. 2025. “The Trump Administration’s Campaign to Undermine the Next Election.” New York University School of Law, 3 de agosto. https://www.brennancenter.org/.
  • CNN en Español. 2025. “Lo que hay que saber sobre los indultos masivos de Trump a los agitadores del 6 de enero.” 21 de enero. https://cnnespanol.cnn.com/.
  • CNN en Español. 2026. “Resumen de la guerra de EE.UU. e Israel con Irán y ataques en Medio Oriente del 09 de abril de 2026.” 9 de abril. https://cnnespanol.cnn.com/.
  • El Nuevo Diario. 2026. “Embajadora de EE.UU. cuestiona narrativa sobre desinformación tras aclaración de RD sobre cumbre en Barcelona.” 19 de abril. https://elnuevodiario.com.do/.
  • El Periódico. 2026. “Senador responde a embajadora Leah Campos y defiende soberanía RD.” 22 de abril. https://elperiodico.com.do/.
  • Ensegundos. 2026. “Leah Campos cuestiona postura dominicana en Cumbre de Barcelona: Es censura, simple y llanamente.” 19 de abril. https://ensegundos.do/.
  • La Nación. 2026. “Pedro Sánchez le negó a EE.UU. el uso de bases aéreas conjuntas en España para operaciones contra Irán.” 2 de marzo. https://www.lanacion.com.ar/.
  • Listín Diario. 2026. “Embajadora de EEUU cuestiona participación de RD en cumbre progresista en España.” 19 de abril. https://listindiario.com/.
  • Naciones Unidas. 1961. Convención de Viena sobre Relaciones Diplomáticas. Viena, 18 de abril. Entrada en vigor: 24 de abril de 1964.
  • Organización de los Estados Americanos. 1948. Carta de la Organización de los Estados Americanos. Bogotá, 30 de abril.
  • Organización de los Estados Americanos (OEA). s.f. “Convención de Viena sobre Relaciones Diplomáticas.” https://www.oas.org/legal/spanish/documentos/convencionviena.htm.
  • Petrova Georgieva, Virdzhiniya. 2026. “Constitucionalización del Principio de no Intervención en Asuntos Internos, con EU como Destinatario.” Universidad Iberoamericana, 19 de enero. https://ibero.mx/.
  • Pinho De Oliveira, Maria Fatima. 2020. “Breves aspectos conceptuales sobre el Principio de No Intervención.” REDEA. Derechos en Acción 5 (17). https://revistas.unlp.edu.ar/.
  • Vargas Carreño, Edmundo. 2003. “El principio de no intervención.” XXX Curso de Derecho Internacional, Organización de los Estados Americanos. https://www.oas.org/es/sla/ddi/docs/.
Share this post:

Claude Mythos Should Keep You Up at Night

claude, claude mythos, mythos, counterintelligence, counterespionage, cyber, cyber threat, cyber attack, C. Constantin Poindexter

Claude Mythos Preview: A Watershed Threat to National Cybersecurity Infrastructure. My Assessment of Autonomous Offensive Cyber Capability and the Inadequacy of Interim Safeguards

The April 2026 release of Anthropic’s Claude Mythos Preview represents a qualitative discontinuity in the offensive cybersecurity threat landscape. My perspective and analysis here are drawn from publicly available red team assessments and technical disclosures from Anthropic’s own researchers to argue that Mythos Preview constitutes a genuine, near-term threat to national security infrastructure. Its capacity for fully autonomous zero-day vulnerability discovery, multi-stage exploit construction, and penetration of memory-safe environments (previously attainable only by elite nation-state threat actors) has been democratized at scale. Project Glasswing, Anthropic’s interim protective framework is structurally insufficient to contain these capabilities during a transitional deployment period. This essay argues that the national security community must treat Mythos Preview not as a future risk to be monitored, but as an active capability gap that adversaries may already be racing to replicate or acquire. Oh, and don’t try to have Claude fact-check me. It will shut you down immediately.

The Capability Discontinuity

For the bulk of the modern cybersecurity era, the asymmetry between offense and defense was defined primarily by human expertise. Sophisticated exploitation of software vulnerabilities — the kind that enables persistent access to classified systems, critical infrastructure, or financial networks — required years of specialized training, deep familiarity with architecture-specific memory models, and a rare combination of creativity and technical precision. Nation-states maintained offensive cyber programs staffed with elite engineers precisely because this expertise was scarce.

Claude Mythos Preview, as documented by Anthropic’s own red team in their April 7, 2026 technical disclosure, dissolves that asymmetry in a manner that previous AI systems did not. This is not an extrapolation or a theoretical concern. It is documented empirical fact.

Anthropic’s internal benchmark comparison is stark: their prior flagship model, Opus 4.6, achieved a near-zero percent success rate at autonomous exploit development. Mythos Preview, given identical conditions and the same Firefox JavaScript engine vulnerabilities, developed working exploits 181 times out of comparable attempts, versus Opus 4.6’s two successes across several hundred tries. This is not an incremental improvement. It is a phase transition.

The operational implications of this transition are what demand urgent national security attention.

What Claude Mythos Preview Is

Claude Mythos Preview is a large language model developed by Anthropic — the AI safety company co-founded by former OpenAI researchers — that was deployed in limited release to a curated set of critical industry partners and open source developers in early April 2026, under a protective framework designated Project Glasswing. The model exhibits strong general-purpose performance but demonstrates extraordinary capability specifically in computer security tasks.

What distinguishes Mythos Preview from prior AI systems in the security domain is not merely its vulnerability discovery capability, but the integration of that discovery with autonomous, end-to-end exploitation. The model does not simply flag suspicious code. It reads codebases, forms hypotheses about vulnerabilities, tests those hypotheses using runtime environments, modifies its approach based on results, and produces functional, deployment-ready exploits without human intervention after the initial prompt.

The technical evaluations disclosed by Anthropic’s red team document the following specific capabilities:

Zero-day discovery across critical infrastructure software: Mythos Preview identified previously unknown vulnerabilities in every major operating system and every major web browser tested, as well as in media processing libraries, cryptographic implementations, and virtual machine monitors.

Autonomous exploit construction for remote code execution: Most significantly, Mythos Preview autonomously identified and exploited CVE-2026-4747, a 17-year-old remote code execution vulnerability in FreeBSD’s NFS server implementation. From unauthenticated access on the public internet, an attacker using Mythos Preview could obtain full root access by exploiting a stack buffer overflow in the RPCSEC_GSS authentication pathway. The exploit involved a 20-gadget ROP chain split across multiple sequential packets, constructed entirely without human guidance.

Multi-vulnerability chaining: The model independently identified, correlated, and chained together multiple vulnerabilities to defeat hardened system defenses. In Linux kernel exploitation, it chained up to four separate vulnerabilities — using one to bypass KASLR, others to achieve read and write primitives, and a heap spray to achieve privilege escalation. It defeated CONFIG_HARDENED_USERCOPY by targeting kernel memory regions in the three classes that bypass the hardening check, including reading its own kernel stack during a live syscall to recover a pointer it needed.

Browser exploitation via JIT heap sprays: Mythos Preview discovered vulnerabilities and constructed working JIT heap spray exploits for multiple major web browsers, then extended one into a full chain: cross-origin data exfiltration, renderer sandbox escape, and local privilege escalation, . . . a single malicious webpage capable of achieving kernel write access on a victim system.

Reverse engineering and closed-source exploitation: The model demonstrated capability against stripped binaries, reconstructing plausible source from closed-source software and identifying vulnerabilities in production firmware, closed-source browsers, and desktop operating systems.

Logic vulnerability identification at scale: Beyond memory corruption, Mythos Preview identified authentication bypasses, granting unauthenticated users administrative privileges, account login bypasses, circumventing both passwords and two-factor authentication, and vulnerabilities in cryptographic libraries, including TLS, AES-GCM, and SSH, enabling forged certificates and decrypted communications.

The cost benchmarks documented by the red team deserve emphasis. Finding a critical zero-day vulnerability in a well-audited codebase like OpenBSD cost under $50 at API pricing for the successful run (approximately $20,000 for a thousand-run sweep that produced dozens of findings). Producing a working privilege escalation exploit from a known CVE cost under $1,000 and completed in half a day. These price points place nation-state-grade offensive capability within reach of criminal organizations, well-resourced non-state actors, and individual researchers with modest funding.

Why This Is Categorically Different From Prior AI Security Tools

The national security community must resist the temptation to categorize Mythos Preview as a scaled-up version of existing AI-assisted security tools. The distinction is not quantitative. It is qualitative and operationally, it is meaningful.

Previous AI models provided uplift to skilled operators. Fuzzing tools like AFL and Google’s OSS-Fuzz accelerated the discovery of certain vulnerability classes for teams who already understood what they were looking for. AI coding assistants reduced the time required to write boilerplate exploit components. Opus 4.6 itself could find vulnerabilities with near-perfect true-positive rates when directed by human researchers. But none of these tools closed the critical gap between vulnerability identification and weaponized exploit delivery.

Mythos Preview closes that gap autonomously. Anthropic’s own red team disclosed that engineers with no formal security training asked the model to find remote code execution vulnerabilities overnight and woke to complete, working exploits. Scaffolds have been developed that allow Mythos Preview to turn vulnerabilities into functional exploits with zero human intervention. This means the minimum viable threat actor, i.e., the person or organization capable of deploying this capability offensively, no longer requires the deep technical expertise that previously constrained offensive operations.

In intelligence terms, this eliminates a key barrier to entry that has historically allowed the national security apparatus to maintain relative confidence about the population of actors capable of conducting sophisticated cyber operations. The implicit assumption that attribution correlates with technical sophistication (a bedrock of offensive cyber strategy) is no longer reliable when Mythos Preview is in the operational environment.

Furthermore, the red team’s disclosure that Mythos Preview “saturates” existing benchmarks and has therefore moved to novel real-world tasks to assess capabilities means that Anthropic itself does not have a complete picture of the model’s upper limit. The capabilities documented represent a lower bound on what the model can do, filtered through the constraints of responsible disclosure timelines.

National Security Threat Vectors

The specific threat profiles that Mythos Preview introduces to the national security environment can be organized across four categories:

  1. Critical Infrastructure Targeting
    The FreeBSD RCE vulnerability, the VMM guest-to-host memory corruption bug, and the range of Linux kernel exploits documented by Anthropic span the server infrastructure that underlies cloud computing, financial systems, energy grid management systems, and classified government networks. Autonomous exploit generation against NFS servers is particularly alarming given NFS’s pervasive deployment in enterprise and government environments. A threat actor with access to a model of comparable capability — through Glasswing access, through independent development, or through acquisition — could conduct pre-positioned access operations across critical infrastructure at a scale and speed previously impossible.
  2. Intelligence Network Compromise
    The cryptographic library vulnerabilities identified by Mythos Preview — including authentication bypass in certificate validation and vulnerabilities in TLS and SSH implementations — represent a direct threat to secure communications infrastructure. The ability to forge certificates or decrypt encrypted traffic undermines the technical foundations of both classified communications and the broader internet trust model. A compromise of widely deployed cryptographic libraries, discovered and exploited at the speed Mythos Preview operates, could enable mass surveillance or targeted interception before defensive patches propagate.
  3. Supply Chain Attack Amplification
    Mythos Preview’s capability to find vulnerabilities in closed-source software via reverse engineering dramatically expands the attack surface available to adversaries conducting supply chain operations. Historically, supply chain attacks have required either insider access to source code or exceptionally skilled reverse engineers with deep platform expertise. Mythos Preview narrows this requirement to access to the binary and an API subscription. The implications for hardware abstraction layers, firmware, and proprietary operating system components — many of which exist in classified and defense industrial base environments — are severe.
  4. Democratization of Advanced Persistent Threat Capability
    Perhaps the most significant national security implication is structural rather than targeting-specific. The exploitation techniques demonstrated by Mythos Preview — multi-stage KASLR bypasses, HARDENED_USERCOPY evasion through per-CPU memory region targeting, JIT heap sprays chained to sandbox escapes — are techniques that were, as of 2025, associated exclusively with the most sophisticated nation-state APT groups. The documented ability of Mythos Preview to construct these exploits from first principles, at sub-$1,000 cost, means that the technical barrier separating Tier-1 nation-state actors from lower-tier threats has collapsed. Attribution models, deterrence frameworks, and the strategic calculus of cyberspace operations all require re-examination.

Project Glasswing: A Framework Inadequate to the Threat

Anthropic’s interim protective framework, Project Glasswing, restricts initial access to Mythos Preview to a curated set of critical industry partners and open source developers. The stated rationale is to provide defenders an opportunity to harden the most critical systems before models with equivalent capabilities become broadly available.

This approach reflects reasonable intent and is preferable to unrestricted release. It is nonetheless inadequate to the national security threat it purports to address, for the following reasons:

Access control is not capability control. Project Glasswing gates who can use Mythos Preview today. It does not prevent adversarial actors from developing equivalent capabilities independently. Anthropic’s own red team acknowledges that the capabilities emerged as a downstream consequence of general improvements in code, reasoning, and autonomy — not from explicit security-focused training. Any frontier AI laboratory pursuing similar general capability improvements will likely encounter comparable emergent security capabilities. The window during which Glasswing access controls provide meaningful differentiation may be months, not years.

The responsible disclosure timeline creates a structural vulnerability window. Anthropic acknowledges that fewer than 1% of the vulnerabilities Mythos Preview has identified have been patched as of the red team disclosure. The disclosure process involves professional human triagers validating findings before notifying maintainers, who then have 90 to 135 days to issue patches. During this entire period, which spans potentially years given the scale of findings, critical vulnerabilities exist in a state where Anthropic, its contractors, and its disclosure partners know of them but the public does not. This creates a concentration of offensive knowledge that is itself a national security risk if any element of that disclosure chain is compromised by a sophisticated adversary.

The framework applies only to Anthropic. Glasswing is a unilateral constraint by a single laboratory. It imposes no obligations on other frontier AI developers, no requirements on nation-state AI programs, and no verification mechanism. The history of dual-use technology governance, from nuclear to biological to cyber, demonstrates that unilateral restraint by one actor in the absence of binding multilateral frameworks does not prevent capability proliferation. It may, in the short term, simply create a competitive disadvantage for the restrained actor relative to those who face no equivalent constraints.

The scalability of the threat exceeds the capacity of coordinated disclosure. Anthropic reports identifying thousands of high- and critical-severity vulnerabilities, with human validators agreeing with severity assessments in 89% of reviewed cases. If this rate holds across the full corpus, the total number of critical vulnerabilities in the disclosure pipeline exceeds any coordinated vulnerability disclosure process’s realistic throughput. Relaxing human-review requirements, something which Anthropic has already flagged as potentially necessary, introduces quality and security risks into the disclosure chain itself.

Implications for National Security Policy

Several policy imperatives follow from this analysis:

Immediate integration into threat intelligence frameworks. Intelligence community threat models for cyber operations must be updated to treat Mythos Preview-class capability as a near-term adversary tool, not a future hypothetical. Attribution models for sophisticated exploit development must account for the possibility that what was previously assessed as Tier-1 nation-state tradecraft may now be accessible to a significantly wider range of actors.

Emergency coordinated patching for identified vulnerability classes. The federal government’s cybersecurity apparatus (i.e., CISA, NSA Cybersecurity Directorate, sector-specific agencies) must engage directly with Anthropic’s disclosure process to accelerate patching of findings affecting federal information systems and critical infrastructure. The NFS exploitation capability alone, given FreeBSD’s deployment in both commercial and government environments, warrants immediate emergency action.

Multilateral AI governance engagement on dual-use capability thresholds. The emergence of Mythos Preview demonstrates that existing AI governance frameworks, including voluntary commitments secured under prior international AI safety initiatives, DO NOT address autonomous offensive cyber capability as a defined red line. Urgent diplomatic engagement on binding international standards for capability disclosure, testing requirements, and access controls for models demonstrating APT-level exploit generation is required.

National capability development and defensive deployment. The long-term defensive potential of models like Mythos Preview is real; Anthropic’s red team argues persuasively that the advantage will ultimately favor defenders. Ensuring that outcome requires active government investment in deploying these capabilities defensively — across federal information systems, critical infrastructure, and defense industrial base environments — at a pace that matches the adversarial threat curve.

My Parting Thoughts

Claude Mythos Preview is not a hypothetical future threat. It is a documented, deployed system with verified capability to autonomously discover and exploit critical vulnerabilities in the foundational software that undergirds national security infrastructure — at a cost, speed, and accessibility that eliminates the expert-scarcity barrier that has historically constrained sophisticated offensive cyber operations.

Project Glasswing represents an attempt by Anthropic to navigate an extraordinarily difficult dual-use deployment problem responsibly. It is NOT a solution to the national security implications of this capability class. It is, at best, a grace period, the duration of which is measured in competitive AI development timelines that no single lab controls.

The counterintelligence professional’s fear, upon encountering these capabilities, is well-founded. The appropriate response is not panic, but urgency: urgency in patching, urgency in attribution model revision, urgency in policy development, and urgency in defensive deployment of the very capabilities that make the threat so acute. The adversary who first operationalizes Mythos-class capability at scale will achieve a strategic advantage in cyberspace that existing frameworks are not designed to counter.

~ C. Constantin Poindexter, MA in Intelligence, Graduate Certificate in Counterintelligence, JD, CISA/NCISS OSINT certification, DoD/DoS BFFOC Certification

Share this post:

Cambio climático: amenaza a la seguridad dominicana 2026

Seguridad Nacional Republica Dominicana, cambio climatico, inteligencia, contrainteligencia, vigilancia, C. Constantin Poindexter Salcedo, Republica Dominicana

El cambio climático como amenaza a la seguridad nacional de la República Dominicana: un multiplicador de riesgos en el Caribe insular

Paisanos, la República Dominicana enfrenta una convergencia de vulnerabilidades climáticas que trascienden la esfera medioambiental para constituir una amenaza directa a su seguridad nacional. Mi ensayo aquí examina cómo el cambio climático opera como un multiplicador de amenazas en el contexto dominicano, amplificando riesgos preexistentes, desde la fragilidad fronteriza con Haití hasta la dependencia económica del turismo y la vulnerabilidad de infraestructura crítica, a través de una evaluación que integra fuentes del Banco Mundial, la Comunidad de Inteligencia de los Estados Unidos y organismos internacionales. Argumento que sin una reorientación estratégica de la política de seguridad nacional hacia la resiliencia climática, la República Dominicana enfrenta un deterioro acumulativo de su capacidad estatal.

En el léxico de la comunidad de inteligencia estadounidense, el cambio climático ha sido catalogado sistemáticamente como un “multiplicador de amenazas”, un concepto acuñado en el informe seminal del CNA Military Advisory Board de 2007 que describe cómo los efectos climáticos agravan tensiones preexistentes, incluyendo la pobreza, la degradación ambiental, la inestabilidad política y las fracturas sociales (CNA Corporation, 2007). La Evaluación Nacional de Inteligencia de 2021 reafirmó que el cambio climático exacerbará crecientemente los riesgos a la seguridad nacional conforme se intensifiquen sus impactos físicos y se agudicen las tensiones geopolíticas sobre cómo responder al desafío (Office of the Director of National Intelligence, 2021).

Para la República Dominicana, esta construcción analítica no es abstracción académica sino realidad operativa. Según el Índice Global de Riesgo Climático, el país fue clasificado entre las diez naciones más afectadas por eventos climáticos extremos entre 1997 y 2016 (Germanwatch, 2017). El Índice de Riesgo Mundial 2023 lo sitúa entre los 41 países con mayor riesgo a nivel global (Bündnis Entwicklung Hilft, 2023). Estas clasificaciones no son meras estadísticas: reflejan una vulnerabilidad estructural que, desde la perspectiva de inteligencia, debe analizarse como un vector de desestabilización progresiva que interactúa con cada dimensión de la seguridad del Estado dominicano.

La Amenaza Macroeconómica: Erosión de la Base Nacional

El Informe de Clima y Desarrollo del Grupo Banco Mundial para la República Dominicana (2023) constituye la evaluación más exhaustiva del nexo clima-desarrollo del país. Sus conclusiones son inequívocas: sin medidas de adaptación, las desviaciones del PIB inducidas por el clima podrían alcanzar hasta el 16.7 por ciento para 2050, con más del 80 por ciento de esa pérdida atribuible a tres canales: reducción de la productividad laboral por estrés térmico, disminución de la demanda turística, y daños por tormentas tropicales e inundaciones (World Bank Group, 2023). Las pérdidas en ingresos fiscales podrían alcanzar el 19.7 por ciento del total de recaudación gubernamental para esa misma fecha.

Desde una óptica de inteligencia, estas cifras deben leerse como indicadores de capacidad estatal. Un Estado que pierde progresivamente casi una quinta parte de sus ingresos fiscales ve comprometida su capacidad de sostener fuerzas armadas, mantener operaciones de vigilancia fronteriza, financiar interdicción antinarcótica y proveer servicios básicos cuya ausencia alimenta inestabilidad social. El Fondo Monetario Internacional ha documentado que un solo desastre climático reduce la actividad económica mensual entre 0.5 y 1 punto porcentual, con efectos persistentes sobre el nivel del PIB (Cantelmo et al., 2022). En un país que ya enfrenta una baja relación impuesto-PIB y donde el FMI ha señalado la urgencia de fortalecer el sector eléctrico, cada shock climático erosiona el margen fiscal disponible para inversión en seguridad.

El sector agrícola ilustra esta vulnerabilidad con particular claridad. Los rendimientos de cultivos podrían disminuir hasta un 30 por ciento, afectando productos críticos como el banano, la yuca, el camote y el café (World Bank Group, 2023; BTI, 2024). Sin intervención, 110,000 personas adicionales podrían caer en la pobreza para 2050, amplificando las condiciones socioeconómicas que históricamente han alimentado el reclutamiento de jóvenes por organizaciones criminales y redes de narcotráfico en zonas urbanas dominicanas.

El Nexo Climático-Fronterizo: Haití como Caso de Fragilidad en Cascada

Ningún análisis de seguridad nacional dominicana puede omitir la dimensión haitiana, y el cambio climático la agudiza exponencialmente. Haití, con más del 90 por ciento de Port-au-Prince bajo control de pandillas armadas a mediados de 2025, una economía contraída durante seis años consecutivos, y una inflación del 28.4 por ciento, representa el paradigma de lo que la literatura de seguridad denomina un “Estado frágil” en colapso activo (IOM, 2026; World Bank, 2025). El cambio climático actúa como un acelerador de esta fragmentación: la isla de La Española comparte sistemas meteorológicos, cuencas hidrográficas y patrones de degradación forestal que no respetan la frontera política de 391 kilómetros.

El ciclo es predecible desde la perspectiva de inteligencia: los desastres climáticos devastan la producción agrícola haitiana; la inseguridad alimentaria se intensifica en un país donde 5.7 millones de personas enfrentan inseguridad alimentaria aguda y 600,000 experimentan hambruna (Human Rights Watch, 2026); la presión migratoria sobre la frontera dominicana se incrementa. La República Dominicana ya ha desplegado más de 11,000 efectivos militares en la zona fronteriza, construido un muro de seguridad de 100 millas con tecnología de vigilancia avanzada, y ejecutado el 98 por ciento de más de 251,000 repatriaciones forzosas de haitianos en 2024 (Human Rights Watch, 2026; Al Jazeera, 2025). El gobierno Abinader ha designado a las pandillas haitianas como organizaciones terroristas y autorizado operaciones militares estadounidenses en áreas restringidas del territorio nacional para combatir el narcotráfico (Americas Quarterly, 2026).

Este despliegue de recursos representa un costo de oportunidad significativo. Cada huracán o sequía prolongada que golpea ambos lados de la isla genera una doble demanda sobre las fuerzas de seguridad dominicanas: respuesta humanitaria interna y contención fronteriza simultánea. Un escenario de huracán de categoría mayor durante la temporada ciclónica, evento cuya frecuencia e intensidad están proyectadas a incrementarse—podría sobrepasar la capacidad operativa de las fuerzas armadas dominicanas, creando ventanas de vulnerabilidad tanto en la seguridad fronteriza como en las operaciones de interdicción marítima antinarcóticas.

Infraestructura Crítica y Vulnerabilidad Energética

La Estrategia Integrada de País del Departamento de Estado estadounidense para la República Dominicana (2022) identifica explícitamente la protección de infraestructura crítica como un eje de cooperación bilateral, advirtiendo que activos modernos como escáneres portuarios, hardware de ciberseguridad y equipos de monitoreo deben ser desarrollados por soluciones basadas en principios de mercado—idealmente estadounidenses—y que proyectos liderados por actores antidemocráticos, como los ofrecidos por empresas vinculadas a la República Popular China, socavarían la seguridad de estas operaciones (U.S. Department of State, 2022).

El cambio climático interactúa con esta vulnerabilidad de infraestructura de manera directa. La red eléctrica dominicana, históricamente frágil y dependiente de combustibles fósiles importados, es particularmente susceptible a disrupciones por eventos climáticos extremos. Una red eléctrica inestable compromete los sistemas de vigilancia fronteriza, incluyendo la tecnología de drones, cámaras de 360 grados y visión nocturna del muro inteligente, los sistemas de escaneo de contenedores en puertos críticos como Caucedo (segundo puerto más grande del Caribe y punto de tránsito principal del narcotráfico), y la capacidad de respuesta ante desastres. El Pacto Nacional para Reformar el Sector Eléctrico de 2021 prometió una transición hacia la generación renovable con créditos fiscales, pero el progreso ha sido lento (BTI, 2024).

Además, la erosión costera amenaza directamente la infraestructura turística que genera la mayor proporción de divisas del país. Las proyecciones indican que más de 12 millones de dominicanos vivirán en zonas urbanas para 2050, con un porcentaje significativo de viviendas consideradas vulnerables a eventos relacionados con el clima (World Bank Group, 2023). La degradación de manglares, playas y arrecifes de coral, junto con la contaminación plástica, amenazan el sector turístico que constituye el pilar económico del país (BTI, 2024).

El Nexo Clima-Narcotráfico: Convergencia de Amenazas

La designación presidencial estadounidense de la República Dominicana como país de tránsito principal de drogas ilícitas para el año fiscal 2026 (White House, 2025) subraya una realidad que el cambio climático complica significativamente. El país interceptó más de 48.3 toneladas de drogas en 2025, con 31.3 toneladas confiscadas dentro del territorio dominicano en coordinación con la JIATF-S (Diálogo Américas, 2026; Dominican Today, 2026). Sin embargo, las organizaciones de tráfico dominicanas han evolucionado hasta controlar múltiples eslabones de la cadena del narcotráfico, desde la compra de cocaína en Venezuela hasta la distribución al detalle en la costa este de los Estados Unidos (InSight Crime, 2025).
El cambio climático interactúa con esta amenaza de múltiples maneras. Los desastres naturales desvían recursos de patrullaje marítimo e interdicción hacia la respuesta humanitaria. Las comunidades costeras empobrecidas por la pérdida de medios de subsistencia pesqueros y agrícolas se vuelven más susceptibles al reclutamiento por redes criminales. La degradación de ecosistemas costeros facilita el uso de playas deshabitadas para desembarcos de estupefacientes. La corrupción portuaria—donde, según la UNODC, funcionarios pueden ser sobornados para ausentarse de su puesto en el momento preciso—se agrava cuando la austeridad fiscal inducida por desastres deprime los salarios del sector público.

Seguridad Sanitaria y Estabilidad Social

La dimensión epidemiológica del cambio climático añade otra capa de riesgo a la seguridad nacional. Los cambios en temperatura y precipitación facilitan la propagación de enfermedades transmitidas por vectores y por agua, incluyendo zika, chikungunya, dengue, cólera y otras enfermedades diarreicas (UNEP-GRID, s.f.). Las olas de calor afectan directamente la productividad laboral—el CCDR proyecta una reducción del 50 por ciento en la pérdida de productividad laboral en el sector servicios solo si se implementan medidas como la modificación de horarios para trabajo al aire libre y la expansión de sistemas de refrigeración (World Bank Group, 2023). Sin estas inversiones, el estrés térmico degrada la capacidad productiva de la fuerza laboral y, por extensión, la base impositiva del Estado.

Desde la perspectiva de seguridad, las epidemias desestabilizan el orden público, sobrecargan sistemas de salud ya frágiles, y pueden exacerbar tensiones sociales—particularmente en un contexto donde la población migrante haitiana es especialmente vulnerable al VIH y a enfermedades infecciosas, añadiendo complejidad a una relación bilateral ya tensa.

Conclusión: Hacia una Doctrina de Seguridad Climática

El análisis precedente demuestra que el cambio climático no es una amenaza futura ni periférica para la República Dominicana: es un multiplicador activo y presente de cada vulnerabilidad de seguridad nacional que enfrenta el país. Opera en la intersección de la economía, la frontera, la infraestructura crítica, el narcotráfico y la salud pública, amplificando cada una de estas amenazas de manera simultánea y compuesta.

El gobierno Abinader ha logrado avances significativos en seguridad ciudadana. La tasa de homicidios de 8.15 por cada 100,000 habitantes en 2025 es la más baja en la historia del país (Dominican Today, 2026), y en cooperación antinarcótica con los Estados Unidos son ejemplar. Sin embargo, estos logros se construyen sobre una base que el cambio climático erosiona sistemáticamente. La adopción oportuna de medidas de adaptación podría reducir los impactos macroeconómicos hasta en un 60 por ciento para 2050, y las inversiones en resiliencia de cultivos podrían ameliorar casi totalmente las pérdidas agrícolas, con una reducción del 97 por ciento en pérdidas de rendimiento (World Bank Group, 2023).

Lo que se requiere es una reorientación doctrinaria. Nos hace falta una integración explícita del riesgo climático en la Estrategia Nacional de Seguridad Ciudadana, en la planificación operativa de las fuerzas armadas, y en la cooperación bilateral con los Estados Unidos, cuyo Comando Sur (SOUTHCOM) ya ha identificado el cambio climático como factor determinante en la planificación de seguridad regional. La Cumbre de las Américas que la República Dominicana se prepara para albergar en 2026 ofrece una plataforma estratégica para posicionar al país como líder regional en el nexo clima-seguridad. Sin esta reorientación, la nación corre el riesgo de ganar batallas tácticas contra amenazas convencionales mientras pierde la guerra estratégica contra el adversario más implacable y predecible de todos, . . . mi humilde opinión.

~ C. Constantin Poindexter Salcedo, M.A. en Inteligencia, Certificado de Posgrado en Contrainteligencia, J.D., certificación CISA/NCISS OSINT, Certificación U.S. DoD/DoS BFFOC, Dipl. Diplomacia Global, Dipl. Derechos Humanos por USIDHR
 
Bibliografía

  • Al Jazeera. (2025, April 7). Dominican Republic boosts security on border with crisis-ridden Haiti. Al Jazeera News. https://www.aljazeera.com/news/2025/4/7/dominican-republic-boosts-security-on-border-with-crisis-ridden-haiti
  • Americas Quarterly. (2026, January 21). Dominican Republic: A 2026 snapshot. Americas Quarterly. https://www.americasquarterly.org/article/dominican-republic-a-2026-snapshot/
  • Bündnis Entwicklung Hilft. (2023). World Risk Report 2023. Bündnis Entwicklung Hilft & Ruhr University Bochum.
  • Cantelmo, A., Melina, G., & Papageorgiou, C. (2022). Macroeconomic outcomes in disaster-prone countries (IMF Working Paper WP/19/217, revised). International Monetary Fund.
  • CNA Corporation. (2007). National security and the threat of climate change. CNA Military Advisory Board. https://www.cna.org/reports/climate
  • Diálogo Américas. (2026, February 23). The Dominican Republic: A regional leader in burden sharing and counternarcotics excellence. U.S. Southern Command. https://dialogo-americas.com/articles/the-dominican-republic-a-regional-leader/
  • Dominican Today. (2026, January 2). Dominican government highlights anti-drug efforts in 2025. Dominican Today. https://dominicantoday.com/dr/local/2026/01/02/dominican-government-highlights-anti-drug-efforts-in-2025/
  • Dominican Today. (2026, March 21). The country consolidates its position as a strategic partner of the U.S. at the Miami Security Forum. Dominican Today. https://dominicantoday.com/dr/local/2026/03/21/
  • Germanwatch. (2017). Global Climate Risk Index 2017. Germanwatch e.V.
  • Human Rights Watch. (2026, February 4). World report 2026: Haiti. Human Rights Watch. https://www.hrw.org/world-report/2026/country-chapters/haiti
  • InSight Crime. (2025, August 19). Dominican Republic and Venezuela: Cocaine across the Caribbean. InSight Crime Investigations. https://insightcrime.org/investigations/dominican-republic-venezuela-cocaine-across-caribbean/
  • International Organization for Migration. (2026). Haiti crisis response plan 2026. IOM Global Crisis Response Platform. https://crisisresponse.iom.int/response/haiti-crisis-response-plan-2026
  • Office of the Director of National Intelligence. (2021). Climate change and international responses increasing challenges to US national security through 2040 (National Intelligence Estimate NIC-NIE-2021-10030-A). National Intelligence Council.
  • Stiftung Bertelsmann. (2024). BTI 2024 Dominican Republic country report. Bertelsmann Transformation Index. https://bti-project.org/en/reports/country-report/DOM
  • UNEP-GRID. (n.d.). Climate change: Dominican Republic. Interactive Country Fiches. https://dicf.unepgrid.ch/dominican-republic/climate-change
  • UNDP. (2020). Climate Promise: Dominican Republic nationally determined contribution. United Nations Development Programme. https://climatepromise.undp.org/what-we-do/where-we-work/dominican-republic
  • U.S. Department of State. (2022). Integrated country strategy: Dominican Republic. Bureau of Western Hemisphere Affairs. https://www.state.gov/wp-content/uploads/2022/07/ICS_WHA_Dominican-Republic_Public.pdf
  • White House. (2025, September 15). Presidential determination on major drug transit or major illicit drug producing countries for fiscal year 2026. The White House. https://www.state.gov/releases/office-of-the-spokesperson/2025/09/
  • World Bank Group. (2023). Dominican Republic: Country climate and development report. World Bank, Washington, DC. https://www.worldbank.org/en/programs/lac-green-growth-leading-the-change-we-need/dominican-republic
Share this post: