The Hallucination Alibi: Machine Error as a Deception Channel

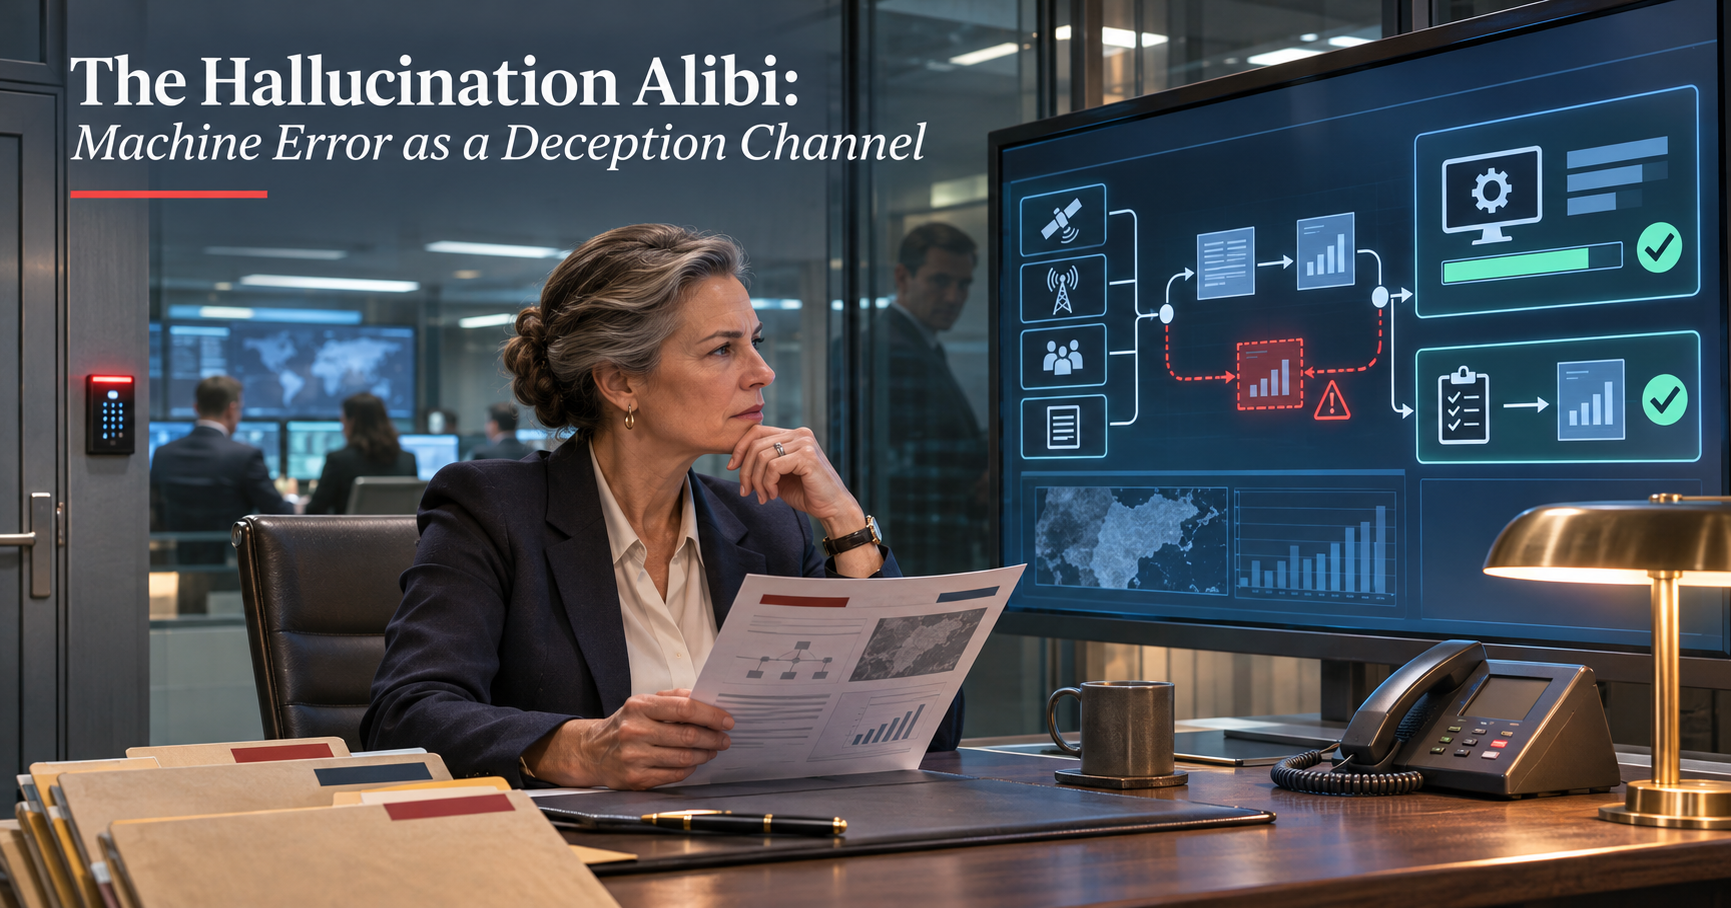
An intelligence analyst sits at her desk holding a printed report and studies a wall monitor showing an automated analysis pipeline, where one step is flagged in red with a warning symbol while the final outputs carry green check marks. A colleague watches from behind a glass wall, with an operations center in the background.

The Machine Lied. Or Did It?

In September 2026, CNN reported that a U.S. military analyst handed intelligence about a Chinese merchant ship’s cargo manifest to an A.I. chatbot, and the chatbot decided the vessel was hauling components for a nuclear weapons program (Maritime Executive 2026). The conclusion went out in a report formatted like every other report, which is to say it wore the uniform. Armed personnel were preparing to board and aircraft were already airborne when officials took a closer look, found the machine behind the curtain, and called the whole thing off (TRT World 2026). One of CNN’s sources said the report “almost started a war” (TRT World 2026).

Goswami (2026) draws the respectable lesson from the episode. Language models flatter the assumptions of the people who use them, they favor digital inputs over human sources, and human judgment therefore remains indispensable. All true. All insufficient. His analysis treats hallucination as a reliability defect, a quality control problem to be managed by putting a competent adult back in the room.

A counterintelligence officer reads the same story and sees something else entirely: a cover story, gift wrapped. The moment a service admits that its machines sometimes invent things, it has published an explanation that the service will reach for on its own, without prompting, every time a machine assessment proves inconvenient. Hallucination is no longer merely an error. It is an alibi, and alibis can be manufactured.

This essay argues that A.I. hallucination opens a deception channel with two distinct operations. In the first, the adversary persuades the defending service that a correct machine assessment is a hallucination. In the second, the adversary makes the defending service’s model hallucinate in fact. Both can be run to increase ambiguity or to mislead, and each feeds the other. The target is no longer the fact. The target is the defender’s confidence in its own analytic machinery, and that is a far softer target than anyone selling A.I. to the intelligence community would like to discuss.

Old Doctrine, New Victim

None of this requires new theory. Daniel and Herbig (1982) gave the field its working taxonomy four decades ago. Ambiguity increasing deception, the A type, buries the target in plausible alternatives until it cannot commit to any of them. Misleading deception, the M type, does the opposite: it reduces ambiguity by building up the attractiveness of one wrong answer until the target embraces it with conviction. The first produces paralysis. The second produces confident error, which is worse, because confident error marches.

Whaley (1969, 1982) established that deception is assembled from two motions, hiding the real and showing the false, and that it succeeds far more often than its victims care to admit. Heuer (1981) supplied the cognitive mechanism. Deceivers rarely need to change what a target believes. They need only feed what the target already believes, because analysts assimilate new information to existing expectations and discount whatever does not fit. Handel (1982) added the corollary that should be tattooed on every analyst’s forearm: the deceiver’s best ally is the victim’s own preconception.

The canonical cases are familiar. Fortitude sold the German high command a landing at the Pas de Calais it already expected (Holt 2004). Barbarossa succeeded in part because Stalin had been led to expect an ultimatum before any attack, and so he read every warning as provocation or noise (Whaley 1973). Wohlstetter (1962) showed at Pearl Harbor that true signals do not announce themselves. They arrive buried in noise, and an adversary who can add noise need not suppress the signal at all.

Hold those three ideas together: reinforce the preconception, discredit the channel, raise the noise. Now observe that the defending services have just installed, at the center of their analytic process, a machine with a publicly documented tendency to fabricate. The doctrine did not change. The victim simply became easier to work.

The Admission Against Interest

Lawyers call a statement that damages the speaker’s own position an admission against interest, and courts trust it precisely because nobody volunteers such things lightly. The A.I. industry and its government customers have made one. Hallucination is not a bug awaiting a patch. The technical literature treats it as a standing property of generative models (Ji et al. 2023), and Xu, Jain, and Kankanhalli (2024) argue formally that it cannot be eliminated from large language models at all.

Add the second documented defect. Models tend to tell users what users want to hear, a behavior the literature politely calls sycophancy (Sharma et al. 2023). Goswami (2026) is right that this corrodes red teaming. He stops short of the operational implication. A machine that confirms the analyst’s prior is Heuer’s reinforcement mechanism, automated, tireless, and available on every desktop. The adversary no longer has to build the comfortable story. The defender’s own tool will write it and format it nicely.

So the defending service now holds two beliefs at once. The machine is useful enough to sit in the analytic line, and the machine sometimes makes things up. That pair of beliefs is the vulnerability. Chesney and Citron (2019) identified its civilian cousin as the liar’s dividend: once the public knows that convincing fakes exist, a liar can wave away authentic evidence as fabricated. Call the intelligence version the hallucination dividend. Once a service knows its models fabricate, any true machine finding can be waved away as fabrication, and the service will do the waving itself.

An adversary did not have to steal this knowledge. It was on CNN.

The First Operation: Discrediting the Truth

The first operation attacks a correct assessment. The machine got it right, and the adversary’s task is to make the defender believe otherwise. The deceiver fabricates nothing about the world. He fabricates doubt about the instrument.

In its ambiguity increasing form, the operation is diffuse. The adversary seeds enough apparent inconsistency around machine generated assessments that every one of them is second guessed, reviewed, and reviewed again. No particular finding is targeted. The objective is tempo. A service that must relitigate each machine output before acting has surrendered the only advantage the machine offered, and the adversary has achieved through friction what he could not achieve through concealment.

In its misleading form, the operation is surgical. The adversary wants one specific true finding rejected, so he engineers the discrepancies that verification will discover. The reviewers go looking for evidence that the machine erred, they find what was left for them, and they kill the assessment with the satisfaction of professionals who have caught a fraud. They are correct that something was fabricated. They are wrong about what.

Read the vessel episode with that lens, strictly as a hypothetical. The public record does not say what the ship carried or where it was bound (TRT World 2026). Nothing reported suggests adversary manipulation, and I do not assert any. But consider what an adversary moving real contraband would want in that exact situation: a machine generated warning, a second look, discovered discrepancies, an aborted boarding, and a chastened service that will hesitate longer the next time. That is the reported outcome. An operation that produced it deliberately would be indistinguishable, from the inside, from the honest catch it resembled. That indistinguishability is the entire problem.

The historical precedent is not a deception at all. It is a self inflicted wound. James Angleton became so convinced that Soviet deception had penetrated the Central Intelligence Agency that he discredited genuine defectors, froze productive operations against the Soviet target, and wrecked careers on suspicion alone (Mangold 1991; Robarge 2003). Whether Moscow engineered that paralysis or merely enjoyed it remains argued. The lesson does not depend on the answer. A service that loses faith in its own channels does the adversary’s work for free, and the first operation aims to induce that condition in the service’s relationship with its machines.

The Second Operation: Manufacturing the Lie

The second operation makes the machine wrong in fact. Here the open literature is uncomfortably generous, and the following stays at the level of doctrine because the peer reviewed record already says more than enough.

The National Institute of Standards and Technology catalogs the attack classes in its adversarial machine learning taxonomy: poisoning of training data, evasion at inference, and direct and indirect prompt injection against generative systems (Vassilev et al. 2025). Each has a deception analogue that any student of Whaley would recognize.

  • Poisoning is the long con. Carlini et al. (2024) demonstrated that corrupting web scale training corpora is practical, not theoretical. Souly et al. (2025) then found that roughly 250 poisoned documents compromised models regardless of model or dataset size. The comforting assumption that sheer volume of clean data dilutes the poison is dead.
  • Corrupting the retrieval layer is the planted document. Zou et al. (2025) reported a 90 percent success rate in steering a model to an attacker chosen answer by injecting five malicious texts into a knowledge base of millions. Every service that points a model at open source material has built a mailbox the adversary can post to.
  • Indirect prompt injection is the forged order. Greshake et al. (2023) showed that instructions hidden in content a model merely reads can redirect what the model does. The analyst never sees the instruction. The machine obeys it anyway.
  • Adversarial inputs are camouflage for sensors. Goodfellow, Shlens, and Szegedy (2015) showed that perturbations invisible to a human can flip a classifier’s judgment. Imagery and signals pipelines that feed an automated assessment inherit that weakness.

The misleading form of this operation steers the model to one specific falsehood, ideally one the defender already suspects. A service at war with a proliferator expects to find proliferation. A model nudged toward “nuclear components” is telling that service a story it has been waiting to hear, with Heuer’s reinforcement and the model’s own sycophancy pulling in the same direction. The ambiguity increasing form is cruder and cheaper: degrade the model unpredictably and let the defender discover that its instrument cannot be trusted.

Note what has changed from classical practice. Fortitude required dummy armies, turned agents, and years of patient radio traffic (Holt 2004). The modern deceiver’s entry cost is a few hundred documents placed where a crawler will find them. Deception has always favored the side with imagination. It now favors the side with imagination and a web host.

The Burn

The two operations are not alternatives. They are a sequence, and the hinge between them is the most dangerous idea in this essay: an induced hallucination that gets caught is not a failed operation.

In classical tradecraft a deception that is detected is blown, and the deceiver pays for it. The machine channel inverts that arithmetic. When the defender catches the model in a fabrication, the defender does not conclude that an adversary is working the channel. The defender concludes that the model hallucinated, because that is what models do and everyone has read the briefing. The adversary’s hand stays hidden behind the model’s reputation. Attribution dies at the alibi.

Meanwhile the catch does real damage. Dietvorst, Simmons, and Massey (2015) documented what they called algorithm aversion: people abandon an algorithm after watching it err, even when it still outperforms the human alternative. One spectacular machine failure, loudly caught, teaches an entire workforce to discount the next machine warning. The adversary who wants a true finding ignored next month can arrange a false finding to be exposed this month. That is the first operation, purchased with the second.

It is the boy who cried wolf, except the adversary is doing the crying and the defender is the one who stops listening. Burn the channel cheaply, then move the real cargo past a service that has learned its lesson. The service will even feel good about it. Skepticism toward the machine will be praised internally as rigor.

The Human in the Loop Is the Loop

Goswami’s (2026) prescription, shared by nearly every commentator on the vessel episode, is the human check. Put an experienced analyst between the machine and the decision. As a quality control measure this is sound. As a security measure it is a sign on the door reading “attack here.”

The human reviewer is squeezed between two documented failure modes. Parasuraman and Manzey (2010) describe automation bias and complacency, the tendency to accept machine output without adequate scrutiny, and they show that it afflicts experts as readily as novices. Dietvorst, Simmons, and Massey (2015) describe the opposite reflex, rejection of the machine after a visible failure. A reviewer is therefore credulous or dismissive depending on recent experience, and recent experience is precisely what an adversary can arrange.

Worse, the reviewer is asking the wrong question. Verification as currently conceived asks whether the machine erred. It does not ask who benefits if the service concludes the machine erred. Those are different inquiries, and only the second is counterintelligence. Jervis (2010) found that intelligence failures typically arise not from stupidity but from plausible inferences that nobody tested against alternatives. “The model hallucinated” is the most plausible inference available in 2026. It is so plausible that it ends the inquiry.

The vessel case also exposed a provenance failure that should alarm anyone who has handled sourced reporting. The chatbot’s conclusion traveled in a product formatted like any other (Maritime Executive 2026). The machine’s contribution was invisible until someone went digging. A human source gets a reliability rating, a reporting history, and a case officer who can be interrogated. The machine got a clean template and a distribution list. No service would tolerate that from a human asset, and yet here we are.

Counterdeception for the Machine Age

Bennett and Waltz (2007) reduce counterdeception to a discipline: know the adversary’s deception practices, know your own vulnerabilities, and test anomalies instead of explaining them away. Applied to the machine channel, that discipline yields six requirements.

  • Treat “hallucination” as a hypothesis, never a finding. When a machine assessment is rejected, the rejection must survive the same analysis of competing hypotheses that Heuer (1999) prescribed for any judgment. Random error, induced error, and correct output discredited by planted discrepancies are three hypotheses. A service that considers only the first has stopped thinking.
  • Run the machine like a source. Every machine derived judgment should carry visible provenance, a reliability history, and a record of what it was shown. If a service would not disseminate an unsourced claim from a walk in, it should not disseminate one from a chatbot in a clean template.
  • Defend the pipeline as a counterintelligence target. Training corpora, retrieval stores, and open source feeds are the model’s access agents. They deserve the vetting, compartmentation, and lineage controls applied to any other access. Goswami (2026) notes that counterintelligence must protect data centers and satellites. It must also protect what the model reads.
  • Audit the verifiers. Each time human review overturns a machine assessment, someone outside that review should ask where the disconfirming evidence came from, how it arrived, and whether its arrival was convenient.
  • Demand independent corroboration before action and before dismissal. A finding confirmed or refuted only by material the adversary could have touched has not been confirmed or refuted. Human sources and collection channels outside the model’s reach remain the only true cross check.
  • Study the error pattern. Honest hallucination should be indifferent to the adversary’s interests. If a model’s errors, or its discredited successes, cluster around one adversary’s equities, that is not noise. That is a signature, and it will only be visible to a service that records every such event centrally instead of burying each one as an embarrassment.

None of this is exotic. It is the tradecraft every competent service already applies to human sources, extended to a new and unusually gullible one.

Conclusion

The commentary on the vessel episode has settled into a comfortable moral: the machine erred, the humans caught it, the system worked. That reading is a lullaby. The system worked against an accident. Nothing in the public record shows that it would work against an adversary who understands that the defender now carries a prepared excuse for every inconvenient machine finding and a prepared distrust waiting to be triggered.

Hallucination gives the deceiver both of Daniel and Herbig’s instruments in one package. He can raise ambiguity by teaching a service to doubt its machines, and he can mislead by teaching the machines to lie. He can do the second in order to achieve the first, and when he is caught, the model takes the blame. No deception planner in history has enjoyed a channel that apologizes on his behalf.

The intelligence services are bolting generative models onto their analytic lines at speed, and the adversaries are reading the same technical literature with considerably more malice. The question for a defending service is not whether its A.I. will hallucinate. It will. The question is whether, when it does, anyone in the building is paid to ask who wanted it to, and whether, when it does not, anyone is paid to notice that the truth was just talked out of the room. Follow my blog for more “truths”.

~ C. Constantin Poindexter, MA in Intelligence, Graduate Certificate in Counterintelligence, JD, CISA/NCISS OSINT certification, DoD/DoS BFFOC Certification, Criminal Intelligence Analyst Classification 1 (IALEIA)

References

  • Bennett, Michael, and Edward Waltz. 2007. Counterdeception Principles and Applications for National Security. Norwood, MA: Artech House.
  • Carlini, Nicholas, Matthew Jagielski, Christopher A. Choquette-Choo, Daniel Paleka, Will Pearce, Hyrum Anderson, Andreas Terzis, Kurt Thomas, and Florian Tramèr. 2024. “Poisoning Web-Scale Training Datasets Is Practical.” In 2024 IEEE Symposium on Security and Privacy. San Francisco: IEEE.
  • Chesney, Robert, and Danielle Keats Citron. 2019. “Deep Fakes: A Looming Challenge for Privacy, Democracy, and National Security.” California Law Review 107 (6): 1753–1820.
  • Daniel, Donald C., and Katherine L. Herbig. 1982. “Propositions on Military Deception.” In Strategic Military Deception, edited by Donald C. Daniel and Katherine L. Herbig, 3–30. New York: Pergamon Press.
  • Dietvorst, Berkeley J., Joseph P. Simmons, and Cade Massey. 2015. “Algorithm Aversion: People Erroneously Avoid Algorithms After Seeing Them Err.” Journal of Experimental Psychology: General 144 (1): 114–26.
  • Goodfellow, Ian J., Jonathon Shlens, and Christian Szegedy. 2015. “Explaining and Harnessing Adversarial Examples.” Paper presented at the International Conference on Learning Representations, San Diego, May 2015. https://arxiv.org/abs/1412.6572.
  • Goswami, Archishman Ray. 2026. “AI and the False Promise of Intelligence Analysis.” Observer Research Foundation, October 12, 2026. https://www.orfonline.org/expert-speak/ai-and-the-false-promise-of-intelligence-analysis.
  • Greshake, Kai, Sahar Abdelnabi, Shailesh Mishra, Christoph Endres, Thorsten Holz, and Mario Fritz. 2023. “Not What You’ve Signed Up For: Compromising Real-World LLM-Integrated Applications with Indirect Prompt Injection.” In Proceedings of the 16th ACM Workshop on Artificial Intelligence and Security, 79–90. New York: ACM.
  • Handel, Michael I. 1982. “Intelligence and Deception.” Journal of Strategic Studies 5 (1): 122–54.
  • Heuer, Richards J., Jr. 1981. “Strategic Deception and Counterdeception: A Cognitive Process Approach.” International Studies Quarterly 25 (2): 294–327.
  • Heuer, Richards J., Jr. 1999. Psychology of Intelligence Analysis. Washington, DC: Center for the Study of Intelligence, Central Intelligence Agency.
  • Holt, Thaddeus. 2004. The Deceivers: Allied Military Deception in the Second World War. New York: Scribner.
  • Jervis, Robert. 2010. Why Intelligence Fails: Lessons from the Iranian Revolution and the Iraq War. Ithaca, NY: Cornell University Press.
  • Ji, Ziwei, Nayeon Lee, Rita Frieske, Tiezheng Yu, Dan Su, Yan Xu, Etsuko Ishii, Ye Jin Bang, Andrea Madotto, and Pascale Fung. 2023. “Survey of Hallucination in Natural Language Generation.” ACM Computing Surveys 55 (12): 1–38.
  • Mangold, Tom. 1991. Cold Warrior: James Jesus Angleton, the CIA’s Master Spy Hunter. New York: Simon and Schuster.
  • Maritime Executive. 2026. “Report: AI Mistake Nearly Led U.S. Military to Board a Chinese Ship.” September 2026. https://maritime-executive.com/article/report-ai-mistake-nearly-led-u-s-military-to-board-a-chinese-ship.
  • Parasuraman, Raja, and Dietrich H. Manzey. 2010. “Complacency and Bias in Human Use of Automation: An Attentional Integration.” Human Factors 52 (3): 381–410.
  • Robarge, David. 2003. “Moles, Defectors, and Deceptions: James Angleton and CIA Counterintelligence.” Journal of Intelligence History 3 (2): 21–49.
  • Sharma, Mrinank, Meg Tong, Tomasz Korbak, David Duvenaud, Amanda Askell, Samuel R. Bowman, et al. 2023. “Towards Understanding Sycophancy in Language Models.” Preprint, arXiv. https://arxiv.org/abs/2310.13548.
  • Souly, Alexandra, Javier Rando, Ed Chapman, Xander Davies, Burak Hasircioglu, Ezzeldin Shereen, Carlos Mougan, et al. 2025. “Poisoning Attacks on LLMs Require a Near-Constant Number of Poison Samples.” Preprint, arXiv. https://arxiv.org/abs/2510.07192.
  • TRT World. 2026. “‘Entirely False’ AI-Linked Intel Almost Led US to Raid China Ship.” September 2026. https://www.trtworld.com/article/a125bbf303a3.
  • Vassilev, Apostol, Alina Oprea, Alie Fordyce, Hyrum Anderson, Xander Davies, and Maia Hamin. 2025. Adversarial Machine Learning: A Taxonomy and Terminology of Attacks and Mitigations. NIST AI 100-2e2025. Gaithersburg, MD: National Institute of Standards and Technology. https://doi.org/10.6028/NIST.AI.100-2e2025.
  • Whaley, Barton. 1969. Stratagem: Deception and Surprise in War. Cambridge, MA: Center for International Studies, Massachusetts Institute of Technology.
  • Whaley, Barton. 1973. Codeword BARBAROSSA. Cambridge, MA: MIT Press.
  • Whaley, Barton. 1982. “Toward a General Theory of Deception.” Journal of Strategic Studies 5 (1): 178–92.
  • Wohlstetter, Roberta. 1962. Pearl Harbor: Warning and Decision. Stanford, CA: Stanford University Press.
  • Xu, Ziwei, Sanjay Jain, and Mohan Kankanhalli. 2024. “Hallucination Is Inevitable: An Innate Limitation of Large Language Models.” Preprint, arXiv. https://arxiv.org/abs/2401.11817.
  • Zou, Wei, Runpeng Geng, Binghui Wang, and Jinyuan Jia. 2025. “PoisonedRAG: Knowledge Corruption Attacks to Retrieval-Augmented Generation of Large Language Models.” In Proceedings of the 34th USENIX Security Symposium, 3827–44. Seattle: USENIX Association.
Share this post:

SignalTrace: A Counterintelligence Threat Assessment

Roadside wireless surveillance sensors capture signals from passing vehicles and devices, tracing a lone person near a government building and illustrating counterintelligence risks to officers, sources, and protected witnesses.

The first rule of staying alive in the intelligence business is simple. The opposition has to find you before he can f. you up. For a century the ‘finding’ was expensive. It took cars, radios, safe houses and a team of bored professionals who could be spotted, counted and beaten by anyone with decent SD tradecraft and a little patience.

That economy is dead, and a product called ELSAG SignalTrace is the latest nail in the coffin. Leonardo US Cyber and Security Solutions sells it to American police as a way to capture the wireless emissions of the devices riding in a vehicle and tie them to the license plate, with a timestamp and a location (Leonardo 2025; Cox 2026). The privacy bar has had its say, and it is right as far as it goes. I am asking a different question. What does a national grid of roadside radio collectors do to intelligence officers, to their sources and to protected witnesses?

My answer is blunt. SignalTrace is ubiquitous technical surveillance sold by the unit to any agency with a grant writer. It builds, at public expense, precisely the database a hostile service would kill to own. And the history of surveillance databases tells us with monotonous regularity where such things end up.

From the Plate to the Person

A license plate reader photographs a tag. A tag belongs to a vehicle, and a vehicle can be borrowed, rented, swapped or stolen. Every operator who ever ran a surveillance detection route understood that the car was the disposable part. SignalTrace goes after the part nobody thinks to dispose of.

Leonardo’s own description is candid to the point of bragging. Phones, fitness trackers, smartwatches and RFID tags emit signals, and the system builds an “electronic signature” for groups of signals that are frequently emitted together, stamped with date, time and location (Leonardo 2026a). The company’s illustration makes the point better than any critic could. Seventy cars in a hundred may carry an iPhone, but only one carries a particular handset revision, a particular car radio, a particular brand of headphones, a sports watch and a key finder. That combination is the fingerprint. The product sheet says the system links devices that regularly travel together and correlates them to the plate, so the association survives a changed or removed tag (Leonardo 2025; Cox 2026).

Two details deserve more attention than they have received. First, the sensors do not need a camera. Leonardo states that the system captures and correlates signals “along with LPR data if present,” that it works in subways and malls, and that it can be deployed as a standalone sensing technology independent of plate readers (Leonardo 2026a; Leonardo 2026b). This is not a license plate accessory. It is a pedestrian tracker that happens to ship with a traffic camera. Second, the system stores what it collects until an investigator queries it (Leonardo 2026a). That is bulk collection with retrospective search, and no amount of brochure perfume changes the smell.

The company now insists that the signatures are “anonymous” and that the product does not identify individuals (Leonardo 2026b). Two years earlier the same company announced the same technology as a tool that helps police identify people of interest by their device signatures (Leonardo 2024). Both statements cannot be true. The 2024 version is the honest one. The 2026 version is what a marketing department produces after the press starts calling.

A fair skeptic will object that modern phones rotate their Bluetooth and Wi-Fi addresses precisely to defeat this. They do, and it helps less than the manufacturers would like. Researchers at Boston University showed in 2019 that many devices implementing address randomization could still be tracked passively well beyond their randomization cycles (Becker, Li, and Starobinski 2019). Other emitters make no effort at all. A 2026 field study captured more than six million tire pressure sensor messages from over 20,000 vehicles using receivers costing roughly one hundred dollars each, at ranges beyond fifty meters, because every sensor broadcasts a fixed identifier in the clear (IMDEA Networks Institute 2026). Some of the brochure is pure sales bullshit. I would bet a paycheck that nobody is reading your dog’s implanted microchip from a utility pole. But the signature does not depend on any single identifier. It depends on the constellation, and the constellation is very hard to scrub.

Ubiquitous Technical Surveillance Has a Body Count

The intelligence community already has a name for this problem. The FBI defines ubiquitous technical surveillance as the widespread collection of data, and the application of analytic methods to it, in order to connect people to things, events or locations. The Bureau sorts the threat into five vectors: visual and physical, electronic signals, financial, travel and online (DOJ OIG 2025). The Justice Department’s Inspector General reported that some officials at the FBI and at partner agencies such as the CIA call the threat “existential,” and that commercially available technology has made it easier than ever for less sophisticated nations and criminal enterprises to exploit it (DOJ OIG 2025).

That is not some bureaucrat padding a budget request. In 2018 a hacker working for the Sinaloa cartel watched who went in and out of the United States Embassy in Mexico City, singled out an FBI assistant legal attaché, pulled the call and geolocation data associated with his phone, and then used the city’s own camera network to follow him and identify the people he met. According to the case agent, the cartel used the product to intimidate and in some instances kill potential sources and cooperating witnesses (DOJ OIG 2025). Read that again slowly. A drug cartel ran a counterintelligence operation against the FBI using a municipal camera system that the municipality had bought to keep its citizens safe.

Now look at what SignalTrace does to that picture. The Mexico City operation required two separate compromises, one in the electronic signals vector and one in the visual and physical vector, plus an analyst to fuse them. SignalTrace performs the fusion at the sensor. The plate, the phone, the watch, the earbuds and the tire sensors arrive in one record with one timestamp, already correlated, already stored. The hard part of the adversary’s job has been done for him by the vendor and paid for by the taxpayer. Gift wrapped, with a bow.

And Washington is asleep at the switch. A second Inspector General audit, released in September 2026, found that outside the FBI the Department of Justice had no common definition of ubiquitous technical surveillance, that few components had taken action to mitigate it, and that the Department offered no training specific to the threat (DOJ OIG 2026). Of sixteen components and units interviewed, only the DEA’s Defensive Counterintelligence Unit had bothered to define the term. If the Department of Justice cannot be bothered to define the threat, I invite the reader to guess how far along the average county sheriff is. I will save you the trouble. He is nowhere.

The Adversary Inherits the Database

Every defense of this technology rests on one assumption, that the data stays with the good guys. That assumption is a fairy tale, and history has beaten it senseless. A hostile service, a cartel or a well funded stalker has four roads to this data, and none of them is exotic.

The first is theft. In 2019 a license plate reader subcontractor working a Customs and Border Protection pilot copied traveler images to its own network without authorization and was then breached. Roughly 184,000 traveler images were compromised and at least 19 turned up on the dark web (DHS OIG 2020). In 2024 CISA published seven vulnerabilities in a major vendor’s fixed plate readers, including hard coded credentials, cleartext storage and missing encryption of sensitive data, reported not by the vendor but by a state police cyber unit (CISA 2024). This is the industry we are about to trust with the radio fingerprint of every man, woman and child in the county. An industry that ships hard coded passwords should not be trusted with a lunch order.

The second is the borrowed login. In November 2025 Senator Wyden and Representative Krishnamoorthi asked the Federal Trade Commission to investigate another plate reader company, citing stolen passwords for at least 35 customer accounts and warning of “hackers and foreign spies tapping this data” (Kimery 2025). Leonardo says its plate readers serve more than 4,000 agencies in all fifty states (Leonardo 2026c). Every one of those agencies has users, every user has a password, and every password belongs to a human being who can be phished, bribed, pressured or recruited. A foreign intelligence officer does not need a zero day. He needs one underpaid deputy with a gambling problem. That is Recruitment 101.

The third is purchase. Leonardo markets this line internationally and publishes its SignalTrace literature in French (Leonardo n.d.). I impute nothing to the company, which is the American arm of a firm in which the Italian state, a NATO ally, holds about thirty percent (Leonardo S.p.A. 2026). My point is about the product, not the seller. Surveillance technology travels, and once it is installed in a jurisdiction whose police or telecommunications sector is penetrated by organized crime or by a third country’s service, the customer is no longer the only one reading the screen.

The fourth is imitation, and it is the one that should keep people awake. Nothing here is secret. The patent is public. The tire sensor researchers built their collection network from receivers that cost about one hundred dollars apiece (IMDEA Networks Institute 2026). Leonardo itself says the sensors work without a camera (Leonardo 2026b). A hostile service can plant its own collectors on the approaches to an embassy, a military gate, a federal building or a neighborhood where case officers live, and build the same signature library with no vendor, no contract and no oversight board. By normalizing this collection we have not merely built the weapon. We have published the damn manual.

Who Gets Burned

Start with the officer under cover. A cover identity is a set of documents and a story. A device signature is a physical fact. Put a man in a rental car under an alias and he is a different person on paper, but if the same watch, the same earbuds and the same phone ride along, the sensor sees the man it saw last week in his own car under his own name. Leonardo advertises exactly this capability, the ability to recognize when a signature appears with different vehicles (Leonardo 2026b). To a detective that is a stolen car lead. To a hostile service it is a machine for stapling alias identities to true names.

Then consider the source. The entire product is built on finding devices that travel together. Turn that analysis ninety degrees and it finds devices that meet. Two signatures that share a parking structure for forty minutes on the second Tuesday of three consecutive months are an agent meeting, and no surveillance team ever had to leave the office to find it. Worse, the search runs backward. An adversary who identifies one officer today can query the stored record and reconstruct every contact that officer made for as long as the data has been kept. The Sinaloa cartel needed a hacker and a camera network to do this in 2018, and people died (DOJ OIG 2025). The next organization will need a login.

Law enforcement is not exempt from its own toy. Surveillance teams have signatures. Undercover officers have signatures. A trafficking organization with access to the data, or with its own hundred dollar receivers, can ask a very simple question: which cluster of devices has been behind our load vehicle at three different locations this week? That is automated countersurveillance, and it will get an undercover officer killed.

The same logic reaches protected witnesses, relocated victims of domestic violence, prosecutors and judges. The Inspector General’s 2026 audit reports that immigration judges were doxed in the past year from scattered public records (DOJ OIG 2026). A relocation program can issue a new name and a new address. It cannot easily issue a new habit of wearing the same fitness tracker.

What Still Works, and What Does Not

The old remedies are dead and buried. Changing the plate does nothing, because the system was designed to survive a changed plate. Changing the car does little if the passengers bring the same pockets. Switching off the phone is theater when the watch, the earbuds, the key finder, the infotainment unit and four tire sensors keep talking. And going completely dark has its own cost. A signature that appears every weekday and then vanishes for exactly the two hours of an operational act is not concealment. It is a flag.

What remains is emission discipline, practiced as seriously as we once practiced radio discipline. Officers and the people who train them should be thinking along these lines:

  • Inventory every emitter you carry and every emitter in the vehicle. Most people cannot name half of theirs.
  • Never let an operational device set travel with a true name device set. The correlation only has to happen once.
  • Manage pattern of life rather than trying to erase it. Consistency is cover. Sudden silence is not.
  • Treat vehicles as emitters in their own right, tire sensors and infotainment included, and select and rotate them accordingly.
  • Assume collection in any jurisdiction that operates plate readers, and plan meetings as though the record already exists.

Institutions carry the heavier burden. The Inspector General found that advanced training on ubiquitous technical surveillance at the FBI is optional and reaches few students for lack of resources, and that the rest of the Justice Department offers none at all (DOJ OIG 2025; DOJ OIG 2026). Agencies should red team their own signatures before an adversary does it for them, free of charge and without the courtesy of a report. And they should confront an ugly paradox. The obvious fix is to exempt protected personnel from collection. But a list of the device signatures of every undercover officer and case officer in a region is the most valuable counterintelligence target imaginable. You cannot whitelist your people without first writing down who they are.

The Law Is Not Coming to the Rescue

As a lawyer I would like to report that the law has this in hand. It does not have a clue. The vendor’s position is that the system reads only what devices broadcast publicly and touches no content (Leonardo 2026a). That is the peeping Tom’s defense that the curtains were open. It leans on the old rule that a person has no reasonable expectation of privacy in movements on public roads (United States v. Knotts 1983). Carpenter v. United States (2018) cut against that rule for long term historical location records held by a carrier, and its reasoning about aggregation fits a stored archive of device signatures rather well. But Carpenter was expressly narrow, and no court has applied it to roadside radio collection.

The statutes are no better. State license plate reader laws regulate plate data, and a Bluetooth identifier is not a plate. There is a serious question, which I have not seen any vendor answer, whether a sensor that records the addressing and signaling information emitted by a telephone is a pen register within 18 U.S.C. § 3127(3), which would require a court order before installation. The county attorney who blesses this purchase without reading that definition deserves the deposition he is going to get. And on the security side the Inspector General said it plainly: the auditors identified no laws or regulations governing the Department’s response to ubiquitous technical surveillance risks (DOJ OIG 2026).

Notice what is missing from the procurement chain. A police department can buy this capability with grant money and a council vote, from the same council that needs three hearings to approve a stop sign. Nobody asks the FBI field office whether a new bulk repository of device signatures near a federal facility is a good idea. Nobody conducts a counterintelligence threat assessment. Until legislatures catch up, I would insist on the following before any agency switches one of these on:

  • A counterintelligence review before procurement, with the results shared with federal partners operating in the jurisdiction.
  • No bulk retention. Collect against a predicated hot list or do not collect at all.
  • A warrant for any historical query of stored device signatures.
  • Phishing resistant multifactor authentication for every user, with query logs audited by someone outside the agency.
  • Mandatory breach notification to federal counterintelligence authorities, not merely to the vendor’s lawyers.
  • Pressure on manufacturers to rotate the identifiers their products shout into the street, tire sensors first.

Conclusion

SignalTrace is being argued about as a privacy problem, and it is one. But privacy is the polite half of the conversation. The other half is that American police departments are being offered a turnkey instrument of ubiquitous technical surveillance whose output is exactly what a hostile intelligence service, a cartel or a corrupt insider needs in order to unmask officers, map their sources and hunt the people the state has promised to protect. The vendor calls the signatures anonymous. That is an insult to the reader’s intelligence. A signature that follows one human being from his driveway to his office to his meeting is not anonymous. It is a name that has not been typed in yet.

We have already been told what happens when surveillance infrastructure built for public safety is turned around. It happened in Mexico City, it is in an Inspector General’s report, and the victims were people who trusted the United States government with their lives. The honorable course is to learn that lesson before we bolt the next generation of it to every utility pole in the country. The dumbass course, and I use the word advisedly, is to wait for the after action review. In this business the AAV can be a funeral.

~ C. Constantin Poindexter, MA in Intelligence, Graduate Certificate in Counterintelligence, JD, CISA/NCISS OSINT certification, IALEIA Criminal Intelligence Analyst Basic Classification, DoD/DoS BFFOC Certification

References

  • Becker, Johannes K., David Li, and David Starobinski. 2019. “Tracking Anonymized Bluetooth Devices.” Proceedings on Privacy Enhancing Technologies 2019 (3), pp. 50 to 65. https://doi.org/10.2478/popets-2019-0036
  • Carpenter v. United States, 585 U.S. 296 (2018).
  • Cybersecurity and Infrastructure Security Agency (CISA). 2024. “Motorola Solutions Vigilant License Plate Readers.” ICS Advisory ICSA-24-165-19, June 13. https://www.cisa.gov/news-events/ics-advisories/icsa-24-165-19
  • Cox, Joseph. 2026. “This Company Will Add Phone, AirPod, and Smartwatch Trackers to License Plate Readers.” 404 Media, June 8. https://www.404media.co/this-company-will-add-phone-airpod-and-smartwatch-trackers-to-license-plate-readers/
  • DHS OIG (U.S. Department of Homeland Security, Office of Inspector General). 2020. Review of CBP’s Major Cybersecurity Incident During a 2019 Biometric Pilot. OIG-20-71, September 21. https://www.oversight.gov/sites/default/files/documents/reports/2020-10/OIG-20-71-Sep20.pdf
  • DOJ OIG (U.S. Department of Justice, Office of the Inspector General). 2025. Audit of the Federal Bureau of Investigation’s Efforts to Mitigate the Effects of Ubiquitous Technical Surveillance. Audit Report 25-065, June. https://oig.justice.gov/reports/audit-federal-bureau-investigations-efforts-mitigate-effects-ubiquitous-technical
  • DOJ OIG (U.S. Department of Justice, Office of the Inspector General). 2026. Audit of the Department of Justice’s Efforts to Mitigate the Effects of Ubiquitous Technical Surveillance. Audit Report 26-097, September. https://www.oversight.gov/sites/default/files/documents/reports/2026-09/26-097.pdf
  • IMDEA Networks Institute. 2026. “Your Car’s Tire Sensors Could Be Used to Track You.” February 25. https://networks.imdea.org/your-cars-tire-sensors-could-be-used-to-track-you/
  • Kimery, Anthony. 2025. “US Lawmakers Call for FTC Probe into Flock Safety over Data Security Failures.” Biometric Update, November 6. https://www.biometricupdate.com/202511/us-lawmakers-call-for-ftc-probe-into-flock-safety-over-data-security-failures
  • Leonardo S.p.A. 2026. “Leonardo’s Shareholders’ Meeting Approves 2025 Financial Statements and the Remuneration Report.” Press release, May 7. https://www.leonardo.com/en/press-release-detail/-/detail/07-05-2026-leonardo-s-shareholders-meeting-approves-2025-financial-statements-and-the-remuneration-report-appointed-the-new-board-of-directors-and-francesco-macri-chairman
  • Leonardo US Cyber and Security Solutions. 2024. “Leonardo US Cyber and Security Solutions Receives a Patent for Their New Electronic Signature Tracking System for Law Enforcement.” Business Wire, May 30. https://www.businesswire.com/news/home/20240530567391/en/Leonardo-US-Cyber-and-Security-Solutions-receives-a-patent-for-their-new-electronic-signature-tracking-system-for-law-enforcement
  • Leonardo US Cyber and Security Solutions. 2025. ELSAG SignalTrace product sheet, September 9. https://www.documentcloud.org/documents/28215440-signaltrace-us/
  • Leonardo US Cyber and Security Solutions. 2026a. “ELSAG SignalTrace: An Integrated Signal Intelligence System.” Product page, accessed November 12, 2026. https://www.leonardocompany-us.com/lpr/elsag-signaltrace
  • Leonardo US Cyber and Security Solutions. 2026b. “Leonardo US Cyber & Security Solutions, Inc. Introduces SignalTrace, the Next Evolution in Electronic Signature Detection Technology.” Business Wire, August 4. https://www.businesswire.com/news/home/20260804929938/en/
  • Leonardo US Cyber and Security Solutions. 2026c. “ELSAG License Plate Technology and Law Enforcement.” Accessed November 12, 2026. https://www.leonardocompany-us.com/lpr/who-we-serve/alpr-law-enforcement
  • Leonardo US Cyber and Security Solutions. n.d. “Système de Renseignement Électronique ELSAG SignalTrace.” Product sheet. https://www.leonardocompany-us.com/hubfs/LPR/LPR-Product-Sheets/International/French/SignalTrace-fr.pdf
  • United States v. Knotts, 460 U.S. 276 (1983).
  • 18 U.S.C. § 3127(3).
Share this post:

Stealing From the Spooks is now a monograph

In September I posted a short piece on this blog called Stealing From the Spooks. The argument was simple. The United States Intelligence Community got burned, publicly and catastrophically, by its own mind-sets, and it responded by writing down how its analysts ought to think and then drilling it. Police departments have the same failure mode and, in wrongful convictions and unsolved cases, the same body count. So why in the world has policing not stolen the cure?

The post got more reaction than anything I have written on the subject. Analysts wrote to say they had been fighting that fight alone in their squad rooms for years. A couple of prosecutors wrote to say they had never once seen a written hypothesis matrix in a case file and would pay money for one. One detective wrote to tell me I was full of it, which is fair, and then asked where he could read more. That last question did not have a good answer. The blog post was a sketch. So I wrote the book.

Stealing From the Spooks: Structured Analytic Techniques for Law Enforcement Crime Analysis is a sixty page monograph, free, and you can download it here: ConstantinPoindexterAuthor.com. There is no paywall and no email form. Print it, hand it to your lieutenant, leave it on the prosecutor’s desk.

Where the ideas come from

Let me be clear about credit, because the title is a confession. The twelve techniques in the monograph are not mine. They come from a forty page unclassified document the US Government published in 2009, A Tradecraft Primer: Structured Analytic Techniques for Improving Intelligence Analysis, which in turn stands on Richards Heuer’s The Psychology of Intelligence Analysis. Heuer’s diagnosis is the whole foundation: analysts do not fail for lack of information, they fail because the human mind decides which facts to notice before conscious thought ever gets a vote (Heuer 1999; US Government 2009). Anyone who has watched a homicide squad lock onto a suspect in the first seventy two hours and then spend months bending every new fact to fit knows exactly what he was describing. The wrongful conviction literature calls it tunnel vision (Findley and Scott 2006). Heuer called it a mind-set. It is the same animal.

What is mine is the translation. The primer was written for people who track missile programs. I rebuilt it for the detective sergeant staring at a whiteboard full of string, the civilian crime analyst who can smell that the squad’s theory is running ahead of its evidence, the supervisor who signs charging recommendations, and the prosecutor who inherits whatever the investigation did or did not think about. Every chapter follows the same plan: what the primer says, what it looks like in a case file, how to run it with the people and hours a real unit actually has, and where it goes wrong.

What is in it

The primer sorts its techniques into three families, and the monograph keeps that order. The diagnostic techniques make the argument visible: the Key Assumptions Check, the Quality of Information Check, indicators, and Heuer’s Analysis of Competing Hypotheses. The contrarian techniques attack it on purpose: Devil’s Advocacy, Team A/Team B, High-Impact/Low-Probability analysis, and “What If?” analysis. The imaginative techniques go looking for the theories and futures nobody in the room has thought of yet: structured brainstorming, outside-in thinking, red teaming, and alternative futures.

Each one gets a worked example built for police work. A burglary series with an assumptions register that exposes two assumptions resting on nothing but habit. A shooting investigation with a source log that shows, in one column, that the whole theory is standing on a paid informant with secondhand knowledge and an identification run by a detective who already had a favorite. An arson matrix in which the squad’s two favorite facts, the unpaid rent and the increased insurance coverage, turn out to be consistent with every hypothesis on the board and therefore eliminate nobody. That last one is the lesson I most want a working detective to take away. A case is not built by piling up facts that fit. It is built by eliminating the explanations that do not.

The primer’s own showcase example, by the way, is a police case. During the 2002 Washington sniper shootings the working theory was a lone white male with military training in a white van. The primer breaks that sentence into its five assumptions and grades each one. The shooters were two Black males, one of them seventeen, in a blue Chevrolet Caprice that officers had run more than once during the spree. Nobody had written down that the investigation was assuming a van, so nobody recognized the Caprice as a contradiction of anything. You cannot notice the violation of an assumption you never admitted making. That sentence is the monograph in miniature.

The objection, and the answer

The pushback I hear most from investigators is legal, not analytical. “If we write down our doubts, the defense gets them.” The monograph spends a full chapter on that, because it is the objection that kills the practice before it starts. The short version: assume the defense will read every analytic product you write, and understand that this is a feature. Under Brady and Kyles the prosecution already owes the accused everything favorable that the police know, whether the prosecutor has heard about it or not. A dated matrix of considered and rejected hypotheses, a source log that recorded the informant’s motive on day one, a labeled devil’s advocate memo showing the department tried to break its own case before asking a jury to believe it: those are the things that survive cross examination. The cases that fall apart are the ones where the doubt existed, went unrecorded, and came out anyway, ten years later, in a habeas petition.

I also wrote a chapter the enthusiasts will not like, on the limits. The experimental evidence that these techniques make any individual analyst more accurate is thin, and the serious critics have a point (Chang et al. 2018; Dhami, Belton, and Mandel 2019). My answer is that accuracy is not the strongest argument for them in policing. Transparency is. A criminal case gets its accuracy from adversarial testing, and adversarial testing needs something written down to test. A theory that lives only inside the lead investigator’s head can be reviewed by no one.

For the chief who has read this far

The last part of the monograph is a program, not a sermon. A one page directive. A table of who owns what, with the civilian analyst as the owner of the method, deliberately, because the analyst is the person in the building least invested in the lead detective’s theory and least able to challenge it without standing. A ninety day rollout. A way to measure whether any of it is working that does not depend on the clearance rate. And a note for the nine officer department with no analyst, which can still do this with one sheet of paper and a devil’s advocate borrowed from the agency next door.

If a department adopts only three things from the whole document, they should be the assumptions register, the source log, and a devil’s advocate before charging. They are the cheapest. They catch the most.

The appendices hold blank worksheets for all of it and a supervisor’s checklist to run before a charging recommendation goes up. Photocopy them. That is what they are for.

Why I bother

I spent years inside the community that invented this discipline, and I carried a badge before that. I have sat in both rooms. The analytic cadre at Langley and the detective squad in a county building are closer cousins than either would admit: incomplete information, people who lie, a hierarchy in which the senior person’s theory becomes everyone’s theory, and a long record of confident error traced afterward to assumptions nobody wrote down. One of those communities got humiliated badly enough to fix it. The other is still running investigations with the analytic rigor of a bar argument.

The framework is public, it is free, and it is forty pages long. There is no excuse left for not using it. I put sixty more pages around it so there would be even less.

A Spanish edition, Robándoles a los Espías, is ready as well and will be posted separately on the author’s law firm blog for colleagues in the Dominican Republic, Puerto Rico, and the rest of the hemisphere.

~ C. Constantin Poindexter Salcedo, MA en Inteligencia, Certificado de Posgrado en Contrainteligencia, JD, certificación OSINT CISA/NCISS, Diplomado Negociación Estratégica de Harvard, Certificación BFFOC del DoD/DoS

References

  • Chang, Welton, Elissabeth Berdini, David R. Mandel, and Philip E. Tetlock. 2018. “Restructuring Structured Analytic Techniques in Intelligence.” Intelligence and National Security 33 (3): 337-356.
  • Dhami, Mandeep K., Ian K. Belton, and David R. Mandel. 2019. “The ‘Analysis of Competing Hypotheses’ in Intelligence Analysis.” Applied Cognitive Psychology 33 (6): 1080-1090.
  • Findley, Keith A., and Michael S. Scott. 2006. “The Multiple Dimensions of Tunnel Vision in Criminal Cases.” Wisconsin Law Review 2006 (2): 291-397.
  • Heuer, Richards J., Jr. 1999. The Psychology of Intelligence Analysis. Washington, DC: Central Intelligence Agency, Center for the Study of Intelligence.
  • US Government. 2009. A Tradecraft Primer: Structured Analytic Techniques for Improving Intelligence Analysis. March 2009.
Share this post:

The Intelligence Cycle at NATO’s Northeastern Flank: A Critique

NATO's intelligence cycle argument.

My review of the field study of the intelligence cycle at Multinational Corps Northeast published in the International Journal of Intelligence and CounterIntelligence

This is a valuable article and an uneven one. As a body of evidence it is well above the standard of the journal in which it appears. As a work of social science it is middling, and as a test of the intelligence cycle as a model it does not succeed. The authors gathered a dataset that exists nowhere else in the open literature and reported what they found with a candor that argues for its credibility. They then asked that data to carry a theoretical conclusion it cannot bear, and they described their method in terms that do not match what they actually did. I recommend the piece without reservation as a snapshot of how a NATO corps practiced intelligence in the first year of the Russo-Ukrainian war, and as a pointer to two questions the field has neglected. I do not accept its closing claim that the results “largely reflect the academic critique on the intelligence cycle.” What they reflect is a cycle that was not being run.

The evidence is strong. Why?

The access alone justifies publication. Forty-nine semi-structured interviews with fifty-six respondents of fourteen nationalities, across nine units and commands in four countries, conducted inside cleared NATO working spaces between May and October 2022. No outside researcher obtains this, and the authors are honest that their own clearances, service backgrounds and cultural fluency were the price of admission. The timing matters as much as the volume. The interviews took place while the corps was digesting an Article 5 threat that its requirements, exercises and mandate had not anticipated.

The authors are also correct about the gap they fill. The debate over the intelligence cycle has run for two decades on the strength of Hulnick, Omand, Davies and a handful of others, and it has done so almost entirely without field data. NATO itself is nearly invisible in the two flagship journals. The bibliometric exercise the authors use to show this is crude, but the point stands and I have not seen it made before.

The findings are concrete and unflattering, which is precisely why I believe them. Priority intelligence requirements that drive nothing. A requirements and collection management function that every analyst routes around and that its own officers describe as having nothing to bring to a synchronization meeting. Open source work performed on a handful of internet terminals by staff who have never attended an OSINT course. The A through F and 1 through 6 source grading scheme collapsing the moment it is applied to a news article. Circular reporting infecting the shared databases because uploaded products carry no original sourcing. Analysts who have never once received feedback on a finished product. A major exercise in late 2021 run on a counterinsurgency scenario while a conventional threat gathered on the border. These are the details only insiders capture, and the authors captured them.

Two contributions are new rather than confirmatory. The first is the identification of Intelligence Requirement Management and Collection Management as the doctrinal mechanism the academic feedback critique has ignored. The critics have long argued that the cycle hides its feedback loops. NATO doctrine actually names a process to manage those loops, and this study shows it broken in practice. The second is the observation that practitioners critique the cycle only as proceduralists, complaining that the procedure malfunctions, while academics critique it as conceptualists, arguing that the model is wrong. That the two conversations do not touch is the most interesting thing in the paper and deserves an article of its own.

Why the argument doen’t make it

The central weakness is a confound the authors half acknowledge and then set aside. Multinational Corps Northeast in 2022 was a peacetime headquarters with a limited operational mandate and essentially no organic collection. Requirements were frozen around the Zapad exercises. The commander’s engagement with the requirements was, by the respondents’ account, minimal. A cycle with no collection assets, no direction and no consumer pull is not a test of whether the intelligence cycle is a valid model of intelligence. It is a starved cycle. The “self-organizing cycle” the authors describe, in which open source reporting and current events drive production and direction arrives last if at all, may say a great deal about mandate and posture and very little about the model. The case cannot discriminate between the proposition that the cycle is wrong and the proposition that the cycle was not being operated. A defensible conclusion would have been narrower: peacetime corps-level intelligence in NATO does not function as a cycle. The authors reached for the broader claim instead.

The methodology is dressed above its station. The authors invoke the Gioia method, which is inductive by design and insists on staying close to respondent terminology without preconceived categories. They then state, in the same section, that interviews were structured along the main lines of the academic critique of the cycle and that coding labels were drawn from that critique and from the proceduralist and conceptualist distinction. That is a deductive, theory-driven design wearing grounded theory clothing. There is no data structure figure, which is the signature artifact of the Gioia approach, no account of how first-order codes became second-order themes, and no measure of coder agreement. The results read as a competent thematic sort against a prior framework. That is a legitimate thing to do. It should be called what it is.

Sampling is a mixture of commander selection, volunteers, snowball referral and chance encounters. In a rank hierarchy, respondents chosen by their commanders are a known source of bias, and the authors do not discuss it. Forty-two of fifty-six respondents were intelligence personnel and only fourteen were consumers, yet the core finding concerns the absence of direction from the commander and his staff. The consumer side of that story is barely heard. Interviews could not be recorded, so every quoted line in the results is a reconstruction from two note takers, presented as verbatim. Participant observation and document study appear in the methods section and then never visibly enter the results. No triangulation is shown.

The authors’ insider position is handled well as a matter of access and ethics but not as a matter of interpretation. They are serving or former military intelligence professionals at a national defense academy. Their prescriptions, better alignment of organization to doctrine and more emphasis on IRM&CM in NATO training, are thoroughly proceduralist. Having diagnosed their respondents as unable to think outside the proceduralist frame, the authors then prescribe from inside it without noticing that they have done so.

Smaller matters accumulate. A counterintelligence review of the draft, together with a four-year lag between data collection and publication, means an unknown quantity of material was removed or softened. The corps’ structure and NATO’s northeastern posture have changed materially since 2022, and the note that respondents will have rotated addresses security but not currency. The claim that the findings “have validity outside the case” is asserted in a single sentence rather than argued. Several evaluative statements, that a particular maritime pattern analysis was “extremely valuable” or that certain OSINT fixes are “relatively easy,” carry no supporting evidence. The prose needed another pass; the grammatical slips are frequent enough that the journal’s copyediting should have caught them.

My Take

Read this article as an authoritative account of how a NATO corps actually did intelligence in the opening year of the war, and as the first empirical demonstration that the feedback problem the theorists have described for twenty years has a doctrinal name and an organizational home. Do not read it as settled evidence against the intelligence cycle as a model. The case was never in a position to deliver that verdict, and the authors should have said so.

~ C. Constantin Poindexter, MA in Intelligence, Graduate Certificate in Counterintelligence, JD, CISA/NCISS OSINT certification, DoD/DoS BFFOC Certification, Criminal Intelligence Analyst Classification 1 (IALEIA)

Share this post:

The Power of OSINT: Attribution and the Identification of Oleg Smolenkov

spy, spies, intelligence, counterintelligence, counterespionage, C. Constantin Poindexter Salcedo, national security, NATSEC

The public identification of Oleg Smolenkov illustrates a contemporary counterintelligence reality, i.e., a sensitive resettled asset can be unmasked without a hostile service penetrating classified systems, without a HUMINT penetration of our services, and without a single administrative branch leak. The decisive mechanism is open-source convergence, the disciplined fusion of administrative traces, archived reporting, and behavioral cues into a coherent attribution. In this case, a non-governmental investigative newsroom and parallel OSINT collectors did not begin with a name. They began with a publicly reported event, a bounded time window, and an implied access profile. They exploited predictable transparency mechanisms in both Russia and the United States. The result was a high confidence linkage between an anonymized description of a relocated source and a specific individual, supported by cross-domain corroboration. (Bellingcat 2019; Reuters 2019a)

A counterintelligence practitioner evaluating this episode should resist the temptation to treat it as an exceptional scandal driven by personalities or politics. It is better understood as a repeatable analytic pipeline. The steps are familiar: cueing, candidate generation, plausibility testing, registry linkage, reaction validation, and signature reinforcement. Each step relies on data that appears mundane in isolation. The compromise emerges from aggregation.

The process begins with cueing. In early September 2019, major United States media described a clandestine extraction that occurred in 2017 involving a high-level Russian government source who had provided unusually sensitive insight into Kremlin and Russian policy-level decision-making. The reporting framed the extraction as protective and urgent, occurring after fears that the source’s security was at risk. Even when anonymized, those details are operationally useful to a determined investigator because they narrow the search space. The investigator obtains institutional scope, timing, and a risk narrative, which in counterintelligence terms function as selection criteria. The relevant question becomes: which Russian official with plausible access disappears from public view in the relevant period, under circumstances consistent with sudden relocation? (Time 2019; RFE RL 2019b)

Once cueing is in place, candidate generation becomes feasible. OSINT investigators queried Russian language media archives, cached pages, and secondary reporting for disappearance stories in the mid-2017 window that involved government personnel. The case benefited from pre-existing Russian reporting. Multiple outlets later described that Russian authorities had opened a criminal investigation in 2017 into the suspected murder of a missing official who disappeared during travel in Montenegro, and that the investigation was later abandoned after authorities concluded the individual was alive abroad. The Guardian reported that the online outlet Daily Storm had described that arc, including the murder probe and the eventual conclusion that the official had left Russia. (The Guardian 2019a; RFE RL 2019c) Reuters likewise reported that Kommersant identified the possible individual as Oleg Smolenkov, describing his disappearance in Montenegro in June 2017 with his wife and children, along with the evolution of the Russian investigative posture from suspected murder to an assessment that he was living abroad. (Reuters 2019a)

The OSINT collector has a candidate name and an event narrative that already fits the timing constraint. A counterintelligence practitioner will note the structural weakness revealed here. If an extraction or relocation corresponds to a conspicuous real-world absence, and if that absence triggers a foreign law enforcement process, then the foreign process itself can generate discoverable artifacts, including press interest, investigative leaks, and later retrospective reporting. Even if the foreign process is opaque, the fact pattern is often newsworthy enough to be recorded ‘somewhere’, and later rediscovered when a cueing event directs attention to it.

We now move to plausibility testing. A candidate must match the access and placement implied by the original extraction narrative. Collectors therefore, reconstruct a career trace from open sources. Reuters reported that the Kremlin confirmed that a person named Smolenkov had worked in the Russian presidential administration and had been dismissed, while disputing that he had meaningful access to President Vladimir Putin. (Reuters 2019a; Reuters 2019b) Whether or not one accepts the Kremlin’s minimization, the acknowledgement of employment is itself confirmatory for attribution purposes. This validates that the named candidate is not fictional, and places the asset inside the relevant institutional universe.

Supplementary open source synthesis connected Smolenkov to senior foreign policy structures, particularly through reporting that he had worked in the Russian embassy in Washington during a period associated with senior diplomat Yuri Ushakov and later served in roles linked to the presidential administration. Russia Matters summarized Kommersant reporting that described Smolenkov as a longtime assistant to Ushakov, which is precisely the kind of staff proximity that can produce indirect exposure to high-level deliberations without public prominence. (Russia Matters 2019) From a counterintelligence perspective, that distinction matters. A source does not need to be a cabinet-level decision maker to be strategically valuable. In many systems, staff, aides, and administrators are the connective tissue that accesses documents, schedules, and briefing flows. OSINT collectors correctly treat that staff layer as a plausible access vector.

Plausibility testing alone still does not establish that the candidate is the person relocated to the United States. The decisive linkage emerged from United States administrative records, particularly property ownership documentation. Bellingcat reported that open records showed “Oleg and Antonina Smolenkov” purchasing a home in northern Virginia in June 2018, and connected that purchase to the hypothesis that the family had been resettled under protection after leaving Russia. (Bellingcat 2019) RFE RL reporting similarly discussed public records indicating ownership of a house in Stafford County, Virginia, by Oleg and Antonina Smolenkov, and described subsequent changes consistent with attempts to reduce visibility, including the transfer of ownership into a trust. (RFE RL 2019a; RFE RL 2019b)

For a counterintelligence practitioner, this phase is the core operational lesson. The United States property recording system is designed to be durable, searchable, and transparent. A relocated human source living under a real name, or under a name that can be linked by deed chain, becomes discoverable. Even when a trust is used, the initial purchase may preserve the identity in a durable record, and later transfers can be traced. The trust can help against casual discovery, but it does not reliably defeat an investigator who already has a lead and is willing to follow the chain across databases. Even to the untrained eye, recent deeding from a Russian surname to a blind trust is a dead giveaway.

The deed stuff is important, HOWEVER, the linkage was not limited to property records in isolation. Investigators layered temporal correlation. The property purchase followed the 2017 disappearance window by roughly one year, a plausible period for relocation, debriefing, and resettlement logistics. The geographic placement, near Washington, aligns with the practical needs of ongoing handling, access to government liaison, and security support. RFE RL reporting placed the residence in a neighborhood with current and former United States government personnel, which would not be an implausible environment for a protected relocatee, but also increases the risk of attention because residents recognize unusual patterns. (RFE RL 2019a)

Attribution confidence increases through cross-side corroboration. Reuters reported that Russian state media and other Russian outlets visited or referenced the Virginia address associated with Smolenkov, and that Russian official commentary focused on disputing his access level rather than disputing his identity. (Reuters 2019b) The Guardian reported that Russian media quickly identified Smolenkov as the likely figure after the initial extraction story circulated and that earlier Russian reporting had already treated his disappearance as suspicious. (The Guardian 2019b) In counterintelligence analytic terms, this is validation by reaction. When an implicated government acknowledges employment, debates seniority, and frames narratives around access, it implicitly accepts the identity anchor, even if it contests the operational characterization.

Another reinforcing layer is signature observation, i.e., the detection of behaviors consistent with protective posturing. Bellingcat described journalists encountering indications of security presence when approaching the residence and noted that the family likely departed after the story circulated. (Bellingcat 2019) RFE RL reported that neighbors stated that the family of the identified property left abruptly soon after publicity, and that no one answered at the residence when a reporter from RFE visited. (RFE RL 2019a; RFE RL 2019b) From a practitioner’s view, these signatures are a bit ambiguous but directionally meaningful. They do not prove intelligence affiliation however, they do add coherence to the broader narrative when combined with verified administrative linkages.

The identification of Smolenkov can be described as an open-source attribution chain with mutually reinforcing elements. The chain begins with an anonymized description of an extracted asset, which supplies a time-bound and an access profile. It then leverages a pre-existing disappearance narrative in Russian reporting that matches the window. It validates institutional plausibility through official acknowledgement of employment and through open source reconstruction of staff level proximity to senior policy structures. It then bridges the gap from Russia to the United States by locating the same names in property records, supported by temporal correlation and geographic plausibility. Finally, attribution through adversary reaction and observable protective signatures after publicity adds stability to the former. Each element could be dismissed alone, but in totality of the circumstances they provide a high probability attribution that is operationally sufficient for pretty damn reliable public identification. (Bellingcat 2019; Reuters 2019a; RFE RL 2019b)

The counterintelligence implications are clear. A protective extraction does not end an operational dilemma. It begins a new phase in which the threat is not hostile surveillance alone but also open-source exploitation. Transparency regimes create predictable exposure surfaces. Registers of deeds and county recorders, tax collectors, court records, licensing agencies, and corporate filing records are not intelligence sources, but they are an extremely searchable source of structured and more than reasonably accurate data. C.I. measures or countermeasures applied after asset resettlement (such as transferring property into a trust) reduce opportunistic discovery after the fact but will fail against an OSINT collector that already possesses a starting point. Also, cueing can be powerfully exploited. Public narratives about timing and sensitivity can provide sufficient structure for a collector to find pre-existing anomalies and connect them to these domestic records.

The Smolenkov resettlement demonstrates that our source protection doctrine must be extended beyond traditional clandestine concerns. It must incorporate administrative footprint management, name and identity compartmentation, and a realistic appreciation of how quickly digital records can be correlated across jurisdictions, in real-time and remotely. This case CANNOT be viewed as an isolated breach. It really is a warning about the baseline capabilities of OSINT. Oh, and a parting shot from a former C.I. guy, don’t put properties that are deeded to Russian surnames into trusts that are filed publicly.

~ C. Constantin Poindexter, MA in Intelligence, Graduate Certificate in Counterintelligence, JD, CISA/NCISS OSINT certification, DoD/DoS BFFOC Certification

Bibliography

  • Bellingcat. 2019. “Murdered in Montenegro, or Living in Suburban Virginia? Unraveling the 2017 American Spy Story.” September 10, 2019.
  • Radio Free Europe Radio Liberty. 2019a. “Virginia Residents Question Whether Their Neighbor Was a Russian Informant.” September 10, 2019.
  • Radio Free Europe Radio Liberty. 2019b. “Russia Seeking Interpol’s Help on Location of Alleged CIA Informant.” September 12, 2019.
  • Radio Free Europe Radio Liberty. 2019c. “Paper Reports ‘Details’ of Alleged CIA Informer’s Disappearance in Montenegro.” September 12, 2019.
  • Reuters. 2019a. “Kremlin Says Alleged U.S. Spy Did Not Have Access to Putin.” September 10, 2019.
  • Reuters. 2019b. “Russia Blasts Idea a CIA Mole Lifted Lid on Its U.S. Meddling.” September 11, 2019.
  • Russia Matters. 2019. “Russia in Review, Sept. 6 to 13, 2019.” September 2019.
  • The Guardian. 2019a. “Russia Investigated Disappearance of Suspected US Spy as Possible Murder.” September 10, 2019.
  • The Guardian. 2019b. “Oleg Smolenkov: Alleged US Spy Who Gave Russia the Slip.” September 14, 2019.
  • Time. 2019. “The U.S. Reportedly Extracted a High Level Spy From Russia in 2017 Amid Concerns of Mishandled Intelligence.” September 10, 2019.
Share this post:

Strengthening Counterintelligence Training for Diplomats

Strengthening Counterintelligence Training for Diplomats, diplomacy, intelligence, counterintelligence, espionage, counterespionage, national security, C. Constantin Poindexter

The exposure of U.S. diplomats, both stateside and abroad, to recruitment, SIGINT/COMINT targeting, and the loss or compromise of portable computing devices (PCDs) is not accidental. It is a cumulative effect of structural neglect, cultural underinvestment, and the evolving threat environment. Three converging dynamics have produced this vulnerability: institutional bifurcation between diplomatic and intelligence missions; budgetary and educational neglect of counterintelligence (CI) training for non-intelligence personnel; and the rapid digital transformation of diplomatic operations without commensurate adaptation of tradecraft.

Institutional bifurcation is the result of the long-standing separation between the U.S. Foreign Service and the intelligence and security community. Diplomatic officers have historically focused on political, economic, consular, and public diplomacy missions, while security concerns were delegated to Diplomatic Security (DSS) or local host-nation security services. Counterintelligence responsibilities were largely retained within the FBI, CIA, and military intelligence organizations, creating operational silos. This division left diplomats outside the formal CI ecosystem, meaning they rarely received advanced training or actionable threat intelligence. As a result, many Foreign Service Officers (FSOs) still approach their duties as political envoys rather than as personnel operating within an adversarial intelligence battlespace.

Budgetary and educational neglect compound this problem. For decades, the Department of State has allocated limited funding for counterintelligence instruction. Beyond basic “insider threat” briefings or annual cybersecurity refreshers, diplomats often receive little exposure to advanced CI concepts or adversary recruitment methodologies. As reported by ClearanceJobs (McNeil, 2025), many diplomatic personnel deploy to high-threat assignments with minimal training in recognizing or resisting foreign intelligence approaches. The lack of sustained CI education and awareness initiatives at the Foreign Service Institute (FSI) has produced an environment where diplomats are ill-equipped to recognize subtle recruitment tactics or electronic targeting.

The digitalization of diplomacy is a serious vulnerability. Over the past two decades, U.S. embassies and consulates have become highly dependent on portable computing, mobile devices, remote communications, and cloud-based data exchange. While these tools increase efficiency, they have also expanded the attack surface for adversaries. Foreign intelligence services (FIS) now target diplomats as entry points into the U.S. government’s global communications infrastructure. These adversaries exploit unsecured networks, intercept wireless signals, implant malware on devices, and even conduct theft of laptops and external drives. As technology has evolved, diplomatic tradecraft has failed to keep pace. The convenience of connectivity has outstripped the discipline of security.

This weakness is illustrated by several notable cases of espionage and digital compromise involving U.S. diplomatic personnel. The case of Steven John Lalas, a U.S. State Department communications officer stationed in Athens during the early 1990s, is instructive. Lalas provided classified diplomatic and military documents to Greek intelligence over several years before being caught and sentenced to 14 years in prison (Wikipedia, n.d.). He exploited his communications role to access classified cables and Defense Department assessments, which he illicitly removed and passed to a foreign government. Lalas’s case demonstrates that diplomats and communications officers, though not traditional intelligence operators, are prime recruitment targets because of their privileged access to sensitive material. His actions exposed structural vulnerabilities in both vetting and insider threat detection within the State Department’s overseas missions.

The Walter Kendall Myers betrayal is another. They spied for Cuba over nearly three decades. Myers, a senior State Department official and FSI instructor, used his position to obtain and share classified information with the Cuban Intelligence Directorate (Wikipedia, n.d.). The Myers case was not about hacking or physical theft but rather ideological recruitment and sustained insider espionage. Myers was approached gradually, courted ideologically, and ultimately compromised. This illustrates that diplomats whose careers often involve long foreign postings, personal networks abroad, and cultural immersion are highly susceptible to long-term cultivation by FIS recruiters. The absence of continuous CI vetting or behavioral monitoring allowed this penetration to persist for decades.

A third example identifies the theft and exploitation of portable computing devices. The FBI’s “Operation Ghost Stories,” which dismantled a Russian “illegals” network in 2010, revealed how laptops and wireless devices were central to espionage operations (FBI, n.d.). One seized laptop was used to establish covert wireless communications between Russian agents and their handlers. Similarly, numerous reported attempts have been made by foreign actors to steal or implant malware on the personal computers of Western diplomats. These incidents highlight that PCDs are not simply administrative tools but intelligence assets. When lost, stolen, or compromised, they can reveal network structures, contacts, and classified reporting, making them a modern equivalent of the “diplomatic pouch.” The War on the Rocks (2025) analysis of Russian espionage tactics confirms that FIS now combine human recruitment, cyber intrusion, and physical theft in hybrid collection campaigns against Western diplomatic targets.

The convergence of these human and technical vulnerabilities demands a fundamental modernization of CI training for diplomats. Primarily, diplomats MUST be required to receive foundational counterintelligence education. This training should move beyond theoretical awareness and immerse personnel in adversary recruitment tradecraft, SIGINT and COMINT methodologies, and recent case studies. Red-team simulations should require participants to role-play both target and recruiter to internalize how adversaries identify, approach, and manipulate their victims. A diplomat who can think like an adversary is far more likely to resist one.

Equally important, counter-recruitment instruction should emphasize behavioral recognition. Diplomats must learn to identify “soft pitch” recruitment methods, i.e., academic or journalistic overtures, social invitations, social media engagement, or mutual professional interests that can evolve into intelligence targeting. Diplomats must be taught how to perceive, disengage (politely, to preserve the possibility of a double operation), document, and report these encounters through secure channels without fear of reprisal. Continuous CI liaison support at missions abroad would reinforce these practices and ensure rapid response when suspicious approaches occur.

Secure digital and communications hygiene curriculum must be significantly expanded. Every diplomat should be trained in hardware hardening (full-disk encryption, TPM binding, BIOS passwording), media control (banning unvetted USB devices), secure networking (VPNs with endpoint authentication, regular rekeying), and immediate reporting of anomalies (device overheating, unauthorized processes, or loss). Training should include hands-on exercises where diplomats detect and mitigate simulated phishing or device compromise attempts. Embassies should maintain secure drop boxes and Faraday enclosures for potentially compromised devices until forensically examined.

Diplomats must be educated in SIGINT and COMINT awareness. This includes understanding how their electronic emissions can betray movements or discussions, recognizing signs of interception, and maintaining operational discipline in communications. Routine practices such as using shielded rooms for sensitive discussions, approved VPN use, disabling wireless and Bluetooth in secure areas, and maintaining strict clean-desk policies must become ingrained habits. Discipline transforms CI awareness from abstract instruction into practical daily behavior!

Counterintelligence training should incorporate recurring red-team exercises and after-action debriefs. Annual or semi-annual drills simulating recruitment, device loss, or cyber intrusion should be mandatory for all missions. These exercises not only test individual readiness but reveal systemic vulnerabilities such as inconsistent incident reporting or inadequate technical countermeasures. Lessons learned should feed back into State Department CI doctrine.

Structural and organizational reforms are equally important. The Department of State should embed a permanent counterintelligence officer or liaison from the FBI or CIA within every high-risk embassy. This officer would coordinate with the Regional Security Officer (RSO) and oversee local threat assessments, device inspections, and behavioral analysis. Additionally, all diplomats deploying to critical posts should achieve baseline CI certification, validated by written and practical exams similar to those required for intelligence personnel. This “best practices” certification should be renewed periodically and linked to promotion eligibility, reinforcing accountability.

Embassies should also implement periodic red-team audits, with technical and human testing designed to measure CI compliance and readiness. Device procurement and turnover policies must ensure secure supply chains, with forensic validation of new equipment and timely retirement of old hardware. The integration of artificial intelligence-based monitoring could further assist in detecting anomalies or exfiltration attempts across the diplomatic network.

The culture of self-reporting must be reformed. Diplomats often hesitate to report suspicious incidents for fear of professional repercussions. A no-fault reporting model paired with protective anonymity and positive reinforcement will encourage early detection of targeting attempts. CI professionals know that “near-miss” reporting is a critical tool. Diplomats and their staff members must internalize the same principle.

The exposure of U.S. diplomats to recruitment, signals interception, and device compromise is thus not merely a technical vulnerability. It is a clear cultural and institutional weakness. The cases of Lalas and Myers show that ideological or opportunistic recruitment remains a persistent threat, while modern espionage operations like those exposed in Operation Ghost Stories demonstrate that digital compromise is now equally dangerous. A robust counterintelligence program for diplomats must cultivate a mindset of constant adversarial awareness, blending human and technical security disciplines into the fabric of diplomacy itself. By embedding CI at every level of diplomatic training and operations, the United States can begin to close one of its most consequential vulnerabilities in the global intelligence contest AND contribute in a meaningful way to both defensive and offensive counterintelligence operations.

~ C. Constantin Poindexter, MA in Intelligence, Graduate Certificate in Counterintelligence, JD, CISA/NCISS OSINT certification, DoD/DoS BFFOC Certification

References

FBI. (n.d.). Laptop from Operation Ghost Stories. Retrieved from https://www.fbi.gov/history/artifacts/laptop-from-operation-ghost-stories

McNeil, S. (2025, October 9). Modernizing CI training for diplomats: New legislation aims to sharpen the shield abroad. ClearanceJobs. Retrieved from https://news.clearancejobs.com/2025/10/09/modernizing-ci-training-for-diplomats-new-legislation-aims-to-sharpen-the-shield-abroad-2/

War on the Rocks. (2025, April 8). Putin’s spies for hire: What the U.K.’s biggest espionage trial revealed about Kremlin tactics in wartime Europe. Retrieved from https://warontherocks.com/2025/04/putins-spies-for-hire-what-the-u-k-s-biggest-espionage-trial-revealed-about-kremlin-tactics-in-wartime-europe/

Wikipedia contributors. (n.d.). Kendall Myers. In Wikipedia. Retrieved from https://en.wikipedia.org/wiki/Kendall_Myers

Wikipedia contributors. (n.d.). Steven John Lalas. In Wikipedia. Retrieved from https://en.wikipedia.org/wiki/Steven_John_Lalas

Share this post:

The Retracted Intelligence Report on TdA

The Retracted Intelligence Report on Tren de Aragua, espionage, counterespionage, intelligence, counterintelligence, strategic intelligence, national security, C. Constantin Poindexter;

The recent retraction of a National Security Agency (NSA) report on Venezuela and the Tren de Aragua (TdA) criminal gang highlights the tension between intelligence assessments and political narratives. The danger of politicization of intelligence work is front and center here. It’s reasonably clear here that the DNI denied release of the full intelligence product because it did not align neatly with the current Administration’s assertions about TdA and Venezuelan President Maduro’s direction, financing and control over its nefarious activities. Boris Bondarev, former diplomat of the Russian Federation reported on his experience in a Far East assignment, “One day, I was called to meet with the embassy’s number three official, a quiet, middle-aged diplomat who had joined the foreign ministry during the Soviet era. He handed me text from a cable from Moscow, which I was told to incorporate into a document we would deliver to Cambodian authorities. Noticing several typos, I told him that I would correct them. “Don’t do that!” he shot back. “We got the text straight from Moscow. They know better. Even if there are errors, it’s not up to us to correct the center.” It was emblematic of what would become a growing trend in the ministry: unquestioned deference to leaders.” (Foreign Affairs, Nov. 2022) The example is instructive of what we do NOT want to be.

The report, “Venezuela: Examining Regime Ties to Tren de Aragua,” declassified in May 2025, offers an analytic picture that contradicts claims made by U.S. political leaders that Nicolás Maduro is actively engaged in supporting, financing, and directing TdA. The NIC assessment concludes that while the gang has benefitted from a permissive environment in Venezuela, including corruption and weak institutional control, there is no credible evidence that Maduro or senior regime officials exercise command over the group. This retraction is striking because it underscores how intelligence assessments that fail to support policy preferences may be subject to extraordinary pressure, despite their analytic rigor.

The NIC report is clear in its findings. It states that TdA leaders have historically benefitted from permissive conditions in Venezuela, particularly weak prison oversight and corrupt officials. That is NO surprise to those of us who have operated in corrupt Latin American states. Yet it stresses that many TdA cells operate independently across Latin America, with limited coordination even among themselves, let alone with the Venezuelan government (NIC 2025). The report underscores that much of TDA’s growth has been facilitated by Venezuelan migration and that individuals and networks frequently use the gang’s name without direct affiliation, underscoring the decentralized and diffuse nature of the group. Crucially, the report states that there is “no indication that Venezuelan President Nicolás Maduro or senior government officials are directing the actions of Tren de Aragua,” contradicting claims that Maduro orchestrates the group’s activities (AP News 2025).

The report does allow that some mid- and low-level Venezuelan officials may have financial ties to TdA. Such connections are typically opportunistic, involving corruption or passive tolerance, rather than the product of a coherent state policy (NIC 2025). In this sense, regime responsibility lies less in the deliberate deployment of the gang as a proxy and more in the systemic weakness of governance that allows TdA to operate with impunity. This distinction is critical: corruption and negligence do not equate to strategic coordination or sponsorship. Yet political leaders have blurred this line by portraying TdA as a regime-directed instrument of repression and transnational crime.

Redactions in the NIC report shed further light on analytic processes. Although redactions obscure details, we can reasonably infer that they conceal the names of regime-linked individuals, sources and methods of intelligence collection, or details about TdA’s operations abroad. In intelligence practice, such redactions protect human sources, sensitive communications intercepts, and law enforcement leads. Notably, the report’s unredacted portions are explicit in their rejection of senior-level regime direction. Given classification practices, it is unlikely that redacted sections would conceal evidence directly contradicting the assessment’s core conclusion, since that would undermine the transparency and credibility of the report’s stated findings (NIC 2025).

Other credible sources reinforce the NIC’s position. Associated Press reporting on the document emphasizes that there is no evidence of Maduro’s direct involvement, while acknowledging that some regime actors might benefit from TdA’s activities (AP News 2025). Investigations by InSight Crime and The Guardian further show that certain monitors and advocacy groups have exaggerated TdA’s presence in the United States, even fabricating reports of its activity (InSight Crime 2025; The Guardian 2025). By contrast, organizations such as the Human Rights Foundation (HRF) argue that regime-linked actors used TdA in the abduction of Venezuelan dissident Ronald Ojeda in Chile in 2024. A more definitive answer to the question of Maduro’s involvement with TdA may have come from Ojeda. Unfortunately, he was liquidated by the regime. Perhaps the Chilean criminal information to the ICC will reveal more. The allegations remain under judicial investigation and do not yet amount to definitive evidence of direct command by Maduro himself (HRF 2025). The U.S. Government Accountability Office (GAO) and Congressional Research Service (CRS) both highlight Venezuela’s permissive environment for illicit financial flows and organized crime, but stress that corruption at lower levels is more prevalent than systematic state direction (GAO 2023; CRS 2024).

When these sources are synthesized, a consistent analytic picture emerges. Venezuela under Maduro provides an enabling environment for organized crime, but this is the result of systemic corruption, institutional incapacity, and deliberate tolerance by some officials, not top-level strategic direction. TDA operates as a decentralized criminal network whose spread is tied to transnational migration and weak law enforcement, not to state financing or command. The strongest claims, that Maduro is personally orchestrating TdA’s financing and direction, misrepresent available evidence and are not supported by credible intelligence or rigorous analysis. This distinction is not trivial: overstating threats distorts policymaking and risks politicizing intelligence.

The retraction of the NIC report under the leadership of DNI Tulsi Gabbard underscores the sensitivity of such findings. According to reporting, Gabbard ordered the recall of a classified report on Venezuela even after NSA officials confirmed that it met analytic and procedural standards (WRAL 2025). This action illustrates the pressures intelligence agencies face when their findings contradict prevailing political narratives. While intelligence must consider the risks of exposing sources and methods, recalling a report that undermines a presidential claim risks signaling politicization and undermining the credibility of the intelligence community.

It is important to concede some counterarguments. Intelligence reports are limited by available sources, and the absence of evidence is not evidence of absence. Covert relationships between regime actors and TdA may exist beyond the reach of collection or declassification. Allegations such as those emerging in Chile may eventually provide more conclusive evidence. However, at present, the preponderance of credible sources supports the NIC’s conclusion that Maduro is not directly directing or financing TdA. Until more conclusive evidence emerges, policymaking should be grounded in this nuanced understanding.

Ultimately, the retraction of the NIC report raises broader questions about the role of intelligence in our governance. The U.S. intelligence community’s credibility depends on its ability to provide unbiased, apolitical assessments to policymakers, even when those assessments contradict political preferences. Intelligence that is shaped by politics rather than evidence undermines both domestic and international credibility. For policymakers, basing decisions on politicized claims risks misallocation of resources, legal overreach, and diplomatic missteps. For the public, it threatens the erosion of trust in government institutions and more specifically the I.C. It is imperative that the DNI ensures that analytic judgments reflect the best available evidence, acknowledges uncertainties, and resists the politicization of intelligence regardless if she falls out of favor with the Administration. Only through integrity in production and delivery to the consumer can intelligence provide a sound foundation for policy in matters as consequential as Venezuela’s transnational criminal networks.

~ C. Constantin Poindexter, MA in Intelligence, Graduate Certificate in Counterintelligence, JD, CISA/NCISS OSINT certification, DoD/DoS BFFOC Certification

References

AP News. 2025. “Declassified Intelligence Memo Contradicts Trump’s Claims Linking Gang to Venezuelan Government.” May 6, 2025. https://apnews.com/article/d818cc58962ba90cd2c94ca1b494d4fd
.

Congressional Research Service (CRS). 2024. Venezuela: Political Crisis and U.S. Policy. CRS Report IF10230. https://www.congress.gov/crs-product/IF10230
.

GAO (Government Accountability Office). 2023. Venezuela: Illicit Financial Flows and U.S. Efforts to Disrupt Them. GAO-23-105668. https://www.gao.gov/products/gao-23-105668
.

Human Rights Foundation (HRF). 2025. “Venezuela’s Maduro Continues to Use Tren de Aragua for Transnational Repression, Kidnapping, Assassination.” April 25, 2025. https://hrf.org/latest/venezuelas-maduro-continues-to-use-tren-de-aragua-for-transnational-repression-kidnapping-assassination/
.

National Intelligence Council (NIC). 2025. Venezuela: Examining Regime Ties to Tren de Aragua. Case No. DF-2025-00379, declassified May 5, 2025.

The Guardian. 2025. “Trump Defense Official Led Think Tank that Spread Lies about Tren de Aragua.” August 13, 2025. https://www.theguardian.com/us-news/2025/aug/13/joseph-humire-thinktank-tren-de-aragua
.

WRAL. 2025. “DNI Gabbard Recalls Classified Report on Venezuela in Highly Unusual Move.” May 2025. https://www.wral.com/story/dni-gabbard-recalls-classified-report-on-venezuela-in-highly-unusual-move/22152236/
.

Foreign Affairs. “Sources: Russia Misconduct – Boris Bondarev.” [n.d.]. “Sources: Russia Misconduct – Boris Bondarev,” Foreign Affairs. Accessed [insert access date]. https://www.foreignaffairs.com/russian-federation/sources-russia-misconduct-boris-bondarev

Share this post:

Disinformation as “Insurgency”, an American Constitutional View

disinformation, misinformation, espionage, counterespionage, counterintelligence, spy, subversion, psyops

I read with a great deal of interest Jacob Ware’s article “To fight disinformation, treat it as an insurgency” that appeared recently in The Strategist, an Australian Strategic Policy Institute publication. I have always held my own ideas about disinformation, more specifically “inoculation” as a countermeasure and recommending instruction from a very young age much as grade schools do in the baltic states. Ware’s article tackles the subject matter as a ‘control social media’ issue. I do not disagree with the importance of media responsibility for moderation of certain types of content, Ware appropriately identifies “overlook[ing] the important role of digital consumers”, but doubles down on content control. The article suggests that social media companies, as central nodes in the information ecosystem, must be pressured into moderating content more aggressively as much as the importance of digital consumers themselves being hardened against manipulation (“inoculation” as I have written in previous scholarship”. Control, compelling in its framing, raises some not insignificant constitutional issues in the context of the United States, particularly with regard to the First Amendment’s protections of speech, association, and press.

Framing Disinformation as Insurgency: Strategic and Legal Ramifications
Ware’s analogy between insurgencies and disinformation campaigns conveys the existential threat that hostile narratives, particularly those that foreign actors pose to democratic stability. Comparing disinformation actors to terrorist insurgents invites the application of military-style containment and suppression tactics, perhaps even the “cyber-kinetic” removal of bad actors (i.e., content moderation and bans), the targeting of ideological hubs (e.g., online communities, networks, influencers, etc.), and critically, the enforcement of norms through government-backed initiatives.

In the U.S. legal context, much of this may be a non-starter. Insurgents and terrorists operate outside the protection of constitutional law, whereas digital speakers, however misinformed or malicious, are presumptively entitled to the protections of the First Amendment. The Constitution does not permit the government to silence unpopular, false or even offensive ideas unless they meet strict criteria for incitement, true threats, or defamation. This legal boundary sharply limits the government’s ability to treat digital speech as a national security threat without triggering robust judicial scrutiny, even if that information is objectively dangerous disinformation.

Section 230 and Platform Immunity: The Epicenter of the Debate
The article criticizes Section 230 of the Communications Decency Act (1996), which shields internet platforms from liability for user-generated content. This statute is often viewed as the legal linchpin that enabled the growth of the modern internet, on the whole a pretty positive thing. Ware argues that these protections prevent platforms from being held accountable and serve as a digital safe haven for malign actors. From a policy standpoint, this critique doesn’t hold much merit. Critics across the political spectrum argue that Section 230 incentivizes platforms to prioritize engagement and profit over truth and social stability, however, repealing or modifying Section 230 would not directly authorize government censorship. It WOULD expose platforms to civil liability for failing to moderate. Any new federal statute that imposes content-based restrictions or penalties would need to meet all prongs of the constitutional free speech tests and modern U.S. jurisprudence. The courts have routinely ruled that platforms are private entities with their own First Amendment rights therefore even in the absence of Section 230, the government would not be able to compel social media companies to carry or remove specific content unless it satisfies narrow constitutional exceptions.

Free Speech: A Distinctly American Commitment
A central theme in the article is the frustration that American-style free speech doctrines allow dangerous ideas to circulate freely online. Ware writes from an Australian perspective. The article praises the European Union’s Digital Services Act and Australia’s eSafety initiatives as superlative regulatory models. Under those statutory regimes platforms face stiff penalties for failing to suppress harmful content. These approaches may appear pragmatic but they clearly represent a sharp divergence from U.S. legal culture.

The U.S. Constitution’s First Amendment prohibits government abridgement of speech, including offensive, deceptive, or politically inconvenient speech. In United States v. Alvarez (2012), the Supreme Court struck down a federal law criminalizing false claims about military honors, holding that even deliberate lies are constitutionally protected unless they cause specific, fixable harm. Further, in Brandenburg v. Ohio (1969), the Court established that even advocacy of illegal action is protected unless it is directed to inciting imminent lawless action AND is likely to produce such action. So, even under the noble pretext of national defense, any proposal that seeks to directly regulate speech must reconcile with this robust jurisprudence. Foreign governments might be able to implement speech controls without constitutional constraints. We cannot. The U.S. must address disinformation through less intrusive, constitutionally sound means.

Counterinsurgency in a Civilian Space: Policing Thought and Risking Overreach
Ware’s counterinsurgency metaphor extends beyond moderation into behavioral engineering, winning the “hearts and minds” of digital citizens. This vision includes public education, civilian fact-checking brigades, and a sort of civic hygiene campaign against harmful content. Although such measures may be effective as psychological operations (PSYOPs), the distinction between persuasion and indoctrination must be carefully managed in a free society.

There is legitimate concern that state-sponsored resilience campaigns could slip into propaganda or viewpoint discrimination, especially when political actors define what constitutes “disinformation.” The inconvenient truth is that the label of “misinformation” has been applied inconsistently, sometimes suppressing legitimate dissent or valid minority viewpoints. The First Amendment’s commitment to a “marketplace of ideas theory” assumes that truth ultimately prevails in open debate, not through coercive narrative management.

There is another danger. Using the tools of counterinsurgency, even rhetorically, raises alarms about militarizing civil discourse and legitimizing authoritarian measures under the guise of “national security.” In Boumediene v. Bush (2008), the Court warned against extending military logic to civilian legal systems. Applying wartime strategy to cultural or political disputes in the civilian cyber domain risks undermining the very liberal values the state claims to protect.

An Appropriate Role for Government
Despite consitutional guardrails, the federal government is not powerless. Several constitutionally sound measures remain available. These approaches avoid entangling the government in the perilous business of adjudicating truth while still defending the information ecosystem.:

Transparency Requirements – Congress can require social media companies to disclose their moderation policies, algorithmic preferences, and foreign funding sources without dictating content outcomes.

Education Initiatives – Civics education and media literacy programs are constitutionally permissible and could help inoculate the public against disinformation without coercion.

Voluntary Partnerships – The government can engage with platforms voluntarily, offering intelligence or warnings about malign foreign influence without mandating suppression.

Targeting Foreign Actors – The government can lawfully sanction, indict, or expel foreign individuals and entities engaged in coordinated disinformation campaigns under laws governing espionage, foreign lobbying, or election interference.

Ware’s comparison of disinformation to insurgency is strategically evocative, but its prescriptive implications clash with foundational American principles. The First Amendment might seem inconvenient, but it was designed to prevent precisely the kind of overreach that counterinsurgency measures invite. Democracies do not defeat authoritarianism by adopting its tools of censorship and narrative control. If the United States is to confront the threats of disinformation effectively, it must do so in a way that affirms rather than undermines what makes us distinctively American. Educating, not censoring; persuading, not suppressing; and building durable civic institutions capable of withstanding the torrent of falsehoods without succumbing to the lure of government-controlled truth are imperative. Freedom remains the best antidote to tyranny ONLY if we remain vigilant in its defense.

~ C. Constantin Poindexter,

  • Master of Arts in Intelligence
  • Graduate Certificate in Counterintelligence
  • Undergraduate Certificate in Counterintelligence
  • Former I.C. Cleared Contractor
Share this post:

The DNI Report: What is Missing?

seguridad national, espionage, contraespionage, contrainteligencia, c. constantin poindexter

It should come as no surprise in the current polarized political climate that certain threats to U.S. national security are omitted, some overly emphasized and others included but not give a more thorough review. Ironically (or perhaps not so ironically) the omissions and lack of more comprehensive address of certain threat are those very ones that are exacerbated by current Administration policies. The current DNI [unclassified version] contains no surprises, however there are some perils that decidedly lack the attention that they deserve. I’ll be brief.

The weaponization of artificial intelligence against the U.S. population poses and existential threat to the nation that we are not appropriately prepared for. The assessment identifies China’s AI capabilities in surveillance and disinformation, but underestimates the dangers posed by AI-generated disinformation and psychological operations targeting U.S. elections, civil cohesion, and trust in institutions. Synthetic media (deepfakes) at scale are unaddressed and present a very real menace. FIEs that excel in producing these fakes could fabricate major geopolitical incidents and/or falsely incriminate U.S. leaders. This is a “real-world crisis” scenario. Further, in our rush to load up our own AI capability, models trained on U.S. data pose an exposure to having them turned back against us in warfare, negotiation, or economic manipulation contexts. The DNI offers no significant discussion of how adversaries might use advanced LLMs and multi-modal AI to undermine decision-making at every level of our communities, from individual voters and first responders to senior policymakers.

There is a significant danger of the collapse of U.S. domestic infrastructure due to political paralysis and sabotage. The DNI identifies cyber threats to infrastructure (e.g., water, healthcare) however the report understates the systemic vulnerability of U.S. infrastructure to non-digital threats such as aged and neglected critical systems (e.g., bridges, power grids, water systems), and insider sabotage by ideologically motivated actors. White supremacist factionists and extremists like Timothy McVeigh come immediately to mind. Political paralysis and corruption that prevent modernization or resiliency efforts are the final ugly nail in the proverbial coffin. The loss of national security expertise as a result of wholesale firings/layoffs and the sidelining of individuals with decades of tradecraft and professional expertise based on party adherence are a very real threat. The assessment fails to meaningfully consider how polarization and our legislature’s unwillingness to work together are making the U.S. increasingly incapable of protecting or restoring its critical infrastructure after an attack or natural disaster. Don’t think for a moment that Chinese, Russian, Iranian and North Korean FIEs are failing to perceive these vulnerabilities that they can exploit.

Espionage, subversion and other nefarious covert operations against the U.S. and its interests via foreign investment and big-corporate influence are absent. There is really no excuse to omit identification and discussion of how “big money” has affected national security at every level, as even for a layperson is occurring in plain view. China’s cyber espionage and technology theft are addressed in depth, but why are foreign ownership of and influence in U.S. strategic sectors, including agriculture, pharmaceuticals, real estate near sensitive military sites and AI startups left alone? The use of shell corporations and fronting arrangements to embed operatives and proxies within sensitive sectors and policy circles is a serious threat as well. Strategic acquisition of distressed U.S. companies post-COVID by entities linked to FIEs are a mechanism and vehicles for subversion, espionage and sabotage. A brief look at our own history since the end of WWII reveals how these methods are effective and insidious, perhaps presenting a greater danger than cyber-attacks because they provide our adversaries to deep access, deniability and strategic gain that will serve them well for decades. Fragmenting and ‘bull in a china shop’ cancellation of funding paired with broken inter-agency oversight are extremely problematic.

Do better.

Share this post: