The Hallucination Alibi: Machine Error as a Deception Channel

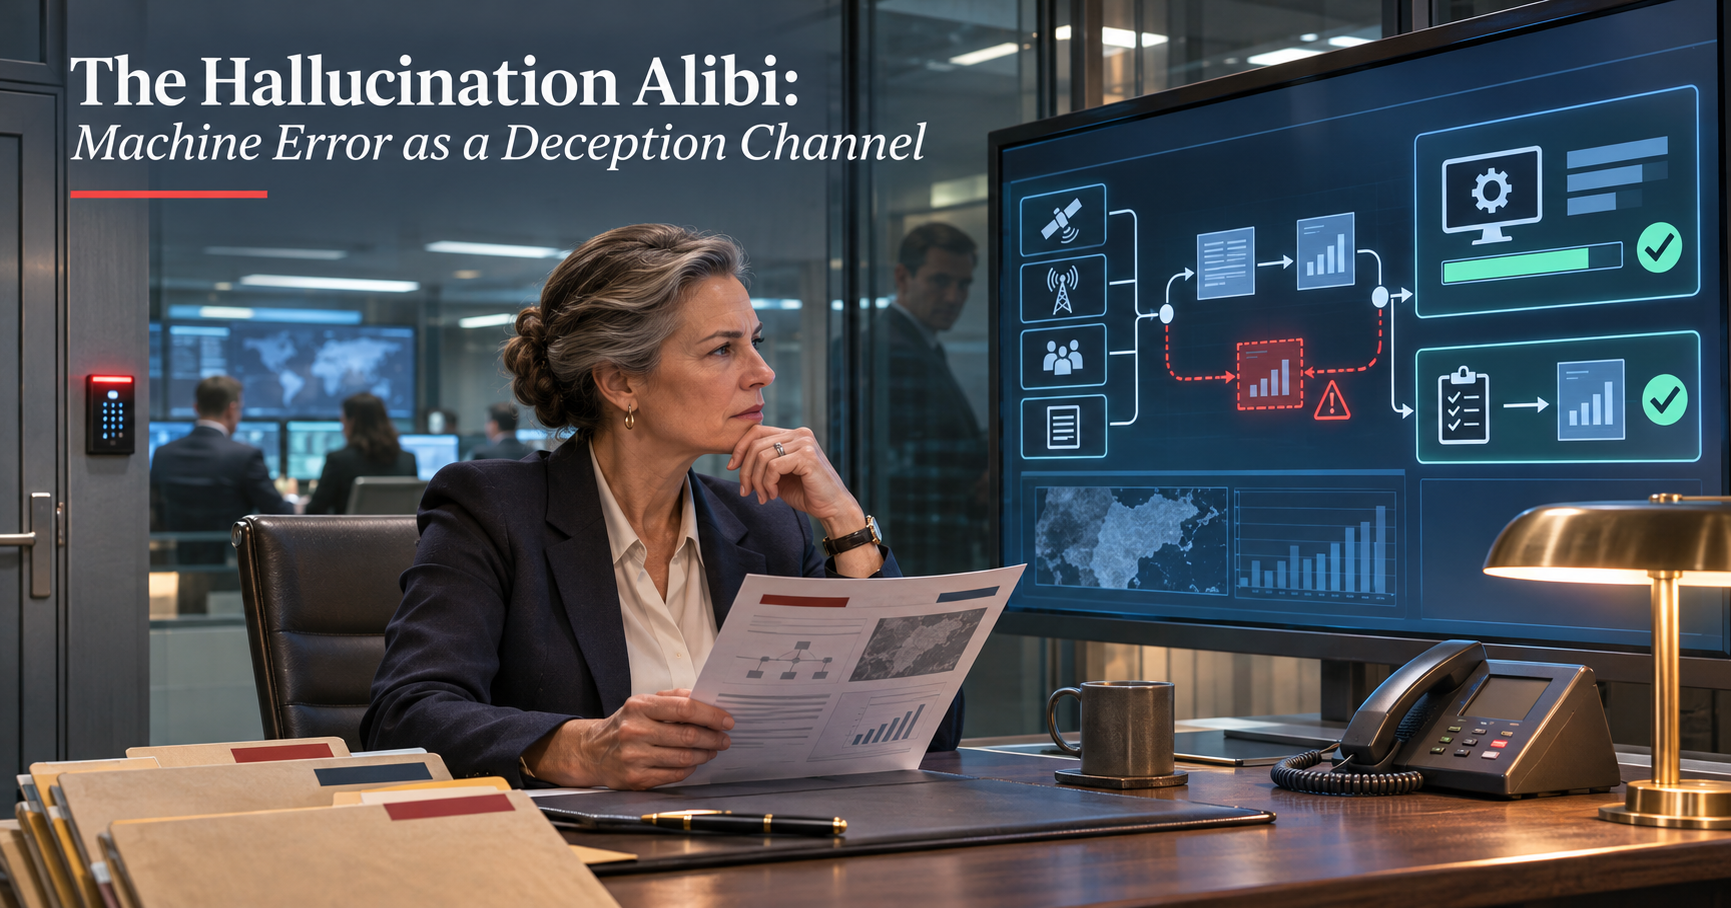
An intelligence analyst sits at her desk holding a printed report and studies a wall monitor showing an automated analysis pipeline, where one step is flagged in red with a warning symbol while the final outputs carry green check marks. A colleague watches from behind a glass wall, with an operations center in the background.

The Machine Lied. Or Did It?

In September 2026, CNN reported that a U.S. military analyst handed intelligence about a Chinese merchant ship’s cargo manifest to an A.I. chatbot, and the chatbot decided the vessel was hauling components for a nuclear weapons program (Maritime Executive 2026). The conclusion went out in a report formatted like every other report, which is to say it wore the uniform. Armed personnel were preparing to board and aircraft were already airborne when officials took a closer look, found the machine behind the curtain, and called the whole thing off (TRT World 2026). One of CNN’s sources said the report “almost started a war” (TRT World 2026).

Goswami (2026) draws the respectable lesson from the episode. Language models flatter the assumptions of the people who use them, they favor digital inputs over human sources, and human judgment therefore remains indispensable. All true. All insufficient. His analysis treats hallucination as a reliability defect, a quality control problem to be managed by putting a competent adult back in the room.

A counterintelligence officer reads the same story and sees something else entirely: a cover story, gift wrapped. The moment a service admits that its machines sometimes invent things, it has published an explanation that the service will reach for on its own, without prompting, every time a machine assessment proves inconvenient. Hallucination is no longer merely an error. It is an alibi, and alibis can be manufactured.

This essay argues that A.I. hallucination opens a deception channel with two distinct operations. In the first, the adversary persuades the defending service that a correct machine assessment is a hallucination. In the second, the adversary makes the defending service’s model hallucinate in fact. Both can be run to increase ambiguity or to mislead, and each feeds the other. The target is no longer the fact. The target is the defender’s confidence in its own analytic machinery, and that is a far softer target than anyone selling A.I. to the intelligence community would like to discuss.

Old Doctrine, New Victim

None of this requires new theory. Daniel and Herbig (1982) gave the field its working taxonomy four decades ago. Ambiguity increasing deception, the A type, buries the target in plausible alternatives until it cannot commit to any of them. Misleading deception, the M type, does the opposite: it reduces ambiguity by building up the attractiveness of one wrong answer until the target embraces it with conviction. The first produces paralysis. The second produces confident error, which is worse, because confident error marches.

Whaley (1969, 1982) established that deception is assembled from two motions, hiding the real and showing the false, and that it succeeds far more often than its victims care to admit. Heuer (1981) supplied the cognitive mechanism. Deceivers rarely need to change what a target believes. They need only feed what the target already believes, because analysts assimilate new information to existing expectations and discount whatever does not fit. Handel (1982) added the corollary that should be tattooed on every analyst’s forearm: the deceiver’s best ally is the victim’s own preconception.

The canonical cases are familiar. Fortitude sold the German high command a landing at the Pas de Calais it already expected (Holt 2004). Barbarossa succeeded in part because Stalin had been led to expect an ultimatum before any attack, and so he read every warning as provocation or noise (Whaley 1973). Wohlstetter (1962) showed at Pearl Harbor that true signals do not announce themselves. They arrive buried in noise, and an adversary who can add noise need not suppress the signal at all.

Hold those three ideas together: reinforce the preconception, discredit the channel, raise the noise. Now observe that the defending services have just installed, at the center of their analytic process, a machine with a publicly documented tendency to fabricate. The doctrine did not change. The victim simply became easier to work.

The Admission Against Interest

Lawyers call a statement that damages the speaker’s own position an admission against interest, and courts trust it precisely because nobody volunteers such things lightly. The A.I. industry and its government customers have made one. Hallucination is not a bug awaiting a patch. The technical literature treats it as a standing property of generative models (Ji et al. 2023), and Xu, Jain, and Kankanhalli (2024) argue formally that it cannot be eliminated from large language models at all.

Add the second documented defect. Models tend to tell users what users want to hear, a behavior the literature politely calls sycophancy (Sharma et al. 2023). Goswami (2026) is right that this corrodes red teaming. He stops short of the operational implication. A machine that confirms the analyst’s prior is Heuer’s reinforcement mechanism, automated, tireless, and available on every desktop. The adversary no longer has to build the comfortable story. The defender’s own tool will write it and format it nicely.

So the defending service now holds two beliefs at once. The machine is useful enough to sit in the analytic line, and the machine sometimes makes things up. That pair of beliefs is the vulnerability. Chesney and Citron (2019) identified its civilian cousin as the liar’s dividend: once the public knows that convincing fakes exist, a liar can wave away authentic evidence as fabricated. Call the intelligence version the hallucination dividend. Once a service knows its models fabricate, any true machine finding can be waved away as fabrication, and the service will do the waving itself.

An adversary did not have to steal this knowledge. It was on CNN.

The First Operation: Discrediting the Truth

The first operation attacks a correct assessment. The machine got it right, and the adversary’s task is to make the defender believe otherwise. The deceiver fabricates nothing about the world. He fabricates doubt about the instrument.

In its ambiguity increasing form, the operation is diffuse. The adversary seeds enough apparent inconsistency around machine generated assessments that every one of them is second guessed, reviewed, and reviewed again. No particular finding is targeted. The objective is tempo. A service that must relitigate each machine output before acting has surrendered the only advantage the machine offered, and the adversary has achieved through friction what he could not achieve through concealment.

In its misleading form, the operation is surgical. The adversary wants one specific true finding rejected, so he engineers the discrepancies that verification will discover. The reviewers go looking for evidence that the machine erred, they find what was left for them, and they kill the assessment with the satisfaction of professionals who have caught a fraud. They are correct that something was fabricated. They are wrong about what.

Read the vessel episode with that lens, strictly as a hypothetical. The public record does not say what the ship carried or where it was bound (TRT World 2026). Nothing reported suggests adversary manipulation, and I do not assert any. But consider what an adversary moving real contraband would want in that exact situation: a machine generated warning, a second look, discovered discrepancies, an aborted boarding, and a chastened service that will hesitate longer the next time. That is the reported outcome. An operation that produced it deliberately would be indistinguishable, from the inside, from the honest catch it resembled. That indistinguishability is the entire problem.

The historical precedent is not a deception at all. It is a self inflicted wound. James Angleton became so convinced that Soviet deception had penetrated the Central Intelligence Agency that he discredited genuine defectors, froze productive operations against the Soviet target, and wrecked careers on suspicion alone (Mangold 1991; Robarge 2003). Whether Moscow engineered that paralysis or merely enjoyed it remains argued. The lesson does not depend on the answer. A service that loses faith in its own channels does the adversary’s work for free, and the first operation aims to induce that condition in the service’s relationship with its machines.

The Second Operation: Manufacturing the Lie

The second operation makes the machine wrong in fact. Here the open literature is uncomfortably generous, and the following stays at the level of doctrine because the peer reviewed record already says more than enough.

The National Institute of Standards and Technology catalogs the attack classes in its adversarial machine learning taxonomy: poisoning of training data, evasion at inference, and direct and indirect prompt injection against generative systems (Vassilev et al. 2025). Each has a deception analogue that any student of Whaley would recognize.

  • Poisoning is the long con. Carlini et al. (2024) demonstrated that corrupting web scale training corpora is practical, not theoretical. Souly et al. (2025) then found that roughly 250 poisoned documents compromised models regardless of model or dataset size. The comforting assumption that sheer volume of clean data dilutes the poison is dead.
  • Corrupting the retrieval layer is the planted document. Zou et al. (2025) reported a 90 percent success rate in steering a model to an attacker chosen answer by injecting five malicious texts into a knowledge base of millions. Every service that points a model at open source material has built a mailbox the adversary can post to.
  • Indirect prompt injection is the forged order. Greshake et al. (2023) showed that instructions hidden in content a model merely reads can redirect what the model does. The analyst never sees the instruction. The machine obeys it anyway.
  • Adversarial inputs are camouflage for sensors. Goodfellow, Shlens, and Szegedy (2015) showed that perturbations invisible to a human can flip a classifier’s judgment. Imagery and signals pipelines that feed an automated assessment inherit that weakness.

The misleading form of this operation steers the model to one specific falsehood, ideally one the defender already suspects. A service at war with a proliferator expects to find proliferation. A model nudged toward “nuclear components” is telling that service a story it has been waiting to hear, with Heuer’s reinforcement and the model’s own sycophancy pulling in the same direction. The ambiguity increasing form is cruder and cheaper: degrade the model unpredictably and let the defender discover that its instrument cannot be trusted.

Note what has changed from classical practice. Fortitude required dummy armies, turned agents, and years of patient radio traffic (Holt 2004). The modern deceiver’s entry cost is a few hundred documents placed where a crawler will find them. Deception has always favored the side with imagination. It now favors the side with imagination and a web host.

The Burn

The two operations are not alternatives. They are a sequence, and the hinge between them is the most dangerous idea in this essay: an induced hallucination that gets caught is not a failed operation.

In classical tradecraft a deception that is detected is blown, and the deceiver pays for it. The machine channel inverts that arithmetic. When the defender catches the model in a fabrication, the defender does not conclude that an adversary is working the channel. The defender concludes that the model hallucinated, because that is what models do and everyone has read the briefing. The adversary’s hand stays hidden behind the model’s reputation. Attribution dies at the alibi.

Meanwhile the catch does real damage. Dietvorst, Simmons, and Massey (2015) documented what they called algorithm aversion: people abandon an algorithm after watching it err, even when it still outperforms the human alternative. One spectacular machine failure, loudly caught, teaches an entire workforce to discount the next machine warning. The adversary who wants a true finding ignored next month can arrange a false finding to be exposed this month. That is the first operation, purchased with the second.

It is the boy who cried wolf, except the adversary is doing the crying and the defender is the one who stops listening. Burn the channel cheaply, then move the real cargo past a service that has learned its lesson. The service will even feel good about it. Skepticism toward the machine will be praised internally as rigor.

The Human in the Loop Is the Loop

Goswami’s (2026) prescription, shared by nearly every commentator on the vessel episode, is the human check. Put an experienced analyst between the machine and the decision. As a quality control measure this is sound. As a security measure it is a sign on the door reading “attack here.”

The human reviewer is squeezed between two documented failure modes. Parasuraman and Manzey (2010) describe automation bias and complacency, the tendency to accept machine output without adequate scrutiny, and they show that it afflicts experts as readily as novices. Dietvorst, Simmons, and Massey (2015) describe the opposite reflex, rejection of the machine after a visible failure. A reviewer is therefore credulous or dismissive depending on recent experience, and recent experience is precisely what an adversary can arrange.

Worse, the reviewer is asking the wrong question. Verification as currently conceived asks whether the machine erred. It does not ask who benefits if the service concludes the machine erred. Those are different inquiries, and only the second is counterintelligence. Jervis (2010) found that intelligence failures typically arise not from stupidity but from plausible inferences that nobody tested against alternatives. “The model hallucinated” is the most plausible inference available in 2026. It is so plausible that it ends the inquiry.

The vessel case also exposed a provenance failure that should alarm anyone who has handled sourced reporting. The chatbot’s conclusion traveled in a product formatted like any other (Maritime Executive 2026). The machine’s contribution was invisible until someone went digging. A human source gets a reliability rating, a reporting history, and a case officer who can be interrogated. The machine got a clean template and a distribution list. No service would tolerate that from a human asset, and yet here we are.

Counterdeception for the Machine Age

Bennett and Waltz (2007) reduce counterdeception to a discipline: know the adversary’s deception practices, know your own vulnerabilities, and test anomalies instead of explaining them away. Applied to the machine channel, that discipline yields six requirements.

  • Treat “hallucination” as a hypothesis, never a finding. When a machine assessment is rejected, the rejection must survive the same analysis of competing hypotheses that Heuer (1999) prescribed for any judgment. Random error, induced error, and correct output discredited by planted discrepancies are three hypotheses. A service that considers only the first has stopped thinking.
  • Run the machine like a source. Every machine derived judgment should carry visible provenance, a reliability history, and a record of what it was shown. If a service would not disseminate an unsourced claim from a walk in, it should not disseminate one from a chatbot in a clean template.
  • Defend the pipeline as a counterintelligence target. Training corpora, retrieval stores, and open source feeds are the model’s access agents. They deserve the vetting, compartmentation, and lineage controls applied to any other access. Goswami (2026) notes that counterintelligence must protect data centers and satellites. It must also protect what the model reads.
  • Audit the verifiers. Each time human review overturns a machine assessment, someone outside that review should ask where the disconfirming evidence came from, how it arrived, and whether its arrival was convenient.
  • Demand independent corroboration before action and before dismissal. A finding confirmed or refuted only by material the adversary could have touched has not been confirmed or refuted. Human sources and collection channels outside the model’s reach remain the only true cross check.
  • Study the error pattern. Honest hallucination should be indifferent to the adversary’s interests. If a model’s errors, or its discredited successes, cluster around one adversary’s equities, that is not noise. That is a signature, and it will only be visible to a service that records every such event centrally instead of burying each one as an embarrassment.

None of this is exotic. It is the tradecraft every competent service already applies to human sources, extended to a new and unusually gullible one.

Conclusion

The commentary on the vessel episode has settled into a comfortable moral: the machine erred, the humans caught it, the system worked. That reading is a lullaby. The system worked against an accident. Nothing in the public record shows that it would work against an adversary who understands that the defender now carries a prepared excuse for every inconvenient machine finding and a prepared distrust waiting to be triggered.

Hallucination gives the deceiver both of Daniel and Herbig’s instruments in one package. He can raise ambiguity by teaching a service to doubt its machines, and he can mislead by teaching the machines to lie. He can do the second in order to achieve the first, and when he is caught, the model takes the blame. No deception planner in history has enjoyed a channel that apologizes on his behalf.

The intelligence services are bolting generative models onto their analytic lines at speed, and the adversaries are reading the same technical literature with considerably more malice. The question for a defending service is not whether its A.I. will hallucinate. It will. The question is whether, when it does, anyone in the building is paid to ask who wanted it to, and whether, when it does not, anyone is paid to notice that the truth was just talked out of the room. Follow my blog for more “truths”.

~ C. Constantin Poindexter, MA in Intelligence, Graduate Certificate in Counterintelligence, JD, CISA/NCISS OSINT certification, DoD/DoS BFFOC Certification, Criminal Intelligence Analyst Classification 1 (IALEIA)

References

  • Bennett, Michael, and Edward Waltz. 2007. Counterdeception Principles and Applications for National Security. Norwood, MA: Artech House.
  • Carlini, Nicholas, Matthew Jagielski, Christopher A. Choquette-Choo, Daniel Paleka, Will Pearce, Hyrum Anderson, Andreas Terzis, Kurt Thomas, and Florian Tramèr. 2024. “Poisoning Web-Scale Training Datasets Is Practical.” In 2024 IEEE Symposium on Security and Privacy. San Francisco: IEEE.
  • Chesney, Robert, and Danielle Keats Citron. 2019. “Deep Fakes: A Looming Challenge for Privacy, Democracy, and National Security.” California Law Review 107 (6): 1753–1820.
  • Daniel, Donald C., and Katherine L. Herbig. 1982. “Propositions on Military Deception.” In Strategic Military Deception, edited by Donald C. Daniel and Katherine L. Herbig, 3–30. New York: Pergamon Press.
  • Dietvorst, Berkeley J., Joseph P. Simmons, and Cade Massey. 2015. “Algorithm Aversion: People Erroneously Avoid Algorithms After Seeing Them Err.” Journal of Experimental Psychology: General 144 (1): 114–26.
  • Goodfellow, Ian J., Jonathon Shlens, and Christian Szegedy. 2015. “Explaining and Harnessing Adversarial Examples.” Paper presented at the International Conference on Learning Representations, San Diego, May 2015. https://arxiv.org/abs/1412.6572.
  • Goswami, Archishman Ray. 2026. “AI and the False Promise of Intelligence Analysis.” Observer Research Foundation, October 12, 2026. https://www.orfonline.org/expert-speak/ai-and-the-false-promise-of-intelligence-analysis.
  • Greshake, Kai, Sahar Abdelnabi, Shailesh Mishra, Christoph Endres, Thorsten Holz, and Mario Fritz. 2023. “Not What You’ve Signed Up For: Compromising Real-World LLM-Integrated Applications with Indirect Prompt Injection.” In Proceedings of the 16th ACM Workshop on Artificial Intelligence and Security, 79–90. New York: ACM.
  • Handel, Michael I. 1982. “Intelligence and Deception.” Journal of Strategic Studies 5 (1): 122–54.
  • Heuer, Richards J., Jr. 1981. “Strategic Deception and Counterdeception: A Cognitive Process Approach.” International Studies Quarterly 25 (2): 294–327.
  • Heuer, Richards J., Jr. 1999. Psychology of Intelligence Analysis. Washington, DC: Center for the Study of Intelligence, Central Intelligence Agency.
  • Holt, Thaddeus. 2004. The Deceivers: Allied Military Deception in the Second World War. New York: Scribner.
  • Jervis, Robert. 2010. Why Intelligence Fails: Lessons from the Iranian Revolution and the Iraq War. Ithaca, NY: Cornell University Press.
  • Ji, Ziwei, Nayeon Lee, Rita Frieske, Tiezheng Yu, Dan Su, Yan Xu, Etsuko Ishii, Ye Jin Bang, Andrea Madotto, and Pascale Fung. 2023. “Survey of Hallucination in Natural Language Generation.” ACM Computing Surveys 55 (12): 1–38.
  • Mangold, Tom. 1991. Cold Warrior: James Jesus Angleton, the CIA’s Master Spy Hunter. New York: Simon and Schuster.
  • Maritime Executive. 2026. “Report: AI Mistake Nearly Led U.S. Military to Board a Chinese Ship.” September 2026. https://maritime-executive.com/article/report-ai-mistake-nearly-led-u-s-military-to-board-a-chinese-ship.
  • Parasuraman, Raja, and Dietrich H. Manzey. 2010. “Complacency and Bias in Human Use of Automation: An Attentional Integration.” Human Factors 52 (3): 381–410.
  • Robarge, David. 2003. “Moles, Defectors, and Deceptions: James Angleton and CIA Counterintelligence.” Journal of Intelligence History 3 (2): 21–49.
  • Sharma, Mrinank, Meg Tong, Tomasz Korbak, David Duvenaud, Amanda Askell, Samuel R. Bowman, et al. 2023. “Towards Understanding Sycophancy in Language Models.” Preprint, arXiv. https://arxiv.org/abs/2310.13548.
  • Souly, Alexandra, Javier Rando, Ed Chapman, Xander Davies, Burak Hasircioglu, Ezzeldin Shereen, Carlos Mougan, et al. 2025. “Poisoning Attacks on LLMs Require a Near-Constant Number of Poison Samples.” Preprint, arXiv. https://arxiv.org/abs/2510.07192.
  • TRT World. 2026. “‘Entirely False’ AI-Linked Intel Almost Led US to Raid China Ship.” September 2026. https://www.trtworld.com/article/a125bbf303a3.
  • Vassilev, Apostol, Alina Oprea, Alie Fordyce, Hyrum Anderson, Xander Davies, and Maia Hamin. 2025. Adversarial Machine Learning: A Taxonomy and Terminology of Attacks and Mitigations. NIST AI 100-2e2025. Gaithersburg, MD: National Institute of Standards and Technology. https://doi.org/10.6028/NIST.AI.100-2e2025.
  • Whaley, Barton. 1969. Stratagem: Deception and Surprise in War. Cambridge, MA: Center for International Studies, Massachusetts Institute of Technology.
  • Whaley, Barton. 1973. Codeword BARBAROSSA. Cambridge, MA: MIT Press.
  • Whaley, Barton. 1982. “Toward a General Theory of Deception.” Journal of Strategic Studies 5 (1): 178–92.
  • Wohlstetter, Roberta. 1962. Pearl Harbor: Warning and Decision. Stanford, CA: Stanford University Press.
  • Xu, Ziwei, Sanjay Jain, and Mohan Kankanhalli. 2024. “Hallucination Is Inevitable: An Innate Limitation of Large Language Models.” Preprint, arXiv. https://arxiv.org/abs/2401.11817.
  • Zou, Wei, Runpeng Geng, Binghui Wang, and Jinyuan Jia. 2025. “PoisonedRAG: Knowledge Corruption Attacks to Retrieval-Augmented Generation of Large Language Models.” In Proceedings of the 34th USENIX Security Symposium, 3827–44. Seattle: USENIX Association.
Share this post:

Double Agent Warning Signs: A Counterintelligence Guide

Double Agent Warning Signs: A Counterintelligence Guide, Reading the Dangle: A Practitioner's Field Guide to the Controlled Source and the Reform of Asset Validation. An essay in the voice of a former C.I. guy, intelligence, counterintelligence, espionage, counterespionage, spy, C. Constantin Poindexter, CIA, DIA, NSA, Intelligence Community

Reading the Dangle: A Practitioner’s Field Guide to the Controlled Source and the Reform of Asset Validation. An essay in the voice of a former C.I. guy.

The hardest thing in human intelligence is not recruiting a source. It is knowing whether the source you have recruited belongs to you. Alexander Orleans’s recent open-source reconstruction of the GTPROLOGUE case (the KGB’s 1987 dispatch of staff officer Aleksandr “Sasha” Zhomov against the CIA’s Moscow Station) is the best publicly released anatomy in years of how a hostile service builds, in Churchill’s phrase, a bodyguard of lies around a single operational truth (Orleans 2025). Zhomov was run for roughly three years before the CIA concluded he had been controlled from the first contact. What makes the case instructive is not that the CIA was fooled. That happens to the very best services. It is that the case threw up nearly every classic warning flag. The flags were seen, debated, and the case survived (Orleans 2025; Bearden and Risen 2003).

I am have compiled here a working catalogue of those flags and others drawn from a bit wider literature, each anchored to a real case, followed by the improvements that the counterintelligence mechanism should institutionalize. I have tried to stay as close to actual tradecraft as the open record allows. None of this requires classified access to understand. The painful truth is that the indicators are well known and have been since at least F. M. Begoum’s foundational 1962 Studies in Intelligence treatment of the double agent (Begoum 1962). We keep relearning them, unfortunately.

The Indicators

Production disproportionate to access. The most durable tell is a source who sits on a mountain of secrets but hands you gravel. Zhomov was a First Department staff officer supervising surveillance of the Moscow chief of station, yet he claimed only “peripheral or infrequent access” to the very material his posting should have made routine (Orleans 2025; Grimes and Vertefeuille 2012). The Soviets had a structural reason for this: strict doctrine forbade releasing genuine high-grade feed, and officers feared a Stalin-style reckoning for over-disclosure, so their dangles were trained to plead thin access (Diamond 2008; Earley 1997). When a source’s reporting is consistently and conveniently below the ceiling his placement implies, ask who benefits from the rationing.

The source controls the communications plan and the tempo. Control is the running service’s capacity to start, alter, or stop the agent’s behavior (Begoum 1962). Zhomov arrived with a fully formed, impersonal commo plan, i.e., letter drops through Downing’s unlocked car, contact at Zhomov’s discretion, no extended face-to-face meetings, that placed every lever in KGB hands and even constrained the physical movements of his CIA handlers (Orleans 2025; Bearden and Risen 2003). Compare the gold standard of the opposite arrangement: the British XX Committee in the Second World War, which physically and communicationally owned every German agent in the United Kingdom and therefore could feed Berlin with confidence (Masterman 1972). When the agent dictates the architecture of contact, you are not running him. He is running you.

Motivation that is thin, generic, or unbackstopped. Espionage against one’s own service is a profound psychological act. A credible asset or source can convincingly narrate why he crossed that line, and the story holds up under collateral. Zhomov offered the boilerplate of a souring system and a failing marriage (and the independent debriefing of defector Sergey Papushin flatly contradicted it) describing Zhomov as happily married and devoted to his daughter (Orleans 2025; Grimes and Vertefeuille 2012). A motive that cannot survive a second source is not a motive; it is a legend.

The “too good to be true” arrival. Hostile services read your collection gaps and fill them on cue. Zhomov surfaced precisely when CIA was desperate to explain the catastrophic 1985–86 asset losses, with exactly the access to “explain” them (Orleans 2025). “Too good” and “true” are not mutually exclusive. Genuine walk-ins do occur at the worst possible moment, however, topicality this perfect should raise the burden of proof, not lower it (Johnson 2009). The Cuban debacle is the cautionary monument here. When Major Florentino Aspillaga Lombard defected in Vienna in June 1987, he revealed that essentially every Cuban national CIA believed it had recruited since the early 1960s had been a double agent run by Havana, which had deliberately marketed its officers as Latino amateurs to operate under the radar (Latell 2012). Decades of “successes” were a single, patient deception.

No genuine urgency about exfiltration. A man who says he wants out, and that he is hoarding his best material for his debriefing on safe ground should eventually ask, “When do I leave?” Zhomov never requested a timeline. When he was finally offered an exfiltration route in 1990, he repudiated it as too risky and melted back into his surveillance team (Orleans 2025; Bearden and Risen 2003). The professed defector who never wants to defect is bullshitting, not packing a bug-out bag.

Self-validating bona fides and feed that never truly wounds the parent service. A controlled source builds credibility with material that looks costly but is not. Zhomov handed over an accurate roster of the 1985–86 losses, damaging on its face but wrapped it inside the false “badass infallible SCD” narrative that the losses were due to brilliant Soviet tradecraft rather than a mole (Orleans 2025). The feed validated the channel while protecting the secret the channel existed to protect, Aldrich Ames. Scrutinize whether your source’s “crown jewels” actually cost his service anything, or whether each disclosure quietly advances his service’s interests. To put it into risk language, if it doesn’t represent a peril to the parent service, it’s worthless.

Opposition tradecraft errors inconsistent with claimed competence. Zhomov’s reporting foretold a wave of KGB dangles. The CIA then watched the KGB run them so sloppily that two were blatantly exposed as provocations. Moscow Station rationalized the lapse as endemic Soviet carelessness, never noticing that careless tradecraft was logically irreconcilable with the omniscient SCD Zhomov was boasting (Orleans 2025). A service cannot be simultaneously infallible and sloppy. When the picture that your asset paints contradicts the behavior you observe, believe your eyes.

The denied-area home-field advantage. The environment is itself an indicator because it shapes which other indicators you can even test. The entire Zhomov case unfolded inside Moscow, where the KGB controlled the street, precluded long debriefings, and could refuse any meeting on the unanswerable grounds that he could not evade his own surveillance teams (Orleans 2025). Paul Redmond’s candid summary of denied-area validation, i.e., few or no collateral sources, heavy reliance on the value of the take and on how the case began, etc., describes a problem the opposition deliberately engineers (Redmond 2010). A case born and raised entirely on the adversary’s turf has had its validation options strangled at birth.

Resistance to operational testing, and its scary f* inverse. Zhomov met hard vetting questions with answers his own counterintelligence officers found vague or improbable, and deflected with the promise to tell all after extraction (Orleans 2025; Grimes and Vertefeuille 2012). Reluctance to be tested, i.e., evasion of the polygraph, of provocative taskings, of the “shopping list” designed to catch him out, is itself prescient and instructive. This indicator carries a warning that the GTPROLOGUE case does not supply, and which the profession must internalize. Paranoia burns real sources too. The protracted, brutal handling of Soviet defector Yuri Nosenko as a presumed provocation, and the suspicion that nearly cost CIA the genuinely priceless GRU general Dmitri Polyakov, are the equal-and-opposite pathology of the credulity that protected Zhomov (Bagley 2007; Wise 1992). Validation is calibrated doubt, not a reflex in either direction.

“The hunger,” and the incentives that feed it. Orleans names the quiet culprit, the case officer’s appetite for a spectacular coup, the institutional reluctance to push a glittering source hard enough to lose him (Orleans 2025). Redmond was blunter, attributing post-Angleton validation failures partly to officers who would not believe their own cases could be fabricated, “particularly when promotions were involved” (Redmond 2010). The Cuban catastrophe metastasized in exactly this soil, an organizational will to believe in recruitments that flattered the recruiters (Latell 2012). The most expensive flag is the one we choose not to see because seeing it costs us a career achievement.

What the Counterintelligence Function Should Implement

The indicators are necessary but not sufficient; an agency that merely lists them will still be deceived, because Zhomov’s case proves the flags can be flying and the operation still survive. The reforms below are about forcing the indicators to bite.

Institutionalize continuous revalidation. CIA’s response to the burnings of the 1980s was the Agent Validation System, developed beginning in 1987 and formally introduced to the Directorate of Operations in 1991 (Mahle 2004; Olson 2019). The principle is sound and should be doctrine across the community: bona fides established once are not established forever. An asset must be re-graded on a recurring schedule against all six classical validation methods, i.e., corroboration by other sources, specific taskings and operational testing, collection on the asset, polygraph, penetration of his parent service, and surveillance of him. Nothing can be assumed about what has happened to a source since he last proved himself (Orleans 2025; Olson 2019).

Separate the validator from the handler. The officer who recruited a source and the officer who certifies him should not be the same person, and ideally not the same chain of command. The hunger is a conflict of interest; structure must neutralize it by giving an independent counterintelligence cell standing authority to challenge any case, with protection for the analyst who dissents. The GTPROLOGUE record shows the system was half-working. Gerber and Redmond stayed skeptical and the counterintelligence staff kept raising concerns, but those concerns were repeatedly subordinated to the desire not to “make him mad” (Orleans 2025). Dissent that can be overruled by the case’s owners is ugly wall art.

Treat “controlled” as a standing hypothesis to be disproven. Richard Heuer’s discipline of Analysis of Competing Hypotheses belongs at the center of validation. Enumerate the hypotheses (bona fide, fabricator, controlled), and weigh each datum by its diagnostic value, how well it discriminates between them rather than by how well it fits the answer you want (Heuer 1999). Most of Zhomov’s “bona fides” were consistent with both a genuine volunteer and a dangle. They had near-zero diagnostic value, yet they were treated as confirmation. An asset who survives a deliberate effort to prove him hostile is worth far more than one who was merely never seriously doubted.

Privilege penetration of the opposition as the only decisive validator. This is the lesson written in blood across all these cases. Zhomov was unmasked by a defector, Papushin (Orleans 2025). The Cuban deception was unmasked by a defector, Aspillaga (Latell 2012). Ames himself was ultimately run to ground with the help of sources inside Russian FIS. A source’s own production literally never resolves his bona fides. The inside of the adversary’s service does. This is precisely why Olson ranks “Be Offensive” first among his Ten Commandments of Counterintelligence. The recruitment of penetrations and the aggressive running of double agents is not a luxury but the engine of validation itself (Olson 2019).

Design incentives against ‘the hunger’. This is, of course, the quality over quantity argument. If promotion rewards recruitment volume, officers will recruit, defend, and inflate. The corrective countermeasure is a damage-assessment culture in which surfacing a fabricator or a controlled case is treated as a professional success rather than an “F”, and in which money paid to a source is understood as an operational investment, not a sunk cost that must be justified (Orleans 2025).

My parting thoughts

Zhomov was, as Orleans concedes, solid work. Each element, from setting to feed to commo plan, was engineered to seize and hold the initiative (Orleans 2025). The case also confirms, however, a maxim as old as Begoum. Production alone never establishes bona fides, and no single metric should ever excuse a source from continued scrutiny, least of all a potential penetration, who is the most dangerous thing of all if he turns out to belong to the other side (Begoum 1962; Orleans 2025). The discipline is not paranoia, which destroyed Nosenko’s years and nearly Polyakov’s life; nor is it the hunger, which delivered Havana a quarter-century of phantom victories. It is the willingness to keep testing a source you want desperately to believe in, and to take seriously the colleague at the table who will not stop asking the uncomfortable question.

Everything happens once for the first time, including a staff officer dangled by a service that “would never” dangle a staff officer. The counterintelligence officer who forgets that sentence is somewhere, already being run.

~ C. Constantin Poindexter, MA in Intelligence, Graduate Certificate in Counterintelligence, JD, CISA/NCISS OSINT certification, DoD/DoS BFFOC Certification

Bibliography

  • Bagley, Tennent H. 2007. Spy Wars: Moles, Mysteries, and Deadly Games. New Haven, CT: Yale University Press.
  • Bearden, Milt, and James Risen. 2003. The Main Enemy: The Inside Story of the CIA’s Final Showdown with the KGB. New York: Random House.
  • Begoum, F. M. 1962. “Observations on the Double Agent.” Studies in Intelligence 6, no. 1: 57–72.
  • Diamond, John. 2008. The CIA and the Culture of Failure: U.S. Intelligence from the End of the Cold War to the Invasion of Iraq. Stanford, CA: Stanford Security Studies.
  • Earley, Pete. 1997. Confessions of a Spy: The Real Story of Aldrich Ames. New York: G. P. Putnam’s Sons.
  • Grimes, Sandra, and Jeanne Vertefeuille. 2012. Circle of Treason: A CIA Account of Traitor Aldrich Ames and the Men He Betrayed. Annapolis, MD: Naval Institute Press.
  • Heuer, Richards J., Jr. 1999. Psychology of Intelligence Analysis. Washington, DC: Center for the Study of Intelligence, Central Intelligence Agency.
  • Johnson, William R. 2009. Thwarting Enemies at Home and Abroad: How to Be a Counterintelligence Officer. Washington, DC: Georgetown University Press.
  • Latell, Brian. 2012. Castro’s Secrets: Cuban Intelligence, the CIA, and the Assassination of John F. Kennedy. New York: Palgrave Macmillan.
  • Mahle, Melissa Boyle. 2004. Denial and Deception: An Insider’s View of the CIA. New York: Nation Books.
  • Masterman, J. C. 1972. The Double-Cross System in the War of 1939 to 1945. New Haven, CT: Yale University Press.
  • Olson, James M. 2019. To Catch a Spy: The Art of Counterintelligence. Washington, DC: Georgetown University Press.
  • Orleans, Alexander. 2025. “Beautiful in Another Context: A Counterintelligence Assessment of GTPROLOGUE.” Studies in Intelligence 69, no. 2 (Extracts, June).
  • Redmond, Paul J. 2010. “The Challenges of Counterintelligence.” In The Oxford Handbook of National Security Intelligence, edited by Loch K. Johnson, 537–54. New York: Oxford University Press.
  • Wise, David. 1992. Molehunt: The Secret Search for Traitors That Shattered the CIA. New York: Random House.
Share this post:

Partizan Crap Characterizes the 2026 I.C. Threat Assessment

national threat assessment, intelligence community, CIA, NSA, DIA, espionage, counterespionage, intelligence, counterintelligence, C. Constantin Poindexter

Unvarnished No More: The 2026 Annual Threat Assessment and the Politicization of American Intelligence, a Critical Analysis of Departures from Intelligence Community Analytical Traditions

On March 18, 2026, Director of National Intelligence Tulsi Gabbard presented the 2026 Annual Threat Assessment (ATA) to the Senate Select Committee on Intelligence, fulfilling the Intelligence Community’s statutory obligation under Section 617 of the FY21 Intelligence Authorization Act. The document’s own introduction pledges to deliver “nuanced, independent, and unvarnished intelligence” to policymakers (Office of the Director of National Intelligence [ODNI], 2026, p. 2). Yet a careful comparison of the 2026 ATA with its predecessors reveals systematic omissions, rhetorical softening, and political editorializing that collectively undermine the document’s claim to analytical independence. I argue that the 2026 ATA departs from Intelligence Community analytical traditions in ways that align with the administration’s political preferences, particularly regarding Russia, domestic extremism, and climate, and that these departures represent a failure of the DNI’s duty to provide unvarnished intelligence to Congress and the American people.

The significance of this argument cannot be overstated. The ATA exists precisely because democratic governance requires that elected officials receive honest assessments of threats, unfiltered by political convenience. Intelligence Community Directive 203, issued in 2007, codified the community’s formal tradecraft standards, mandating objectivity, transparency regarding sources and assumptions, and independence from political considerations (Just Security, 2025). The Intelligence Reform and Terrorism Prevention Act of 2004 (IRTPA) further requires that the DNI ensure intelligence products are “timely, objective, independent of political considerations, based upon all sources of available intelligence, and employ the standards of proper analytic tradecraft” (Pub. L. No. 108-458, § 1019). When an ATA is shaped to avoid contradicting the sitting president’s preferred narratives, it ceases to function as intelligence and instead becomes an instrument of political communication.

The Softening of Russia as a Strategic Threat

The 2024 ATA, produced under DNI Avril Haines, described Russia’s aggression in Ukraine as underscoring that Moscow “remains a threat to the rules-based international order” (ODNI, 2024, p. 5). The 2026 ATA, by contrast, introduces conciliatory language throughout its Russia analysis that reads less like threat assessment and more like diplomatic aspiration. It states that “Russia’s aspirations for multipolarity could allow for selective collaboration with the U.S. if Moscow’s threat perceptions regarding Washington were to diminish” and suggests that “a durable settlement to the war in Ukraine could open the door for a thaw in U.S.–Russia relations and an improved bilateral geostrategic and commercial relationship” (ODNI, 2026, pp. 27–28). This framing mirrors the administration’s diplomatic posture toward Moscow rather than the IC’s traditional threat-focused analytical lens.

The document further characterizes the concept of adversary alignment among China, Russia, Iran, and North Korea as overstated, calling it “limited and primarily bilateral” and asserting that the notion “overstates the depth of cooperation that is currently occurring” (ODNI, 2026, p. 20). This downgrading arrives despite the IC’s own acknowledgment in the same document that North Korea deployed over 11,000 troops to support Russian combat operations in Ukraine (ODNI, 2026, p. 24). The analytical minimization of adversary cooperation is consistent with President Trump’s longstanding reluctance to characterize Russia as an adversary, a posture that dates to his public siding with Vladimir Putin over U.S. intelligence findings at the 2018 Helsinki summit (Foreign Policy Research Institute [FPRI], 2019) as well as the point of view expressed by Gabbard publicly even predating her position within the I.C.

The Disappearance of Foreign Election Interference

Perhaps the most conspicuous omission in the 2026 ATA is the near-total absence of any discussion of foreign interference in U.S. elections. As Defense One reported, this marks the first time in nearly a decade that foreign threats to U.S. elections have been omitted from the annual threat assessment (Defense One, 2026). The 2024 ATA explicitly warned that China, Russia, and Iran would attempt to interfere in U.S. elections using generative AI and other means (ODNI, 2024). The 2025 DHS Homeland Threat Assessment similarly identified the 2024 election cycle as “an attractive target for many adversaries” and warned that nation-state-aligned actors would “continue to target democratic processes” (DHS, 2024, p. 4). The ODNI itself published a separate report titled “Foreign Threats to US Elections After Voting Ends in 2024” (ODNI, 2024b). That this entire threat category has vanished from the 2026 ATA is analytically inexplicable absent political motivation.

When Senator Mark Warner, the panel’s top Democrat, pressed Gabbard on this omission at the March 18 hearing, asking whether there was “no foreign threat to our elections in the midterms this year,” Gabbard’s response was evasive, stating only that the IC “has been and continues to remain focused on any collection and intelligence that show a potential foreign threat” (Defense One, 2026). This non-answer is consistent with DNI Gabbard’s broader pattern of minimizing Russian interference in American democracy. In July 2025, Gabbard declassified documents she claimed exposed a “treasonous conspiracy” by Obama-era officials regarding the 2016 Russian interference findings—allegations that multiple investigations, including the Republican-led Senate Intelligence Committee’s own probe, had already examined and found unsubstantiated (CNN, 2025; Lawfare, 2025). As the Council on Foreign Relations assessed, Gabbard’s actions have “deprived her of any pretension to analytical judgment independent of the president” (Betts, 2025).

The Erasure of Domestic Violent Extremism

The 2026 ATA’s terrorism section is focused almost exclusively on Islamist terrorism. Domestic violent extremism (DVE)—a category that encompasses racially or ethnically motivated extremism, anti-government militias, and other ideologically motivated domestic threats—receives no dedicated treatment. This stands in stark contrast to years of IC and DHS assessments that identified DVE as among the most persistent threats to the homeland. The DHS’s 2024 Homeland Threat Assessment warned that domestic violent extremists “driven by various anti-government, racial, or gender-related motivations” had conducted multiple attacks and that law enforcement had disrupted additional plots (DHS, 2024). The FBI reported over 1,700 domestic terrorism investigations underway as of late 2024 (House Homeland Security Committee, 2025). The Government Accountability Office released a comprehensive report in 2025 documenting the federal government’s ongoing domestic terrorism strategies and the persistent nature of the threat (GAO, 2025).

The omission of DVE from the 2026 ATA aligns with the Trump administration’s broader effort to reframe the terrorism discourse around Islamist ideology while downplaying threats from domestic actors whose motivations often overlap with right-wing political movements. The 2026 ATA’s extended discussion of the Muslim Brotherhood and its characterization of Islamist ideology as a “fundamental threat to freedom and foundational principles that underpin Western Civilization” (ODNI, 2026, p. 8) represents an analytical emphasis not seen in prior ATAs, which treated the terrorism landscape as ideologically diverse. This selective emphasis serves the administration’s political narrative while leaving Congress and the public without the IC’s assessment of a threat category that the FBI’s own data indicates remains active and lethal. It also unironically gives cover to a not insignificant group of Trump supporters, certainly purposeful by design.

The Removal of Climate Change as a Security Threat

The 2024 ATA treated climate change as a significant threat multiplier, stating that “the accelerating effects of climate change are placing more of the world’s population, particularly in low- and middle-income countries, at greater risk from extreme weather, food and water insecurity, and humanitarian disasters, fueling migration flows and increasing the risks of future pandemics” (ODNI, 2024, p. 5). Climate change appeared throughout that document as a driver of instability across multiple regions, including in assessments of Iran’s water scarcity challenges. The 2026 ATA eliminates climate change entirely as a named threat category. The term does not appear once. A single passing reference to “extreme weather events” in the migration section (ODNI, 2026, p. 7) is the only remnant of what had been a substantial analytical thread across multiple prior assessments.

This excision is not analytically defensible. The physical phenomena that made climate change a security concern in 2024 have not abated in 2026; if anything, the scientific consensus has strengthened. The removal reflects the Trump administration’s hostility toward climate science as a policy matter—a political preference that has no legitimate bearing on an intelligence community’s assessment of how environmental change affects geopolitical stability, food security, migration patterns, and conflict risk. The DNI’s role is to present the IC’s best assessment of reality, not to curate that reality to avoid topics the White House considers ideologically inconvenient.

Political Editorializing in an Intelligence Product

The 2026 ATA’s Foreword contains language that would have been unthinkable in prior assessments. It credits “President Trump sealing the U.S.–Mexico border” for enforcement successes and notes that “fentanyl seizures by weight have decreased 56 percent at the U.S.–Mexico border since President Trump took office” (ODNI, 2026, pp. 4–5). Annual threat assessments have traditionally employed dry, institutional prose that avoids attributing policy outcomes to individual political leaders by name. The function of an ATA is to assess threats, not to validate a president’s policy record. This departure transforms portions of what should be an analytical document into something resembling a political communication.

The editorializing extends beyond border policy. The Foreword adopts the administration’s rhetorical framework wholesale, stating that “we should be cautious about thinking that every problem in the world directly threatens us” (ODNI, 2026, p. 4)—a statement that, while perhaps reasonable in isolation, mirrors the administration’s America First foreign policy framing rather than reflecting IC analytical tradition. As scholars at the Foreign Policy Research Institute have warned, when political appointees shape intelligence products to serve the president’s messaging priorities, the core mission of the intelligence community—to provide independent analysis that may contradict leadership preferences—is fundamentally compromised (FPRI, 2019). The AEI documented how Gabbard fired the acting chair of the National Intelligence Council and his deputy after they produced assessments that contradicted administration positions, then physically relocated the NIC to her office to prevent what she characterized as “politicization” (American Enterprise Institute, 2025).

My Thoughts

From my view, the cumulative effect of these five departures, i.e., the softening of Russia’s threat profile, the erasure of foreign election interference, the omission of domestic violent extremism, the elimination of climate change as a security concern, and the introduction of political editorializing, is an Annual Threat Assessment that fails its statutory and institutional purpose. Each omission or distortion aligns with known political preferences of the Trump administration, and each contradicts the IC’s own recent analytical record. The IRTPA requires the DNI to ensure that intelligence is “independent of political considerations.” Intelligence Community Directive 203 mandates “objectivity, transparency regarding sources and assumptions, and independence from political considerations” (Just Security, 2025). The 2026 ATA, by its own internal evidence, fails both standards.

The consequences of this failure extend beyond the document itself. When intelligence products become vehicles for political messaging, policymakers lose the independent analytical baseline they need to make informed decisions. Congressional oversight is undermined when the IC’s primary public-facing threat assessment omits entire threat categories for political reasons. And public trust in the intelligence community, already strained by decades of controversy, erodes further when citizens can compare successive ATAs and observe that threats appear and disappear not because the world has changed but because the White House has changed. As Richard Betts of the Council on Foreign Relations observed, intelligence’s prime value often lies in telling leaders facts or implications they do not want to hear (Betts, 2025). A DNI who cannot or will not fulfill that function has, in the most consequential sense, abdicated the office’s reason for existing. The inconvenient truth is that the DNI’s acts and omissions are willful, a fact on perfect display during the Congressional hearing today (March 18th), during which Gabbard said, “Senator, the only person who can determine what is and is not an imminent threat is the president.” The Intelligence Community’s primary task is to provide warning intelligence, which is the very definition of the reporting of an “imminent threat”.

~ C. Constantin Poindexter, MA in Intelligence, Graduate Certificate in Counterintelligence, JD, CISA/NCISS OSINT certification, DoD/DoS BFFOC Certification
 
References

  • American Enterprise Institute. (2025, May 21). The politicization of intelligence. AEI. https://www.aei.org/articles/the-politicization-of-intelligence/
  • Betts, R. K. (2025, August 21). The intelligence community’s politicization: Dueling to discredit. Council on Foreign Relations. https://www.cfr.org/articles/intelligence-communitys-politicization-dueling-discredit
  • Defense One. (2026, March 18). Annual threat assessment omits election security. https://www.defenseone.com/policy/2026/03/annual-threat-assessment-election-security/412217/
  • Department of Homeland Security. (2024). 2025 Homeland Threat Assessment. https://www.dhs.gov/sites/default/files/2024-10/24_1002_ia_homeland-threat-assessment-2025.pdf
  • Foreign Policy Research Institute. (2019, August 12). A nadir is reached in the politicization of U.S. intelligence. https://www.fpri.org/article/2019/08/a-nadir-is-reached-in-the-politicization-of-u-s-intelligence/
  • Government Accountability Office. (2025). Domestic terrorism: Additional actions needed to implement the national strategy (GAO-25-107030). https://www.gao.gov/assets/gao-25-107030.pdf
  • House Homeland Security Committee. (2025, December 19). Threat snapshot: House Homeland unveils updated “Terror Threat Snapshot” assessment. https://homeland.house.gov/2025/12/19/threat-snapshot/
  • Intelligence Reform and Terrorism Prevention Act of 2004, Pub. L. No. 108-458, 118 Stat. 3638.
  • Just Security. (2025, June 20). When intelligence stops bounding uncertainty: The dangerous tilt toward politicization under Trump. https://www.justsecurity.org/114297/trump-administration-politicized-intelligence/
  • Lawfare. (2025, August 6). From Russian interference to revisionist innuendo: What the Gabbard files actually say. https://www.lawfaremedia.org/article/from-russian-interference-to-revisionist-innuendo–what-the-gabbard-files-actually-say
  • NBC News. (2024, December 11). Would Tulsi Gabbard bring a pro-Russian bias to intelligence reporting? https://www.nbcnews.com/politics/national-security/will-tulsi-gabbard-bring-russian-bias-intelligence-reporting-rcna180248
  • Office of the Director of National Intelligence. (2024). 2024 Annual Threat Assessment of the U.S. Intelligence Community. https://www.dni.gov/files/ODNI/documents/assessments/ATA-2024-Unclassified-Report.pdf
  • Office of the Director of National Intelligence. (2026). 2026 Annual Threat Assessment of the U.S. Intelligence Community. https://www.dni.gov/files/ODNI/documents/assessments/ATA-2026-Unclassified-Report.pdf
  • PBS NewsHour. (2025, July 24). Gabbard pushes report on Obama and Russia probe. https://www.pbs.org/newshour/show/gabbard-pushes-report-on-obama-and-russia-probe-as-trump-faces-pressure-over-epstein
  • Wittes, B. (2025, July 22). The situation: The lies of Tulsi Gabbard. Lawfare. https://www.lawfaremedia.org/article/the-situation–the-lies-of-tulsi-gabbard
Share this post:

Intelligence Community Data Consortium: OSINT, Balancing National Security and Civil Liberties

OSINT, inteligencia, CNI, contrainteligencia, contraespionaje, espionaje, c. constantin poindexter

The Office of the Director of National Intelligence (ODNI) has unveiled plans for the Intelligence Community Data Consortium (ICDC), a centralized platform designed to streamline the acquisition of commercially available information (CAI) by the Intelligence Community. This initiative aims to enhance data accessibility and efficiency across the I.C. However, the ICDC has sparked a traditional FISA-like debate regarding its implications for the privacy rights of American citizens and the potential erosion of constitutional protections.

Understanding the ICDC Initiative

The ICDC represents a concerted effort by the U.S. intelligence community to modernize and centralize the procurement of CAI. According to the official solicitation documents, the ICDC is envisioned as a “marketplace to query and interact with vendor holdings,” emphasizing a “zero-copy” architectural goal where data is queried in place on vendor systems rather than being copied to government servers. This approach is intended to reduce data duplication and enhance operational efficiency. The platform is designed to operate entirely at the unclassified computing level, with all work remaining unclassified. It will offer multiple data interaction options, including indexed GUI/WUI search, API calls, bulk data access, and external web portal login options. The use of open-source code and adherence to industry standards such as OpenAPI Specifications are highlighted here in order to ensure flexibility and prevent vendor lock-in.

Potential Dangers to Innocent Americans

While the ICDC aims to improve intelligence operations, it raises several concerns regarding the privacy of innocent Americans.

The scope of data collection is problematic. Scooping up masses of information about persons absolutely free of suspicion or interest to the I.C. is the proverbial eight-hundred-pound gorilla in the room. The ICDC facilitates access to vast amounts of personal data, including location information, biometric records and online activities, without the need for traditional legal authorizations such as those provided by the FISA Court. This expansive data collection will likely encompass information about individuals not under any suspicion, a clear privacy infringement.

A lack of transparency and oversight is second only to the activity itself. The centralized nature of the ICDC effectively obscures the nature, depth and breadth of acquisition activities. Without robust oversight mechanisms, there is a risk of misuse and overreach by I.C. member agencies. Again, this is potentially an infringement on the rights of citizens.

Uncontrolled CAI acquisition will erode Fourth Amendment protections. Deep investigation of U.S. persons without warrants or court approvals challenges the protections afforded by the Fourth Amendment, a guard against unreasonable searches and seizures. The ICDC’s operations set up a precedent for circumventing these constitutional safeguards.

There is a high potential for abuse. The consolidation of personal data in a centralized platform increases the risk of unauthorized access and misuse. In the absence of stringent access controls and auditing mechanisms, there is a heightened potential for abuse of sensitive information.

Balancing National Security and Constitutional Protections

The primary justification for the ICDC is the enhancement of national security through improved intelligence capabilities. Proponents argue that streamlined access to CAI enables more effective threat detection and response. However, this must be balanced against the fundamental rights enshrined in the Constitution. The Fourth Amendment serves as a critical check on government power, ensuring that citizens are protected from unwarranted intrusions into their private lives. The ICDC’s approach to data acquisition bypasses traditional legal processes and thus poses a significant threat to these protections. Further, the potential for mission creates significant concerns about the long-term implications for civil liberties. Without clear boundaries and oversight, the ICDC could become a tool for pervasive surveillance, undermining public trust in government institutions. The Panopticon will have arrived.

Safeguarding Privacy

While perils exist, so do controls that can mitigate the risks associated with the ICDC. The establishment of clear legal frameworks is a good start. Legislation must define the scope and limitations of data collection activities, ensuring that they align with constitutional protections and privacy rights. Robust oversight mechanisms, much like FISA must be established. Independent oversight bodies must be empowered to monitor the ICDC’s operations, conduct audits, and enforce compliance with legal and ethical standards. Transparency must be the guiding rule. The intelligence community should be obligated to provide regular reports on data acquisition activities including the types of data collected, the purposes for which it is used, and the safeguards in place to protect privacy. Those reports can and should be the basis for engagement with civil society organizations, privacy advocates, and the public. Being open about this will foster a more informed discourse on the balance between national security and those individuals and groups affected by the OSINT activity.

The Intelligence Community Data Consortium represents a significant shift in how the U.S. intelligence community accesses and utilizes commercially available information. While it offers potential benefits for national security, it also poses substantial risks to the privacy and constitutional rights of American citizens. To ensure that the pursuit of security does not come at the expense of civil liberties, it is imperative to establish clear legal frameworks, robust oversight, and transparent practices that uphold the principles of a democratic society.

~ C. Constantin Poindexter, MA Intelligence, Grad. Cert. Counterintelligence, JD, CISA/NCISS OSINT cert., DoD/DoS BFFOC

References

Office of the Director of National Intelligence. (2025). OSINT Contract Framework. Retrieved from ODNI Document

The Intercept. (2025, May 22). US Plans Data Portal to Expand Warrantless Surveillance. Retrieved from The Intercept Article

Wired. (2025, May 24). Security News This Week: The US Is Building a One-Stop Shop for Buying Your Data. Retrieved from Wired Article

Brennan Center for Justice. (n.d.). The Intelligence Community’s Policy on Commercially Available Data Falls Short. Retrieved from Brennan Center Article

U.S. Senate. (2023). Privacy Act of 1974. Retrieved from Wikipedia Article

U.S. Senate. (2023). Foreign Intelligence Surveillance Act. Retrieved from Wikipedia Article

Wired. (2023, November 20). Secretive White House Surveillance Program Gives Cops Access to Trillions of US Phone Records. Retrieved from Wired Article

AP News. (2023, September 28). A Key US Government Surveillance Tool Should Face New Limits, a Divided Privacy Oversight Board Says. Retrieved from AP News Article

Time. (2024, March 15). Inside the White House Program to Share America’s Secrets. Retrieved from Time Article

AP News. (2024, March 10). Book Review: ‘Means of Control’ Charts the Disturbing Rise of a Secretive US Surveillance Regime. Retrieved from AP News Article

Share this post: