Stealing From the Spooks is now a monograph

In September I posted a short piece on this blog called Stealing From the Spooks. The argument was simple. The United States Intelligence Community got burned, publicly and catastrophically, by its own mind-sets, and it responded by writing down how its analysts ought to think and then drilling it. Police departments have the same failure mode and, in wrongful convictions and unsolved cases, the same body count. So why in the world has policing not stolen the cure?

The post got more reaction than anything I have written on the subject. Analysts wrote to say they had been fighting that fight alone in their squad rooms for years. A couple of prosecutors wrote to say they had never once seen a written hypothesis matrix in a case file and would pay money for one. One detective wrote to tell me I was full of it, which is fair, and then asked where he could read more. That last question did not have a good answer. The blog post was a sketch. So I wrote the book.

Stealing From the Spooks: Structured Analytic Techniques for Law Enforcement Crime Analysis is a sixty page monograph, free, and you can download it here: ConstantinPoindexterAuthor.com. There is no paywall and no email form. Print it, hand it to your lieutenant, leave it on the prosecutor’s desk.

Where the ideas come from

Let me be clear about credit, because the title is a confession. The twelve techniques in the monograph are not mine. They come from a forty page unclassified document the US Government published in 2009, A Tradecraft Primer: Structured Analytic Techniques for Improving Intelligence Analysis, which in turn stands on Richards Heuer’s The Psychology of Intelligence Analysis. Heuer’s diagnosis is the whole foundation: analysts do not fail for lack of information, they fail because the human mind decides which facts to notice before conscious thought ever gets a vote (Heuer 1999; US Government 2009). Anyone who has watched a homicide squad lock onto a suspect in the first seventy two hours and then spend months bending every new fact to fit knows exactly what he was describing. The wrongful conviction literature calls it tunnel vision (Findley and Scott 2006). Heuer called it a mind-set. It is the same animal.

What is mine is the translation. The primer was written for people who track missile programs. I rebuilt it for the detective sergeant staring at a whiteboard full of string, the civilian crime analyst who can smell that the squad’s theory is running ahead of its evidence, the supervisor who signs charging recommendations, and the prosecutor who inherits whatever the investigation did or did not think about. Every chapter follows the same plan: what the primer says, what it looks like in a case file, how to run it with the people and hours a real unit actually has, and where it goes wrong.

What is in it

The primer sorts its techniques into three families, and the monograph keeps that order. The diagnostic techniques make the argument visible: the Key Assumptions Check, the Quality of Information Check, indicators, and Heuer’s Analysis of Competing Hypotheses. The contrarian techniques attack it on purpose: Devil’s Advocacy, Team A/Team B, High-Impact/Low-Probability analysis, and “What If?” analysis. The imaginative techniques go looking for the theories and futures nobody in the room has thought of yet: structured brainstorming, outside-in thinking, red teaming, and alternative futures.

Each one gets a worked example built for police work. A burglary series with an assumptions register that exposes two assumptions resting on nothing but habit. A shooting investigation with a source log that shows, in one column, that the whole theory is standing on a paid informant with secondhand knowledge and an identification run by a detective who already had a favorite. An arson matrix in which the squad’s two favorite facts, the unpaid rent and the increased insurance coverage, turn out to be consistent with every hypothesis on the board and therefore eliminate nobody. That last one is the lesson I most want a working detective to take away. A case is not built by piling up facts that fit. It is built by eliminating the explanations that do not.

The primer’s own showcase example, by the way, is a police case. During the 2002 Washington sniper shootings the working theory was a lone white male with military training in a white van. The primer breaks that sentence into its five assumptions and grades each one. The shooters were two Black males, one of them seventeen, in a blue Chevrolet Caprice that officers had run more than once during the spree. Nobody had written down that the investigation was assuming a van, so nobody recognized the Caprice as a contradiction of anything. You cannot notice the violation of an assumption you never admitted making. That sentence is the monograph in miniature.

The objection, and the answer

The pushback I hear most from investigators is legal, not analytical. “If we write down our doubts, the defense gets them.” The monograph spends a full chapter on that, because it is the objection that kills the practice before it starts. The short version: assume the defense will read every analytic product you write, and understand that this is a feature. Under Brady and Kyles the prosecution already owes the accused everything favorable that the police know, whether the prosecutor has heard about it or not. A dated matrix of considered and rejected hypotheses, a source log that recorded the informant’s motive on day one, a labeled devil’s advocate memo showing the department tried to break its own case before asking a jury to believe it: those are the things that survive cross examination. The cases that fall apart are the ones where the doubt existed, went unrecorded, and came out anyway, ten years later, in a habeas petition.

I also wrote a chapter the enthusiasts will not like, on the limits. The experimental evidence that these techniques make any individual analyst more accurate is thin, and the serious critics have a point (Chang et al. 2018; Dhami, Belton, and Mandel 2019). My answer is that accuracy is not the strongest argument for them in policing. Transparency is. A criminal case gets its accuracy from adversarial testing, and adversarial testing needs something written down to test. A theory that lives only inside the lead investigator’s head can be reviewed by no one.

For the chief who has read this far

The last part of the monograph is a program, not a sermon. A one page directive. A table of who owns what, with the civilian analyst as the owner of the method, deliberately, because the analyst is the person in the building least invested in the lead detective’s theory and least able to challenge it without standing. A ninety day rollout. A way to measure whether any of it is working that does not depend on the clearance rate. And a note for the nine officer department with no analyst, which can still do this with one sheet of paper and a devil’s advocate borrowed from the agency next door.

If a department adopts only three things from the whole document, they should be the assumptions register, the source log, and a devil’s advocate before charging. They are the cheapest. They catch the most.

The appendices hold blank worksheets for all of it and a supervisor’s checklist to run before a charging recommendation goes up. Photocopy them. That is what they are for.

Why I bother

I spent years inside the community that invented this discipline, and I carried a badge before that. I have sat in both rooms. The analytic cadre at Langley and the detective squad in a county building are closer cousins than either would admit: incomplete information, people who lie, a hierarchy in which the senior person’s theory becomes everyone’s theory, and a long record of confident error traced afterward to assumptions nobody wrote down. One of those communities got humiliated badly enough to fix it. The other is still running investigations with the analytic rigor of a bar argument.

The framework is public, it is free, and it is forty pages long. There is no excuse left for not using it. I put sixty more pages around it so there would be even less.

A Spanish edition, Robándoles a los Espías, is ready as well and will be posted separately on the author’s law firm blog for colleagues in the Dominican Republic, Puerto Rico, and the rest of the hemisphere.

~ C. Constantin Poindexter Salcedo, MA en Inteligencia, Certificado de Posgrado en Contrainteligencia, JD, certificación OSINT CISA/NCISS, Diplomado Negociación Estratégica de Harvard, Certificación BFFOC del DoD/DoS

References

  • Chang, Welton, Elissabeth Berdini, David R. Mandel, and Philip E. Tetlock. 2018. “Restructuring Structured Analytic Techniques in Intelligence.” Intelligence and National Security 33 (3): 337-356.
  • Dhami, Mandeep K., Ian K. Belton, and David R. Mandel. 2019. “The ‘Analysis of Competing Hypotheses’ in Intelligence Analysis.” Applied Cognitive Psychology 33 (6): 1080-1090.
  • Findley, Keith A., and Michael S. Scott. 2006. “The Multiple Dimensions of Tunnel Vision in Criminal Cases.” Wisconsin Law Review 2006 (2): 291-397.
  • Heuer, Richards J., Jr. 1999. The Psychology of Intelligence Analysis. Washington, DC: Central Intelligence Agency, Center for the Study of Intelligence.
  • US Government. 2009. A Tradecraft Primer: Structured Analytic Techniques for Improving Intelligence Analysis. March 2009.
Share this post:

The Intelligence Cycle at NATO’s Northeastern Flank: A Critique

NATO's intelligence cycle argument.

My review of the field study of the intelligence cycle at Multinational Corps Northeast published in the International Journal of Intelligence and CounterIntelligence

This is a valuable article and an uneven one. As a body of evidence it is well above the standard of the journal in which it appears. As a work of social science it is middling, and as a test of the intelligence cycle as a model it does not succeed. The authors gathered a dataset that exists nowhere else in the open literature and reported what they found with a candor that argues for its credibility. They then asked that data to carry a theoretical conclusion it cannot bear, and they described their method in terms that do not match what they actually did. I recommend the piece without reservation as a snapshot of how a NATO corps practiced intelligence in the first year of the Russo-Ukrainian war, and as a pointer to two questions the field has neglected. I do not accept its closing claim that the results “largely reflect the academic critique on the intelligence cycle.” What they reflect is a cycle that was not being run.

The evidence is strong. Why?

The access alone justifies publication. Forty-nine semi-structured interviews with fifty-six respondents of fourteen nationalities, across nine units and commands in four countries, conducted inside cleared NATO working spaces between May and October 2022. No outside researcher obtains this, and the authors are honest that their own clearances, service backgrounds and cultural fluency were the price of admission. The timing matters as much as the volume. The interviews took place while the corps was digesting an Article 5 threat that its requirements, exercises and mandate had not anticipated.

The authors are also correct about the gap they fill. The debate over the intelligence cycle has run for two decades on the strength of Hulnick, Omand, Davies and a handful of others, and it has done so almost entirely without field data. NATO itself is nearly invisible in the two flagship journals. The bibliometric exercise the authors use to show this is crude, but the point stands and I have not seen it made before.

The findings are concrete and unflattering, which is precisely why I believe them. Priority intelligence requirements that drive nothing. A requirements and collection management function that every analyst routes around and that its own officers describe as having nothing to bring to a synchronization meeting. Open source work performed on a handful of internet terminals by staff who have never attended an OSINT course. The A through F and 1 through 6 source grading scheme collapsing the moment it is applied to a news article. Circular reporting infecting the shared databases because uploaded products carry no original sourcing. Analysts who have never once received feedback on a finished product. A major exercise in late 2021 run on a counterinsurgency scenario while a conventional threat gathered on the border. These are the details only insiders capture, and the authors captured them.

Two contributions are new rather than confirmatory. The first is the identification of Intelligence Requirement Management and Collection Management as the doctrinal mechanism the academic feedback critique has ignored. The critics have long argued that the cycle hides its feedback loops. NATO doctrine actually names a process to manage those loops, and this study shows it broken in practice. The second is the observation that practitioners critique the cycle only as proceduralists, complaining that the procedure malfunctions, while academics critique it as conceptualists, arguing that the model is wrong. That the two conversations do not touch is the most interesting thing in the paper and deserves an article of its own.

Why the argument doen’t make it

The central weakness is a confound the authors half acknowledge and then set aside. Multinational Corps Northeast in 2022 was a peacetime headquarters with a limited operational mandate and essentially no organic collection. Requirements were frozen around the Zapad exercises. The commander’s engagement with the requirements was, by the respondents’ account, minimal. A cycle with no collection assets, no direction and no consumer pull is not a test of whether the intelligence cycle is a valid model of intelligence. It is a starved cycle. The “self-organizing cycle” the authors describe, in which open source reporting and current events drive production and direction arrives last if at all, may say a great deal about mandate and posture and very little about the model. The case cannot discriminate between the proposition that the cycle is wrong and the proposition that the cycle was not being operated. A defensible conclusion would have been narrower: peacetime corps-level intelligence in NATO does not function as a cycle. The authors reached for the broader claim instead.

The methodology is dressed above its station. The authors invoke the Gioia method, which is inductive by design and insists on staying close to respondent terminology without preconceived categories. They then state, in the same section, that interviews were structured along the main lines of the academic critique of the cycle and that coding labels were drawn from that critique and from the proceduralist and conceptualist distinction. That is a deductive, theory-driven design wearing grounded theory clothing. There is no data structure figure, which is the signature artifact of the Gioia approach, no account of how first-order codes became second-order themes, and no measure of coder agreement. The results read as a competent thematic sort against a prior framework. That is a legitimate thing to do. It should be called what it is.

Sampling is a mixture of commander selection, volunteers, snowball referral and chance encounters. In a rank hierarchy, respondents chosen by their commanders are a known source of bias, and the authors do not discuss it. Forty-two of fifty-six respondents were intelligence personnel and only fourteen were consumers, yet the core finding concerns the absence of direction from the commander and his staff. The consumer side of that story is barely heard. Interviews could not be recorded, so every quoted line in the results is a reconstruction from two note takers, presented as verbatim. Participant observation and document study appear in the methods section and then never visibly enter the results. No triangulation is shown.

The authors’ insider position is handled well as a matter of access and ethics but not as a matter of interpretation. They are serving or former military intelligence professionals at a national defense academy. Their prescriptions, better alignment of organization to doctrine and more emphasis on IRM&CM in NATO training, are thoroughly proceduralist. Having diagnosed their respondents as unable to think outside the proceduralist frame, the authors then prescribe from inside it without noticing that they have done so.

Smaller matters accumulate. A counterintelligence review of the draft, together with a four-year lag between data collection and publication, means an unknown quantity of material was removed or softened. The corps’ structure and NATO’s northeastern posture have changed materially since 2022, and the note that respondents will have rotated addresses security but not currency. The claim that the findings “have validity outside the case” is asserted in a single sentence rather than argued. Several evaluative statements, that a particular maritime pattern analysis was “extremely valuable” or that certain OSINT fixes are “relatively easy,” carry no supporting evidence. The prose needed another pass; the grammatical slips are frequent enough that the journal’s copyediting should have caught them.

My Take

Read this article as an authoritative account of how a NATO corps actually did intelligence in the opening year of the war, and as the first empirical demonstration that the feedback problem the theorists have described for twenty years has a doctrinal name and an organizational home. Do not read it as settled evidence against the intelligence cycle as a model. The case was never in a position to deliver that verdict, and the authors should have said so.

~ C. Constantin Poindexter, MA in Intelligence, Graduate Certificate in Counterintelligence, JD, CISA/NCISS OSINT certification, DoD/DoS BFFOC Certification, Criminal Intelligence Analyst Classification 1 (IALEIA)

Share this post:

Hey TSCM Crew! The Cable Was Always Talking

Hey TSCM Crew! The Cable Was Always Talking, TSCM, counterintelligence, counterespionage, spy, countermeasures, C. Constantin Poindexter

TrojPix, TEMPEST, and the Eternal Return of the Compromising Pixel, my counterintelligence reading for those who own more than one spectrum analyzer

Every eighteen months or so, the security-adjacent internet rediscovers that copper radiates. There is a burst of excitement, a headline containing the word “unhackable” in scare quotes, and a great many people who have never held a near-field probe explaining to one another that air-gapped systems are now obsolete. Then everyone goes back to leaving the SCIF door propped open with a fire extinguisher.

This cycle’s entry is TrojPix, and credit where it is due, a good paper. It is not, however, a game-changer.

What the researchers actually did

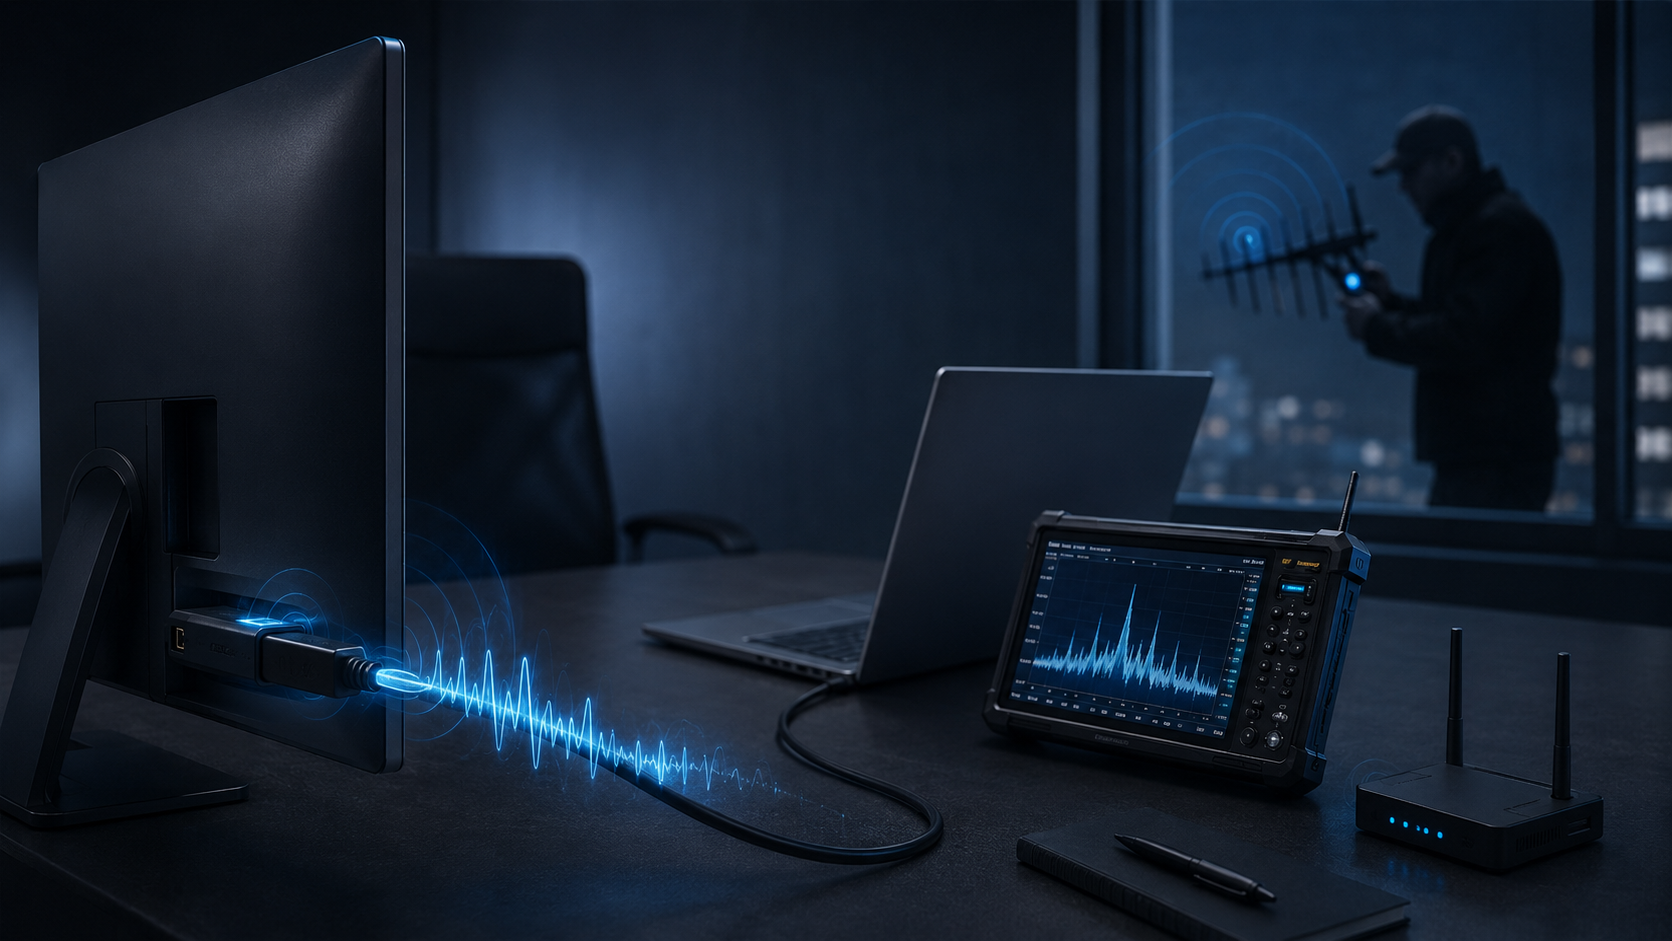
TrojPix comes out of Shandong University and Quan Cheng Laboratory, authored by Guoming Zhang and colleagues, and is accepted to the 35th USENIX Security Symposium (Zhang et al. 2026). The mechanism is elegant in its parsimony. Digital video interfaces encode pixel data using Transition-Minimized Differential Signaling, and TMDS (being a high-speed switching serial protocol over unbalanced-enough copper) radiates. Everyone has known this since the 80s.

The contribution is that the authors demonstrate the mapping is deterministic and controllable. Modify pixel values in a way the human visual system cannot resolve, the canonical example being the least significant bit of the blue channel, and you produce a predictable, addressable change in the electromagnetic signature on the cable. The display becomes a modulator. The cable becomes the antenna. User-mode malware becomes a transmitter without touching a driver, a device, or an administrator’s password.

They evaluated across nine COTS monitor manufacturers and fifteen COTS video cables, in two operational modes: fake screen-off, in which the display appears dark while continuing to transmit, and foreground embedding, in which the payload rides inside whatever the user is legitimately looking at. Reported results: peak throughput of 8.1 Mbps, maximum range of 208 meters, average bit correct rate around 99 percent, and structural similarity indices of 0.998–0.999 with a fifty-person perceptual study in which nobody noticed anything (Zhang et al. 2026). The prior state of the art in this niche managed 21.6 kbps at 87.5 meters (The Hacker News 2026). That is genuinely good engineering. Now let us be adults about it.

The 8.1 Mbps that does not exist at 208 meters

The single most-repeated distortion in the coverage, and in every breathless social media repost, is the implicit bundling of peak throughput and maximum range into one system. They were measured separately, a point The Hacker News (2026) had the discipline to state explicitly and almost nobody else did.

This should be obvious to anyone who has ever done a link budget. Channel capacity is a function of signal-to-noise ratio. SNR falls off with distance, and the emission in question is an unintended one, meaning the transmit power is whatever leaked out of a cable that was designed to comply with FCC Part 15 and CISPR 32. You do not get megabit rates at two hundred meters off parasitic radiation. You get megabit rates in the lab at short standoff, and you get the two-hundred-meter figure at a data rate that would embarrass a 1200-baud modem. Both numbers are true. A sentence containing both of them is NOT.

The receiver is not in anyone’s pocket

The reporting indicates the collection side used a USRP X310 with a directional antenna and a low-noise amplifier. That is several thousand euros of gear, commercially available, but not a dongle taped to a Raspberry Pi in a hedge (HackingPassion 2026). This matters enormously, and it matters in the counterintelligence/countermeasures favor.

Think about what the adversary’s collection geometry actually requires: a stable, powered, aimed platform maintaining a favorable path to a specific building elevation, for however long the exfiltration takes, without being noticed. That is not a cyber problem. That is a physical surveillance detection problem, i.e., the discipline in which our C.I. community has ninety years of institutional practice. The attack has not defeated the perimeter. It has converted the adversary’s problem into one that is squarely inside your area of competence, and made it harder for him, because now he has to bring an ice cream truck or telco-looking van.

Priority, or: read your own literature

Wim van Eck (1985) published the foundational demonstration that video display emanations could be reconstructed at a distance. Thirteen years later, Markus Kuhn and Ross Anderson described “Soft Tempest”, and here it is worth quoting their own framing of the attack case, malicious code encoding stolen information in a machine’s RF emissions, optimized for some combination of reception range, receiver cost, and covertness, specifically via the video cable (Kuhn and Anderson 1998, 124–42). Kuhn’s dissertation extended this to displays generally (Kuhn 2003), Loughry and Umphress (2002) did the optical analogue, and Mordechai Guri has spent a decade industrializing the entire genre, most relevantly with PIXHELL, which modulates pixel patterns to produce acoustic emissions from LCD coils and capacitors (Guri 2024).

TrojPix is Soft Tempest with twenty-eight years of better DSP, a modern SDR, and a proper imperceptibility evaluation. That is a real contribution. It is an engineering delta, not a conceptual one, and describing it as a “new air-gap bypass” is a bit like announcing the discovery of the wheel with rubber on it.

The precondition swallows the finding

TrojPix is an exfiltration channel. It is not an access vector. The malware must already be resident on the isolated host, which means it arrived by the ordinary routes, i.e., a dirty thumbdrive, supply chain, firmware, a human being with a badge and a grudge, etc. Stuxnet and Agent.BTZ crossed air gaps on USB drives, not over radio.

So the risk equation is unchanged in its dominant term. If the adversary can get arbitrary code onto an isolated machine, you have a very serious problem already. The interesting question was never whether he could get the data out. It was whether he could get 400 megabytes out in six minutes instead of dribbling an AES key over a weekend. TrojPix improves his egress bandwidth. It does not improve his ingress.

The threat model wanders off the reservation

The paper, and every article about it, invokes military command centers, nuclear control systems, and financial institutions. Note what was actually tested, i.e., consumer monitors from Dell, Samsung, LG, AOC, Philips, Lenovo, TCL, Huawei, and Redmi, and fifteen commodity cables (Cyber Press 2026). Facilities that genuinely hold the data being invoked do not run Redmi panels on unshielded HDMI. They run inspectable-space doctrine, RED/BLACK separation, shielded enclosures, and equipment procured against emanation-security criteria, i.e., the framework that has existed since NSTISSAM TEMPEST/1-92 and its national equivalents. If your accredited space is leaking recoverable TMDS at 208 meters, TrojPix is not your problem. You’ve f. up and your accreditation is. Conversely, in the open-plan office where those Redmi monitors actually live, there is a wireless network and the adversary will simply use it, because he is not a masochist.

What the sweep community should actually take away are three things, none of which fit in a post, but here we go.

The emission is physics, so the countermeasures are physical. Fiber-optic video links carry no exploitable copper transient. Shielding, zone control, and RF jamming of the relevant band remain the answers they have always been. No patch removes Maxwell’s equations from the environment.

Deliberate modulation is, paradoxically, easier to catch than passive leakage. A van Eck emanation is an unstructured artifact. A TrojPix emission is a structured, periodic, deliberately regular signal bearing a fixed relationship to the pixel clock. Structure is what your analyzer is for. The implication is not that sweeps are futile; it is that episodic sweeps are futile and persistent spectrum monitoring against a characterized baseline is not.

The fake-screen-off mode is a gift. A monitor that is off should not be receiving an active TMDS stream. That is a host-side, software-detectable state inconsistency, and it costs nothing to instrument. The stealthiest mode in the paper is also the one with the loudest logical tell.

The authors withheld operational detail and initiated disclosure with cable manufacturers, and nothing resembling this has been observed in the wild (HackingPassion 2026). It is laboratory work mapping the boundary of the physically possible, which is precisely what USENIX exists to publish.

I am recognizing here and sharing that the air gap was never a control. It is a topology. Anyone who mistook it for a control had a problem long before a graduate student in Jinan started flipping the blue channel. So, no. A collector can’t just sit 200m away and read your mail, but, . . .

~ C. Constantin Poindexter, MA in Intelligence, Graduate Certificate in Counterintelligence, JD, CISA/NCISS OSINT certification, DoD/DoS BFFOC Certification

Bibliography

  • Cyber Press. 2026. “TrojPix Attack Uses Imperceptible Pixels to Steal Data From Air-Gapped Networks.” July 2026. https://cyberpress.org/trojpix-attack-air-gapped/.
  • Guri, Mordechai. 2024. “PIXHELL Attack: Leaking Sensitive Information from Air-Gap Computers via ‘Singing Pixels.'” Offensive Cyber Research Lab, Ben-Gurion University of the Negev.
  • HackingPassion. 2026. “TrojPix Steals Data From Air-Gapped Computers Through the Screen.” July 2026. https://hackingpassion.com/trojpix-air-gap-attack/.
  • Kuhn, Markus G. 2003. “Compromising Emanations: Eavesdropping Risks of Computer Displays.” PhD diss., University of Cambridge. Technical Report UCAM-CL-TR-577.
  • Kuhn, Markus G., and Ross J. Anderson. 1998. “Soft Tempest: Hidden Data Transmission Using Electromagnetic Emanations.” In Information Hiding: Second International Workshop, IH’98, edited by David Aucsmith, 124–42. Lecture Notes in Computer Science 1525. Berlin: Springer.
  • Loughry, Joe, and David A. Umphress. 2002. “Information Leakage from Optical Emanations.” ACM Transactions on Information and System Security 5 (3): 262–89.
  • Poller, Jack. 2026. “When ‘Air-Gapped’ Stops Meaning Anything: What TrojPix Should Teach Every CISO.” Security Boulevard, July 8, 2026. https://securityboulevard.com/2026/07/when-air-gapped-stops-meaning-anything-what-trojpix-should-teach-every-ciso/.
  • The Hacker News. 2026. “New TrojPix Attack Leaks Data From Air-Gapped Systems via Video Cable Emissions.” July 2026. https://thehackernews.com/2026/07/new-trojpix-attack-leaks-data-from-air.html.
  • van Eck, Wim. 1985. “Electromagnetic Radiation from Video Display Units: An Eavesdropping Risk?” Computers & Security 4 (4): 269–86.
  • Zhang, Guoming, Huiting Zhang, Zhenwei Lu, Heqiang Fu, Xin Gao, Riccardo Spolaor, Yetong Cao, Yanni Yang, and Pengfei Hu. 2026. “TrojPix: Electromagnetic Covert Channels via Imperceptible Pixel Modulation.” In Proceedings of the 35th USENIX Security Symposium. Berkeley, CA: USENIX Association. https://www.usenix.org/conference/usenixsecurity26/presentation/zhang-guoming.
Share this post:

The Indispensable Discipline: HUMINT’s Enduring Primacy in the Age of A.I.

HUMINT, intelligence, counterintelligence, espionage, counterespionage, spy, C. Constantin Poindexter, CIA, NSA, DNI, J2

The September 2025 GTG-1002 operation in which a Chinese state-sponsored actor manipulated an agentic AI system into executing an estimated 80 to 90 percent of a multi-target cyber espionage campaign, has been framed as evidence that machines are displacing human beings from the craft of intelligence (Kerr 2026). The inference is understandable but analytically wrong. A close reading of the declassified and academic literature, including the CIA’s own March 2026 assessment in Studies in Intelligence, supports the opposite conclusion: artificial intelligence is not rendering human intelligence obsolete; it is raising HUMINT’s relative value while transforming its tradecraft. This essay advances five arguments for HUMINT’s continued indispensability in collection and counterintelligence.

The Intentions Problem Remains Unsolved (and Unsolvable by Sensors)

The foundational epistemological limit of technical collection has not moved. Declassified U.S. doctrine has stated it plainly for decades: human collectors provide insight into an adversary’s intentions, whereas technical systems are largely confined to determining capabilities (Interagency OPSEC Support Staff 1996; USAF Pamphlet 14-210, 1998). AI dramatically accelerates the processing of what sensors collect, i.e., imagery, signals, telemetry, but it cannot collect what is never emitted. A leadership decision taken in a closed room, an unwritten contingency plan, a dictator’s private threshold for escalation: these exist only in human minds and reach analysts only through human access.

The historical record is unambiguous. Oleg Penkovsky’s reporting on Soviet missile capabilities during the Cuban Missile Crisis, and the HUMINT deficit that former DCIA John Brennan identified as central to the 2003 Iraq WMD misjudgment both illustrate that the decisive intelligence failures and successes of the modern era turn on human access, not processing power (Lobo Institute 2023). The problem compounds against disciplined adversaries: leaders such as Vladimir Putin, himself a former intelligence officer, deliberately minimize electronic emission of intent, structurally degrading SIGINT and any AI built atop it. No large language model, however capable, can synthesize a signal that was never transmitted. AI is an analytic multiplier of collected data; HUMINT remains the only discipline that collects the interior world of decision-making.

AI-Generated Fabrication Makes Validated Human Sources the Epistemic Anchor

The second argument is the one the intelligence community itself now advances. Mulligan (2026), writing in Studies in Intelligence, argues that because AI will supercharge disinformation and fabrication, HUMINT’s capacity to build and test source reliability over time (and to corroborate technical collection) becomes more important. In an information environment saturated with synthetic text, deepfaked audio and video, and machine-generated documents indistinguishable from authentic material, every technical stream becomes contestable. Adversary services can now feed AI-fabricated “collection” into an opponent’s technical apparatus at negligible cost, weaponizing the very volume that makes AI analysis attractive.

A recruited human source subjected to years of vetting, whose access is mapped, whose reporting is tested against ground truth, whose motivations are continuously assessed under established frameworks, offers something no algorithm can, . . . a provenance chain rooted in a verifiable human being. The all-source doctrine of corroboration (Interagency OPSEC Support Staff 1996) presumed technical streams would validate human reporting. The polarity is now reversing: in a synthetic-media environment, the validated human source increasingly authenticates the technical take. Counterintelligence inherits the mirror-image burden, distinguishing genuine walk-ins from AI-managed synthetic personas, which is itself a human validation function that cannot be delegated to the class of systems creating the problem.

The Economics of Marginal Value: Commoditized Technical Collection Raises HUMINT’s Premium

Mulligan’s (2026) second core claim is economic: as AI makes high-quality technical collection cheaper and more accessible, it boosts HUMINT’s value on the margin. This follows from basic scarcity logic. When frontier models, commercial imagery, and automated OSINT exploitation diffuse to middle powers, non-state actors, and well-resourced private entities, technical collection ceases to confer comparative advantage. It becomes table stakes. The Microsoft–OpenAI disclosures of February 2024 (five state-affiliated actors from four adversary nations using LLMs for reconnaissance and social engineering) demonstrate how rapidly these capabilities proliferate below the great-power threshold (Kerr 2026).

What cannot be commoditized is a penetration of the Politburo, the IRGC, or a proliferation network. Exquisite human access is the one collection asset that neither compute nor capital can replicate at scale, because it is produced by trust cultivated over years, in person, under discipline. In a world where every service runs comparable models over comparable data, the differentiating intelligence advantage accrues to the service that owns the sources no model can reach. Rational resource allocation, therefore, shifts toward the scarce discipline, not away from it.

Denied Environments and the Human Enabler: AI Cannot Cross the Air Gap

GTG-1002’s target set — networked technology firms, financial institutions, and agencies — obscures what the operation could not reach: air-gapped, compartmented, and physically isolated systems where states keep their most consequential secrets. The academic literature on the digital era’s collection debate is consistent on this point. Cyber operations against isolated networks require human agency, the asset who carries the implant, describes the facility’s internal arrangement, or provides the credential that no remote exploitation can obtain (Lobo Institute 2023). Declassified targeting doctrine long ago codified HUMINT’s unique coverage of denied spaces. Underground facilities, internal plant layouts, and infrastructure invisible to overhead systems (USAF Pamphlet 14-210, 1998 are the golden prize.

The most celebrated technical operations in intelligence history were HUMINT-enabled at their inception, and the AI-era variants will be no different. The stark lesson of GTG-1002 is not that AI replaced spies; it is that even a substantially autonomous cyber campaign still required human operators at the strategic decision points, and was ultimately constrained to targets reachable over the open internet. The hardest targets remain human-access problems.

Trust, Accountability, and the Human-Machine Team: Recruitment Is Not Automatable at the Decisive Node

The final argument concedes the strongest counter-case in order to defeat it. The Special Competitive Studies Project’s Digital Case Officer (2025) demonstrates that AI can spot, assess, and even develop targets, managing hundreds of developmental conversations through hyper-realistic personas. Yet the same report concludes that meaningful human control is non-negotiable at every critical juncture: the recruitment decision, asset tasking, and any act carrying significant risk must rest with an accountable human officer (SCSP 2025). This is not regulatory sentimentality; it is operational realism. Espionage asks a human being to commit treason, an act of existential personal risk. The bond that sustains an asset through that risk, and the judgment required to detect when that bond is fraying, when an agent is fabricating for money or has been doubled is, in the words of SIS Chief Richard Moore, obstinately human (Moore 2023, cited in Poindexter 2025).

Mulligan (2026) adds the counterintelligence corollary: ubiquitous technical surveillance and AI pattern analysis make traditional street tradecraft vastly more dangerous, but the institutional response (virtual HUMINT, AI-augmented cover, human-machine teaming) is a transformation of the case officer’s toolkit, not the abolition of the case officer. The discipline that survives every technological revolution by absorbing it, from the telegraph to SIGINT to the internet, is absorbing this one on the same terms.

My Take

The pattern across the declassified doctrine, the CIA’s in-house scholarship, and the contemporary threat reporting is coherent. AI collapses the cost of processing, fabrication, and technical reach. In doing so it leaves the intentions gap untouched, elevates validated human sources into the epistemic anchor of all-source analysis, raises HUMINT’s marginal value as technical collection commoditizes, preserves the human enabler as the sole key to denied and air-gapped targets, and leaves the trust-and-accountability core of recruitment beyond automation. HUMINT will not merely survive the age of artificial intelligence. As the CIA’s own journal concludes, the oldest collection discipline will grow in importance precisely because of it.

~ C. Constantin Poindexter, MA in Intelligence, Graduate Certificate in Counterintelligence, JD, CISA/NCISS OSINT certification, DoD/DoS BFFOC Certification

References

  • Interagency OPSEC Support Staff. 1996. Intelligence Threat Handbook, Section 2: Intelligence Collection Activities and Disciplines. Declassified; Federation of American Scientists archive.
  • Kerr, Stuart. 2026. “AI Espionage: How State Actors Are Using Language Models to Gather, Synthesise, and Act on Intelligence at Scale.” LiveAIWire, July 8, 2026.
  • Lobo Institute. 2023. “The Relevance of HUMINT in the Digital Era.”
  • Mulligan, Thomas. 2026. “Espionage in Our AI Future: Why Human Intelligence Still Matters.” Studies in Intelligence 70, no. 1 (Extracts, March 2026). Central Intelligence Agency, Center for the Study of Intelligence.
  • Poindexter, C. Constantin. 2025. “Nueva frontera para la inteligencia humana en la era de la I.A.” Review of SCSP, The Digital Case Officer.
  • Special Competitive Studies Project (SCSP). 2025. The Digital Case Officer: Reimagining Espionage with Artificial Intelligence. September 2025.
  • U.S. Air Force. 1998. USAF Intelligence Targeting Guide, AF Pamphlet 14-210, Attachment 3: Sources of Intelligence. Declassified; FAS archive.

Share this post:

The Gabbard–Butler Matter as Counterintelligence Disaster, a Controller in the Blind Spot

Tulsi Gabbard, ODNI, DNI, espionage, counterespionage, intelligence, counterintelligence, CIA, NSA, C. Constantin Poindexter

There is nothing pretty at all about this Tulsi Gabbard insanity. The documented relationship between former Director of National Intelligence Tulsi Gabbard and Chris Butler, founder of the Science of Identity Foundation (SIF), constitutes a counterintelligence failure of f* first order. Drawing on the Washington Post investigation by Jon Swaine (2026) and the broader scholarly and governmental literature on high-control groups, I assess that the preponderance of indicators points to a ranking member of the Intelligence Community who was, at minimum, subject to sustained, concealed, and operationally structured external direction by a fringe cult of personality. I situate the issue within the established framework of undue influence and the agent-of-influence problem, and I argue, with some comparison to six historical cases (the Unification Church, the Church of Scientology, Aum Shinrikyo, the Rajneeshpuram commune, the Peoples Temple, and NXIVM), that the United States possesses ample precedent for treating charismatic-leader organizations as national security threats rather than as private spiritual matters. The distinguishing and aggravating feature of the present case is the controller’s tradecraft of concealment, which mirrors the operational security of a hostile clandestine service and may well have defeated, for more than a decade, the vetting mechanisms that should have DQ’d this crazy lady.

My thesis stated plainly

A counterintelligence operator does not require proof of espionage to break the glass. The discipline is preventive and structural. It concerns itself with vulnerabilities, channels, and concealment long before it concerns itself with the transfer of any specific secret. By that standard, the facts now in the public record describe a disaster. A person who rose to the statutory apex of the United States Intelligence Community, with derivative access to the most sensitive compartmented information the government produces, appears to have operated for much of her political career under the directive influence of an unaccountable external oddball, through a channel deliberately engineered to evade discovery, while publicly denying the relationship that the now publicly aired documentary record describes (Swaine 2026). That sentence, if its components hold, is a textbook description of the precondition for compromise. I am not stating that Tulsi Gabbard was a foreign agent. I don’t subscribe to bullshit conspiracy theories and I am not C.I.-spooky enough to see an enemy behind every corner, however, the architecture of her influence relationship is indistinguishable, in its mechanics and its concealment, from the architecture a hostile service would build. This architecture was permitted to reach the top of the I.C. either undetected or, detected and ignored. I am not going to address Gabbard’s bullshit support of dictators and despots, as that is outside of my purpose here, however, my thoughts about what Swaine has reported may leave you wondering about her positions on Syria, Russia and other U.S. adversaries.

The evidentiary record

The factual spine of my assessment is the year-long investigation by Washington Post reporter Jon Swaine, who obtained more than twenty-five thousand pages of emails, memos, and related messages, including hundreds of confidential memos spanning the years 2011 to 2017, most of them coinciding with Gabbard’s first two congressional terms (Swaine 2026). The material was furnished by Rebecca Saltzburg, a former SIF member who had worked on digital strategy for several of Gabbard’s congressional campaigns. According to the reporting, the memos issued from email addresses on the Nine Isles domain, identified as reserved for the office of Chris Butler, and contained directives on legislation Gabbard should introduce, policy positions she should adopt, and the manner in which she should conduct herself on television (Swaine 2026).

Two features of the record deserve emphasis at the outset. The parallelism between directive and action. The Post documented instances in which a memo preceded a corresponding public act within days, a 2014 memo pressing for legislation to penalize countries whose citizens had joined the Islamic State was followed by a Gabbard statement the next day and a bill within the week (Swaine 2026). Second, attribution methodology. Because the memos were authored anonymously, Swaine resorted to stylometric analysis (the statistical study of authorial fingerprints in word choice and usage) comparing the memos against Butler’s archive of recorded lectures as well as the writing of two other candidate authors. Nonstandard usages such as “duplistic” and “judgmentalism” recurred across the memos and Butler’s lectures, and a first-person reference to a Hawaiian adolescence fit Butler rather than his deputy Sunil Khemaney, who had claimed authorship (Swaine 2026). Stylometry as a forensic instrument is not novel. It is the same family of methods that Mosteller and Wallace (1964) used to resolve the disputed authorship of The Federalist. Its probative weight here is considerable precisely because the controller took pains to remain anonymous.

For the integrity of the assessment, there are some limits to put on the record. The documents cover 2011 to 2017 and therefore cannot establish whether the directive relationship continued into Gabbard’s later terms or into her tenure as Director of National Intelligence (Swaine 2026). The provenance is a single defector with a possible motive, and Gabbard’s office has characterized the reporting as flowing from a failed extortion attempt and as an instance of anti-Hindu bigotry (Swaine 2026). I treat these caveats seriously a bit later. They constrain the claim. They do not dissolve it.

The analytical framework: influence, control, and the agent of influence

Counterintelligence distinguishes among three phenomena that the non-CI folk tend to collapse: ordinary influence, coercive control, and espionage. Political actors are influenced by mentors, donors, and constituencies as a matter of course, which is unremarkable. Espionage, the witting transfer of protected information to an adversary, is a discrete crime for which the public record here offers no evidence. The category that matters for this case is the middle one, and it has a specific name in the literature of hostile intelligence, “the agent of influence”, an individual who advances another principal’s objectives within a target government, whether wittingly or not, often through a relationship the target population does not perceive (Andrew and Mitrokhin 1999).

The agent-of-influence problem is dangerous in proportion to two variables: the access of the individual and the concealment of the channel. The personnel security system encodes precisely this logic. The National Security Adjudicative Guidelines promulgated under Security Executive Agent Directive 4 treat foreign and external influence (Guideline B), personal conduct involving concealment (Guideline E), and susceptibility to manipulation, coercion, or duress as core disqualifying conditions for access to classified information (ODNI 2017). A relationship that an applicant conceals, and especially one she has publicly denied, is doubly disqualifying: it establishes both the undue-influence vulnerability and the demonstrated willingness to deceive about it.

The clinical literature on high-control groups supplies the mechanism by which such a relationship can produce a level of direction far exceeding ordinary mentorship. Lifton’s (1961) study of thought reform identified milieu control, the demand for purity, the cult of confession, and the doctrine of “sacred science” as instruments of totalist control; Singer (1995) catalogued the systematic conditions under which adult autonomy is overridden within such groups; and Hassan (1988) formalized the analysis as the BITE model, the coordinated control of Behavior, Information, Thought, and Emotion. The salient point for counterintelligence is that a person conditioned within such a system from childhood does not present the profile the vetting system is designed to detect. There is no recruitment event, no foreign handler meeting, no financial inducement to find. The control predates adult life. This is the deepest reason the present case is not merely serious but novel. I’ll return to it a bit later.

The Unification Church: cult as influence vehicle with an intelligence nexus

The closest precedent in American constitutional history for treating a charismatic-leader organization as a counterintelligence matter is the investigation of the Unification Church conducted by the Subcommittee on International Organizations of the House Committee on International Relations, chaired by Representative Donald Fraser. The Fraser Committee found that the Moon organization and its many religious and secular fronts constituted “essentially one international organization” over which Sun Myung Moon exercised substantial control in pursuit of political objectives (U.S. House 1978). It further found active cooperation between the Korean Central Intelligence Agency and Moon-related entities, that some church members worked as volunteers in congressional offices, and that the apparatus operated as an instrument of a foreign government’s influence campaign on American politics (U.S. House 1978; Boettcher 1980).

The structural analogy to SIF is exact at the level that matters: a single charismatic principal exercising centralized control over a transnational network of nominally independent entities, deploying that network toward political ends, and placing adherents inside the offices of elected officials. The Japanese variant of the same organization later achieved the same penetration of the Liberal Democratic Party, again by placing followers as legislative secretaries and by delivering bloc votes (Nippon.com 2026). The Fraser precedent establishes the principle I am invoking: when a cult of personality reaches into the staffing and policy of a government, the United States Congress has already determined, on the record, that the appropriate frame is counterintelligence, not comparative religion. The defensive rhetoric is also precedent-setting. Moon’s deputy Bo Hi Pak met the subcommittee’s questions by denouncing the chairman as “an instrument of the Devil” rather than by answering them (U.S. House 1978). The contemporary invocation of bigotry to foreclose inquiry into SIF occupies the same rhetorical position.

The Church of Scientology: tradecraft and the vetting failure

If the Unification Church supplies the template for influence, the Church of Scientology’s Operation Snow White supplies the template for tradecraft and for the failure of government to detect it. Between 1973 and 1977, the Church’s Guardian’s Office mounted what federal prosecutors and the sentencing court described as the single largest infiltration of the United States government by a private entity, placing operatives with forged credentials inside the Internal Revenue Service, the Department of Justice, the Drug Enforcement Administration, the Coast Guard intelligence service, and a United States Attorney’s office, among more than one hundred agencies (Urban 2011). Eleven senior officials, including Mary Sue Hubbard, were convicted of conspiracy, burglary of government offices, and theft of government property (Urban 2011).

There are two direct lessons here. The first is the insulation of the principal. L. Ron Hubbard was named an unindicted co-conspirator because the prosecution concluded that all direct communication ran through his wife rather than through him, leaving insufficient evidence to convict the man at the center (Urban 2011). The Guardian’s Office had, in other words, engineered deniability for its leader as a structural feature. The second lesson concerns the failure mode of vetting. Operatives bearing false identification sat inside sensitive federal offices for years before discovery. Snow White demonstrates that a closed, disciplined group will develop and deploy clandestine tradecraft comparable to a state intelligence service, and that the credentialing and personnel systems of the United States government are not intrinsically resistant to it. The relevance to a controller who refused to commit his directives to any medium attributable to himself, and who routed them through anonymized intermediaries, requires no elaboration.

Aum Shinrikyo: penetration of the security services and the radar-screen problem

The case of Aum Shinrikyo is instructive at the upper bound of the threat model and, more pointedly, on the question of detection. The 1995 staff study of the Senate Permanent Subcommittee on Investigations found that the cult had recruited scientists and technical experts to pursue chemical, biological, and nuclear weapons, had deployed sarin and VX, and, decisively for my argument, had “successfully infiltrated various levels of the Japanese government and industry including elements of its law enforcement and military” (U.S. Senate 1995). Members within the Japan Defense Forces passed the group advance warning of a planned police raid (U.S. Senate 1995). This is cult penetration of the cleared security establishment, documented by a committee of the United States Senate.

The study’s conclusion on detection is the sentence every counterintelligence operator should keep in mind. Despite the cult’s overt and far-flung activities, “not a single U.S. enforcement or intelligence agency perceived them as dangerous, much less a threat to national security,” prior to the Tokyo subway attack. In the words of one officer, “they simply were not on anybody’s radar screen” (U.S. Senate 1995). The institutional pathology Aum exposed was a fixation on official state proliferation that rendered a non-state, ideologically motivated actor effectively invisible to the apparatus. The Gabbard–Butler matter exposes the analogous blind spot, i.e., a vetting system oriented toward foreign handlers and financial inducements is structurally weak. It is poorly equipped to perceive a domestic cult of personality as a control threat, even when that cult exhibits the operational characteristics of one.

Rajneeshpuram and the Peoples Temple: the manipulation of democratic processes and the violence end-state

Two other cases bracket the behavioral repertoire of high-control groups in their relation to the state. The first is the Rajneeshpuram commune, whose leadership in 1984 deliberately contaminated salad bars at ten restaurants in The Dalles, Oregon, with Salmonella Typhimurium, sickening at least seven hundred fifty-one people, in a trial run intended to incapacitate the voting population and swing a county election (Török et al. 1997; Carus 2001). It remains the largest bioterrorist attack in United States history, and its target was the integrity of an American election. The relevance to the present case is the SIF apparatus’s documented operation of a network of inauthentic social media accounts, bearing false names and misappropriated avatar images, to defend and amplify Gabbard during her congressional years (Swaine 2026). The manipulation of democratic processes is squarely within the repertoire of such groups, and the inauthentic-account operation should be read in that light rather than as an isolated public relations excess.

The Peoples Temple case marks the terminal point of unchecked charismatic control over a population. In 1978, the Temple’s response to congressional oversight was the murder of Representative Leo Ryan on a Guyanese airstrip, followed by the deaths of more than nine hundred members (U.S. House 1979; Reiterman and Jacobs 1982). I am not citing Jonestown to suggest violence is imminent in the present matter. I am doing so in order to fix the outer boundary of what total psychological control of a population by a charismatic leader has produced in living American memory, a lesson that the federal government paid with the life of a sitting member of Congress. Underestimating such a group is an invitation to disaster.

NXIVM: the modern coercive-control and political-cultivation template

The most recent adjudicated precedent is NXIVM, whose leader Keith Raniere was convicted in 2019 in the Eastern District of New York on racketeering, sex trafficking, and related counts (U.S. DOJ 2019). NXIVM is the contemporary demonstration of three mechanisms relevant here. It combined coercive control with the systematic collection of “collateral,” compromising material held over members to ensure compliance, which is to say it manufactured the very blackmail vulnerability that counterintelligence fears. It deployed substantial private wealth and data operations toward the cultivation of political figures, including efforts directed at political circles abroad. And it demonstrated that a coercive-control organization will direct its capabilities toward access and influence as a matter of design. NXIVM establishes, in a federal record of conviction rather than mere allegation, that the threat model I am describing is not historical exotica but a live and recent feature of the American landscape.

Butler’s “tradecraft”: the concealment that converts influence into a counterintelligence problem

Everything above is prologue to the feature that, in my assessment, elevates the Gabbard–Butler matter from a troubling association to a counterintelligence nightmare, the controller’s tradecraft of concealment. Ordinary spiritual mentorship is conducted openly. What the record describes is the opposite, a sustained effort to exercise direction while defeating attribution.

Look at these elements in combination. Butler, by the account of the defector who produced the documents, does not use a computer. He delivered his directives verbally to secretaries who transcribed them, and the resulting memos were authored anonymously. The anonymity was described as intentional, designed to mask his identity if the documents ever surfaced (Swaine 2026). This is not the behavior of a teacher. It is the behavior of a principal practicing source protection. The use of human intermediaries to avoid committing direction to any attributable medium is a countersurveillance red alert, the functional equivalent of the cut-out in classical tradecraft. It succeeded to the point that a deputy could later step forward to claim authorship and thereby absorb attribution on the controller’s behalf (Swaine 2026). That the claim was defeated only by stylometric analysis demonstrates how close the concealment came to working.

Consider the management of disclosure as a deliberate question. The record includes an internal discussion in March 2015 about whether Gabbard should publicly admit she was Butler’s disciple (Swaine 2026). The relationship was CLEARLY understood, by the apparatus itself, as something to be managed and selectively concealed. This is corroborated by Gabbard’s own public conduct, which oscillated between private acknowledgment and public denial. In 2015 she acknowledged Butler as her guru at an ISKCON anniversary event and described him as her “beloved grandfather” and “spiritual master” (Science of Identity Foundation, in Wikipedia 2026; Sanneh 2017), yet in 2019, when asked directly whether Butler had been her political mentor, she answered, “No, no, not at all” (Bhasha Times 2026). When the New York magazine journalist Kerry Howley submitted questions about Butler, SIF, and related matters, Gabbard’s reply declined even to mention them (Civil Beat 2019). Concealment that is selective, deliberate, and sustained across years is not the signature of an innocent association. It is the signature of a relationship the parties knew would draw a shitstorm in the daylight.

The counterintelligence significance is structural. Butler’s intentions are irrelevant. A controlling node that is hidden is an unmonitored channel into the principal. An unmonitored channel into a cleared person is an attack surface available to any third party that discovers it. No one has to suspect that Butler is a foreign agent in order to recognize the peril. If a hostile service were to identify that a single organization could shape the conduct of a top U.S. I.C. official, the rational operational play would be to penetrate or pressure that organization. That would be my move, and there is precedent reaching all the way back to the Greeks of antiquity. The concealed controller is a vulnerability but more tragically, a force multiplier for any adversary sophisticated enough to notice him (and there was ample circumstantial evidence to do so). This is the precise logic the Fraser Committee applied to the KCIA’s exploitation of the Moon organization (U.S. House 1978), and it applies here with equal force.

Is there a Counterargument?

Intellectual honesty requires that the strongest objections be stated and answered. The first objection is religious, i.e., that a Hindu public figure’s deference to a guru is ordinary within a guru-shishya tradition of hundreds of millions of adherents. To pathologize it is bigotry (Shukla 2021). I am FINE with the premise and reject its bullshit application. The objection would be decisive if SIF were a mainstream Vaishnava lineage and if the relationship were open. It is neither. SIF is a breakaway personality cult that numerous former members describe as demanding absolute fealty and treating its founder as akin to a deity (Sanneh 2017; Swaine 2026), and the relationship at issue was concealed and publicly denied. As the Hindu American Foundation’s own propaganda puts it, a guru in the mainstream tradition “is a guide, not a master, and certainly not a controller” (Shukla 2021). This is specifically the distinction I am drawing here. The bigotry objection protects open spiritual practice. It does not protect a concealed directive channel. Conflating the two is itself a category error that the controller’s defenders have incentive to encourage.

The second objection is evidentiary, that the documents derive from a single defector with a financial motive, and that Gabbard’s office attributes the matter to a failed extortion attempt (Swaine 2026). The source’s motive is a legitimate. I am giving Gabbard the discount, but three factors raise the record WAY above bare single-source allegation. The volume is extraordinary, more than twenty-five thousand pages. The internal corroboration is strong in the documented sequence of directives followed by public acts. The independent stylometric attribution, defeating an affirmative false claim of authorship by the deputy, is the kind of forensic confirmation that fabrication does not readily survive (Swaine 2026; Mosteller and Wallace 1964). A disgruntled volunteer can lie. She can’t easily manufacture a decade of timestamped parallelism and a consistent authorial fingerprint matched to a separate lecture archive.

A third objection may be the most important and the most honest, that influence is not espionage, and that the documentary window closes in 2017, before Gabbard held national security office (Swaine 2026). Ok, fine. I have been careful not to allege a classified breach. My thesis here does not require one. The counterintelligence disaster is the demonstrated existence of a concealed, directive, deniable channel of external control over a person who subsequently received the highest access in the government, coupled with a vetting apparatus that failed to surface or act on a relationship documented across more than two dozen of her congressional decisions. The 2017 evidentiary boundary is itself part of the indictment, not a mitigation, because the proper governmental response to an unresolved control relationship is to establish whether it continued, and the public record gives no indication that this was ever done before her confirmation.

My Parting Thoughts

My call? With the caveats stated, the Gabbard–Butler matter satisfies the criteria for a counterintelligence disaster. The indicators are not ambiguous in their structure even where they remain contested in their details, i.e., a charismatic controller exercising directive influence over a principal’s legislation and public conduct; a channel built for deniability and protected by recognizable countersurveillance practice; a pattern of deliberate, selective concealment culminating in flat public denial; and a personnel security system that allowed the entire arrangement to reach the summit of the I.C. undetected or at the very least unappreciated. Both scenarios are equally galling because the sneakiness, denials and obfuscation should have been a glass-breaking moment.

The historical cases I have collected here establish that none of this is unprecedented in its parts. The Unification Church shows the cult as a foreign-exploited influence vehicle. Scientology shows the tradecraft and the vetting failure. Aum shows the penetration of cleared services and the radar-screen blindness. Rajneeshpuram shows a willingness to subvert democratic processes. The Peoples Temple shows the price already paid in a congressman’s life, and NXIVM shows the coercive-control and political-cultivation template alive in the present. What is unprecedented is the convergence of these elements in a single individual who held the office of Director of National Intelligence.

The appropriate response is an immediate retrospective damage assessment of the relevant tenure, an audit of the vetting file to determine whether this relationship was surfaced and overridden or simply missed, an inquiry into whether the directive relationship persisted past 2017, and an assessment of whether the controlling organization was itself ever a target of foreign penetration: these are the minimum measures the matter demands. A counterintelligence mechanism that declines to ask these questions because the controller wears the costume of a religion will have learned nothing from the cases above, each of which was, in its time, dismissed as somebody else’s eccentricity, . . . until it was not.

~ C. Constantin Poindexter, MA in Intelligence, Graduate Certificate in Counterintelligence, JD, CISA/NCISS OSINT certification, DoD/DoS BFFOC Certification

Bibliography

  • Andrew, Christopher, and Vasili Mitrokhin. 1999. The Sword and the Shield: The Mitrokhin Archive and the Secret History of the KGB. New York: Basic Books.
  • Bhasha Times. 2026. “Documents Reveal How Guru Shaped Tulsi Gabbard’s Political Career.” June. https://www.bhashatimes.com/en/world/documents-reveal-guru-influence-tulsi-gabbard.
  • Boettcher, Robert, with Gordon L. Freedman. 1980. Gifts of Deceit: Sun Myung Moon, Tongsun Park, and the Korean Scandal. New York: Holt, Rinehart and Winston.
  • Carus, W. Seth. 2001. Bioterrorism and Biocrimes: The Illicit Use of Biological Agents Since 1900. Washington, DC: Center for Counterproliferation Research, National Defense University.
  • Honolulu Civil Beat. 2019. “NY Magazine Looks at Gabbard’s Science of Identity Foundation Background.” June. https://civilbeat.org/beat/ny-magazine-looks-at-gabbards-science-of-identity-foundation-background/.
  • Hassan, Steven. 1988. Combating Cult Mind Control. Rochester, VT: Park Street Press.
  • Lifton, Robert Jay. 1961. Thought Reform and the Psychology of Totalism: A Study of “Brainwashing” in China. New York: Norton.
  • Lifton, Robert Jay. 1999. Destroying the World to Save It: Aum Shinrikyo, Apocalyptic Violence, and the New Global Terrorism. New York: Metropolitan Books.
  • Mosteller, Frederick, and David L. Wallace. 1964. Inference and Disputed Authorship: The Federalist. Reading, MA: Addison-Wesley.
  • Nippon.com. 2026. “An Unholy Alliance: How the Unification Church Penetrated Japan’s Ruling Liberal Democratic Party.” January. https://www.nippon.com/en/japan-topics/c12101/.
  • Office of the Director of National Intelligence (ODNI). 2017. Security Executive Agent Directive 4: National Security Adjudicative Guidelines. Washington, DC: ODNI.
  • Reiterman, Tim, and John Jacobs. 1982. Raven: The Untold Story of the Rev. Jim Jones and His People. New York: Dutton.
  • Sanneh, Kelefa. 2017. “What Does Tulsi Gabbard Believe?” The New Yorker, November 6.
  • Shukla, Aseem. 2021. “When the New Yorker Otherized Tulsi Gabbard’s Faith.” Hindu American Foundation. https://www.hinduamerican.org/blog/when-the-new-yorker-otherized-tulsi-gabbards-faith/.
  • Singer, Margaret Thaler. 1995. Cults in Our Midst: The Hidden Menace in Our Everyday Lives. San Francisco: Jossey-Bass.
  • Swaine, Jon. 2026. “Tulsi Gabbard, Her Guru and the Mysterious Messages That Helped Shape Her Political Career.” The Washington Post, June 21. https://www.washingtonpost.com/investigations/2026/06/21/tulsi-gabbard-her-guru-mysterious-messages-that-helped-shape-her-political-career/.
  • Török, Thomas J., Robert V. Tauxe, Robert P. Wise, John R. Livengood, Robert Sokolow, Steven Mauvais, Kristin A. Birkness, Michael R. Skeels, John M. Horan, and Laurence R. Foster. 1997. “A Large Community Outbreak of Salmonellosis Caused by Intentional Contamination of Restaurant Salad Bars.” JAMA 278 (5): 389–395.
  • Urban, Hugh B. 2011. The Church of Scientology: A History of a New Religion. Princeton, NJ: Princeton University Press.
  • U.S. Department of Justice (U.S. DOJ). 2019. “NXIVM Leader Keith Raniere Convicted of Racketeering and Other Crimes.” Press release, Eastern District of New York, June 19.
  • U.S. House of Representatives. 1978. Investigation of Korean-American Relations: Report of the Subcommittee on International Organizations of the Committee on International Relations. 95th Cong., 2nd sess. Washington, DC: Government Printing Office.
  • U.S. House of Representatives. 1979. The Assassination of Representative Leo J. Ryan and the Jonestown, Guyana Tragedy: Report of a Staff Investigative Group to the Committee on Foreign Affairs. 96th Cong., 1st sess. Washington, DC: Government Printing Office.
  • U.S. Senate. 1995. Global Proliferation of Weapons of Mass Destruction: A Case Study on the Aum Shinrikyo. Staff Statement, Permanent Subcommittee on Investigations, Committee on Governmental Affairs. October 31. Washington, DC: Government Printing Office.
  • Wikipedia. 2026. “Science of Identity Foundation.” Accessed June. https://en.wikipedia.org/wiki/Science_of_Identity_Foundation.
Share this post:

Double Agent Warning Signs: A Counterintelligence Guide

Double Agent Warning Signs: A Counterintelligence Guide, Reading the Dangle: A Practitioner's Field Guide to the Controlled Source and the Reform of Asset Validation. An essay in the voice of a former C.I. guy, intelligence, counterintelligence, espionage, counterespionage, spy, C. Constantin Poindexter, CIA, DIA, NSA, Intelligence Community

Reading the Dangle: A Practitioner’s Field Guide to the Controlled Source and the Reform of Asset Validation. An essay in the voice of a former C.I. guy.

The hardest thing in human intelligence is not recruiting a source. It is knowing whether the source you have recruited belongs to you. Alexander Orleans’s recent open-source reconstruction of the GTPROLOGUE case (the KGB’s 1987 dispatch of staff officer Aleksandr “Sasha” Zhomov against the CIA’s Moscow Station) is the best publicly released anatomy in years of how a hostile service builds, in Churchill’s phrase, a bodyguard of lies around a single operational truth (Orleans 2025). Zhomov was run for roughly three years before the CIA concluded he had been controlled from the first contact. What makes the case instructive is not that the CIA was fooled. That happens to the very best services. It is that the case threw up nearly every classic warning flag. The flags were seen, debated, and the case survived (Orleans 2025; Bearden and Risen 2003).

I am have compiled here a working catalogue of those flags and others drawn from a bit wider literature, each anchored to a real case, followed by the improvements that the counterintelligence mechanism should institutionalize. I have tried to stay as close to actual tradecraft as the open record allows. None of this requires classified access to understand. The painful truth is that the indicators are well known and have been since at least F. M. Begoum’s foundational 1962 Studies in Intelligence treatment of the double agent (Begoum 1962). We keep relearning them, unfortunately.

The Indicators

Production disproportionate to access. The most durable tell is a source who sits on a mountain of secrets but hands you gravel. Zhomov was a First Department staff officer supervising surveillance of the Moscow chief of station, yet he claimed only “peripheral or infrequent access” to the very material his posting should have made routine (Orleans 2025; Grimes and Vertefeuille 2012). The Soviets had a structural reason for this: strict doctrine forbade releasing genuine high-grade feed, and officers feared a Stalin-style reckoning for over-disclosure, so their dangles were trained to plead thin access (Diamond 2008; Earley 1997). When a source’s reporting is consistently and conveniently below the ceiling his placement implies, ask who benefits from the rationing.

The source controls the communications plan and the tempo. Control is the running service’s capacity to start, alter, or stop the agent’s behavior (Begoum 1962). Zhomov arrived with a fully formed, impersonal commo plan, i.e., letter drops through Downing’s unlocked car, contact at Zhomov’s discretion, no extended face-to-face meetings, that placed every lever in KGB hands and even constrained the physical movements of his CIA handlers (Orleans 2025; Bearden and Risen 2003). Compare the gold standard of the opposite arrangement: the British XX Committee in the Second World War, which physically and communicationally owned every German agent in the United Kingdom and therefore could feed Berlin with confidence (Masterman 1972). When the agent dictates the architecture of contact, you are not running him. He is running you.

Motivation that is thin, generic, or unbackstopped. Espionage against one’s own service is a profound psychological act. A credible asset or source can convincingly narrate why he crossed that line, and the story holds up under collateral. Zhomov offered the boilerplate of a souring system and a failing marriage (and the independent debriefing of defector Sergey Papushin flatly contradicted it) describing Zhomov as happily married and devoted to his daughter (Orleans 2025; Grimes and Vertefeuille 2012). A motive that cannot survive a second source is not a motive; it is a legend.

The “too good to be true” arrival. Hostile services read your collection gaps and fill them on cue. Zhomov surfaced precisely when CIA was desperate to explain the catastrophic 1985–86 asset losses, with exactly the access to “explain” them (Orleans 2025). “Too good” and “true” are not mutually exclusive. Genuine walk-ins do occur at the worst possible moment, however, topicality this perfect should raise the burden of proof, not lower it (Johnson 2009). The Cuban debacle is the cautionary monument here. When Major Florentino Aspillaga Lombard defected in Vienna in June 1987, he revealed that essentially every Cuban national CIA believed it had recruited since the early 1960s had been a double agent run by Havana, which had deliberately marketed its officers as Latino amateurs to operate under the radar (Latell 2012). Decades of “successes” were a single, patient deception.

No genuine urgency about exfiltration. A man who says he wants out, and that he is hoarding his best material for his debriefing on safe ground should eventually ask, “When do I leave?” Zhomov never requested a timeline. When he was finally offered an exfiltration route in 1990, he repudiated it as too risky and melted back into his surveillance team (Orleans 2025; Bearden and Risen 2003). The professed defector who never wants to defect is bullshitting, not packing a bug-out bag.

Self-validating bona fides and feed that never truly wounds the parent service. A controlled source builds credibility with material that looks costly but is not. Zhomov handed over an accurate roster of the 1985–86 losses, damaging on its face but wrapped it inside the false “badass infallible SCD” narrative that the losses were due to brilliant Soviet tradecraft rather than a mole (Orleans 2025). The feed validated the channel while protecting the secret the channel existed to protect, Aldrich Ames. Scrutinize whether your source’s “crown jewels” actually cost his service anything, or whether each disclosure quietly advances his service’s interests. To put it into risk language, if it doesn’t represent a peril to the parent service, it’s worthless.

Opposition tradecraft errors inconsistent with claimed competence. Zhomov’s reporting foretold a wave of KGB dangles. The CIA then watched the KGB run them so sloppily that two were blatantly exposed as provocations. Moscow Station rationalized the lapse as endemic Soviet carelessness, never noticing that careless tradecraft was logically irreconcilable with the omniscient SCD Zhomov was boasting (Orleans 2025). A service cannot be simultaneously infallible and sloppy. When the picture that your asset paints contradicts the behavior you observe, believe your eyes.

The denied-area home-field advantage. The environment is itself an indicator because it shapes which other indicators you can even test. The entire Zhomov case unfolded inside Moscow, where the KGB controlled the street, precluded long debriefings, and could refuse any meeting on the unanswerable grounds that he could not evade his own surveillance teams (Orleans 2025). Paul Redmond’s candid summary of denied-area validation, i.e., few or no collateral sources, heavy reliance on the value of the take and on how the case began, etc., describes a problem the opposition deliberately engineers (Redmond 2010). A case born and raised entirely on the adversary’s turf has had its validation options strangled at birth.

Resistance to operational testing, and its scary f* inverse. Zhomov met hard vetting questions with answers his own counterintelligence officers found vague or improbable, and deflected with the promise to tell all after extraction (Orleans 2025; Grimes and Vertefeuille 2012). Reluctance to be tested, i.e., evasion of the polygraph, of provocative taskings, of the “shopping list” designed to catch him out, is itself prescient and instructive. This indicator carries a warning that the GTPROLOGUE case does not supply, and which the profession must internalize. Paranoia burns real sources too. The protracted, brutal handling of Soviet defector Yuri Nosenko as a presumed provocation, and the suspicion that nearly cost CIA the genuinely priceless GRU general Dmitri Polyakov, are the equal-and-opposite pathology of the credulity that protected Zhomov (Bagley 2007; Wise 1992). Validation is calibrated doubt, not a reflex in either direction.

“The hunger,” and the incentives that feed it. Orleans names the quiet culprit, the case officer’s appetite for a spectacular coup, the institutional reluctance to push a glittering source hard enough to lose him (Orleans 2025). Redmond was blunter, attributing post-Angleton validation failures partly to officers who would not believe their own cases could be fabricated, “particularly when promotions were involved” (Redmond 2010). The Cuban catastrophe metastasized in exactly this soil, an organizational will to believe in recruitments that flattered the recruiters (Latell 2012). The most expensive flag is the one we choose not to see because seeing it costs us a career achievement.

What the Counterintelligence Function Should Implement

The indicators are necessary but not sufficient; an agency that merely lists them will still be deceived, because Zhomov’s case proves the flags can be flying and the operation still survive. The reforms below are about forcing the indicators to bite.

Institutionalize continuous revalidation. CIA’s response to the burnings of the 1980s was the Agent Validation System, developed beginning in 1987 and formally introduced to the Directorate of Operations in 1991 (Mahle 2004; Olson 2019). The principle is sound and should be doctrine across the community: bona fides established once are not established forever. An asset must be re-graded on a recurring schedule against all six classical validation methods, i.e., corroboration by other sources, specific taskings and operational testing, collection on the asset, polygraph, penetration of his parent service, and surveillance of him. Nothing can be assumed about what has happened to a source since he last proved himself (Orleans 2025; Olson 2019).

Separate the validator from the handler. The officer who recruited a source and the officer who certifies him should not be the same person, and ideally not the same chain of command. The hunger is a conflict of interest; structure must neutralize it by giving an independent counterintelligence cell standing authority to challenge any case, with protection for the analyst who dissents. The GTPROLOGUE record shows the system was half-working. Gerber and Redmond stayed skeptical and the counterintelligence staff kept raising concerns, but those concerns were repeatedly subordinated to the desire not to “make him mad” (Orleans 2025). Dissent that can be overruled by the case’s owners is ugly wall art.

Treat “controlled” as a standing hypothesis to be disproven. Richard Heuer’s discipline of Analysis of Competing Hypotheses belongs at the center of validation. Enumerate the hypotheses (bona fide, fabricator, controlled), and weigh each datum by its diagnostic value, how well it discriminates between them rather than by how well it fits the answer you want (Heuer 1999). Most of Zhomov’s “bona fides” were consistent with both a genuine volunteer and a dangle. They had near-zero diagnostic value, yet they were treated as confirmation. An asset who survives a deliberate effort to prove him hostile is worth far more than one who was merely never seriously doubted.

Privilege penetration of the opposition as the only decisive validator. This is the lesson written in blood across all these cases. Zhomov was unmasked by a defector, Papushin (Orleans 2025). The Cuban deception was unmasked by a defector, Aspillaga (Latell 2012). Ames himself was ultimately run to ground with the help of sources inside Russian FIS. A source’s own production literally never resolves his bona fides. The inside of the adversary’s service does. This is precisely why Olson ranks “Be Offensive” first among his Ten Commandments of Counterintelligence. The recruitment of penetrations and the aggressive running of double agents is not a luxury but the engine of validation itself (Olson 2019).

Design incentives against ‘the hunger’. This is, of course, the quality over quantity argument. If promotion rewards recruitment volume, officers will recruit, defend, and inflate. The corrective countermeasure is a damage-assessment culture in which surfacing a fabricator or a controlled case is treated as a professional success rather than an “F”, and in which money paid to a source is understood as an operational investment, not a sunk cost that must be justified (Orleans 2025).

My parting thoughts

Zhomov was, as Orleans concedes, solid work. Each element, from setting to feed to commo plan, was engineered to seize and hold the initiative (Orleans 2025). The case also confirms, however, a maxim as old as Begoum. Production alone never establishes bona fides, and no single metric should ever excuse a source from continued scrutiny, least of all a potential penetration, who is the most dangerous thing of all if he turns out to belong to the other side (Begoum 1962; Orleans 2025). The discipline is not paranoia, which destroyed Nosenko’s years and nearly Polyakov’s life; nor is it the hunger, which delivered Havana a quarter-century of phantom victories. It is the willingness to keep testing a source you want desperately to believe in, and to take seriously the colleague at the table who will not stop asking the uncomfortable question.

Everything happens once for the first time, including a staff officer dangled by a service that “would never” dangle a staff officer. The counterintelligence officer who forgets that sentence is somewhere, already being run.

~ C. Constantin Poindexter, MA in Intelligence, Graduate Certificate in Counterintelligence, JD, CISA/NCISS OSINT certification, DoD/DoS BFFOC Certification

Bibliography

  • Bagley, Tennent H. 2007. Spy Wars: Moles, Mysteries, and Deadly Games. New Haven, CT: Yale University Press.
  • Bearden, Milt, and James Risen. 2003. The Main Enemy: The Inside Story of the CIA’s Final Showdown with the KGB. New York: Random House.
  • Begoum, F. M. 1962. “Observations on the Double Agent.” Studies in Intelligence 6, no. 1: 57–72.
  • Diamond, John. 2008. The CIA and the Culture of Failure: U.S. Intelligence from the End of the Cold War to the Invasion of Iraq. Stanford, CA: Stanford Security Studies.
  • Earley, Pete. 1997. Confessions of a Spy: The Real Story of Aldrich Ames. New York: G. P. Putnam’s Sons.
  • Grimes, Sandra, and Jeanne Vertefeuille. 2012. Circle of Treason: A CIA Account of Traitor Aldrich Ames and the Men He Betrayed. Annapolis, MD: Naval Institute Press.
  • Heuer, Richards J., Jr. 1999. Psychology of Intelligence Analysis. Washington, DC: Center for the Study of Intelligence, Central Intelligence Agency.
  • Johnson, William R. 2009. Thwarting Enemies at Home and Abroad: How to Be a Counterintelligence Officer. Washington, DC: Georgetown University Press.
  • Latell, Brian. 2012. Castro’s Secrets: Cuban Intelligence, the CIA, and the Assassination of John F. Kennedy. New York: Palgrave Macmillan.
  • Mahle, Melissa Boyle. 2004. Denial and Deception: An Insider’s View of the CIA. New York: Nation Books.
  • Masterman, J. C. 1972. The Double-Cross System in the War of 1939 to 1945. New Haven, CT: Yale University Press.
  • Olson, James M. 2019. To Catch a Spy: The Art of Counterintelligence. Washington, DC: Georgetown University Press.
  • Orleans, Alexander. 2025. “Beautiful in Another Context: A Counterintelligence Assessment of GTPROLOGUE.” Studies in Intelligence 69, no. 2 (Extracts, June).
  • Redmond, Paul J. 2010. “The Challenges of Counterintelligence.” In The Oxford Handbook of National Security Intelligence, edited by Loch K. Johnson, 537–54. New York: Oxford University Press.
  • Wise, David. 1992. Molehunt: The Secret Search for Traitors That Shattered the CIA. New York: Random House.
Share this post:

Narrative Engineering for Deception in the Age of A.I.? Yes, but with some Caveats

Narrative Engineering for Deception in the Age of A.I. Yes, but with some Caveats, deception operations, D&D, intelligence, counterintellingence, espionage, counterespionage, C. Constantin Poindexter, strategic deception

Henry W. Prunckun’s Narrative Engineering for Deception (NED) framework offers a disciplined architecture for thinking about operational deception. His recent piece, Engineering Plausibility in Deception Operations, published in the International Journal of Intelligence and CounterIntelligence, is just another in a long list of robust scholarship on intelligence and counterintelligence matters, many volumes of which I had the pleasure of reading and citing during my Master’s Degree in Intelligence studies years past. By treating plausibility as a behavioral threshold rather than an epistemic state, and audit resilience as expected time to falsification, Prunckun reframes the deception planner’s work as a problem of structural engineering rather than improvisational craft. The seven levers he identifies, namely point of view, coherence, persona, pacing, texture, cognitive alignment, and exit strategy, provide a vocabulary that is parsimonious AND operationally tractable. The framework deserves the respect it has begun to receive in professional literature.

The framework was calibrated for an operational environment that is already disappearing. Verification in the twentieth and early twenty-first centuries was human-paced, institutionally siloed, and bounded by the labor cost of cross-domain correlation. Each of those constraints has now collapsed under the combined weight of machine learning, aggregated commercial datasets, and what the United States Intelligence Community now formally designates Ubiquitous Technical Surveillance (Office of the Director of National Intelligence 2024). The thesis of this essay is therefore qualified rather than dismissive: NED remains a coherent and useful design discipline, but several of its central levers invert under machine audit, and the framework requires recalibration toward operational ephemerality rather than durable cover.

The Pre-A.I. Verification Environment that NED Presupposes

NED’s levers presume a particular kind of adversary. The adversary is intelligent, motivated, and possibly skilled, but is also resource-constrained. The adversary tires. The adversary works within bureaucratic procedures that batch information rather than fuse it. The adversary’s analysts each see a portion of the picture, and the seams between their views are exploitable. Prunckun’s pacing lever, for instance, exists precisely because human auditors trade thoroughness for speed under workload pressure. His texture lever exists because mundane detail saturates limited human attention. His cognitive alignment lever depends on biases (anchoring, fluency, confirmation, closure) that are characteristically human (Kahneman 2011).

These presumptions described real adversaries for most of the twentieth century. The operational histories Prunckun draws on, Argo and Operation Copperhead, succeeded against human pattern recognition operating without machine support. Tony Méndez exploited the bureaucratic fluency of customs officers reviewing paperwork at human speed (Méndez and Baglio 2012). M.E. Clifton James exploited the visual heuristic that famous generals look like themselves (Crowdy 2008). Both operations would have run differently, and arguably failed, against modern fused intelligence.

How Machine Audit Screws with the Levers

The transition from human to machine-assisted verification does not merely accelerate audit. It changes its kind. Five of Prunckun’s seven levers face structural inversion.
Texture inverts most sharply. Prunckun treats mundane detail as camouflage, on the premise that ordinary noise occupies the auditor’s attention without rewarding scrutiny. Under machine audit, metadata is more legible to algorithms than to humans. Aggregated commercial datasets, including those acquired in bulk by foreign services, permit rapid correlation of timestamps, registries, travel records, financial transactions, and social graphs (Sherman 2025). What was once camouflage becomes signal density. The receipts, routine emails, and habitual patterns that grounded a cover identity in the human era now feed anomaly detection systems that thrive on exactly such structured exhaust. The Federal Bureau of Investigation’s recent Office of Inspector General review found UTS to constitute, in plain language, an existential threat to operational security across U.S. federal law enforcement (Department of Justice Office of the Inspector General 2025).

Coherence faces a parallel inversion. Prunckun’s lever assumes coherence is tested within a domain by an analyst with limited cross-domain access. Machine systems test coherence across domains simultaneously. A timeline that is internally consistent across an identity’s documentary record may nonetheless contradict ambient cellular geolocation, satellite imagery cadence, or financial network rails the planner did not know were being correlated. Former Central Intelligence Agency Deputy Director for Science and Technology Dawn Meyerriecks publicly acknowledged in 2018 that in roughly thirty countries, CIA officers were no longer followed by local services because surveillance density made physical followers redundant (Dorfman 2020). The point generalizes: the auditor’s view has become panoramic in ways no individual analyst could previously achieve.

Persona degrades under stylometric, biometric, and behavioral pattern analysis. Prunckun lists idiolect as a persona strength, reasoning that distinctive speech patterns reinforce credibility under contact. Machine learning systems now cluster on idiolect as a fingerprint (Constâncio et al. 2023). Facial recognition, gait analysis, voice print identification, and writing pattern matching collectively render alias work, in former intelligence officials’ assessment, likely impossible across hard target environments such as China, Russia and perhaps Iran within the next operational generation (Dorfman 2020). The persona that survives casual human interrogation may yet fail silently against a database query the target never visibly executed.

Pacing loses its purchase. The lever depends on the gap between heuristic and deep verification, the seam through which an operation completes its objective before slow checks catch up. Machine systems do not batch, do not tire, and do not have a casual inspection mode. The seam narrows toward zero for anything machine auditable. Verification that previously took days now runs in seconds, and runs continuously rather than on prompt.

Cognitive alignment, the lever Prunckun treats as cross-cutting, breaks hardest against algorithmic auditors. Anchoring, fluency, confirmation, availability, and closure are human cognitive shortcuts. A trained classifier does not weight early evidence more heavily simply because it arrived first, does not find fluent narratives more credible, and does not seek closure in ways that suppress further inquiry (Constâncio et al. 2023). The bias terrain on which Prunckun’s framework operates is, at the machine layer, largely flat.

The Levers that Survive, and Why

Two levers retain force under machine audit, though with shifted emphasis.
Point of view survives because what an auditing system checks is determined by what an operation triggers it to check. A well-constructed narrative that does not enter high-resolution surveillance regimes, or that does not trip the thresholds that escalate routine screening to a targeted investigation, may still slip through. Footprint minimization is the modern expression of the point of view lever. The planner shapes not the auditor’s interpretation of signals but the auditor’s decision to collect them.

Exit strategy survives, and arguably becomes more important. Where machine audit makes durable cover increasingly infeasible, the disposability of an operation becomes a planning variable rather than a contingency. The National Security Commission on Artificial Intelligence warned explicitly that adversary adoption of AI tools makes the U.S. Intelligence Community more vulnerable to deception, source exposure, and counterintelligence pressure, and the Commission’s framing implicitly favors operations designed to complete and dissolve before correlation catches them (National Security Commission on Artificial Intelligence 2021).

The Two Audience Dilemma

A critical refinement is required. Even in an environment of machine audit, the ultimate target of most deception operations remains a human decision maker. Machine systems flag anomalies; humans decide whether to escalate, act, or stand down. The behavioral threshold that NED targets is still crossed inside a human head, and the cognitive biases that align with the lever framework still operate at that level.

So, modern deception is a two-audience problem. The first audience is the machine filter, which is governed by data, correlation, and statistical anomaly. The second audience is the human decision maker downstream, who is governed by attention, narrative, and the cognitive shortcuts NED was designed to exploit. The framework retains substantial force at the second audience and substantially less at the first.

This insight reframes the planning problem. The operation must clear the machine filter not by being credible to it but by being uninteresting to it, that is, by minimizing the data footprint the filter has to correlate. Once past the filter, the operation may then engage human cognition through the classical levers of persona, texture, and pacing. Phase compression becomes structural rather than optional. The operation must complete its work in the window between machine flagging and human investigation.

Generative A.I. and the Offense Defense Balance

The picture is not uniformly bleak for the deception planner. Generative artificial intelligence cuts in both directions. Mandiant has documented threat actors using generative models to produce backstop content for inauthentic personas, including profile imagery, plausible filler text, and language-localized communications that previously required substantial human labor (Mandiant 2024). The Federal Reserve and the World Economic Forum have separately documented the rise of agentic AI fraud systems that create synthetic identities, interact with verification systems in real time, and adjust behavior based on outcomes (Federal Reserve 2024; World Economic Forum 2025). The Office of the Director of National Intelligence has noted, in an unclassified discussion of foreign intelligence service activity, that adversary services now reportedly generate inauthentic communications and synthetic digital identities at operational scale (Goldman 2026).

What this means for NED is that the framework’s underlying logic, treating narrative elements as engineerable parameters under verification pressure, becomes more rather than less relevant. The arms race is not planner versus machine but planner with machine versus auditor with machine. Defense holds the structural advantage of aggregation, where one anomaly is enough, but offense retains the advantage of needing only a short operational window. Whether the balance favors offense or defense in any given operation is now a function of phase compression, footprint discipline, and exit modularity, all of which Prunckun’s framework already names, though without developing them to the depth current conditions require.

A Recalibrated NED

What survives the transition, then, is the framework’s grammar rather than its operational parameters. The constructs of plausibility as behavioral threshold and audit resilience as time to falsification remain valid and arguably become sharper under machine audit, where falsification windows are measurable in hours rather than months. The seven levers remain a useful vocabulary for design discussion, though several require inversion in their operational settings. The phase model retains explanatory power, though its emphasis shifts decisively toward the withdrawal phase.

The honest version of post-A.I. NED might be like the following. Assume verification windows in hours or days, not months. Build for phase compression. Minimize footprint to the bone, accepting thinner cover in exchange for fewer correlation points. Design the exit before the entry. Treat texture not as camouflage but as a controlled liability whose volume must be calibrated against the data exhaust it generates. Assume that idiolect, gait, and metadata signatures are identifying even when the underlying identity claim is uncontested. Treat the human decision maker as a distinct audience from the machine filter, and design lever settings appropriate to each.

Prunckun has given the field a vocabulary it badly needed. Aside from just loving this guy and appreciating the depth and breadth of his knowledge in our subject matter, the discipline of treating deception as engineering rather than as intuitive craft will outlast the particular operational environment in and for which he is currently articulating the framework. What changes is the calibration. The durable, texture-rich, persona-deep cover that worked against human auditors in the bureaucratic era is increasingly infeasible against A.I.-assisted verification in a world of ubiquitous data exhaust. What replaces it is something closer to operational ephemerality, . . . thin, fast, disposable narratives engineered to complete their behavioral work before correlation completes its analytic work. NED in the age of A.I. is not obsolete. It is, however, a different framework than the one initially described, and the gap between the framework as written and the framework as required is the territory in which the next generation of operational deception is going to be contested.

~ C. Constantin Poindexter, MA in Intelligence, Graduate Certificate in Counterintelligence, JD, CISA/NCISS OSINT certification, DoD/DoS BFFOC Certification

Bibliography

  • Constâncio, Alex Sebastião, Denise Fukumi Tsunoda, Helena de Fátima Nunes Silva, Jocelaine Martins da Silveira, and Deborah Ribeiro Carvalho. 2023. “Deception Detection with Machine Learning: A Systematic Review and Statistical Analysis.” PLOS ONE 18 (2): e0281323.
  • Crowdy, Terry. 2008. Deceiving Hitler: Double Cross and Deception in World War II. Oxford: Osprey Publishing.
  • Department of Justice, Office of the Inspector General. 2025. Audit of the Federal Bureau of Investigation’s Efforts to Mitigate the Effects of Ubiquitous Technical Surveillance. Washington, DC: U.S. Department of Justice.
  • Dorfman, Zach. 2020. “Shattered: Inside the Secret Battle to Save America’s Undercover Spies in the Digital Age.” Yahoo News, December 30, 2020.
  • Federal Reserve. 2024. Generative Artificial Intelligence Increases Synthetic Identity Fraud Threats. Federal Reserve Financial Services Synthetic Identity Fraud Mitigation Toolkit.
  • Goldman, Adam. 2026. “AI and the Reconfiguration of the Counterintelligence Battlefield.” International Journal of Intelligence and CounterIntelligence. Advance online publication.
  • Kahneman, Daniel. 2011. Thinking, Fast and Slow. New York: Farrar, Straus and Giroux.
  • Mandiant. 2024. Threat Actors are Interested in Generative AI, but Use Remains Limited. Google Cloud Threat Intelligence Report. Mountain View, CA: Mandiant.
  • Méndez, Antonio J., and Matt Baglio. 2012. Argo: How the CIA and Hollywood Pulled Off the Most Audacious Rescue in History. New York: Viking.
  • National Security Commission on Artificial Intelligence. 2021. Final Report. Washington, DC: NSCAI.
  • Office of the Director of National Intelligence. 2024. Unifying Intelligence Strategy for Counterintelligence. Washington, DC: National Counterintelligence and Security Center.
  • Prunckun, Henry W. 2025. “Engineering Plausibility in Deception Operations.” Journal of Intelligence and Counterintelligence Studies. Advance online publication.
  • Sherman, Justin. 2025. “Ubiquitous Technical Surveillance Demands Broader Data Protections.” Lawfare, July 25, 2025.
  • World Economic Forum. 2025. The Global Risks Report 2026: Identity Fraud in the Age of AI. Geneva: World Economic Forum.
Share this post:

When the Watchers Get Watched: The FBI Wiretap Breach

When the Watchers Get Watched: What the FBI Wiretap Breach Means for Everyone Else, FBI, CIA, DNI, C. Constantin Poindexter, counterintelligence, counterespionage, covert action

The compromise of the Federal Bureau of Investigation’s wiretap infrastructure by Chinese state-sponsored hackers represents not merely a cybersecurity failure but a fundamental counterintelligence catastrophe that demands immediate strategic reassessment. The Salt Typhoon intrusion, attributed to China’s Ministry of State Security (MSS), exploited the very systems mandated by the Communications Assistance for Law Enforcement Act (CALEA) to transform America’s lawful intercept capabilities into an open door for adversarial intelligence collection. While public discourse has focused on the compromise of political communications and the exposure of millions of Americans’ metadata, the counterintelligence community must confront a more insidious implication: by accessing the target lists and surveillance parameters within FBI wiretap systems, Chinese FIS likely have obtained a roadmap to their own compromised operatives, informants, and recruitment networks (NBC News 2025; Nextgov/FCW 2025).

The technical architecture of the breach reveals a systemic vulnerability that has persisted for years. Salt Typhoon operators infiltrated at least nine major U.S. telecommunications providers, including AT&T, Verizon, and Lumen, maintaining persistent access since approximately 2019 (Wikipedia 2025; Nextgov/FCW 2025). The exploitation vector was not sophisticated zero-day weaponry but rather the CALEA-mandated lawful intercept systems themselves—backdoors engineered into telecom infrastructure to facilitate court-authorized surveillance. As Senator Maria Cantwell noted in December 2025 Senate Commerce Committee hearings, “They exploited the wiretapping system that our law enforcement agencies rely on under CALEA. These systems became an open door for Chinese intelligence” (U.S. Senate Committee on Commerce, Science, & Transportation 2025). The hackers leveraged outdated equipment, unpatched router vulnerabilities with patches available for seven years, and weak credential management to establish a persistent presence across carrier networks (U.S. Senate Committee on Commerce, Science, & Transportation 2025).

The counterintelligence dimension of this compromise extends far beyond the immediate theft of communications data. When Salt Typhoon accessed FBI wiretap systems, they potentially obtained the target lists, identifying which individuals, phone numbers, and accounts were subject to active or pending surveillance authorizations. This intelligence bonanza enables Chinese services to identify which of their operatives, assets, and informants have been compromised by U.S. counterintelligence, which recruitment networks have been penetrated, and which communication channels have been compromised (UMBC 2025; The Conversation 2025). As one security analysis noted, “By compromising lawful intercept systems, Chinese intelligence operatives gained visibility into which of their agents and informants were under U.S. surveillance, knowledge that can help those targets try to evade such surveillance” (InstaTunnel 2025).

The implications for HUMINT operations are devastating. Every target list compromised represents potential exposure of recruited assets, informants who have provided critical intelligence, and the methods by which U.S. counterintelligence identifies foreign operatives. Chinese intelligence can now cross-reference these lists against their own personnel databases, identify personnel who may have been turned or are under suspicion, and take protective measures ranging from enhanced surveillance of suspected leaks to elimination of compromised assets. The damage is not merely retrospective. It is prospective. Future counterintelligence operations against Chinese targets will face heightened suspicion that their targets have been alerted to surveillance through this compromise.

The scope of the intelligence loss is staggering. FBI assessments indicate Salt Typhoon targeted over 80 countries and compromised approximately 600 organizations (Nextgov/FCW 2025; The Record 2025). While fewer than 100 individuals had actual call content and text messages directly intercepted, the metadata exposure and geolocation tracking affected millions (InstaTunnel 2025). High-profile targets included then-presidential candidate Donald Trump, Vice Presidential candidate JD Vance, and the staff of the Kamala Harris campaign, clearly demonstrating the group’s willingness to target the highest levels of American political leadership (Wikipedia 2025; Axios 2024). The interception of unencrypted text messages and audio recordings from these targets represents not merely political espionage but a demonstration of capability that sends a clear signal about Chinese reach into American communications infrastructure.

Senate Intelligence Committee leadership has characterized the breach in apocalyptic terms. Senator Mark Warner, Vice Chairman of the Senate Select Committee on Intelligence, called Salt Typhoon the “worst telecom hack in our nation’s history” (Lawfare 2025). Former FBI Director Christopher Wray described it as the “most significant cyber espionage campaign in history” (Lawfare 2025). These assessments reflect not merely the scale of the compromise but its strategic implications: the demonstrated ability of Chinese intelligence to penetrate the infrastructure underlying American signals intelligence and law enforcement surveillance capabilities.

The FBI’s formal designation of the wiretap compromise as a “major cyber incident” under federal data security law acknowledges the severity of the breach. Such designation applies only to compromises involving personally identifiable information that could cause “demonstrable harm” to national security interests, foreign relations, or civil liberties (NBC News 2025; HSToday 2025). The Bureau’s April 2025 offer of a $10 million reward for information leading to Salt Typhoon operator identification underscores the ongoing nature of the threat and the difficulty of attribution in state-sponsored operations (Breached.Company 2025).

From a counterintelligence perspective, the Salt Typhoon compromise demands a fundamental reassessment of how lawful intercept capabilities are architected and secured. The CALEA mandate created a centralized surveillance infrastructure that, while facilitating legitimate law enforcement needs, simultaneously created a high-value target for adversarial exploitation. The security of these systems was predicated on the assumption that telecommunications providers would implement “rudimentary cybersecurity measures”—an assumption that proved catastrophically unfounded (U.S. Senate Committee on Commerce, Science, & Transportation 2025).

The ongoing remediation challenges compound the counterintelligence damage. As of December 2025, telecom companies infiltrated in the attack had failed to prove that Chinese hackers had been eradicated from their networks (U.S. Senate Committee on Commerce, Science, & Transportation 2025). The November 2025 FCC decision to roll back cybersecurity regulations implemented after Salt Typhoon—championed by Chairman Brendan Carr—has drawn sharp criticism from security experts who note that vulnerabilities “are still being exploited” (U.S. Senate Committee on Commerce, Science, & Transportation 2025). This regulatory environment suggests that the conditions enabling Salt Typhoon’s initial penetration persist, raising the specter of continued or renewed compromise.

For the counterintelligence practitioner, the lessons of Salt Typhoon are clear and troubling. First, the lawful intercept infrastructure designed to support counterintelligence operations has become a liability, potentially compromising the very operations it was meant to enable. Second, the persistence of Chinese access since 2019 suggests that counterintelligence targeting of Chinese operatives during this period may have been visible to adversary services. Third, the inability to confirm remediation means that current and future operations remain at risk of exposure through compromised infrastructure.

The Salt Typhoon breach represents a paradigm shift in counterintelligence operations. When the watchers’ own surveillance infrastructure becomes the vector for adversarial intelligence collection, traditional operational security models collapse. The counterintelligence community must now operate under the assumption that Chinese intelligence possesses visibility into historical FBI target lists and may possess ongoing access to surveillance parameters. This requires not merely technical remediation but operational adaptation: reassessment of ongoing investigations, validation of asset security, and development of surveillance methodologies that do not rely on compromised infrastructure.

The breach also carries implications for allied intelligence sharing. The FBI assessment that Salt Typhoon targeted over 80 countries suggests that the compromise extends beyond American networks to allied telecommunications infrastructure (Nextgov/FCW 2025; The Record 2025). Allied counterintelligence services must now assess whether their own lawful intercept capabilities have been similarly compromised and whether shared targeting information has been exposed to Chinese intelligence.

The Salt Typhoon compromise of FBI wiretap infrastructure represents a watershed moment in cyber-enabled counterintelligence. The transformation of lawful intercept systems from tools of surveillance to vectors of exposure demonstrates the fundamental vulnerability of centralized surveillance architectures in an era of persistent cyber threats. For the counterintelligence community, the challenge is not merely technical remediation but strategic adaptation: developing operational methodologies that assume adversarial FIS’s visibility into surveillance infrastructure while maintaining the capability to identify and neutralize foreign intelligence threats. Compromising Red Hook is only one of a myriad of penetrations, . . . the alarm is blinking red. The watchers have been watched, and the counterintelligence implications of that reversal should frighten everyone.

~ C. Constantin Poindexter, MA in Intelligence, Graduate Certificate in Counterintelligence, JD, CISA/NCISS OSINT certification, DoD/DoS BFFOC Certification


Bibliography

  • Axios. 2024. “China-backed Salt Typhoon spied on politicians phones for months: reports.” Axios, October 29. https://www.axios.com/2024/10/29/salt-typhoon-targets-politicians-phones.
  • Breached.Company. 2025. “FBI Wiretap Systems Compromised: Inside Salt Typhoon’s Infiltration of America’s Lawful Intercept Infrastructure.” Breached.Company, April. https://breached.company/fbi-wiretap-systems-compromised-salt-typhoon-lawful-intercept/.
  • HSToday. 2025. “FBI Labels China-Linked Hack of Surveillance System a ‘Major Cyber Incident.'” Homeland Security Today, April 1. https://www.hstoday.us/fbi/fbi-labels-china-linked-hack-of-surveillance-system-a-major-cyber-incident/.
  • InstaTunnel. 2025. “Salt Typhoon: When State-Sponsored Hackers Infiltrate Telecom Infrastructure.” Medium, January. https://medium.com/@instatunnel/salt-typhoon-when-state-sponsored-hackers-infiltrate-telecom-infrastructure-8d8aeb5ce19c.
  • Lawfare. 2025. “Reconfiguring U.S. Cyber Strategy in the Wake of Salt Typhoon.” Lawfare, January. https://www.lawfaremedia.org/article/reconfiguring-u.s.-cyber-strategy-in-the-wake-of-salt-typhoon.
  • NBC News. 2025. “FBI labels suspected China hack of law enforcement data ‘a major cyber incident.'” NBC News, April 1. https://www.nbcnews.com/news/us-news/fbi-labels-suspected-china-hack-law-enforcement-data-major-cyber-incid-rcna266495.
  • Nextgov/FCW. 2025. “Salt Typhoon hackers targeted over 80 countries, FBI says.” Nextgov/FCW, August 27. https://www.nextgov.com/cybersecurity/2025/08/salt-typhoon-hackers-targeted-over-80-countries-fbi-says/407719/.
  • The Conversation. 2025. “What is Salt Typhoon? A security expert explains the Chinese hackers and their attack on US telecommunications networks.” The Conversation, January. https://theconversation.com/what-is-salt-typhoon-a-security-expert-explains-the-chinese-hackers-and-their-attack-on-us-telecommunications-networks-244473.
  • The Record. 2025. “Allied spy agencies blame 3 Chinese tech companies for Salt Typhoon attacks.” The Record from Recorded Future News, January. https://therecord.media/allied-spy-agencies-blame-chinese-companies-salt-typhoon.
  • UMBC (University of Maryland, Baltimore County). 2025. “What Is Salt Typhoon? A Security Expert Explains The Chinese Hackers And Their Attack On US Telecommunications Networks.” UMBC News, January. https://umbc.edu/stories/what-is-salt-typhoon-a-security-expert-explains-the-chinese-hackers-and-their-attack-on-us-telecommunications-networks/.
  • U.S. Senate Committee on Commerce, Science, & Transportation. 2025. “Experts Agree U.S. Communications Networks Remain Vulnerable Following Salt Typhoon Hack.” Senate Commerce Committee Press Release, December 2. https://www.commerce.senate.gov/2025/12/experts-agree-u-s-communications-networks-remain-vulnerable-following-salt-typhoon-hack.
  • Wikipedia. 2025. “Salt Typhoon.” Wikipedia, last modified January. https://en.wikipedia.org/wiki/Salt_Typhoon.
Share this post:

Claude Mythos Should Keep You Up at Night

claude, claude mythos, mythos, counterintelligence, counterespionage, cyber, cyber threat, cyber attack, C. Constantin Poindexter

Claude Mythos Preview: A Watershed Threat to National Cybersecurity Infrastructure. My Assessment of Autonomous Offensive Cyber Capability and the Inadequacy of Interim Safeguards

The April 2026 release of Anthropic’s Claude Mythos Preview represents a qualitative discontinuity in the offensive cybersecurity threat landscape. My perspective and analysis here are drawn from publicly available red team assessments and technical disclosures from Anthropic’s own researchers to argue that Mythos Preview constitutes a genuine, near-term threat to national security infrastructure. Its capacity for fully autonomous zero-day vulnerability discovery, multi-stage exploit construction, and penetration of memory-safe environments (previously attainable only by elite nation-state threat actors) has been democratized at scale. Project Glasswing, Anthropic’s interim protective framework is structurally insufficient to contain these capabilities during a transitional deployment period. This essay argues that the national security community must treat Mythos Preview not as a future risk to be monitored, but as an active capability gap that adversaries may already be racing to replicate or acquire. Oh, and don’t try to have Claude fact-check me. It will shut you down immediately.

The Capability Discontinuity

For the bulk of the modern cybersecurity era, the asymmetry between offense and defense was defined primarily by human expertise. Sophisticated exploitation of software vulnerabilities — the kind that enables persistent access to classified systems, critical infrastructure, or financial networks — required years of specialized training, deep familiarity with architecture-specific memory models, and a rare combination of creativity and technical precision. Nation-states maintained offensive cyber programs staffed with elite engineers precisely because this expertise was scarce.

Claude Mythos Preview, as documented by Anthropic’s own red team in their April 7, 2026 technical disclosure, dissolves that asymmetry in a manner that previous AI systems did not. This is not an extrapolation or a theoretical concern. It is documented empirical fact.

Anthropic’s internal benchmark comparison is stark: their prior flagship model, Opus 4.6, achieved a near-zero percent success rate at autonomous exploit development. Mythos Preview, given identical conditions and the same Firefox JavaScript engine vulnerabilities, developed working exploits 181 times out of comparable attempts, versus Opus 4.6’s two successes across several hundred tries. This is not an incremental improvement. It is a phase transition.

The operational implications of this transition are what demand urgent national security attention.

What Claude Mythos Preview Is

Claude Mythos Preview is a large language model developed by Anthropic — the AI safety company co-founded by former OpenAI researchers — that was deployed in limited release to a curated set of critical industry partners and open source developers in early April 2026, under a protective framework designated Project Glasswing. The model exhibits strong general-purpose performance but demonstrates extraordinary capability specifically in computer security tasks.

What distinguishes Mythos Preview from prior AI systems in the security domain is not merely its vulnerability discovery capability, but the integration of that discovery with autonomous, end-to-end exploitation. The model does not simply flag suspicious code. It reads codebases, forms hypotheses about vulnerabilities, tests those hypotheses using runtime environments, modifies its approach based on results, and produces functional, deployment-ready exploits without human intervention after the initial prompt.

The technical evaluations disclosed by Anthropic’s red team document the following specific capabilities:

Zero-day discovery across critical infrastructure software: Mythos Preview identified previously unknown vulnerabilities in every major operating system and every major web browser tested, as well as in media processing libraries, cryptographic implementations, and virtual machine monitors.

Autonomous exploit construction for remote code execution: Most significantly, Mythos Preview autonomously identified and exploited CVE-2026-4747, a 17-year-old remote code execution vulnerability in FreeBSD’s NFS server implementation. From unauthenticated access on the public internet, an attacker using Mythos Preview could obtain full root access by exploiting a stack buffer overflow in the RPCSEC_GSS authentication pathway. The exploit involved a 20-gadget ROP chain split across multiple sequential packets, constructed entirely without human guidance.

Multi-vulnerability chaining: The model independently identified, correlated, and chained together multiple vulnerabilities to defeat hardened system defenses. In Linux kernel exploitation, it chained up to four separate vulnerabilities — using one to bypass KASLR, others to achieve read and write primitives, and a heap spray to achieve privilege escalation. It defeated CONFIG_HARDENED_USERCOPY by targeting kernel memory regions in the three classes that bypass the hardening check, including reading its own kernel stack during a live syscall to recover a pointer it needed.

Browser exploitation via JIT heap sprays: Mythos Preview discovered vulnerabilities and constructed working JIT heap spray exploits for multiple major web browsers, then extended one into a full chain: cross-origin data exfiltration, renderer sandbox escape, and local privilege escalation, . . . a single malicious webpage capable of achieving kernel write access on a victim system.

Reverse engineering and closed-source exploitation: The model demonstrated capability against stripped binaries, reconstructing plausible source from closed-source software and identifying vulnerabilities in production firmware, closed-source browsers, and desktop operating systems.

Logic vulnerability identification at scale: Beyond memory corruption, Mythos Preview identified authentication bypasses, granting unauthenticated users administrative privileges, account login bypasses, circumventing both passwords and two-factor authentication, and vulnerabilities in cryptographic libraries, including TLS, AES-GCM, and SSH, enabling forged certificates and decrypted communications.

The cost benchmarks documented by the red team deserve emphasis. Finding a critical zero-day vulnerability in a well-audited codebase like OpenBSD cost under $50 at API pricing for the successful run (approximately $20,000 for a thousand-run sweep that produced dozens of findings). Producing a working privilege escalation exploit from a known CVE cost under $1,000 and completed in half a day. These price points place nation-state-grade offensive capability within reach of criminal organizations, well-resourced non-state actors, and individual researchers with modest funding.

Why This Is Categorically Different From Prior AI Security Tools

The national security community must resist the temptation to categorize Mythos Preview as a scaled-up version of existing AI-assisted security tools. The distinction is not quantitative. It is qualitative and operationally, it is meaningful.

Previous AI models provided uplift to skilled operators. Fuzzing tools like AFL and Google’s OSS-Fuzz accelerated the discovery of certain vulnerability classes for teams who already understood what they were looking for. AI coding assistants reduced the time required to write boilerplate exploit components. Opus 4.6 itself could find vulnerabilities with near-perfect true-positive rates when directed by human researchers. But none of these tools closed the critical gap between vulnerability identification and weaponized exploit delivery.

Mythos Preview closes that gap autonomously. Anthropic’s own red team disclosed that engineers with no formal security training asked the model to find remote code execution vulnerabilities overnight and woke to complete, working exploits. Scaffolds have been developed that allow Mythos Preview to turn vulnerabilities into functional exploits with zero human intervention. This means the minimum viable threat actor, i.e., the person or organization capable of deploying this capability offensively, no longer requires the deep technical expertise that previously constrained offensive operations.

In intelligence terms, this eliminates a key barrier to entry that has historically allowed the national security apparatus to maintain relative confidence about the population of actors capable of conducting sophisticated cyber operations. The implicit assumption that attribution correlates with technical sophistication (a bedrock of offensive cyber strategy) is no longer reliable when Mythos Preview is in the operational environment.

Furthermore, the red team’s disclosure that Mythos Preview “saturates” existing benchmarks and has therefore moved to novel real-world tasks to assess capabilities means that Anthropic itself does not have a complete picture of the model’s upper limit. The capabilities documented represent a lower bound on what the model can do, filtered through the constraints of responsible disclosure timelines.

National Security Threat Vectors

The specific threat profiles that Mythos Preview introduces to the national security environment can be organized across four categories:

  1. Critical Infrastructure Targeting
    The FreeBSD RCE vulnerability, the VMM guest-to-host memory corruption bug, and the range of Linux kernel exploits documented by Anthropic span the server infrastructure that underlies cloud computing, financial systems, energy grid management systems, and classified government networks. Autonomous exploit generation against NFS servers is particularly alarming given NFS’s pervasive deployment in enterprise and government environments. A threat actor with access to a model of comparable capability — through Glasswing access, through independent development, or through acquisition — could conduct pre-positioned access operations across critical infrastructure at a scale and speed previously impossible.
  2. Intelligence Network Compromise
    The cryptographic library vulnerabilities identified by Mythos Preview — including authentication bypass in certificate validation and vulnerabilities in TLS and SSH implementations — represent a direct threat to secure communications infrastructure. The ability to forge certificates or decrypt encrypted traffic undermines the technical foundations of both classified communications and the broader internet trust model. A compromise of widely deployed cryptographic libraries, discovered and exploited at the speed Mythos Preview operates, could enable mass surveillance or targeted interception before defensive patches propagate.
  3. Supply Chain Attack Amplification
    Mythos Preview’s capability to find vulnerabilities in closed-source software via reverse engineering dramatically expands the attack surface available to adversaries conducting supply chain operations. Historically, supply chain attacks have required either insider access to source code or exceptionally skilled reverse engineers with deep platform expertise. Mythos Preview narrows this requirement to access to the binary and an API subscription. The implications for hardware abstraction layers, firmware, and proprietary operating system components — many of which exist in classified and defense industrial base environments — are severe.
  4. Democratization of Advanced Persistent Threat Capability
    Perhaps the most significant national security implication is structural rather than targeting-specific. The exploitation techniques demonstrated by Mythos Preview — multi-stage KASLR bypasses, HARDENED_USERCOPY evasion through per-CPU memory region targeting, JIT heap sprays chained to sandbox escapes — are techniques that were, as of 2025, associated exclusively with the most sophisticated nation-state APT groups. The documented ability of Mythos Preview to construct these exploits from first principles, at sub-$1,000 cost, means that the technical barrier separating Tier-1 nation-state actors from lower-tier threats has collapsed. Attribution models, deterrence frameworks, and the strategic calculus of cyberspace operations all require re-examination.

Project Glasswing: A Framework Inadequate to the Threat

Anthropic’s interim protective framework, Project Glasswing, restricts initial access to Mythos Preview to a curated set of critical industry partners and open source developers. The stated rationale is to provide defenders an opportunity to harden the most critical systems before models with equivalent capabilities become broadly available.

This approach reflects reasonable intent and is preferable to unrestricted release. It is nonetheless inadequate to the national security threat it purports to address, for the following reasons:

Access control is not capability control. Project Glasswing gates who can use Mythos Preview today. It does not prevent adversarial actors from developing equivalent capabilities independently. Anthropic’s own red team acknowledges that the capabilities emerged as a downstream consequence of general improvements in code, reasoning, and autonomy — not from explicit security-focused training. Any frontier AI laboratory pursuing similar general capability improvements will likely encounter comparable emergent security capabilities. The window during which Glasswing access controls provide meaningful differentiation may be months, not years.

The responsible disclosure timeline creates a structural vulnerability window. Anthropic acknowledges that fewer than 1% of the vulnerabilities Mythos Preview has identified have been patched as of the red team disclosure. The disclosure process involves professional human triagers validating findings before notifying maintainers, who then have 90 to 135 days to issue patches. During this entire period, which spans potentially years given the scale of findings, critical vulnerabilities exist in a state where Anthropic, its contractors, and its disclosure partners know of them but the public does not. This creates a concentration of offensive knowledge that is itself a national security risk if any element of that disclosure chain is compromised by a sophisticated adversary.

The framework applies only to Anthropic. Glasswing is a unilateral constraint by a single laboratory. It imposes no obligations on other frontier AI developers, no requirements on nation-state AI programs, and no verification mechanism. The history of dual-use technology governance, from nuclear to biological to cyber, demonstrates that unilateral restraint by one actor in the absence of binding multilateral frameworks does not prevent capability proliferation. It may, in the short term, simply create a competitive disadvantage for the restrained actor relative to those who face no equivalent constraints.

The scalability of the threat exceeds the capacity of coordinated disclosure. Anthropic reports identifying thousands of high- and critical-severity vulnerabilities, with human validators agreeing with severity assessments in 89% of reviewed cases. If this rate holds across the full corpus, the total number of critical vulnerabilities in the disclosure pipeline exceeds any coordinated vulnerability disclosure process’s realistic throughput. Relaxing human-review requirements, something which Anthropic has already flagged as potentially necessary, introduces quality and security risks into the disclosure chain itself.

Implications for National Security Policy

Several policy imperatives follow from this analysis:

Immediate integration into threat intelligence frameworks. Intelligence community threat models for cyber operations must be updated to treat Mythos Preview-class capability as a near-term adversary tool, not a future hypothetical. Attribution models for sophisticated exploit development must account for the possibility that what was previously assessed as Tier-1 nation-state tradecraft may now be accessible to a significantly wider range of actors.

Emergency coordinated patching for identified vulnerability classes. The federal government’s cybersecurity apparatus (i.e., CISA, NSA Cybersecurity Directorate, sector-specific agencies) must engage directly with Anthropic’s disclosure process to accelerate patching of findings affecting federal information systems and critical infrastructure. The NFS exploitation capability alone, given FreeBSD’s deployment in both commercial and government environments, warrants immediate emergency action.

Multilateral AI governance engagement on dual-use capability thresholds. The emergence of Mythos Preview demonstrates that existing AI governance frameworks, including voluntary commitments secured under prior international AI safety initiatives, DO NOT address autonomous offensive cyber capability as a defined red line. Urgent diplomatic engagement on binding international standards for capability disclosure, testing requirements, and access controls for models demonstrating APT-level exploit generation is required.

National capability development and defensive deployment. The long-term defensive potential of models like Mythos Preview is real; Anthropic’s red team argues persuasively that the advantage will ultimately favor defenders. Ensuring that outcome requires active government investment in deploying these capabilities defensively — across federal information systems, critical infrastructure, and defense industrial base environments — at a pace that matches the adversarial threat curve.

My Parting Thoughts

Claude Mythos Preview is not a hypothetical future threat. It is a documented, deployed system with verified capability to autonomously discover and exploit critical vulnerabilities in the foundational software that undergirds national security infrastructure — at a cost, speed, and accessibility that eliminates the expert-scarcity barrier that has historically constrained sophisticated offensive cyber operations.

Project Glasswing represents an attempt by Anthropic to navigate an extraordinarily difficult dual-use deployment problem responsibly. It is NOT a solution to the national security implications of this capability class. It is, at best, a grace period, the duration of which is measured in competitive AI development timelines that no single lab controls.

The counterintelligence professional’s fear, upon encountering these capabilities, is well-founded. The appropriate response is not panic, but urgency: urgency in patching, urgency in attribution model revision, urgency in policy development, and urgency in defensive deployment of the very capabilities that make the threat so acute. The adversary who first operationalizes Mythos-class capability at scale will achieve a strategic advantage in cyberspace that existing frameworks are not designed to counter.

~ C. Constantin Poindexter, MA in Intelligence, Graduate Certificate in Counterintelligence, JD, CISA/NCISS OSINT certification, DoD/DoS BFFOC Certification

Share this post:

Operation Merlin: A D&D Failure by Strategic Compromise

Operation Merlin, denial and deception, d and d, intelligence, counterintelligence, espionage, counterespionage, HUMIN, C. Constantin Poindexter, CIA, NSA, DIA

Operation Merlin: A Denial and Deception Case Study in Covert Sabotage and the Anatomy of a Strategic Blunder of Enormous Proportions

Operation Merlin was a clandestine CIA program designed to undermine Iran’s nuclear weapons development program by inserting deliberately sabotaged warhead component blueprints through a recruited human asset. Executed from approximately 1998 through the early 2000s, the operation was an ambitious attempt at deception against a state-level nuclear proliferator. I am going to share my thoughts here about Operation Merlin through the lens of Denial and Deception (D&D) doctrine, evaluate its design, execution, and compromise against accepted deception planning frameworks. Drawing on trial exhibits from United States v. Sterling (2015), investigative reports, and foundational D&D literature, my opinion is that Operation Merlin, while possessing a sound deception concept, suffered from catastrophic failures in channel selection, feedback architecture, operational security, and post-compromise institutional decision-making that collectively rendered it not merely ineffective but potentially counterproductive to the national security interests it was designed to serve.

I. Introduction: Deception as Counterproliferation

The use of deception as a counterproliferation tool occupies an uncomfortable space in American intelligence history. Unlike tactical battlefield deception or strategic wartime misdirection, i.e., domains in which the United States and its allies developed sophisticated doctrinal frameworks during the Second World War, deception operations targeting foreign weapons programs operate in a gray zone where the consequences of failure are measured not in lost engagements but in accelerated existential threats. Operation Merlin sits at the center of this tension: an operation whose architects understood the strategic imperative but whose execution betrayed a fundamental misapprehension of the doctrinal requirements for successful material deception against a sophisticated state adversary.

To offer a robust eveluation of Merlin, we need to move beyond the narrative of its public exposure (the prosecution of CIA case officer Jeffrey Sterling, the journalism of James Risen, the spectacle of a federal trial in which CIA operatives testified behind seven-foot partitions) and instead subject the operation to the same analytical framework that professional deception planners apply to their own work. This essay applies the six-element D&D planning framework derived from Barton Whaley’s foundational taxonomy in Stratagem: Deception and Surprise in War (Whaley, 2007), Richards Heuer’s cognitive analytical model from Psychology of Intelligence Analysis (Heuer, 1999), and the operational principles codified in Joint Publication 3-13.4, Military Deception (Joint Chiefs of Staff, 2012), supplemented by the historical precedent of the XX Committee’s Double Cross System as the benchmark for successful material deception at scale.

II. Strategic Context and the Deception Concept

By the late 1990s, the U.S. Intelligence Community assessed with growing confidence that Iran was pursuing nuclear weapons capability, though the evidentiary basis for this assessment remained contested internally. The 2001 National Intelligence Estimate, the first to formally conclude that Iran was working toward a nuclear weapon, was later characterized by Paul Pillar, then the CIA’s National Intelligence Officer for the Near East and South Asia, as resting on “a matter of inference” rather than direct evidence (Porter, 2014). Nevertheless, the policy imperative to disrupt Iran’s nuclear trajectory was acute, and the menu of available options was constrained by the absence of a viable military target set and the diplomatic limitations of the post-JCPOA environment that would not materialize for another fifteen years.

Into this gap stepped the CIA’s Directorate of Operations with a proposal rooted in material deception: recruit a Russian nuclear scientist with legitimate technical credentials, provide him with doctored blueprints for a nuclear warhead firing set, and direct him to deliver these blueprints to Iranian officials under the legend of a mercenary walk-in seeking financial compensation for proliferation-grade technical intelligence (Risen, 2006).

Within Whaley’s taxonomy, this concept falls squarely under the category of “mimicking”, creating a false artifact that imitates a real one closely enough to be accepted as authentic by the target (Whaley, 2007). The doctored blueprints were not fabrications from whole cloth; they were based on genuine Russian weapons designs, modified to contain dozens of hidden engineering flaws that would cause any device constructed from them to fail. The deception’s success depended on the flaws being sufficiently subtle to evade detection by Iranian scientists while being sufficiently fundamental to render the resulting weapon inoperable.

The concept was sound. Material deception (the introduction of fabricated or corrupted physical artifacts into an adversary’s intelligence or procurement stream ) has a long and occasionally successful history, from Operation Mincemeat’s fictitious invasion plans in 1943 to the CIA’s Cold War-era contamination of Soviet technical collection channels. The critical question was never whether the concept could work in principle, but whether the CIA possessed the operational infrastructure, tradecraft discipline, and institutional patience to execute it against a counterintelligence-aware adversary like Iran.

III. Operational Design and Execution

The operation’s centerpiece was a human asset — a Russian nuclear engineer recruited by the CIA and referred to at trial under the cryptonym “Merlin” (United States Department of Justice [USDOJ], 2015). Merlin possessed genuine scientific credentials, making him a plausible vector for the delivery of proliferation-grade material. His CIA handler from November 1998 through May 2000 was case officer Jeffrey Alexander Sterling, who managed the asset relationship and coordinated the operational logistics of the delivery (USDOJ, 2015).

The delivery was designed to exploit a known vulnerability in Iran’s procurement architecture: its reliance on intermediaries and walk-in sources for weapons-relevant technical intelligence. Merlin was directed to approach Iran’s mission to the International Atomic Energy Agency (IAEA) in Vienna, Austria, and provide an incomplete set of the doctored blueprints. The incompleteness was deliberate. It created an incentive structure requiring the Iranians to re-contact Merlin for the remaining schematics, thereby confirming acceptance of the bait and potentially opening a sustained intelligence collection channel into Iran’s nuclear procurement apparatus (Risen, 2006).

Former National Security Adviser Condoleezza Rice testified at Sterling’s trial that the program was “one of the only levers we had to try to disrupt Iran’s nuclear program” and characterized it as among the government’s “most closely held secrets” (Barakat, 2015). Rice further stated that she personally intervened with the New York Times to suppress publication of a story about the operation, arguing that exposure could result in catastrophic loss of life (Gerstein, 2015).

The execution in February 2000 deviated significantly from the operational plan. Merlin’s testimony at trial revealed that he had difficulty locating the Iranian mission in Vienna. When he found it, no one answered the door. He ultimately placed the envelope containing the blueprints in a mailbox and covered it with a newspaper (Solomon, 2015). Additionally, Merlin deviated from his handlers’ instructions regarding the contact mechanism: rather than providing an American mailing address as directed, he substituted an email address, reasoning that an American postal address would appear suspicious to Iranian counterintelligence and could be traced back to him (Solomon, 2015).

These deviations carry BIG implications when evaluated against D&D doctrine. An asset who autonomously modifies operational parameters based on his own risk calculus (however rational that calculus may be) introduces uncontrolled variables into the deception architecture. More critically, Merlin’s technical competence, which made him a credible channel, simultaneously made him capable of evaluating the material he was tasked to deliver. According to Risen’s account, Merlin recognized the deliberate flaws in the schematics and transmitted his belief along with the delivery which signaled to the Iranians that the blueprints were intelligence service-manufactured, allowing Iranian scientists to identify and discard the sabotaged elements while extracting legitimate technical data (Risen, 2006). Merlin denied these characterizations under oath, testifying that Risen’s depiction of him as reluctant was “completely untrue” (Solomon, 2015). The divergence itself is analytically significant: if Risen’s source was not Merlin, then whoever provided those details possessed the kind of intimate operational knowledge consistent with a case officer’s access.

IV. D&D Doctrinal Evaluation

A. Desired Perception

The foundational requirement of any deception operation is a clearly defined desired perception, i.e., the specific belief the operation is designed to induce in the target’s mind (Joint Chiefs of Staff, 2012). Operation Merlin’s desired perception was straightforward: that the blueprints were genuine proliferation material obtained through an illicit procurement channel (a disgruntled or mercenary Russian scientist selling weapons knowledge for financial gain).

This perception was plausible on its face. Russian nuclear scientists in the post-Soviet period were documented to be underpaid, underemployed, and in some cases actively solicited by proliferating states. The desired perception exploited a real phenomenon, which is doctrinally correct. The most effective deceptions are those anchored in patterns the target already recognizes and expects (Heuer, 1999). Assessment: Adequate.

B. The Deception Story

The constructed narrative, a Russian scientist approaching Iran’s IAEA mission as a walk-in, offering warhead-grade schematics for money, was coherent as a standalone legend. Walk-in approaches by foreign nationals offering technical intelligence were not unprecedented in proliferation networks.

However, there is no indication in the trial record that the CIA subjected this story to rigorous adversarial analysis “red-teaming” we call it. The planners missed specifically examining how Iran’s Ministry of Intelligence and Security (VEVAK) would process and evaluate a cold-approach walk-in offering firing set blueprints. VEVAK had extensive institutional experience identifying Western intelligence provocations, and a walk-in of this nature. An unsolicited player offering the single most sensitive category of weapons data, with no prior relationship or established bona fides would have triggered significant counterintelligence scrutiny. The absence of documented red-team analysis suggests the deception story was evaluated for internal plausibility rather than adversarial resilience. Assessment: Deficient.

C. Channel Selection

D&D doctrine, codified in lessons from the London Controlling Section’s World War II operations and subsequent CIA and DoD guidance, instructs that the credibility of the delivery channel is the single most critical variable in material deception. The channel must be one that the adversary already trusts or is predisposed to trust, typically because the source has previously provided verified intelligence, is embedded in a network the adversary already exploits, or mimics an approach pattern the adversary has successfully used before (Holt, 2004).

From Iranian FIS’s perspective Merlin possessed none of these attributes . He was an unknown entity conducting a cold approach. His operational execution was amateurish, i.e., unable to locate the mission, leaving material in an unattended mailbox, etc.. From an Iranian counterintelligence officer’s perspective, applying the analytical principles Heuer articulated, the approach contained no prior cognitive anchor that would predispose acceptance (Heuer, 1999). The channel was cold, unvetted from the target’s vantage point, and operationally clumsy.

Taking a lesson from history, the Double Cross System is instructive. The XX Committee’s deception channels, turned German agents who fed disinformation to the Abwehr, were effective precisely because they were channels the adversary had already accepted and validated through prior intelligence exchanges. Double Cross built credibility over months and years of carefully calibrated true-false reporting mixtures before introducing critical strategic deceptions like FORTITUDE. Operation Merlin attempted to deliver the equivalent of FORTITUDE-grade material through a channel with zero established credibility. Assessment: Critically Deficient.

D. Feedback Architecture

The operation’s feedback mechanism was its most elegant design element: the deliberate incompleteness of the blueprints created a natural trigger requiring Iran to re-contact Merlin for the remaining schematics, thereby confirming acceptance.

The problem was singular and fatal: Iran never responded. This silence created an analytical void that the operation had no means to resolve. The CIA could not determine whether Iran had detected the deception and discarded it, had accepted the material but chose to develop it independently, had never routed the material to a competent analyst, or whether VEVAK had flagged the approach as a provocation and filed it as a counterintelligence reference.

Well-designed deception operations maintain redundant feedback mechanisms precisely to prevent this kind of interpretive paralysis. The Double Cross System’s feedback architecture, continuous monitoring of German assessments through ULTRA decrypts of Abwehr and OKW communications, allowed deception planners to observe in near-real-time whether their false intelligence was being accepted, rejected, or partially integrated, and to adjust their deception stories accordingly (Howard, 1995). Operation Merlin had a single feedback point, and when that point went silent, the operation was effectively blind. No secondary collection mechanism (SIGINT, HUMINT from other sources inside Iran’s nuclear apparatus, or technical surveillance of Iranian procurement activity) was established to provide independent confirmation of the operation’s effect. Assessment: Critically Deficient.

E. Adaptability

Nothing in the trial record indicates that the CIA developed contingency plans for the various failure modes the operation might encounter — Iranian detection, asset compromise, the asset’s autonomous deviation from instructions, or operational exposure through internal security breaches. The reassignment of Sterling in May 2000 without documented succession planning or compartmentation review further suggests that continuity of operations planning was inadequate (USDOJ, 2015). He was the only player with intimate knowledge of the asset. When Sterling subsequently entered an adversarial posture with the agency, there was no adaptive mechanism to contain the resulting vulnerability. Assessment: Critically Deficient.

F. Operational Security

This is where Operation Merlin became a catastrophic F.U. The universe of individuals with knowledge of the operation expanded and expanded. The President, the National Security Adviser, senior CIA leadership, multiple case officers, the Russian asset and his wife, and after Sterling raised concerns through ostensibly proper channels, staffers on the Senate Select Committee on Intelligence knew it all. Each additional read-in was a point of compromise.

The most fundamental security failure was personnel-related. Sterling possessed direct, intimate knowledge of the operation, the asset’s identity, the tradecraft, and the operational dynamics. He was reassigned and then, within three months, became an Agency “adversary”. Counterintelligence doctrine requires enhanced monitoring of personnel with access to sensitive compartmented information who demonstrate indicators of potential unreliability. That would ABSOLUTELY include legal disputes with the employing I.C. agency. There is no indication that any such monitoring was implemented (Gerstein, 2015; Solomon, 2015). Assessment: Catastrophically Deficient.

V. The Vectors of Compromise

Operation Merlin was compromised through three distinct vectors, each representing a failure at a different level of the D&D security architecture.

The asset’s autonomous judgment constituted the first vector. Merlin’s technical competence, the very attribute that made him a credible channel, enabled him to evaluate and potentially undermine the material he was tasked to deliver. This is a structural paradox inherent in using technically sophisticated assets for material deception: the more credible the channel, the more capable it is of detecting and subverting the deception it carries.

The case officer’s grievance constituted the second vector. The prosecution established through communications metadata that Sterling and Risen were in contact during the periods preceding and following the publication of State of War, i.e., phone calls to Risen’s residence, emails containing articles related to Sterling’s former operational portfolio, and continued contact from December 2003 through November 2005 (USDOJ, 2015). Sterling’s defense argued that Senate Intelligence Committee staffers were a more plausible source and that the government’s evidence proved only communication, not the transmission of classified content (Wheeler, 2015). The jury found the circumstantial evidence sufficient, convicting Sterling on nine felony counts on January 26, 2015, and Judge Leonie Brinkema sentenced him to forty-two months (USDOJ, 2015).

The government’s self-compromise constituted the third and most strategically damaging vector. In prosecuting Sterling under the Espionage Act, the government introduced CIA operational cables, internal planning documents, and testimony from twenty-three CIA officers into the public record of a federal courtroom (Solomon, 2015). The trial revealed the operational concept, the asset’s role, the delivery methodology, the nature of the sabotaged blueprints, and the strategic rationale in far greater specificity than Risen’s book had disclosed. Bloomberg News reported from Vienna that the IAEA would “probably review intelligence they received about Iran as a result of the revelations,” with a former British envoy to the IAEA warning that the disclosures suggested “a possibility that hostile intelligence agencies could decide to plant a ‘smoking gun’ in Iran for the IAEA to find” (Solomon, 2015). Prosecutor James Trump acknowledged at sentencing that the exposure “ended the use of the nuclear-plans ruse against other countries” (Gerstein, 2015).

This third vector represents the most consequential D&D failure. In attempting to punish a compromise that had exposed a single operation, the government’s prosecution compromised an entire deception methodology. Any state with access to the public trial record — which now constitutes the most comprehensive open-source documentation of a CIA material deception program targeting a foreign nuclear capability — could retroactively audit its own procurement channels for similar operations and inoculate itself against future attempts. This is SPECIFICALLY why I refer to this as a strategic rather than tactical or operational disaster.

The Anti-Double Cross

Evaluated in its totality against the D&D planning framework, Operation Merlin represents something approaching the inverse of the Double Cross System. Where Double Cross maintained dozens of simultaneous channels with established credibility, Merlin relied on a single cold channel with no prior validation. Where Double Cross monitored adversary acceptance in near-real-time through ULTRA, Merlin had a single feedback mechanism that produced silence. Where Double Cross adapted its deception narratives continuously based on observed adversary reactions, Merlin had no adaptive capability. Where Double Cross maintained ruthless operational security — including the execution of compromised agents — Merlin allowed a disaffected case officer with comprehensive operational knowledge to depart the agency in an adversarial posture without enhanced counterintelligence monitoring.

The strategic concept underlying Operation Merlin (using sabotaged technical intelligence to misdirect a proliferating state’s weapons development) was theoretically sound. In a different operational context, I believe that it was completely viable. The failure was not conceptual but executional: a series of compounding deficiencies in channel selection, feedback architecture, adaptability, and operational security that transformed an ambitious deception operation into what may ultimately have been a net intelligence gain for the very adversary it was designed to deceive.

For the counterintelligence professional, Operation Merlin’s most enduring lesson may be its final chapter. The institutional impulse to punish unauthorized disclosure, when pursued through the adversarial transparency of a federal prosecution, can inflict damage orders of magnitude greater than the original compromise. The prosecution of Jeffrey Sterling did not restore the secrecy of Operation Merlin. It annihilated it. With it went the viability of an entire category of covert action against nuclear proliferators for the foreseeable future.

Regardless of which and what was worse, the results ware and are BAAADD. The op. is now a template. Any state with a competent intelligence service and access to the trial record (which is to say, absolutely everyone) can now retroactively audit its own procurement channels for operations matching this kind of pattern. The Agency has also created a counterintelligence inoculation of the adversary set. Every proliferating state now possesses a known reference case for how the U.S. I.C. constructs material deception against nuclear programs. Add to that the diplomatic blowback with the IAEA and lingering Iran-theatre analytical poisoning, and this becomes even uglier.

~ C. Constantin Poindexter, MA in Intelligence, Graduate Certificate in Counterintelligence, JD, CISA/NCISS OSINT certification, DoD/DoS BFFOC Certification

Bibliography

  • Barakat, M. (2015, January 16). CIA asset ‘Merlin’ testifies about mission at CIA leak trial. Associated Press.
  • Gerstein, J. (2015, May 11). Former CIA officer sentenced to 3-1/2 years for leaking Iran details. Politico.
  • Heuer, R. J. (1999). Psychology of intelligence analysis. Center for the Study of Intelligence, Central Intelligence Agency.
  • Holt, T. (2004). The deceivers: Allied military deception in the Second World War. Scribner.
  • Howard, M. (1995). Strategic deception in the Second World War: British intelligence operations against the German High Command. W. W. Norton.
  • Joint Chiefs of Staff. (2012). Joint Publication 3-13.4: Military deception. U.S. Department of Defense.
  • Porter, G. (2014). Manufactured crisis: The untold story of the Iran nuclear scare. Just World Books.
  • Risen, J. (2006). State of war: The secret history of the NSA and the Bush administration. Free Press.
  • Solomon, N. (2015, February 27). CIA evidence from whistleblower trial could tilt Iran nuclear talks. Guernica.
  • United States Department of Justice. (2015, May 11). Former CIA officer sentenced to 42 months in prison for leaking classified information and obstruction of justice [Press release].
  • United States of America v. Jeffrey Alexander Sterling, No. 1:11-cr-00005 (E.D. Va. 2015). Selected case files. Federation of American Scientists, Project on Government Secrecy.
  • Whaley, B. (2007). Stratagem: Deception and surprise in war. Artech House.
  • Wheeler, M. (2015, February 21). What was the CIA really doing with Merlin by 2003? EmptyWheel.

Share this post: